 OUTPOST
Cyber Threat Intelligence
Breaches, campaigns, advisories and research.
New to this? Key terms for this page
- CVE
- A public identifier, such as CVE-2026-12345, given to one specific security flaw so everyone can refer to the same bug.
- Zero-day
- A vulnerability that attackers exploit before the vendor has released a fix, leaving defenders with no patch to apply.
- Ransomware
- Malware that locks or steals a victim's data and demands payment to unlock it, or to stop the stolen data being published.
- IOC
- A trace of an attack, such as a malicious IP address, domain or file hash, that defenders can search for in their logs.
- APT
- A well-resourced group, often linked to a state, that breaks into targets and stays hidden for a long time.
- Supply-chain attack
- An attack that compromises a trusted supplier or software update so the malicious code reaches many customers at once.
Hitachi Energy CoreTec Product (opens the original article)
Hitachi Energy says OS command injection and Dirty Frag vulnerabilities affect its CoreTec product.
Cyber CISA Advisories
What to checkCheck whether CoreTec is in your environment and review the relevant advisory for mitigation guidance.
Sources1CISA Advisories
Siemens Mendix SAML Module (opens the original article)
The Mendix SAML module contains an authentication bypass vulnerability, according to the advisory snippet.
Cyber CISA Advisories
What to checkIdentify use of the Mendix SAML module and review authentication controls and the advisory.
Sources1CISA Advisories
Hitachi Energy TRO600 series products (opens the original article)
Hitachi Energy says multiple vulnerabilities affect TRO600 series products.
Cyber CISA Advisories
What to checkCheck for TRO600 products and consult the advisory for affected versions and recommended action.
Sources1CISA Advisories
Chrome extensions with 13.4 million installs caught hijacking searches (opens the original article)
BleepingComputer reports that 319 Chrome extensions with 13.4 million reported installations redirected searches through tracking servers to generate advertising revenue from Bing and Yahoo.
Cyber BleepingComputer
What to checkReview installed extensions, remove untrusted ones, and investigate unexpected search redirects.
Sources1BleepingComputer
Federal bankruptcy courts contractor says no data stolen during cyber intrusion (opens the original article)
BAE Systems says no data was extracted during its probe into a cyberattack on systems for federal bankruptcy courts.
Cyber The Record
What to checkCheck the contractor’s incident findings and monitor for updates about affected systems or data.
Sources1The Record
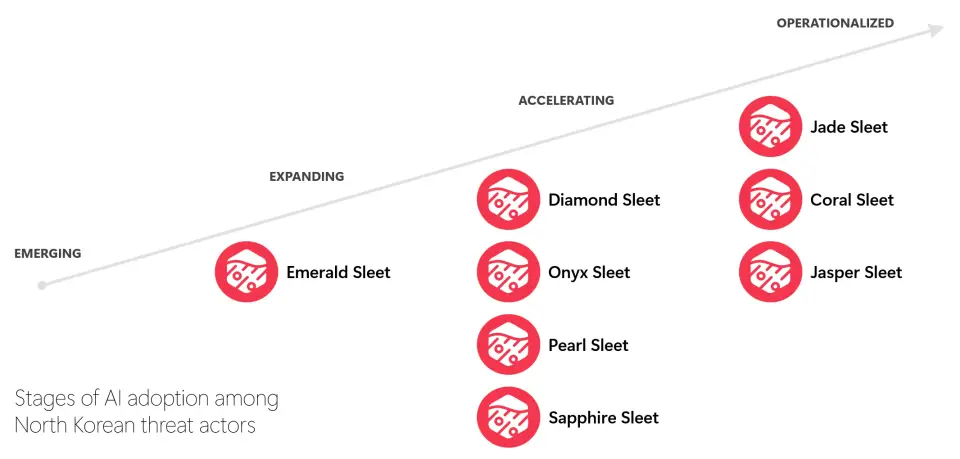
Tracking AI adoption in North Korean threat actor tradecraft (opens the original article)
Microsoft says North Korean threat actors are expanding their use of AI, with varying levels of adoption, to increase attack speed and efficiency.
Cyber Microsoft Security
What to checkReview threat intelligence for changes in reported attacker use of AI and update relevant detection guidance.
Sources1Microsoft Security
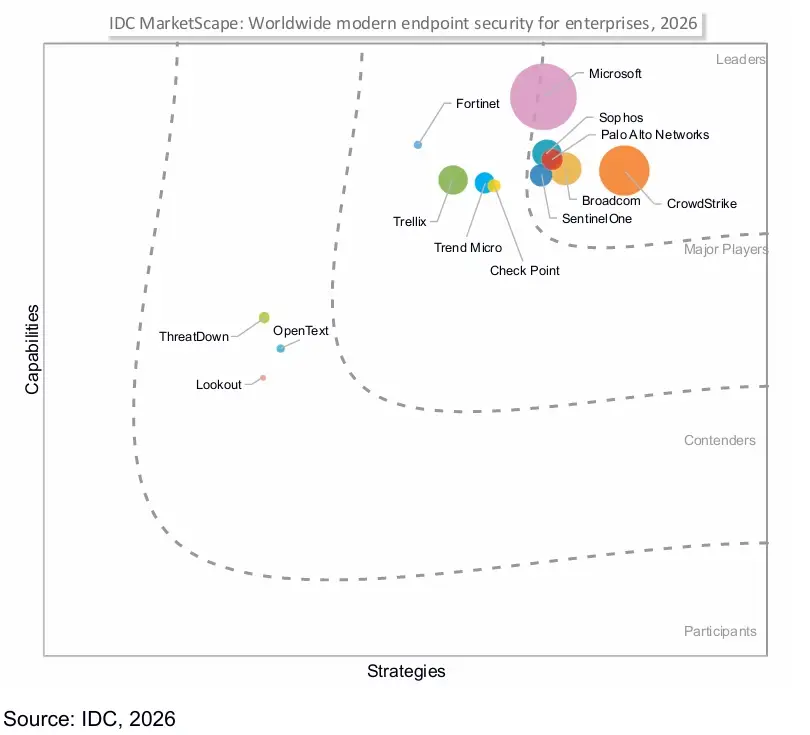
IDC MarketScape names Microsoft a Leader in the 2026 Worldwide Modern Endpoint Security for Enterprises Vendor Assessment (opens the original article)
IDC named Microsoft a Leader in its 2026 Worldwide Modern Endpoint Security for Enterprises Vendor Assessment.
Cyber Microsoft Security
What to checkTreat the assessment as vendor positioning; compare endpoint security claims with your organization’s needs.
Sources1Microsoft Security
Microsoft fixes Remote Desktop failures caused by recent Windows updates (opens the original article)
Microsoft says it resolved a known issue preventing non-admin users from connecting through Remote Desktop when Administrator protection is enabled.
Cyber BleepingComputer
What to checkCheck Remote Desktop access for non-admin users where Administrator protection is enabled.
Sources1BleepingComputer
3 Ways AI Agents Already Operate in Your Browser (opens the original article)
Keep Aware says AI agents can use authenticated browsers, corporate applications, and sensitive data while appearing to act as legitimate employees.
Cyber BleepingComputer
What to checkReview which agents can access authenticated browsers, corporate applications, and sensitive data.
Sources1BleepingComputer
CISA warns of Fragnesia Linux flaw chained in PHP2Shell attacks (opens the original article)
CISA warned federal agencies to patch a high-severity Linux kernel privilege escalation bug attackers are chaining with PHP2Shell flaws.
Cyber BleepingComputer
What to checkCheck for exposure to the Linux flaw and PHP2Shell, and prioritize patching.
Sources1BleepingComputer
Keyword index
Counted from this page. Select one to filter.