 OUTPOST
Dark web
Claims from ransomware leak sites, forums and social media, with context, plus confirmed breaches. Newest first, checked every five minutes.
Latest claims
Showing all 40 claims.
Data for sale
User advertises access to a DarkForums private archive Telegram channel
The title advertises access to a DarkForums private archive Telegram channel.
What we can see
Forum threads can only be read by members, so Outpost has the title of this post and nothing else. It does not log in to criminal forums.
No public write-up of this claim has been found yet.
Unverified claimOriginal forum post (opens in a new tab)
Data for sale
User claims to offer GTA 5 source code
The title advertises GTA 5 source code.
What we can see
Forum threads can only be read by members, so Outpost has the title of this post and nothing else. It does not log in to criminal forums.
No public write-up of this claim has been found yet.
Unverified claimOriginal forum post (opens in a new tab)
Data leak
User claims a Discord CEO dox leak
The title alleges a dox leak involving the Discord CEO.
What we can see
Forum threads can only be read by members, so Outpost has the title of this post and nothing else. It does not log in to criminal forums.
Public coverage of what looks like the same claim: A post claims dark-web listings involving several organizations and data (@socradar).
Unverified claimOriginal forum post (opens in a new tab)
Vulnerability
User claims a SimpleSwap API exploit
The title alleges a SimpleSwap API exploit.
What we can see
Forum threads can only be read by members, so Outpost has the title of this post and nothing else. It does not log in to criminal forums.
Public coverage of what looks like the same claim: Report claims Qilin ransomware targeted Smith, Feddeler & Smith, P.A. (@FalconFeedsio).
Unverified claimOriginal forum post (opens in a new tab)
Data leak
User claims a golfcanada.ca data breach
The title alleges a data breach at golfcanada.ca.
What we can see
Forum threads can only be read by members, so Outpost has the title of this post and nothing else. It does not log in to criminal forums.
Public coverage of what looks like the same claim: Foundation says a backend breach led to phishing from its domains (@DailyDarkWeb).
Unverified claimOriginal forum post (opens in a new tab)
Data for sale
- Size claimed
- 3TB
Actor claims EUROCONTROL database and admin panel are for sale
A threat actor using the alias “Marx1337” claims to offer a 3TB database and administrative panel taken from EUROCONTROL for sale.
Context and what defenders can do
Claims that databases or administrative panels are stolen and offered for sale are common on underground forums. Such posts may be unverified, and advertised material may be fabricated, outdated, or obtained through other means; this is general background, not confirmation of this claim.
What defenders can do
- Review access logs for unusual administrative access.
- Enforce multifactor authentication and rotate exposed credentials if warranted.
Unverified claimOriginal post on X (opens in a new tab)
Ransomware
- Sector
- Legal & professional
- Size claimed
- 214 GB
Report claims Beasley Allen Law Firm fell victim to FALCON ransomware
The title claims Beasley Allen Law Firm reportedly fell victim to FALCON ransomware and that 214 GB of data was compromised.
Context and what defenders can do
Ransomware groups may claim to have compromised organizations or data as part of extortion attempts. Such claims are not independently verified by a post alone; this is general background, not confirmation of this claim.
What defenders can do
- Review endpoint alerts and systems for signs of intrusion.
- Verify backups are isolated and restorable.
Unverified claimOriginal post on X (opens in a new tab)
Data leak
Actor claims Ryanair domain credentials were leaked on a dark web forum
A post alleges that domain credentials tied to Ryanair were leaked on a dark web forum.
Context and what defenders can do
As general background, forum posts about credentials may be unverified and do not establish that credentials are valid or current. Organizations commonly monitor for exposed credentials and investigate reports through trusted channels.
What defenders can do
- Review identity-provider logs for unusual sign-ins.
- Rotate potentially exposed credentials and revoke active sessions.
Unverified claimOriginal post on X (opens in a new tab)
Ransomware
- Sector
- Education
SafePay claims Jumonji University on its ransomware list
SafePay claims Jumonji University as a ransomware victim.
Context and what defenders can do
As general background, ransomware groups may list organizations to pressure them during extortion attempts. A listing alone does not confirm encryption, data theft, or the accuracy of the group's claims.
What defenders can do
- Check backups and incident-response procedures.
- Monitor systems for suspicious access and encryption activity.
Unverified claimOriginal post on X (opens in a new tab)
Ransomware
- Sector
- Technology
The Gentlemen ransomware group claims to list VA Tech WABAG
The title claims that The Gentlemen ransomware group listed VA Tech WABAG on its leak site.
Context and what defenders can do
In general, ransomware groups may use leak-site listings to pressure organizations during extortion attempts. A listing alone does not independently verify a breach or the alleged data.
What defenders can do
- Review relevant systems and security alerts for signs of unauthorized access.
- Follow your incident-response process and preserve relevant logs.
Unverified claimOriginal post on X (opens in a new tab)
Ransomware
- Country
- USUnited States
The Gentlemen ransomware group claims to list SAP Latin America
The title claims that The Gentlemen ransomware group added SAP Latin America to its leak site.
Context and what defenders can do
In general, ransomware groups may use leak-site listings to pressure organizations during extortion attempts. Such posts are claims and do not independently establish a compromise.
What defenders can do
- Review relevant systems and security alerts for signs of unauthorized access.
- Follow your incident-response process and preserve relevant logs.
Unverified claimOriginal post on X (opens in a new tab)
Ransomware
- Sector
- Technology
- Country
- TRTürkiye
The Gentlemen claims to list SoftwareOne Türkiye on a leak site
The title says The Gentlemen ransomware group listed SoftwareOne Türkiye on its leak site.
Context and what defenders can do
As general background, ransomware groups may use leak-site listings to pressure organizations during extortion attempts. A listing alone does not establish that data was accessed or disclosed.
What defenders can do
- Review security alerts and investigate unusual access.
- Verify backups and test restoration procedures.
Unverified claimOriginal post on X (opens in a new tab)
Hacktivism
- Country
- SASaudi Arabia
Dark Storm Team claims to have targeted websites in Saudi Arabia
The title says Dark Storm Team claims to have targeted multiple websites in Saudi Arabia.
Context and what defenders can do
As general background, DDoS attacks attempt to disrupt online services by overwhelming them with traffic. Such claims can be difficult to verify from public posts alone.
What defenders can do
- Monitor service availability and traffic anomalies.
- Confirm DDoS mitigation and response procedures are ready.
Unverified claimOriginal post on X (opens in a new tab)
Ransomware
The Gentlemen claims to list WIKA Beton on a leak site
The title says The Gentlemen ransomware group listed WIKA Beton on its leak site.
Context and what defenders can do
As general background, ransomware groups may use leak-site listings to pressure organizations during extortion attempts. A listing alone does not establish that data was accessed or disclosed.
What defenders can do
- Review security alerts and investigate unusual access.
- Verify backups and test restoration procedures.
Unverified claimOriginal post on X (opens in a new tab)
Ransomware
The Gentlemen claims to list Quito's public works and mobility agency
The title says The Gentlemen ransomware group listed Quito's public works and mobility agency on its leak site.
Context and what defenders can do
As general background, ransomware groups may use leak-site listings to pressure organizations during extortion attempts. A listing alone does not establish that data was accessed or disclosed.
What defenders can do
- Review security alerts and investigate unusual access.
- Verify backups and test restoration procedures.
Unverified claimOriginal post on X (opens in a new tab)
From the original post. May show sensitive material.
Report claims Qilin ransomware targeted Smith, Feddeler & Smith, P.A.
The title alleges that Smith, Feddeler & Smith, P.A. fell victim to Qilin ransomware.
Context and what defenders can do
As general background, ransomware incidents may involve data theft, encryption, or both. This background is not confirmation of the claim in the title.
What defenders can do
- Review endpoint and network alerts for suspicious activity.
- Verify backups are protected and restorable.
Unverified claimOriginal post on X (opens in a new tab)
From the original post. May show sensitive material.
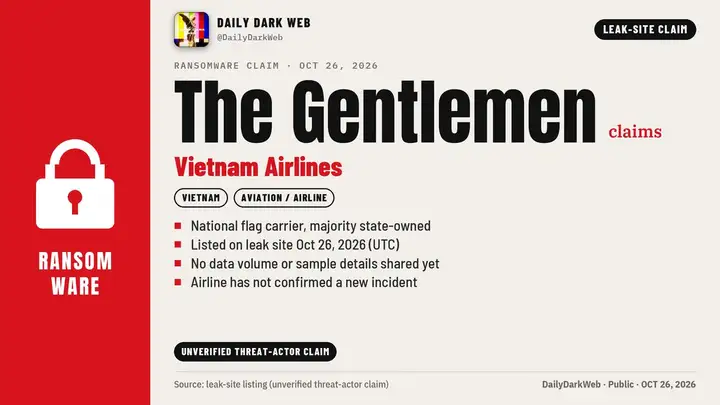
The Gentlemen claims to list Vietnam Airlines on its leak site
The title alleges that The Gentlemen ransomware group listed Vietnam Airlines on its leak site.
Context and what defenders can do
As general background, ransomware groups may use leak-site posts to pressure organizations during extortion attempts. Such posts alone do not establish whether data was accessed or published.
What defenders can do
- Monitor systems for signs of unauthorized access.
- Review incident response and data-exposure procedures.
Unverified claimOriginal post on X (opens in a new tab)
From the original post. May show sensitive material.
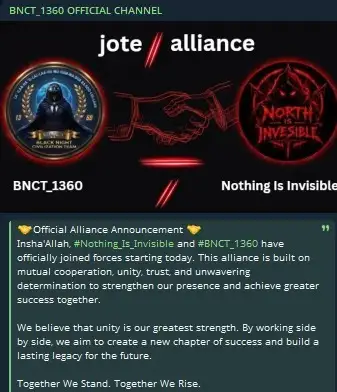
Nothing_Is_Invisible and BNCT_1360 claim to announce an alliance
The title alleges that Nothing_Is_Invisible and BNCT_1360 announced an alliance.
Context and what defenders can do
As general background, hacktivist groups may announce alliances to coordinate messaging or disruptive activity. Such announcements do not by themselves confirm operational capability or future actions.
What defenders can do
- Monitor public threat reporting for relevant activity.
- Ensure internet-facing services have current protections.
Unverified claimOriginal post on X (opens in a new tab)
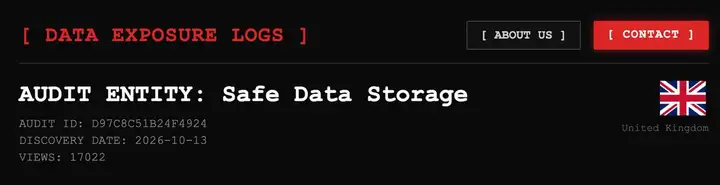
From the original post. May show sensitive material.
Report claims AUDIT TEAM ransomware targeted Safe Data Storage Ltd
The title alleges that Safe Data Storage Ltd fell victim to AUDIT TEAM ransomware.
Context and what defenders can do
As general background, ransomware incidents may involve data theft, encryption, or both. This background is not confirmation of the claim in the title.
What defenders can do
- Review endpoint and network alerts for suspicious activity.
- Verify backups are protected and restorable.
Unverified claimOriginal post on X (opens in a new tab)
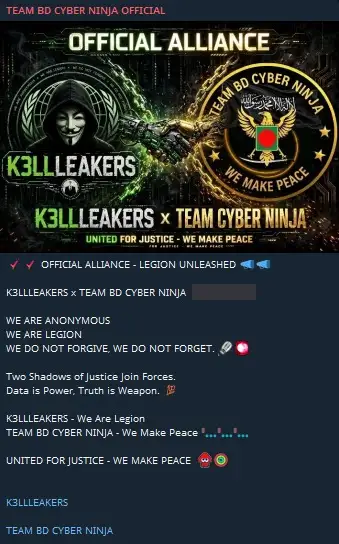
From the original post. May show sensitive material.
K3LLLEAKERS and TEAM BD CYBER NINJA claim to announce an alliance
The title alleges that K3LLLEAKERS and TEAM BD CYBER NINJA announced an alliance.
Context and what defenders can do
As general background, hacktivist groups may announce alliances to coordinate messaging or disruptive activity. Such announcements do not by themselves confirm operational capability or future actions.
What defenders can do
- Monitor public threat reporting for relevant activity.
- Ensure internet-facing services have current protections.
Unverified claimOriginal post on X (opens in a new tab)
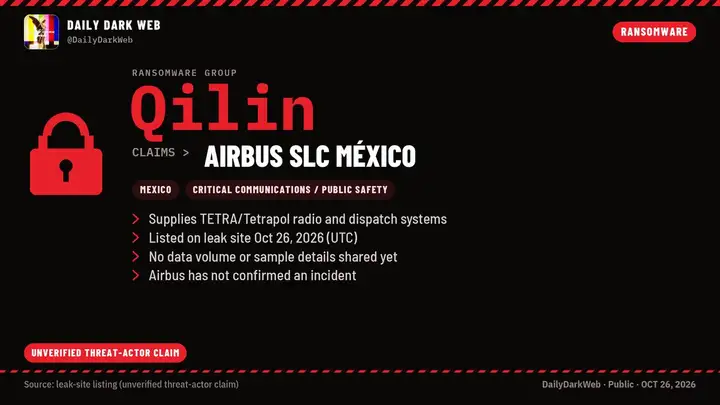
From the original post. May show sensitive material.
Qilin claims to list Airbus SLC México on its leak site
The title alleges that Qilin listed Airbus SLC México on its leak site.
Context and what defenders can do
As general background, ransomware groups may use leak-site posts to pressure organizations during extortion attempts. Such posts alone do not establish whether data was accessed or published.
What defenders can do
- Monitor systems for signs of unauthorized access.
- Review incident response and data-exposure procedures.
Unverified claimOriginal post on X (opens in a new tab)
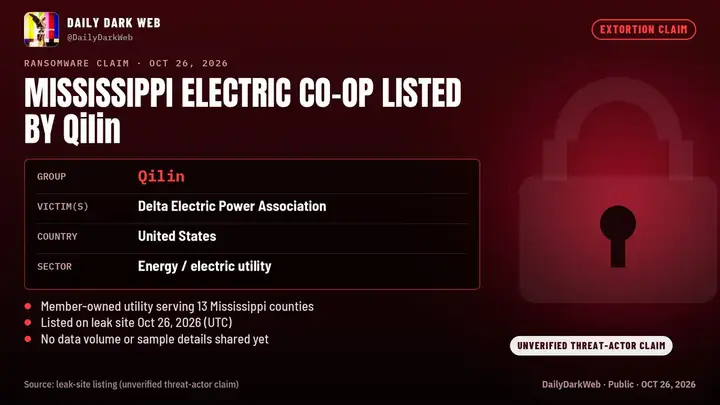
From the original post. May show sensitive material.
Qilin claims to list Delta Electric Power Association on its leak site
The title alleges that Qilin listed Delta Electric Power Association on its leak site.
Context and what defenders can do
As general background, ransomware groups may use leak-site posts to pressure organizations during extortion attempts. Such posts alone do not establish whether data was accessed or published.
What defenders can do
- Monitor systems for signs of unauthorized access.
- Review incident response and data-exposure procedures.
Unverified claimOriginal post on X (opens in a new tab)
From the original post. May show sensitive material.
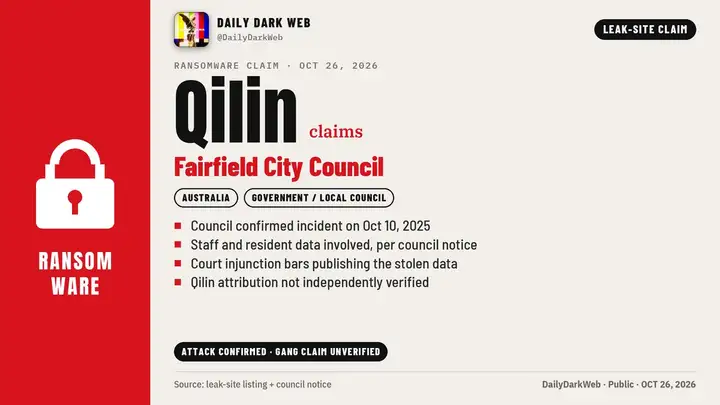
Qilin claims to list Fairfield City Council on its leak site
The title alleges that Qilin listed Fairfield City Council on its leak site and claims a ransomware attack.
Context and what defenders can do
As general background, ransomware groups may use leak-site posts to pressure organizations during extortion attempts. Such posts alone do not establish whether data was accessed or published.
What defenders can do
- Monitor systems for signs of unauthorized access.
- Review incident response and data-exposure procedures.
Unverified claimOriginal post on X (opens in a new tab)
From the original post. May show sensitive material.
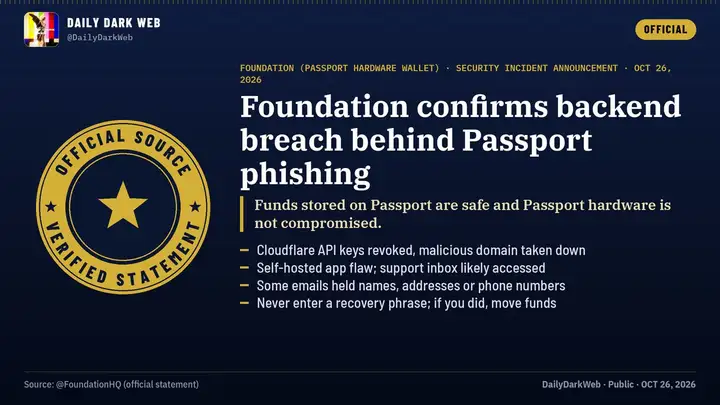
Foundation says a backend breach led to phishing from its domains
The title alleges that Foundation confirmed a backend breach behind phishing sent from its own domains.
Context and what defenders can do
As general background, compromised backend systems can be abused to send deceptive messages that appear to come from legitimate sources. This general risk does not verify the claim in the title.
What defenders can do
- Warn users to verify unexpected messages through trusted channels.
- Review access logs and secure administrative accounts.
Unverified claimOriginal post on X (opens in a new tab)
From the original post. May show sensitive material.
Report claims Qilin ransomware targeted Race Trakka
The title alleges that Race Trakka fell victim to Qilin ransomware.
Context and what defenders can do
As general background, ransomware incidents may involve data theft, encryption, or both. This background is not confirmation of the claim in the title.
What defenders can do
- Review endpoint and network alerts for suspicious activity.
- Verify backups are protected and restorable.
Unverified claimOriginal post on X (opens in a new tab)
From the original post. May show sensitive material.
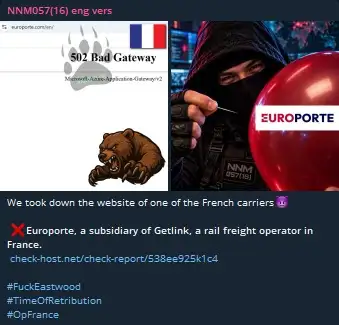
NoName claims to have targeted Europorte's website with a DDoS attack
The title alleges that NoName claimed to have targeted Europorte's website.
Context and what defenders can do
As general background, distributed denial-of-service attacks aim to disrupt access to online services by overwhelming them with traffic. A claim of targeting does not establish service impact.
What defenders can do
- Use DDoS protection and traffic filtering for public services.
- Monitor availability and unusual traffic patterns.
Unverified claimOriginal post on X (opens in a new tab)
Other claim
- Sector
- Technology
- Country
- AUAustralia
A post claims dark-web listings involving several organizations and data
The title alleges dark-web claims involving Finaxis.cloud, WoWInstaller, an Argentine Moodle site, MyHairCare Australia, and HT Médica.
Context and what defenders can do
As general background, dark-web posts may advertise data or make claims that are incomplete, misleading, or unverified. Listing claims alone do not establish the authenticity or exposure of information.
What defenders can do
- Avoid accessing or redistributing allegedly leaked material.
- Review exposure monitoring and incident reporting procedures.
Unverified claimOriginal post on X (opens in a new tab)
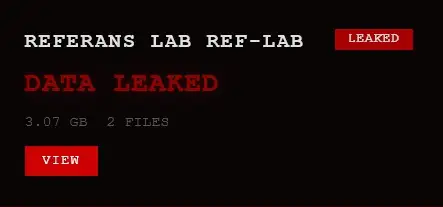
From the original post. May show sensitive material.
Actor claims Referans Lab was affected by DoomMageddon ransomware
The post alleges that Referans Lab, described in the title as a Turkey-based healthcare organization, fell victim to DoomMageddon ransomware.
Context and what defenders can do
In general, ransomware groups may claim to have compromised organizations and may use leak sites or social media to publicize those claims. Such posts are not, by themselves, independent confirmation of an incident.
What defenders can do
- Review endpoint and network alerts for signs of ransomware activity.
- Verify backups are protected and restoration procedures are tested.
Unverified claimOriginal post on X (opens in a new tab)
Hacktivism
Accounts claim THE QWERTY BOY'S and TEAM BD CYBER NINJA formed an alliance
The post claims THE QWERTY BOY'S and TEAM BD CYBER NINJA officially announced a new alliance.
Context and what defenders can do
As general background, hacktivist groups may announce alliances to signal coordination or attract attention. Such announcements alone do not establish the groups’ capabilities or joint activity.
What defenders can do
- Monitor relevant public threat reporting for corroboration.
- Review incident-response contacts and escalation procedures.
Unverified claimOriginal post on X (opens in a new tab)
Ransomware
- Sector
- Transport & logistics
Post claims TRANSPORTES JIMENEZ and REYES JIM REY S.A. fell victim to EMPERADOR ransomware
The post alleges that TRANSPORTES JIMENEZ and REYES JIM REY S.A. fell victim to EMPERADOR ransomware.
Context and what defenders can do
As general background, ransomware claims may be posted before an organization confirms an incident. Transportation and logistics organizations commonly rely on interconnected systems, making prepared response and continuity plans useful.
What defenders can do
- Verify the claim through trusted internal and external channels.
- Review backups and ransomware response procedures.
Unverified claimOriginal post on X (opens in a new tab)
Ransomware
- Sector
- Education
Qilin claims a ransomware attack on Burnaby Schools
The post says Qilin listed Burnaby Schools (School District 41) on its leak site and claimed responsibility for an attack.
Context and what defenders can do
As general background, ransomware groups use leak-site listings to pressure organizations and publicize allegations. Education environments often support many users and services, so access controls and recovery planning are important.
What defenders can do
- Check for corroboration through official district communications.
- Review identity controls and backup readiness.
Unverified claimOriginal post on X (opens in a new tab)
Ransomware
ShinyHunters claims data theft from 7-Eleven's Salesforce environment
The post alleges that ShinyHunters stole data from 7-Eleven's Salesforce environment and listed the company on a dark web forum.
Context and what defenders can do
As general background, extortion groups may claim access to cloud or business platforms and threaten to disclose data. Such claims require independent validation; organizations generally benefit from reviewing access logs and third-party integrations.
What defenders can do
- Review Salesforce access logs and connected applications.
- Follow established procedures for investigating data-exposure claims.
Unverified claimOriginal post on X (opens in a new tab)
Ransomware
ShinyHunters claims records were stolen from CarGurus
The post says ShinyHunters added CarGurus to a dark web forum's claimed-victim list and claims records were stolen.
Context and what defenders can do
As general background, threat actors sometimes publish victim lists to pressure organizations or draw attention to alleged breaches. A listing does not by itself confirm data access, theft, or the scope of an incident.
What defenders can do
- Seek confirmation through trusted organizational channels.
- Review relevant account activity and security alerts.
Unverified claimOriginal post on X (opens in a new tab)
Data leak
Actor claims leak of Zambia social protection registry data
A threat actor claims to have leaked data from the Zambia Integrated Social Protection Information System.
Context and what defenders can do
As general background, social protection registries may contain sensitive information and are attractive targets for data theft claims. Such claims require independent verification; this is general knowledge, not confirmation of this incident.
What defenders can do
- Review access logs and investigate unusual data transfers.
- Verify backups and restrict access to sensitive records.
Unverified claimOriginal post on X (opens in a new tab)
Hacktivism
- Sector
- Government
- Country
- ITItaly
NoName claims it targeted multiple websites in Italy
NoName claims to have targeted multiple websites in Italy, including the Federation of the Greens, Provincia di Treviso, and Municipality of Arzignano.
Context and what defenders can do
DDoS claims generally refer to attempts to disrupt the availability of online services by overwhelming them with traffic. This is general background and does not verify this claim.
What defenders can do
- Monitor service availability and traffic patterns.
- Review DDoS mitigation and escalation procedures.
Unverified claimOriginal post on X (opens in a new tab)
Data leak
Actor claims ADINA / MADINA Foundation estate database was breached
An underground-forum actor claims the ADINA / MADINA Foundation estate database was breached.
Context and what defenders can do
In general, breach claims may be posted before they are independently verified. Database exposure can create risks if systems contain sensitive information.
What defenders can do
- Review database access logs and investigate unusual activity.
- Verify backups and restrict database access.
Unverified claimOriginal post on X (opens in a new tab)
Ransomware
- Sector
- Manufacturing
- Country
- ITItaly
Actor claims Ernesto Malvestiti S.p.A. was affected by Aur0ra ransomware
The post alleges that Italy-based manufacturing company Ernesto Malvestiti S.p.A. fell victim to Aur0ra ransomware.
Context and what defenders can do
Ransomware claims commonly allege that an organization’s systems or data were compromised, but public posts may be unverified. This is general background about ransomware claims, not confirmation of this incident.
What defenders can do
- Review endpoint and network alerts for signs of intrusion.
- Verify backups are isolated and recoverable.
Unverified claimOriginal post on X (opens in a new tab)
Hacktivism
Groups announce a claimed alliance between RBL LEVIATHAN GHOST and TEAM BD CYBER NINJA
The post says RBL LEVIATHAN GHOST and TEAM BD CYBER NINJA announced an alliance.
Context and what defenders can do
Hacktivist groups may announce partnerships to signal shared objectives or amplify attention. Such announcements are general indicators of claimed coordination, not proof of joint operational capability.
What defenders can do
- Monitor relevant threat-intelligence sources for changes in activity.
- Review incident escalation and communications procedures.
Unverified claimOriginal post on X (opens in a new tab)
Data for sale
- Sector
- Retail & consumer
Actor claims DESCO customer data was leaked
A threat actor on a dark web forum is advertising what it says is a customer database from DESCO.
Context and what defenders can do
As general background, claims of data exposure on forums can be difficult to verify from posts alone. Utilities may hold customer information, making access controls and monitoring important.
What defenders can do
- Review access logs for unusual database activity.
- Verify the claim through trusted internal channels.
Unverified claimOriginal post on X (opens in a new tab)
Data for sale
- Sector
- Healthcare
- Country
- SGSingapore
Actor claims patient records from Singapore eye clinics are for sale
A threat actor claims to be selling a database containing patient records from several eye clinics in Singapore.
Context and what defenders can do
As general background, healthcare records can contain sensitive personal and medical information, making alleged sales of such data a concern. Forum listings and samples may be misleading and do not independently verify access or authenticity.
What defenders can do
- Review access to patient-record systems and monitor for unusual data transfers.
- Follow your incident-response process for suspected exposure of health information.
Unverified claimOriginal post on X (opens in a new tab)
Dark web in the news
- ENGIE Data Breach Exposes Customer Details and Energy Contracts (opens in a new tab)
- Hive and Nefilim Ransomware Affiliate Gets 70 Months In Jail (opens in a new tab)
- Summit Public Schools Breach Exposes 115 GB of Student and Staff Data (opens in a new tab)
- Scanner Poses as 32 AI Bots to Find Credentials and Private Keys (opens in a new tab)
- Fake AI Attacks Target US Firms as Researchers Warn of Corporate Credential Theft (opens in a new tab)
- n0n Ransomware: Inside an AI-Assisted Extortion Operation (opens in a new tab)
- September 2026: FBI Breach, Clop Hijack & IDScan Leak (opens in a new tab)
- PHP2Shell Weaponized After Japanese Real Estate Extortion (opens in a new tab)
- Claims written up
- 40
- Ransomware listings, 7 days
- 271
- Active groups, 7 days
- 46
- Confirmed breaches, 45 days
- 10
Ransomware tracker
Listings: RansomLook (ransomlook.io), licensed CC BY 4.0. Each listing is a claim by the group on its own leak site, not a confirmed incident. Outpost shows group names, victim names and dates only, never the screenshots or files a leak site attaches.
Most active groups
Listings in the last 7 days
Latest 20 listings
Confirmed breaches
Source: Have I Been Pwned, licensed under CC BY 4.0. Breaches added in the last 45 days; descriptions are shortened and counts are as HIBP lists them.
Assurance Retraite
lassuranceretraite.fr
Verified breach
Breached Added to HIBP
- Dates of birth
- Email addresses
- Family members' names
- Government issued IDs
- Income levels
- Marital statuses
- Names
- Phone numbers
In September 2024, the French national pension fund Assurance Retraite suffered a data breach affecting approximately 370k assistance beneficiaries.
Details on Have I Been Pwned (opens in a new tab)70,372accounts in HIBP
Gîtes de France
gites-de-france.com
Verified breach
Breached Added to HIBP
- Booking details
- Email addresses
- Names
- Phone numbers
- Physical addresses
In May 2026, the French holiday rental network Gîtes de France suffered a data breach affecting some of its departmental branches.
Details on Have I Been Pwned (opens in a new tab)117,574accounts in HIBP
Crunchbase
crunchbase.com
Verified breach
Breached Added to HIBP
- Email addresses
- Employers
- Job titles
- Names
- Phone numbers
- Physical addresses
- Social media profiles
In January 2026, the private company intelligence platform Crunchbase was targeted in a ShinyHunters "pay or leak" extortion attempt.
Details on Have I Been Pwned (opens in a new tab)559,908accounts in HIBP
Sharecare
sharecare.com
Verified breach
Breached Added to HIBP
- Dates of birth
- Email addresses
- Employers
- Genders
- Government issued IDs
- Job titles
- Marital statuses
- Names
In August 2026, the digital health company Sharecare was the target of a ShinyHunters "pay or leak" extortion campaign.
Details on Have I Been Pwned (opens in a new tab)318,185accounts in HIBP
Neogen
neogen.com
Verified breach
Breached Added to HIBP
- Email addresses
- Employers
- Job titles
- Names
- Phone numbers
- Physical addresses
- Salutations
In August 2026, the food and animal safety organisation Neogen was the target of a ShinyHunters "pay or leak" extortion attempt. The group later published data it claimed had been obtained from Neogen.
Details on Have I Been Pwned (opens in a new tab)435,963accounts in HIBP
CyrusOne
cyrusone.com
Verified breach
Breached Added to HIBP
- Email addresses
- Employers
- Job titles
- Names
- Phone numbers
- Physical addresses
- Support tickets
In August 2026, data centre operator CyrusOne was the target of a ShinyHunters "pay or leak" extortion attempt.
Details on Have I Been Pwned (opens in a new tab)373,460accounts in HIBP
Double Counter
doublecounter.gg
Verified breach
Breached Added to HIBP
- Email addresses
- Geographic locations
- Names
- Usernames
In October 2026, the Discord server protection service Double Counter suffered a data breach attributed to a vulnerability in the Metabase analytics tool.
Details on Have I Been Pwned (opens in a new tab)274,922accounts in HIBP
Angel One
angelone.in
Verified breach
Breached Added to HIBP
- Bank account numbers
- Dates of birth
- Email addresses
- Financial investments
- Government issued IDs
- Names
- Phone numbers
- Physical addresses
In July 2024, the Indian stock brokerage firm Angel One confirmed that data leaked online related to a breach that occurred in April 2023.
Details on Have I Been Pwned (opens in a new tab)6,765,054accounts in HIBP
LimeLeads
limeleads.com
Verified breach
Breached Added to HIBP
- Email addresses
- Employers
- Geographic locations
- Job titles
- Phone numbers
In 2019, the now-defunct B2B marketing leads database service LimeLeads suffered a data breach due to an exposed, unsecured Elasticsearch server.
Details on Have I Been Pwned (opens in a new tab)17,838,396accounts in HIBP
Burger King Russia
burgerkingrus.ru
Verified breach
Breached Added to HIBP
- Dates of birth
- Email addresses
- Genders
- Geographic locations
- Names
- Phone numbers
In October 2024, news of a data breach exposing Burger King Russia customers broke following an August attack on the Mindbox marketing automation platform.
Details on Have I Been Pwned (opens in a new tab)3,155,792accounts in HIBP
How this page is made
Labels
Categories, sectors, countries and sizes on the claim cards are assigned automatically by fixed keyword rules. They can be wrong, and a missing label means the rules found nothing, not that nothing exists.
Write-ups
An AI drafts each write-up from the title of the original post only. The headline and claim sentence restate what the post alleges; the context and advice are general background, not facts about the incident.
Tracker and breaches
Groups, victims and dates appear as RansomLook publishes them; we only merge spelling variants of a group name when counting. Fabricated, spam-list, stealer-log, sensitive and retired entries are left out of the breach list. See the methodology.
Keyword index
Counted from this page. Select one to filter.