 OUTPOST
Edition 222 — 24 October 2026
Cyber, warfare technology and geopolitics as compiled on 24 October 2026.
Cyber
Breaches, campaigns, advisories and research.
BlackX UEFI bootkit exploits Baton Drop flaw to bypass Secure Boot (opens the original article)
The report says the BlackX UEFI bootkit exploited the Baton Drop flaw to bypass Secure Boot and load a malicious driver in an espionage campaign.
Cyber BleepingComputer
What to checkCheck Secure Boot configurations and investigate exposure to the Baton Drop flaw and suspicious drivers.
Sources1BleepingComputer
Brotli Decoder Flaw Behind Node.js RCE Also Affects Bun, Python and Other Widely Used Software (opens the original article)
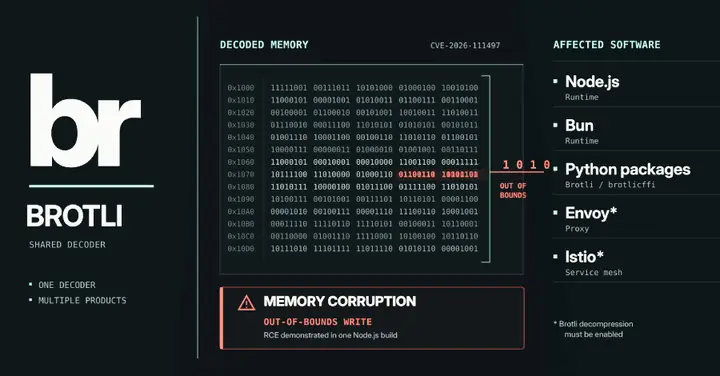
A memory-corruption flaw in Google's Brotli decoder affects software that unpacks Brotli data, including Bun, Python packages and some Envoy proxies; the title says it is behind Node.js RCE.
Cyber The Hacker News
What to checkInventory Brotli-using software and check for fixes, especially in the listed packages and proxies.
Sources1The Hacker News
Leaked LiteLLM Master Key Let Attackers Steal GitHub Tokens and Hijack Release Pipeline (opens the original article)
LiteLLM says a master key published in a public GitHub repository ultimately enabled an attacker to push a malicious version of its Python package.
Cyber The Hacker News
What to checkCheck for exposed secrets and review release-pipeline activity for unauthorized changes.
Sources1The Hacker News
Google Says Gmail and Photos Data Shared With AI Search Could Be Used for Targeted Ads (opens the original article)
Google says personalized AI features in Search or Gemini may allow targeted ads based on activity across connected Google services.
Cyber The Hacker News
What to checkReview connected-service settings and explain how AI feature use may affect ad personalization.
Sources1The Hacker News
Researchers Push Over 2 Million Updates to Remotely Disable Popcorn Time Updater That Could Fuel a Botnet (opens the original article)
Eye Security says it pushed more than 2 million updates to computers it did not own to disable a Popcorn Time updater it said could let an outsider take over a machine.
Cyber The Hacker News
What to checkCheck for the updater and assess whether affected systems received the disabling updates.
Sources1The Hacker News
CISA Adds One Known Exploited Vulnerability to Catalog (opens the original article)
CISA says it added one vulnerability to its Known Exploited Vulnerabilities Catalog based on evidence of active exploitation.
Cyber CISA Advisories
What to checkCheck whether affected systems are present in your environment and prioritize remediation.
Sources1CISA Advisories
CISA Adds One Known Exploited Vulnerability to Catalog (opens the original article)
CISA added one vulnerability to its Known Exploited Vulnerabilities Catalog, citing evidence of active exploitation.
Cyber CISA Advisories
What to checkCheck the KEV Catalog and prioritize remediation for affected systems.
Sources1CISA Advisories
CISA Flags Two Actively Exploited Critical Flaws in Collabora Online and Arista VeloCloud (opens the original article)
CISA added vulnerabilities affecting Collabora Online Built-in CODE Server and Arista VeloCloud Orchestrator to its Known Exploited Vulnerabilities catalog, citing reports of active exploitation.
Cyber The Hacker News
What to checkCheck whether these products are in use and prioritize reviewing and addressing the listed vulnerabilities.
Sources1The Hacker News
Threat Brief: Critical Vulnerabilities in PHP: CVE-2026-109618, CVE-2026-109619 (Updated October 23) (opens the original article)
Unit 42 identifies CVE-2026-109618 and CVE-2026-109619 as critical PHP vulnerabilities affecting software used for web servers and CMS systems.
Cyber Unit 42
What to checkCheck PHP-based web servers and CMS systems for exposure and patches.
Sources1Unit 42
Abandoned Popcorn Time app exposed millions of devices to RCE attacks (opens the original article)
Researchers remotely disabled a vulnerable updater in the abandoned Time4Popcorn app, closing a flaw that could have allowed attackers to execute malicious code with elevated privileges.
Cyber BleepingComputer
What to checkCheck for the abandoned app and vulnerable updater; remove or isolate affected installations.
Sources1BleepingComputer
Warfare
Drones, electronic warfare, missiles and defence systems.
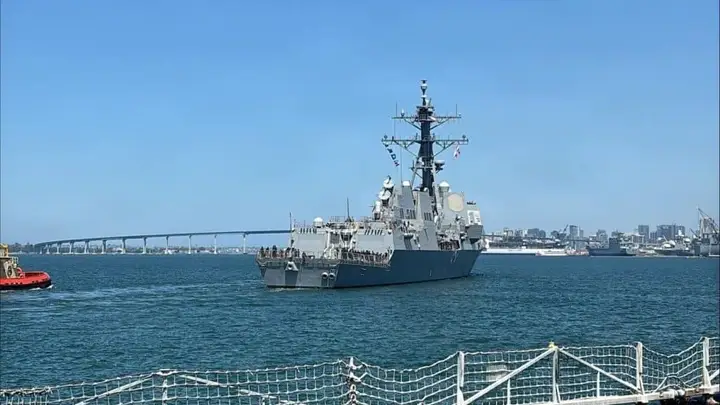
First U.S. Navy Destroyer Enters Phase Two of DDG MOD 2.0 Modernization (opens the original article)
Naval News says USS Pinckney is the first U.S. Navy destroyer in Phase Two of DDG MOD 2.0, adding SPY-6 radars.
Warfare Naval News
Why it mattersThe radar addition is relevant to how destroyers are being modernized to counter threats.
Sources1Naval News
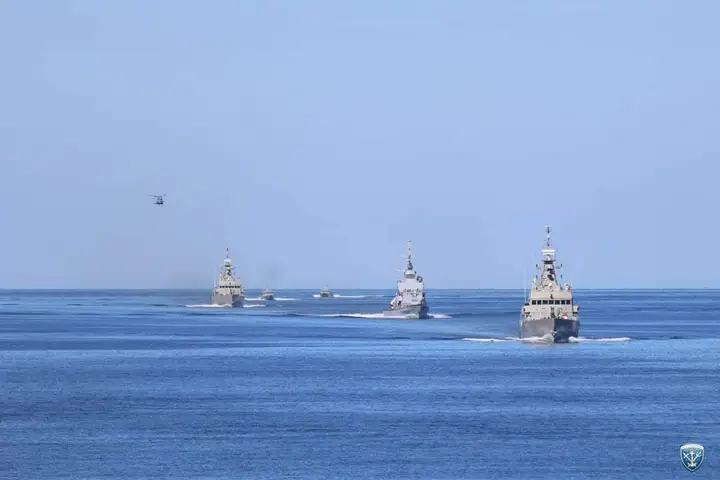
Hellenic Navy Conducts Inaugural SPIKE Missile Firings During Joint Drills with Israel (opens the original article)
Greece and Israel tested SPIKE NLOS and ER2 missile systems during Hellenic Navy live-fire drills in the Cretan Sea, sinking a decommissioned frigate.
Warfare Naval News
Why it mattersThe drills highlight missile-system testing in a joint naval exercise.
Sources1Naval News
Bunker Talk: Let’s Talk About All The Things We Did And Didn’t Cover This Week (opens the original article)
The War Zone’s Bunker Talk post invites discussion of topics covered and not covered during the week.
Warfare The War Zone
Why it mattersIt offers a broad entry point to military topics, but the snippet gives no specific technology or operation.
Sources1The War Zone
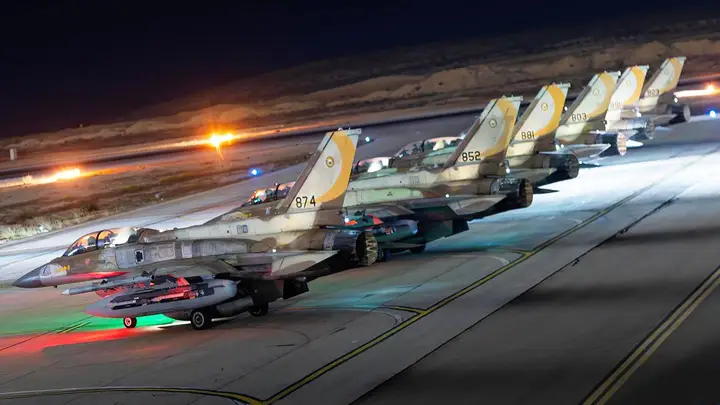
On The Brink Of Epic Fury Round Two? (opens the original article)
The War Zone says Israeli Air Force operations, ship movements and messaging point to the possibility that war with Iran could erupt again.
Warfare The War Zone
Why it mattersMilitary operations and ship movements are indicators analysts may monitor for changes in regional activity.
Sources1The War Zone
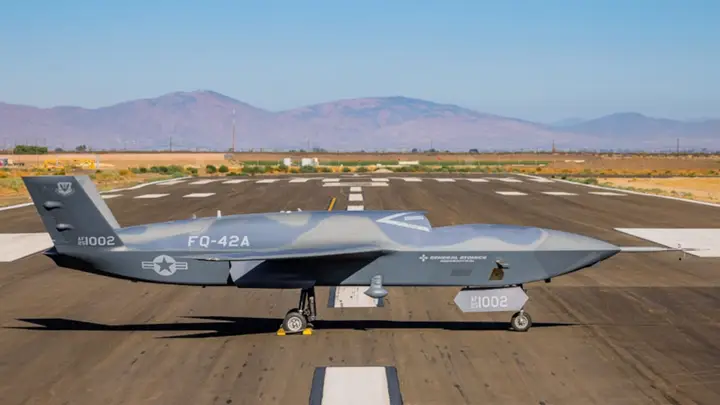
General Atomics FQ-42 CCA Drone Production Ramp Up To Be Boosted By Boeing Subsidiary (opens the original article)
General Atomics is working with Spirit Defense to help meet USAF demand for FQ-42 fighter drones within the next six years.
Warfare The War Zone
Why it mattersThe partnership is relevant to fighter-drone production capacity and military procurement.
Sources1The War Zone
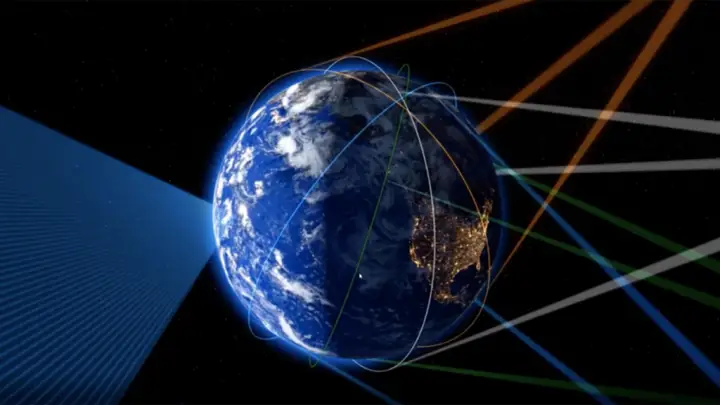
Space Force reveals first 6 ‘operational’ contracts for civil reserve support in space monitoring (opens the original article)
Space Systems Command officials say six initial contracts support the Commercial Augmentation Space Reserve initiative; unresolved issues include service denial rights and reimbursement for lost satellites.
Warfare Breaking Defense
Why it mattersThe contracts concern commercial support for space monitoring and the terms governing that support.
Sources1Breaking Defense
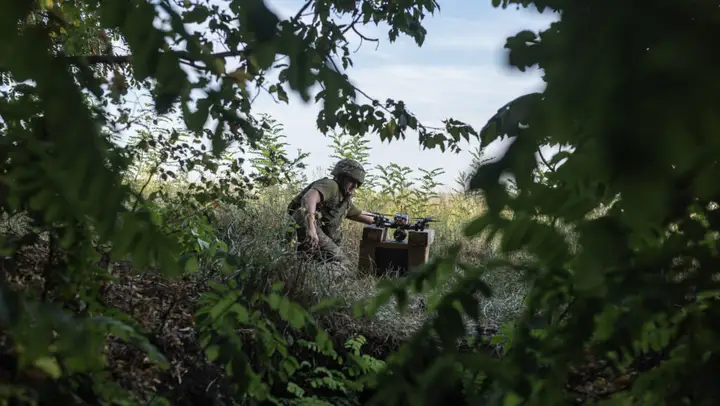
Kyiv eyes purchase of planned ICEYE, Nokia ‘sovereign’ communication sats (opens the original article)
Kyiv is considering planned ICEYE and Nokia sovereign communication satellites, according to the report, amid concerns over access to Starshield.
Warfare Breaking Defense
Why it mattersThe proposal highlights the operational importance of resilient satellite communications.
Sources1Breaking Defense
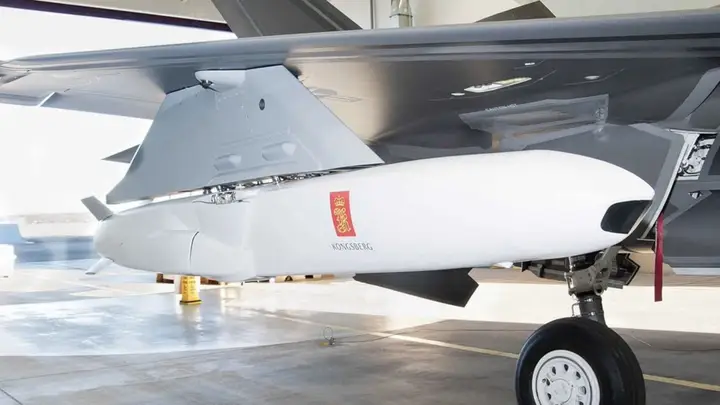
Denmark To Buy Anthem Munitions, Joint Strike Missiles In Dual Long-Range Strike Push (opens the original article)
The War Zone reports Denmark plans to buy ground- and air-launched Anthem Munitions and Joint Strike Missiles for long-range strike options.
Warfare The War Zone
Why it mattersThe weapons add ground- and air-launched options for striking deep behind enemy lines.
Sources1The War Zone
Geopolitics & geodata
Strategy, geo wars, GNSS and satellite security.
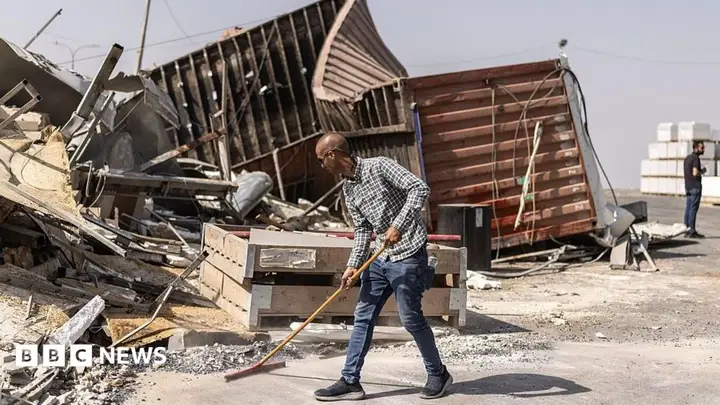
Palestinian families displaced as Israeli forces demolish Hebron homes (opens the original article)
BBC World reports that Israeli forces demolished Hebron homes, displacing Palestinian families. The crackdown follows the killing of two Israeli soldiers and comes days before Israel's election.
Geopolitics BBC World
Strategic relevanceTrack displacement and security measures in Hebron alongside the reported political timing.
Sources1BBC World
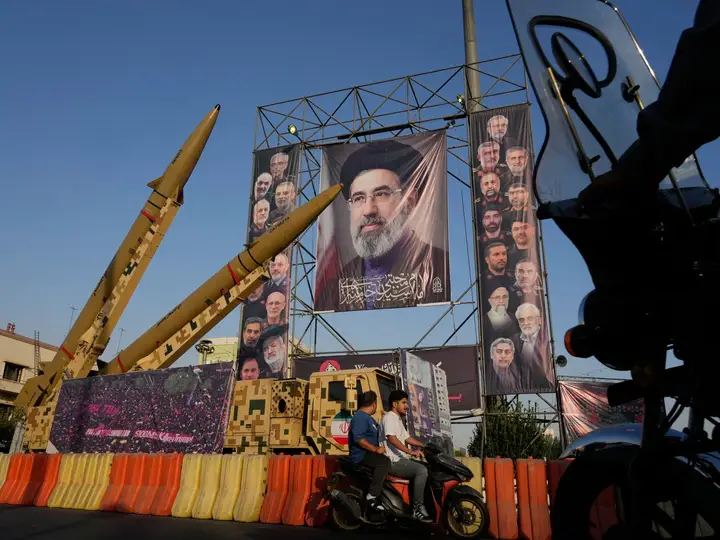
Iran blames US for deal failure, urges new try amid fear of new attacks (opens the original article)
Tehran blames the US for the deal’s failure and urges another attempt, warning that even limited strikes would draw a response several times greater.
Geopolitics Al Jazeera
Strategic relevanceThe warning is relevant to assessing regional tensions and the risks surrounding renewed negotiations.
Sources1Al Jazeera
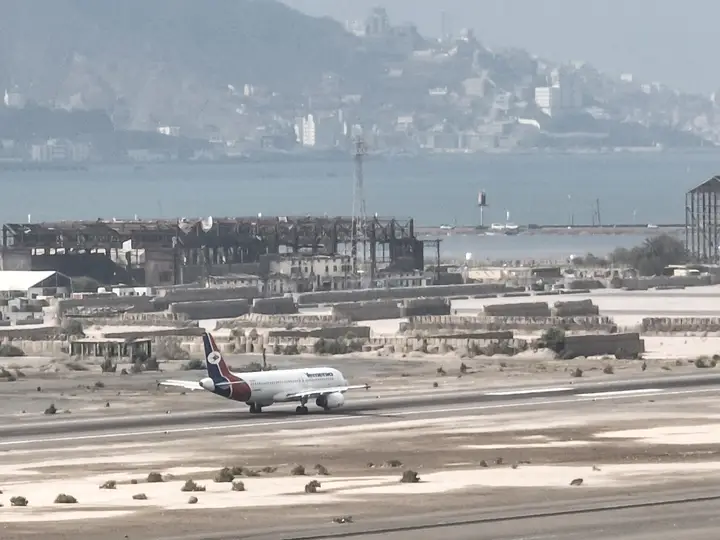
Houthis launch attacks on Saudi Arabia and Yemen’s Aden (opens the original article)
Missiles reportedly struck targets in Yemen, including Aden’s airport and a coastguard base, amid Houthi attacks on Saudi Arabia and Yemen.
Geopolitics Al Jazeera
Strategic relevanceReported strikes on an airport and coastguard base highlight the operational relevance of those sites.
Sources1Al Jazeera
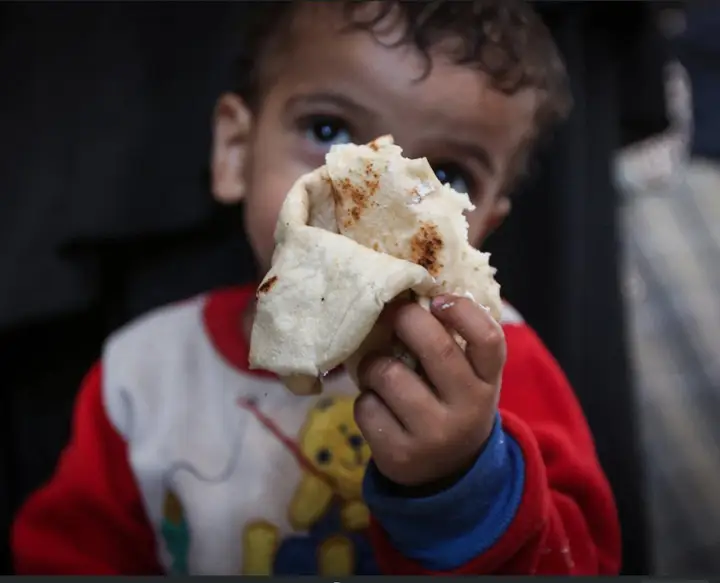
Severe hunger stalks people in Gaza as bakeries close down (opens the original article)
Bakeries across Gaza are struggling to find flour as people face severe hunger and lack bread.
Geopolitics Al Jazeera
Strategic relevanceFlour shortages and bakery closures indicate pressure on food access in Gaza.
Sources1Al Jazeera
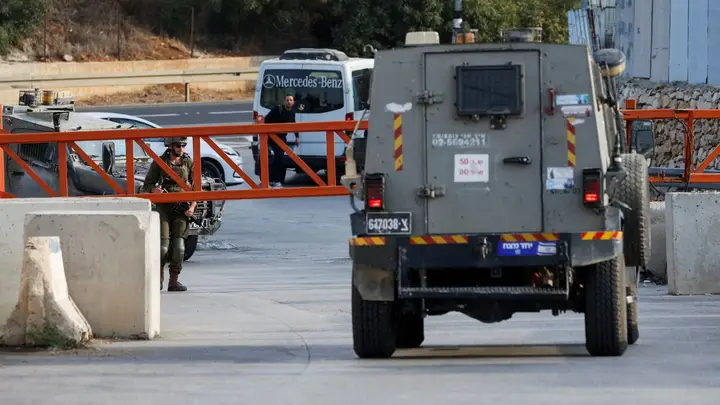
Could Israel’s military crackdown influence Tuesday’s election? (opens the original article)
Israel is preparing a full lockdown of the occupied West Bank after a gunfight in Hebron.
Geopolitics Al Jazeera
Strategic relevanceA possible lockdown is relevant to movement and access across the West Bank.
Sources1Al Jazeera
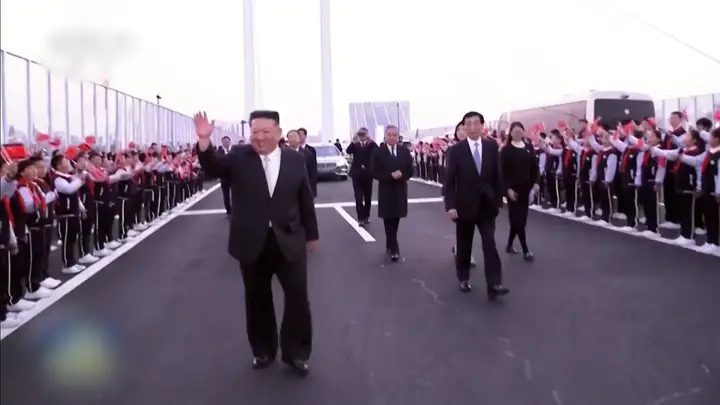
Kim Jong Un crosses new bridge linking North Korea and China (opens the original article)
Al Jazeera reports that Kim Jong Un crossed a new bridge linking North Korea and China.
Geopolitics Al Jazeera
Strategic relevanceThe bridge is a cross-border connection with potential strategic and geospatial relevance.
Sources1Al Jazeera
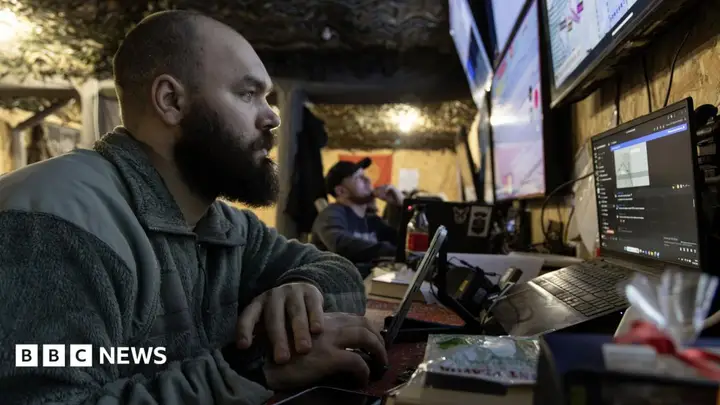
Ukraine says Starlink connection 'now stable' after network limits (opens the original article)
BBC World reports that slowed Starlink connections affected Ukraine's military and drone operations for a week; Ukraine says the connection is now stable.
Geopolitics BBC World
Strategic relevanceThe report highlights the operational importance of satellite connectivity to military and drone activity.
Sources1BBC World
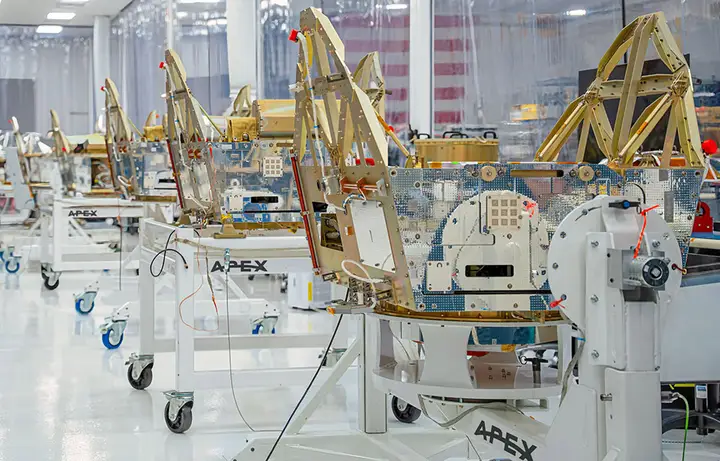
Satellite Bus Maker Apex in Talks to Raise $500M at $4B Valuation (opens the original article)
SatNews reports that satellite bus manufacturer Apex entered discussions to raise approximately $500 million at a roughly $4 billion valuation.
Geopolitics SatNews
Strategic relevanceThe talks are relevant to the satellite manufacturing sector and its financing.
Sources1SatNews
| CVE | CVSS | Product | Ransomware | Added / due | Required action |
|---|---|---|---|---|---|
| CVE-2026-114625 | 9.4Critical | Arista VeloCloud Orchestrator | None known | Added Due | Apply mitigations in accordance with vendor instructions. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage |
| CVE-2026-110447 | 9.2Critical | Collabora Collabora Online – Built-in CODE Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage |
| CVE-2026-106931 | 8.5High | EG Secure Solutions SiteGuard Server Edition | None known | Added Due | Apply mitigations in accordance with vendor instructions. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage |
| CVE-2026-96656 | 8.6High | Plex Media Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage |
| CVE-2026-96655 | 5.3Medium | Plex Media Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage |
| CVE-2026-96654 | 6.9Medium | Plex Media Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage |
| CVE-2026-96652 | 5.3Medium | Plex Media Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage |
| CVE-2026-110936 | 8.4High | Siemens Software Center | None known | Added Due | Apply mitigations in accordance with vendor instructions. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage |
| CVE-2026-102764 | 9.3Critical | BeyondTrust Remote Support | None known | Added Due | Apply mitigations in accordance with vendor instructions. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage |
| CVE-2025-61624 | 6.0Medium | Fortinet Multiple Products | None known | Added Due | Apply mitigations in accordance with vendor instructions. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage |
| CVE-2026-21589 | 9.3Critical | Atlassian Multiple Products | None known | Added Due | Apply mitigations in accordance with vendor instructions. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage |
| CVE-2026-105134 | 9.3Critical | Ahsay AhsayCBS | None known | Added Due | Apply mitigations in accordance with vendor instructions. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage |
Source: CISA KEV catalogue; CVSS scores from NVD where published. “No score” means NVD has not scored it yet.
Keyword index
Counted from this page. Select one to filter.