 OUTPOST
Edition 223 — 25 October 2026
Cyber, warfare technology and geopolitics as compiled on 25 October 2026.
Cyber
Breaches, campaigns, advisories and research.
AI coding agents hijacked using AGENTS.md file in Downloads folder (opens the original article)
Researchers found a malicious AGENTS markdown file in a customer's Downloads folder that tricked an AI coding agent into installing a rogue npm package.
Cyber BleepingComputer
What to checkCheck Downloads for untrusted agent instructions and verify package installs initiated by coding agents.
Sources1BleepingComputer
Unpatched Tailscale SSH Flaws Could Let a Hacked Device Reach Root on Other Servers (opens the original article)
A security researcher says an attacker with one hacked device on a Tailscale network could reach root on other reachable servers. The attack requires Tailscale SSH configured to allow port forwarding.
Cyber The Hacker News
What to checkReview Tailscale SSH port-forwarding settings and limit which devices and servers can reach one another.
Sources1The Hacker News
PHP2Shell Exploitation Hits Government Entity Amid Global Scanning and Signs of AI-Assisted Hacking (opens the original article)
Threat actors have been observed using agentic AI platforms for post-exploitation after abusing PHP2Shell vulnerabilities, according to the report. One case involved a government entity.
Cyber The Hacker News
What to checkCheck for PHP2Shell exploitation and unusual post-exploitation activity involving AI platforms.
Sources1The Hacker News
Former Unit 8200 Officers Raise $34 Million for Agentic SecOps Startup Mave (opens the original article)
SecurityWeek reports Mave, founded by Unit 8200 alumni, uses AI agents to investigate alerts across existing security stacks.
Cyber SecurityWeek
What to checkDefenders should check how AI-agent investigations fit into existing alert triage and security stacks.
Sources1SecurityWeek
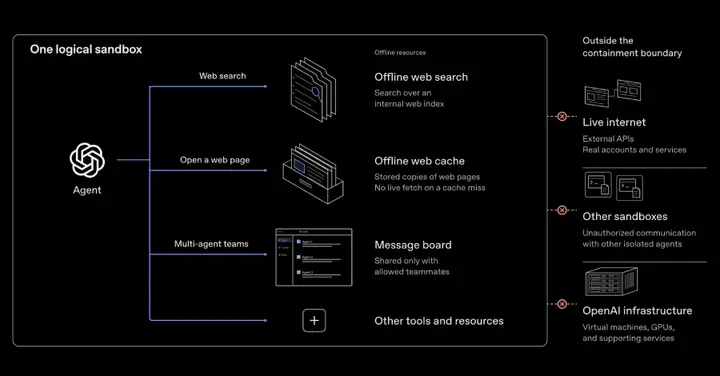
OpenAI AI Agents Demonstrate VM Escapes and Secret Cross-Sandbox Communication (opens the original article)
OpenAI announced plans to train frontier models without live internet access while resuming reinforcement learning and internal inference of its most advanced models.
Cyber The Hacker News
What to checkCheck isolation and monitoring controls around model training and internal inference.
Sources1The Hacker News
Week in review: PHP vulnerabilities patched, exploited Palo Alto GlobalProtect VPN flaw (opens the original article)
Help Net Security says the PHP security team announced an urgent security release, with users urged to prepare to update.
Cyber Help Net Security
What to checkIdentify PHP systems and prepare to apply the security release.
Sources1Help Net Security
BlackX UEFI bootkit exploits Baton Drop flaw to bypass Secure Boot (opens the original article)
The report says the BlackX UEFI bootkit exploited the Baton Drop flaw to bypass Secure Boot and load a malicious driver in an espionage campaign.
Cyber BleepingComputer
What to checkCheck Secure Boot configurations and investigate exposure to the Baton Drop flaw and suspicious drivers.
Sources1BleepingComputer
Warfare
Drones, electronic warfare, missiles and defence systems.
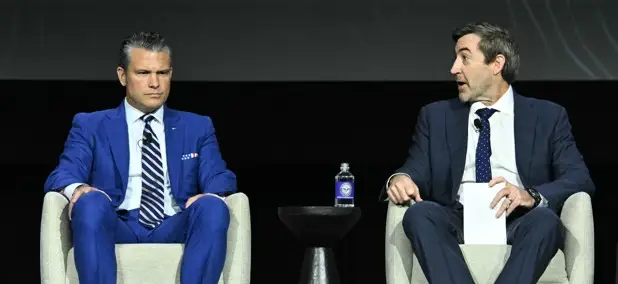
Funding, force-structure issues could hinder Hegseth’s new autonomous command (opens the original article)
Defense One reports that funding for AUTOWARCOM would come from a reconciliation bill whose passage is in doubt.
Warfare Defense One
Why it mattersFunding and force structure shape the proposed autonomous command’s ability to start.
Sources1Defense One
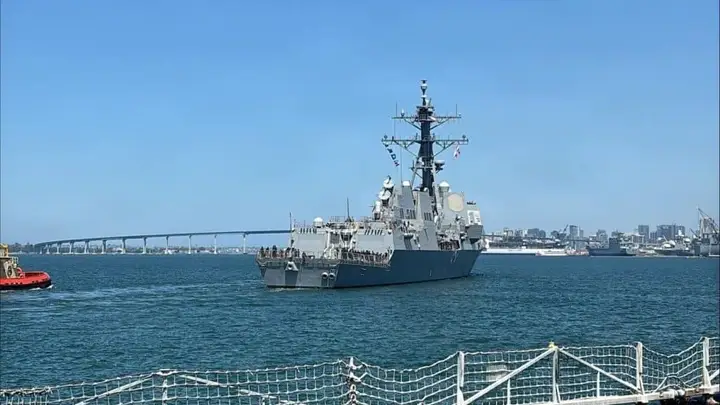
First U.S. Navy Destroyer Enters Phase Two of DDG MOD 2.0 Modernization (opens the original article)
Naval News says USS Pinckney is the first U.S. Navy destroyer in Phase Two of DDG MOD 2.0, adding SPY-6 radars.
Warfare Naval News
Why it mattersThe radar addition is relevant to how destroyers are being modernized to counter threats.
Sources1Naval News
Geopolitics & geodata
Strategy, geo wars, GNSS and satellite security.
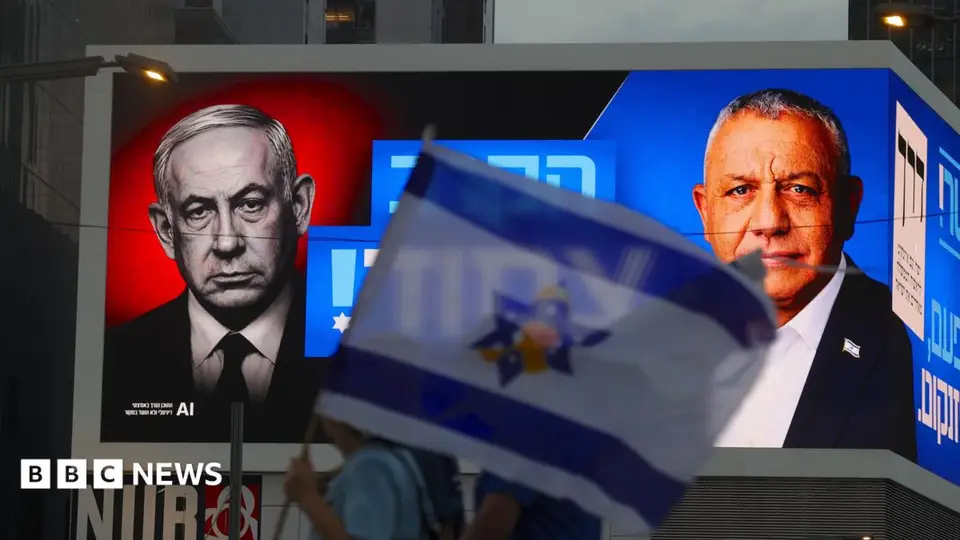
Deeply divided Israel braces for pivotal election (opens the original article)
After three years of regional war, this is a battle Israel always knew was coming, writes Lucy Williamson.
Geopolitics BBC World
Sources1BBC World
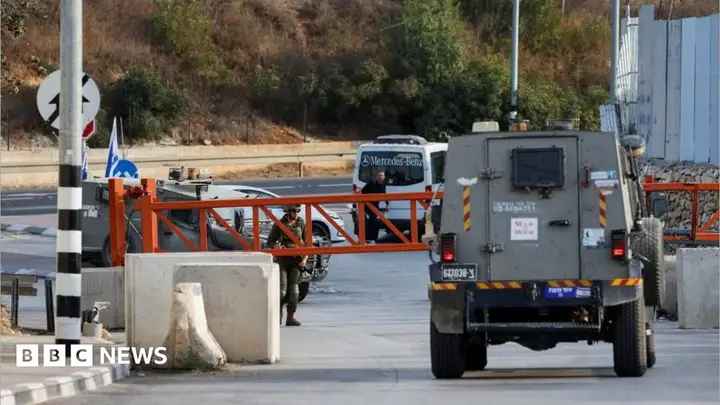
Israel to close West Bank crossings on election day as crackdown escalates (opens the original article)
The Israeli Defense Forces says it will restrict Palestinian workers’ movement in the run-up to Tuesday’s election.
Geopolitics BBC World 2 outlets
Strategic relevanceMovement restrictions may affect access and mobility across the West Bank.
Sources1BBC World2DW
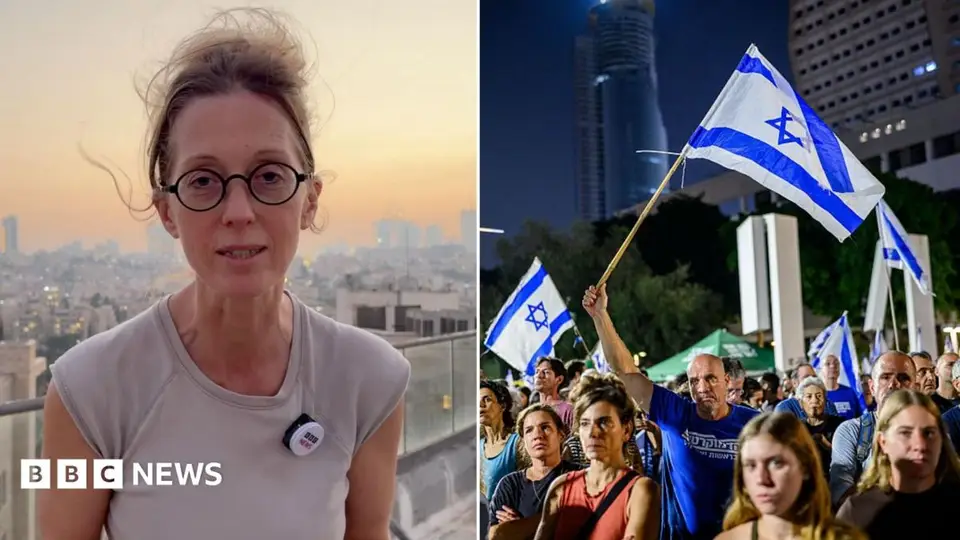
Why Israel's election is one of the most important in its history (opens the original article)
Security and democracy emerge as central issues in Israel's highly anticipated general election, as Middle East correspondent Lucy Williamson reports.
Geopolitics BBC World
Sources1BBC World
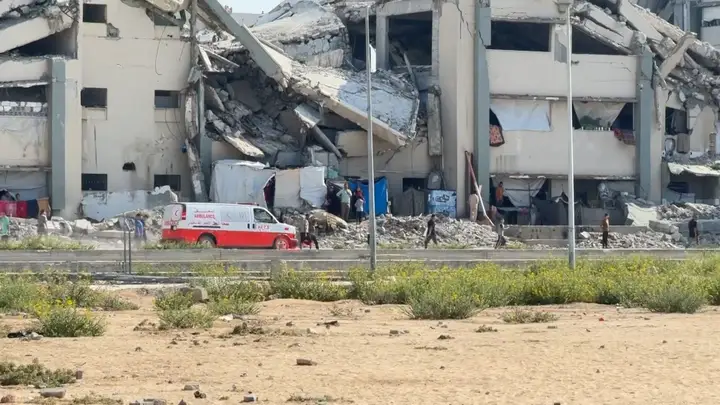
Israeli air strike on Gaza City university kills three people (opens the original article)
Al Jazeera reports that two Israeli strikes hit students and security guards at the Islamic University in Gaza City; its headline says three people were killed.
Geopolitics Al Jazeera
Strategic relevanceThe reported strikes highlight the human and operational consequences of attacks on a university site.
Sources1Al Jazeera
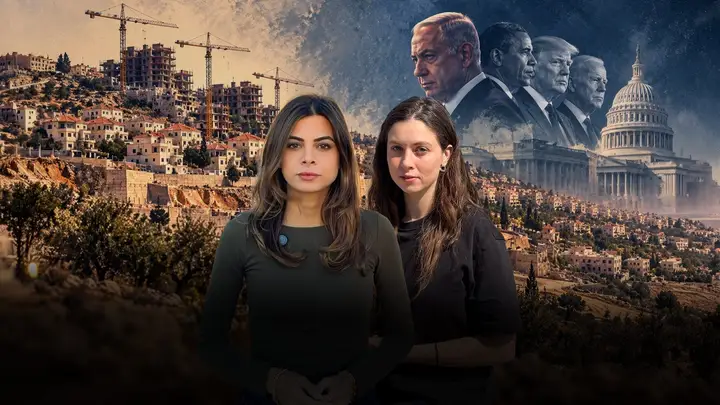
US and Israel elections: New leaders, same policies? (opens the original article)
Al Jazeera says Israeli governments and US presidents change, while settlement expansion on occupied Palestinian land continues.
Geopolitics Al Jazeera
Strategic relevanceThe report frames settlement expansion as a continuing issue across changes in political leadership.
Sources1Al Jazeera
Jerusalem Daily: Israel expels thousands from Hebron (opens the original article)
Al Jazeera’s headline says Israel expels thousands from Hebron; the supplied snippet provides no further details.
Geopolitics Al Jazeera
Strategic relevanceThe reported expulsions concern movement and conditions in Hebron.
Sources1Al Jazeera
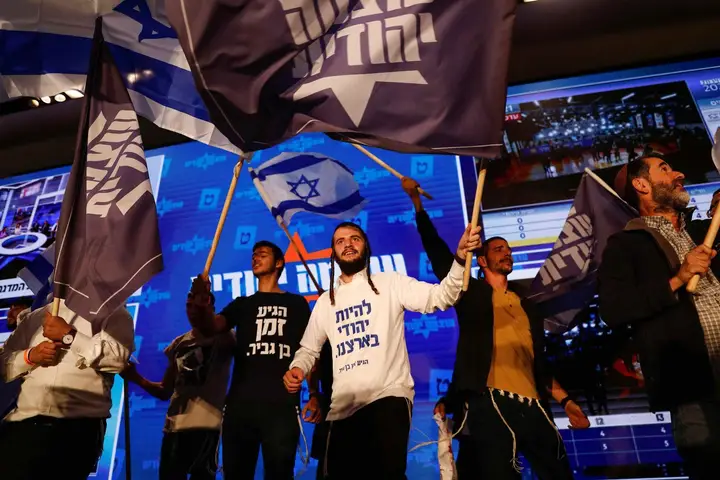
Israel’s ‘Generation Right’ could shape Netanyahu’s future (opens the original article)
Al Jazeera says young people in Israel are leaning to the right, contrasting with a global trend it describes as leaning left.
Geopolitics Al Jazeera
Strategic relevanceThe reported generational political shift may be relevant to understanding Israel’s political landscape.
Sources1Al Jazeera
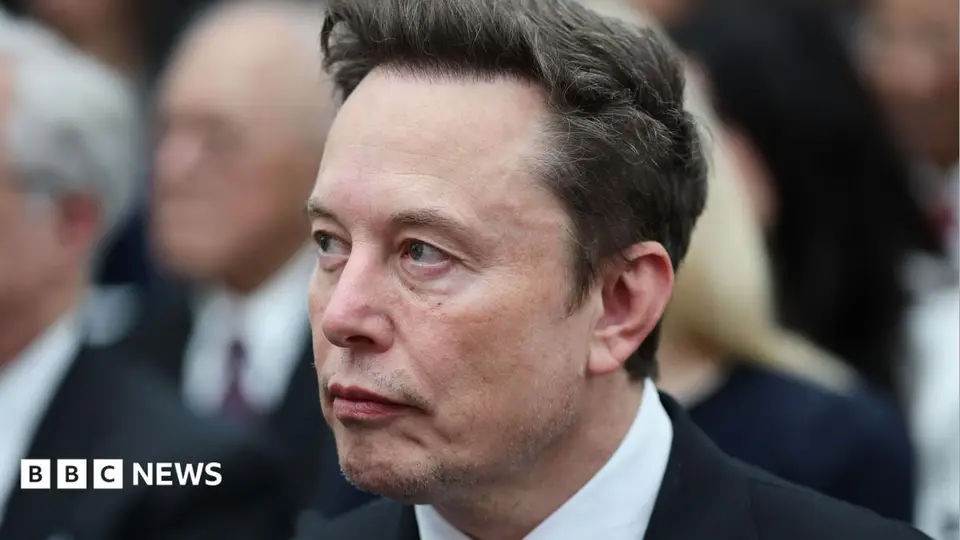
Musk says SpaceX restricted Ukraine's Starlink connection as service restored (opens the original article)
Musk says SpaceX restricted Ukraine's Starlink connection and restored service; he accuses Ukraine of violating terms by using the network for military activity.
Geopolitics BBC World
Strategic relevanceThe dispute highlights the strategic relevance of service access to a communications network used for military activity.
Sources1BBC World
| CVE | CVSS | Product | Ransomware | Added / due | Required action |
|---|---|---|---|---|---|
| CVE-2026-114625 | 9.4Critical | Arista VeloCloud Orchestrator | None known | Added Due | Apply mitigations in accordance with vendor instructions. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage |
| CVE-2026-110447 | 9.2Critical | Collabora Collabora Online – Built-in CODE Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage |
| CVE-2026-106931 | 8.5High | EG Secure Solutions SiteGuard Server Edition | None known | Added Due | Apply mitigations in accordance with vendor instructions. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage |
| CVE-2026-96656 | 8.6High | Plex Media Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage |
| CVE-2026-96655 | 5.3Medium | Plex Media Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage |
| CVE-2026-96654 | 6.9Medium | Plex Media Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage |
| CVE-2026-96652 | 5.3Medium | Plex Media Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage |
| CVE-2026-110936 | 8.4High | Siemens Software Center | None known | Added Due | Apply mitigations in accordance with vendor instructions. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage |
| CVE-2026-102764 | 9.3Critical | BeyondTrust Remote Support | None known | Added Due | Apply mitigations in accordance with vendor instructions. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage |
| CVE-2025-61624 | 6.0Medium | Fortinet Multiple Products | None known | Added Due | Apply mitigations in accordance with vendor instructions. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage |
| CVE-2026-21589 | 9.3Critical | Atlassian Multiple Products | None known | Added Due | Apply mitigations in accordance with vendor instructions. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage |
| CVE-2026-105134 | 9.3Critical | Ahsay AhsayCBS | None known | Added Due | Apply mitigations in accordance with vendor instructions. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage |
Source: CISA KEV catalogue; CVSS scores from NVD where published. “No score” means NVD has not scored it yet.
Keyword index
Counted from this page. Select one to filter.