 OUTPOST
Edition 224 — 26 October 2026
Cyber, warfare technology and geopolitics as compiled on 26 October 2026.
Cyber
Breaches, campaigns, advisories and research.
CISA Adds Two Known Exploited Vulnerability to Catalog (opens the original article)
<div class="OutlineElement Ltr SCXW42064574 BCX8"> <p class="text-align-justify">CISA has added two new vulnerabilities to its <a class="Hyperlink SCXW42064574 BCX8" href="https://www.cisa.gov/known-exploited-vulnerabili
Cyber CISA Advisories
Sources1CISA Advisories
University of Copenhagen data breach exposes data of 525,000 people (opens the original article)
The University of Copenhagen confirmed hackers accessed a test environment containing personal data belonging to 525,000 people.
Cyber BleepingComputer
What to checkCheck access controls and personal data exposure in test environments.
Sources1BleepingComputer
Former pentester used ARTEX AI to steal 8.2 million data records (opens the original article)
South Korean police identified seven suspects linked to breaches of more than 90 organizations; they say the ARTEX AI pentesting framework was used in most attacks.
Cyber BleepingComputer
What to checkCheck for unauthorized use of pentesting tools and review access and data-export logs.
Sources1BleepingComputer
Texas sues OpenAI for deceiving consumers about safety, seeks sweeping reforms and fines (opens the original article)
Texas’s suit alleges OpenAI deceived consumers about safety and seeks reforms and fines; it also seeks to hold Sam Altman personally liable.
Cyber The Record
What to checkReview how AI safety claims are documented, communicated, and assessed.
Sources1The Record
OpenAI launches GPT-6.1 Terra with 3x faster AI agents, 50% lower pricing (opens the original article)
OpenAI says GPT-6.1 Terra focuses on computer use, visual reasoning, coding, and everyday work, at lower cost than its larger models.
Cyber BleepingComputer
What to checkAssess permissions and oversight before deploying AI agents for computer-based tasks.
Sources1BleepingComputer
DreamHost forces password resets in ongoing "incident" (opens the original article)
DreamHost forced email and FTP/SFTP users to reset passwords after an incident disrupted File Manager connections.
Cyber BleepingComputer
What to checkConfirm affected account passwords have been reset and check for unauthorized account activity.
Sources1BleepingComputer
Serbian autocrat loses election following widespread reports of digital repression (opens the original article)
The Record reports that Serbia’s Aleksandar Vučić admitted defeat following incidents of digital repression that galvanized the opposition.
Cyber The Record
What to checkTrack how reported digital repression intersects with political events and public response.
Sources1The Record
Ukraine disputes Musk's claims of Starlink misuse as military connectivity restored (opens the original article)
Ukraine’s defense minister said Starlink and Starshield connectivity had been restored, as Ukraine disputed Musk’s claims of misuse.
Cyber The Record
What to checkConsider the operational importance of connectivity restoration and disputed claims about service use.
Sources1The Record
Dutch police extradite Chinese national accused of laundering Cambodian investment scam funds (opens the original article)
Dutch police extradited a Chinese national accused of laundering funds for a Cambodian investment scam. The report says scammers urged U.S.-based victims to invest in fictitious businesses.
Cyber The Record
What to checkReview scam reporting and financial-risk checks for investment offers involving fictitious businesses.
Sources1The Record
Critical 'HTTP2Shell' Brotli vulnerability triggers emergency patches (opens the original article)
The report says a critical flaw in Brotli, a C decoder library built into Node.js, could let attackers corrupt memory and access sensitive data; emergency patches have been triggered.
Cyber BleepingComputer
What to checkCheck whether Brotli or Node.js components are affected and apply relevant patches.
Sources1BleepingComputer
Warfare
Drones, electronic warfare, missiles and defence systems.
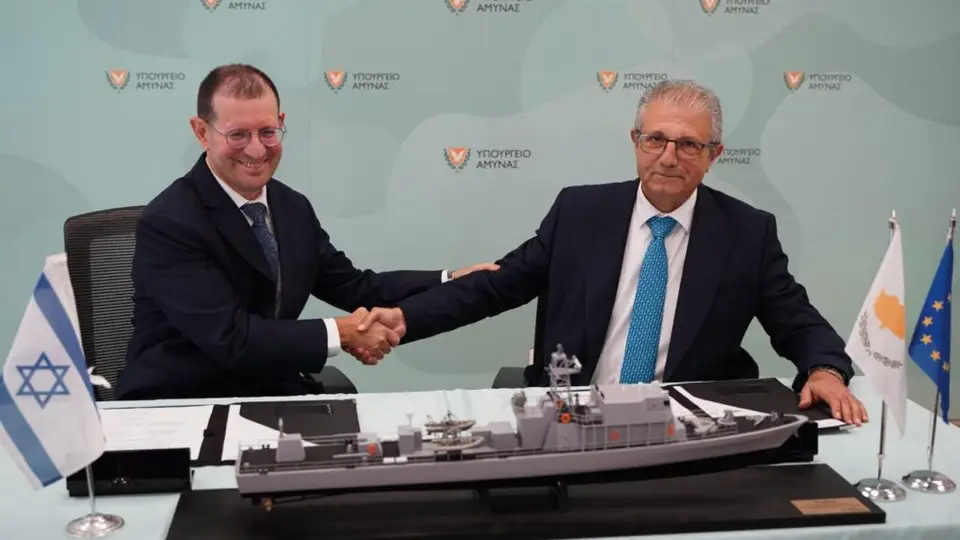
Cyprus to acquire new offshore patrol vessel with ‘advanced’ naval systems from Israel (opens the original article)
Israel’s Ministry of Defense says Israel Shipyards will build Cyprus’s new patrol vessel for expanded patrol, surveillance, and search-and-rescue missions.
Warfare Breaking Defense 2 outlets
Why it mattersThe vessel’s stated mission set links maritime surveillance with patrol and rescue operations.
Sources1Breaking Defense2Naval News
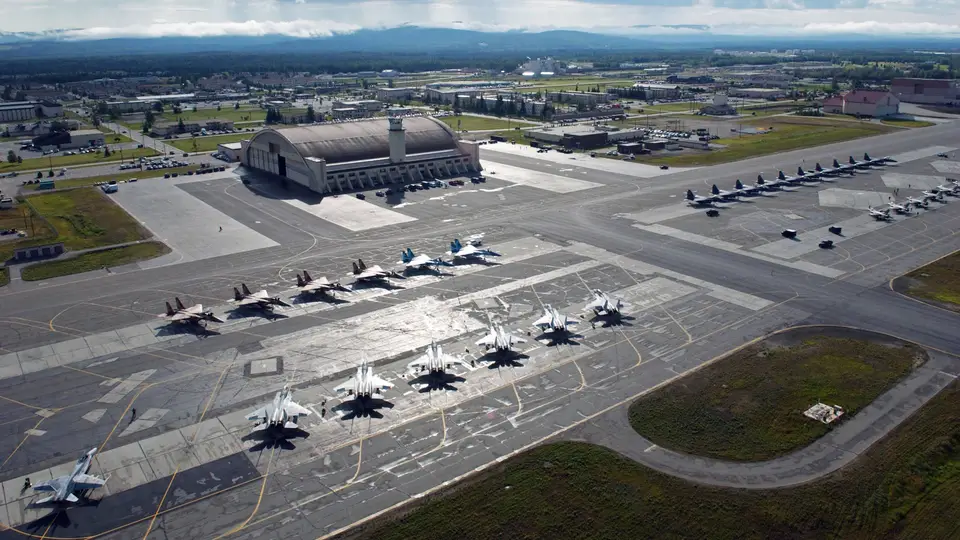
90 Days No Help: Fortress America’s Goal To Make Bases Resilient Bastions In A Crisis (opens the original article)
The War Zone reports concerns that cyber threats to critical infrastructure could affect U.S. military units before they leave their garrisons.
Warfare The War Zone
Why it mattersHighlights the operational importance of resilient military bases and critical infrastructure.
Sources1The War Zone
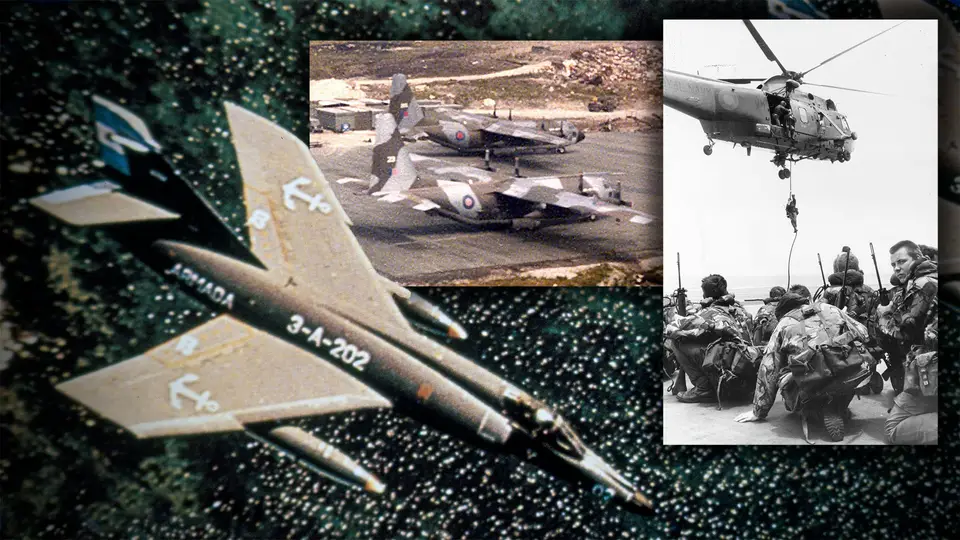
Britain’s Final Plan To Kill Argentina’s Super Étendards Attack Jets (opens the original article)
The War Zone describes Britain’s last bid during the Falklands War to destroy Argentina’s fleet of Exocet-armed Super Étendard combat jets.
Warfare The War Zone
Why it mattersThe account highlights the operational challenge posed by anti-ship missile-armed aircraft.
Sources1The War Zone
Tensions Rise (opens the original article)
The Adversarial describes increasing indications of a return to direct hostilities involving Iran.
Warfare War on the Rocks
Why it mattersThe report frames regional tensions as relevant to analysis of potential direct hostilities.
Sources1War on the Rocks
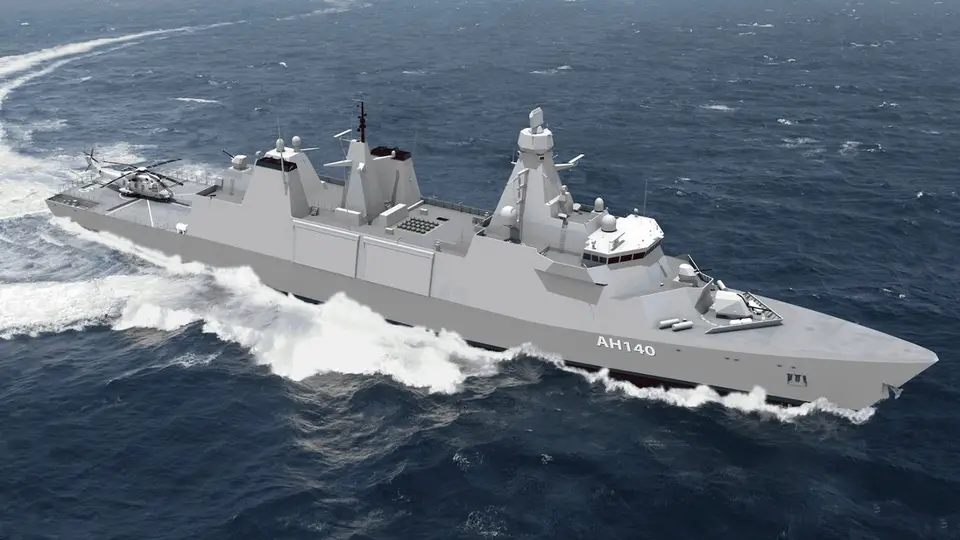
British Type 31 Frigate Variant Offered To The U.S. Navy (opens the original article)
Babcock is seeking to pitch its Arrowhead 140 design for a U.S. Navy frigate requirement, potentially with a U.S. shipbuilder.
Warfare The War Zone
Why it mattersThe proposal shows a frigate design being offered for a U.S. Navy requirement.
Sources1The War Zone
Are Critiques of Zelensky a Side Effect of Societal Exhaustion? (opens the original article)
War on the Rocks presents Ukrainian commentary and analysis, including the question of whether critiques of Zelensky reflect societal exhaustion.
Warfare War on the Rocks
Why it mattersThe question highlights political commentary as a lens on societal attitudes.
Sources1War on the Rocks
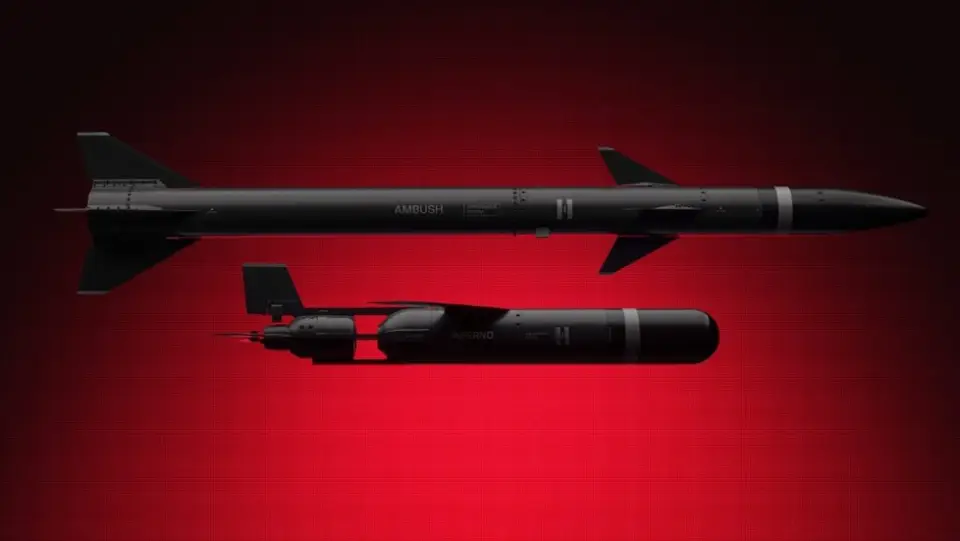
Helsing rolls out Contra air defense design, plus two new inteceptors (opens the original article)
Helsing claims its Contra air defense system can track and engage hundreds or thousands of drone and missile threats simultaneously.
Warfare Breaking Defense
Why it mattersThe claimed ability to handle many threats at once is relevant to air-defense capacity.
Sources1Breaking Defense
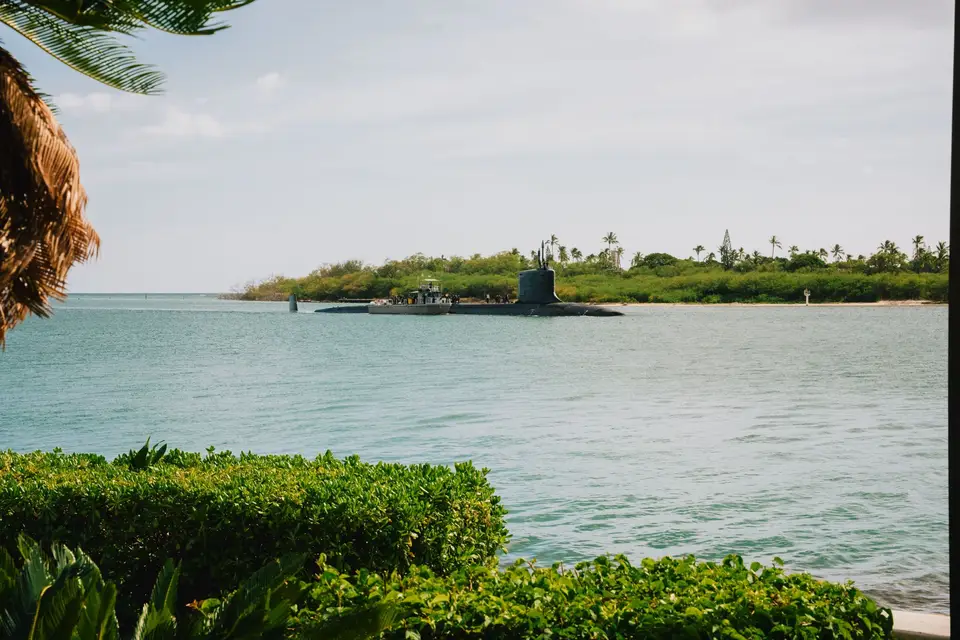
AUKUS: USS Colorado Announced as First Submarine for SRF – West (opens the original article)
Naval News reports the USS Colorado was announced as the first submarine for SRF – West.
Warfare Naval News
Why it mattersThe submarine designation is relevant to naval force planning.
Sources1Naval News
Geopolitics & geodata
Strategy, geo wars, GNSS and satellite security.
Some reasons for hope in Israel’s sharply divided election (opens the original article)
The Atlantic Council says the end of campaigning in Israel could open chances for diplomacy that were previously closed, regardless of the election outcome.
Geopolitics Atlantic Council
Strategic relevanceThe election’s aftermath may affect opportunities for diplomacy.
Sources1Atlantic Council
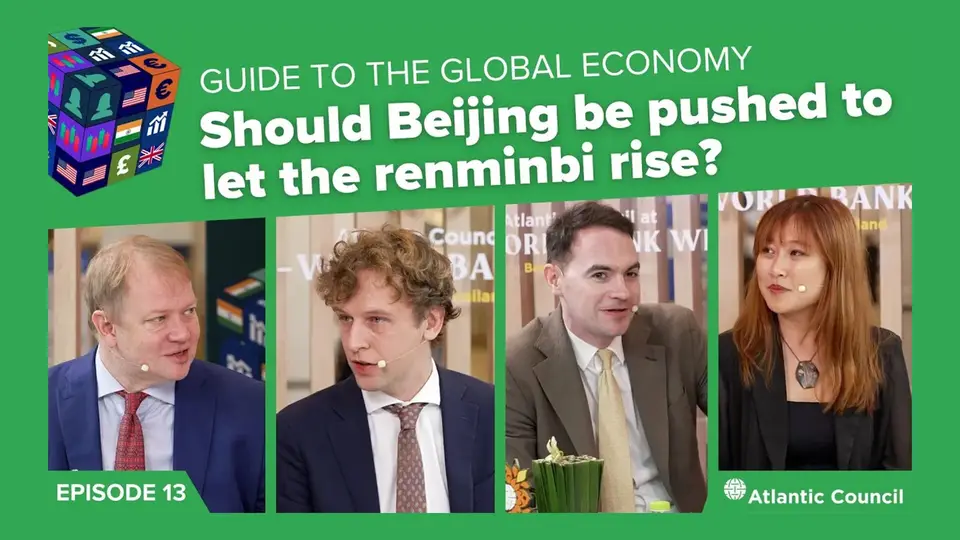
Should Beijing be pushed to let the renminbi rise? (opens the original article)
The article asks whether currency diplomacy could address global imbalances and whether the US and EU can align strategies on China’s overcapacity.
Geopolitics Atlantic Council
Strategic relevanceThe questions connect currency policy and coordination to debate over global imbalances.
Sources1Atlantic Council
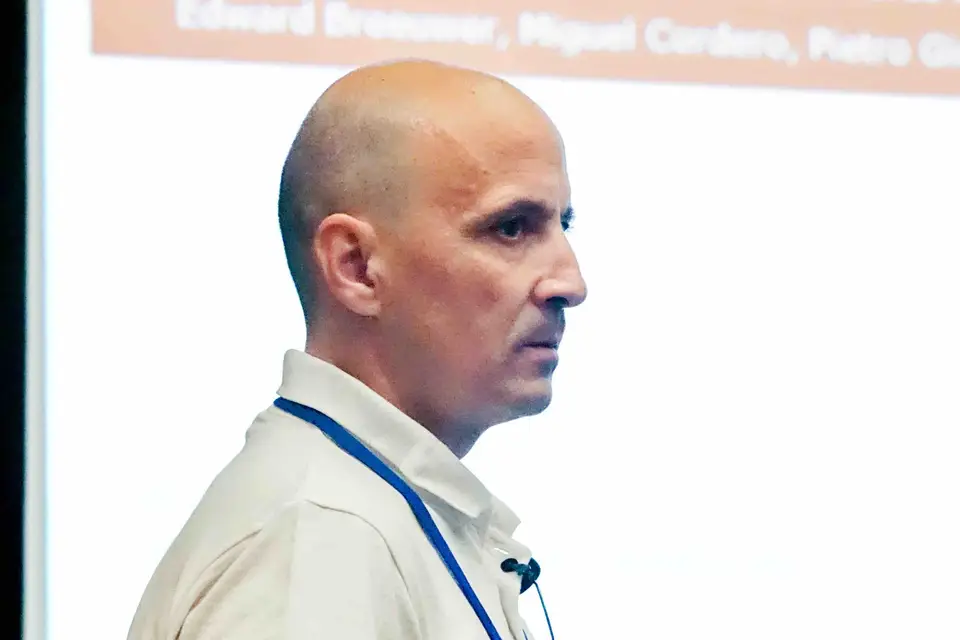
ESA’s Celeste Demonstrates End-to-End LEO-PNT in Orbit (opens the original article)
The European Space Agency says its Celeste demonstration satellite transmitted navigation signals that were successfully tracked and decoded in orbit.
Geopolitics Inside GNSS
Strategic relevanceThe demonstration highlights the operational relevance of LEO-based positioning, navigation and timing.
Sources1Inside GNSS
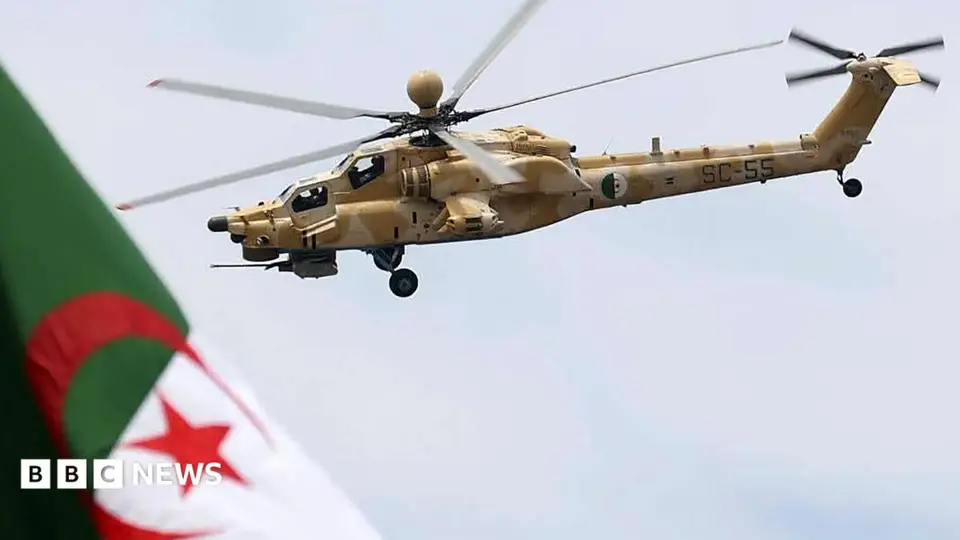
Algeria to send troops to Niger in first foreign deployment since 1973 (opens the original article)
Algeria is expected to send troops to protect energy facilities in northern Niger, near the Libyan border.
Geopolitics BBC World
Strategic relevanceThe deployment places security attention on energy infrastructure near Niger’s border with Libya.
Sources1BBC World
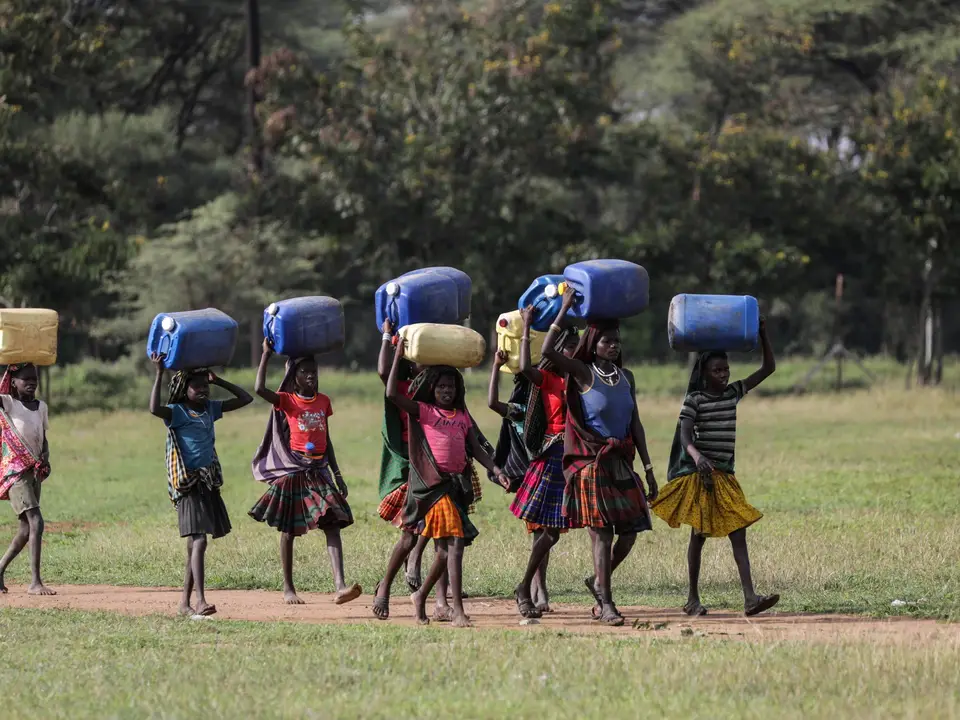
Africa food security under threat due to Iran war, trade officials warn (opens the original article)
Trade officials say the war on Iran is driving up fuel and fertiliser costs across Africa and threatening food security.
Geopolitics Al Jazeera
Strategic relevanceThe reported cost pressures connect conflict to African food security and trade.
Sources1Al Jazeera
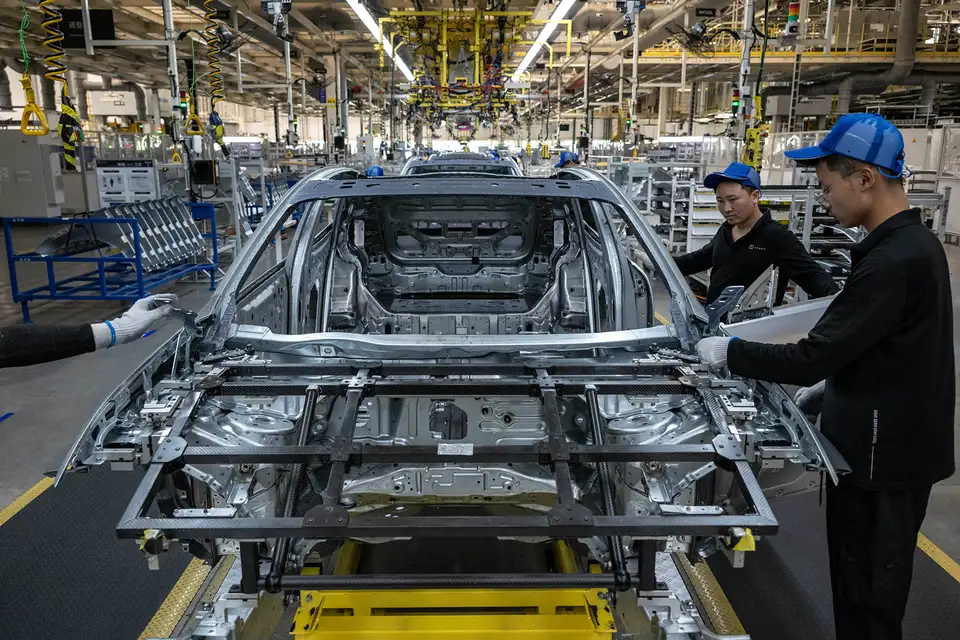
China’s Overcapacity Has a Mind of Its Own (opens the original article)
Foreign Policy argues that Beijing cannot rein in its own industrial machine.
Geopolitics Foreign Policy
Strategic relevanceThe claim bears on analysis of China’s industrial capacity and economic policy.
Sources1Foreign Policy
Israel and the US are both going to the polls - the consequences will be global (opens the original article)
The BBC says elections in Israel and the US are approaching and their outcomes will shape geopolitics and the global economy.
Geopolitics BBC World
Strategic relevanceThe article links election outcomes to geopolitical and economic consequences.
Sources1BBC World
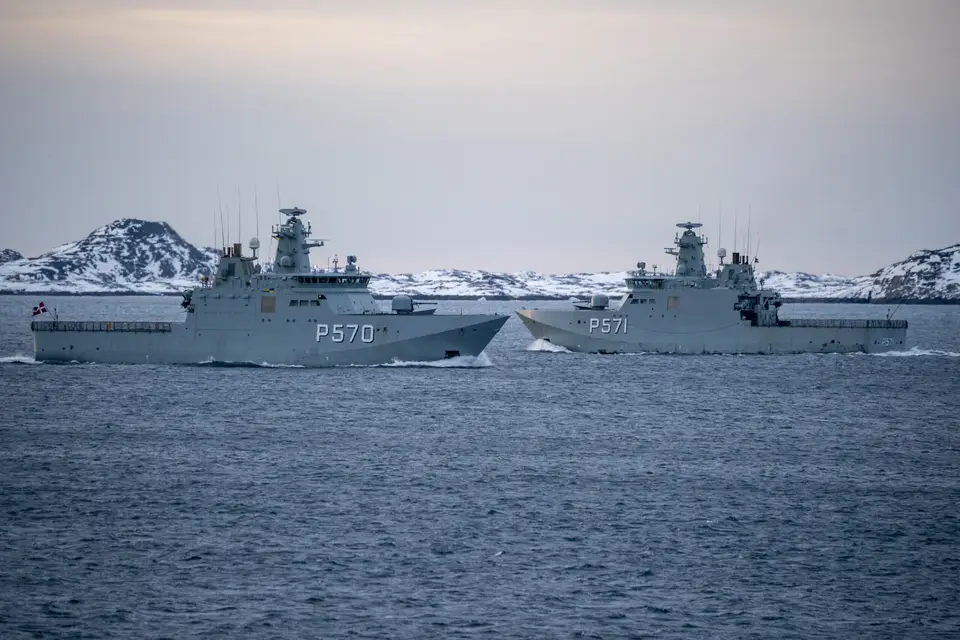
The new EU Arctic strategy shows ambition—but also anxiety (opens the original article)
The Atlantic Council says the EU Arctic strategy shows ambition and anxiety; parts of it read as a response to Trump administration initiatives.
Geopolitics Atlantic Council
Strategic relevanceThe strategy’s framing may help analysts assess how US initiatives feature in EU Arctic policy.
Sources1Atlantic Council
| CVE | CVSS | Product | Ransomware | Added / due | Required action |
|---|---|---|---|---|---|
| CVE-2026-114625 | 9.4Critical | Arista VeloCloud Orchestrator | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-110447 | 9.2Critical | Collabora Collabora Online – Built-in CODE Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-106931 | 8.5High | EG Secure Solutions SiteGuard Server Edition | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-96656 | 8.6High | Plex Media Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-96655 | 5.3Medium | Plex Media Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-96654 | 6.9Medium | Plex Media Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-96652 | 5.3Medium | Plex Media Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-110936 | 8.4High | Siemens Software Center | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-102764 | 9.3Critical | BeyondTrust Remote Support | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2025-61624 | 6.0Medium | Fortinet Multiple Products | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-21589 | 9.3Critical | Atlassian Multiple Products | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-105134 | 9.3Critical | Ahsay AhsayCBS | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
Source: CISA KEV catalogue; CVSS scores from NVD where published. “No score” means NVD has not scored it yet.
Keyword index
Counted from this page. Select one to filter.