 OUTPOST
Edition 225 — 27 October 2026
Cyber, warfare technology and geopolitics as compiled on 27 October 2026.
Cyber
Breaches, campaigns, advisories and research.
Mitsubishi Electric GENESIS, GENESIS64, ICONICS Suite, Hyper Historian, AnalytiX, MobileHMI, IoTWorX, MC Works64, GENESIS32 and BizViz (opens the original article)
CISA says successful exploitation of vulnerabilities in the listed Mitsubishi Electric products could allow an attacker to execute arbitrary actions; the snippet cuts off before specifying them.
Cyber CISA Advisories
What to checkCheck whether these products are in use and review the CISA advisory for further details.
Sources1CISA Advisories
EPICS Base (opens the original article)
CISA says successful exploitation of vulnerabilities in EPICS Base could cause a denial-of-; the snippet cuts off before completing the impact.
Cyber CISA Advisories
What to checkCheck whether EPICS Base is in use and review the CISA advisory for further details.
Sources1CISA Advisories
CISA Adds Two Known Exploited Vulnerabilities to Catalog (opens the original article)
CISA says it added two vulnerabilities to its Known Exploited Vulnerabilities Catalog based on evidence of active exploitation.
Cyber CISA Advisories
What to checkCheck whether your systems are affected and prioritize remediation using the KEV Catalog.
Sources1CISA Advisories
OpenAI's GPT-6.1 Terra is safer overall, but shows more destructive-action flags in tests (opens the original article)
OpenAI says GPT-6.1 Terra is safer overall than some older models, though safety tests also found more destructive-action flags.
Cyber BleepingComputer
What to checkReview safeguards and test how the model handles destructive actions before deployment.
Sources1BleepingComputer
UNM Health ransomware attack disrupts patient care, surgeries (opens the original article)
The University of New Mexico Health Sciences Center disclosed a cyberattack that caused system outages and disrupted patient care and academic activities.
Cyber BleepingComputer
What to checkDefenders should review incident readiness for systems supporting patient care and academic activities.
Sources1BleepingComputer
Hackers hijack Convertr analytics script to steal payment card data (opens the original article)
BleepingComputer reports that a skimming group compromised a shared Convertr analytics script to steal payment data during checkout.
Cyber BleepingComputer
What to checkReview third-party scripts used at checkout and monitor for unauthorized changes or payment-data collection.
Sources1BleepingComputer
Nefilim, Hive ransomware operator given five-year-plus sentence after guilty plea (opens the original article)
The Record reports that a Nefilim and Hive ransomware operator received a sentence of more than five years after pleading guilty to charges related to participating in at least two ransomware groups.
Cyber The Record
What to checkThe case highlights the need to prepare for ransomware threats linked to organized operators.
Sources1The Record
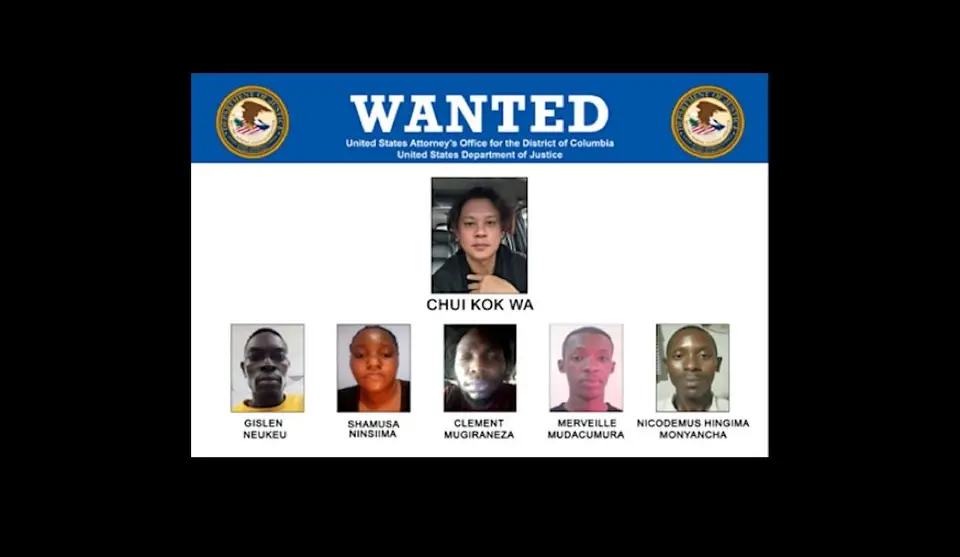
US indicts Malaysian national after Madagascar scam operation uncovered (opens the original article)
The Record reports a US indictment of a Malaysian national and a sting in Madagascar, highlighting the scam center industry's global reach.
Cyber The Record
What to checkReview how staff identify and report suspected scam-related contacts.
Sources1The Record
Microsoft releases Windows OOB updates to distrust eMudhra certificates (opens the original article)
Microsoft released out-of-band Windows updates to remove trust in certificates tied to compromised eMudhra certificate authority keys, including on systems without automatic certificate trust updates.
Cyber BleepingComputer
What to checkCheck whether affected Windows systems have received the updates and whether certificate trust updates are automatic.
Sources1BleepingComputer
Warp discloses breach exposing AI agent logs, user telemetry data (opens the original article)
Warp says user decision logs and telemetry data were exposed in an attack on a third-party vendor in its infrastructure.
Cyber BleepingComputer
What to checkReview third-party access and assess whether exposed agent logs or telemetry require a response.
Sources1BleepingComputer
Warfare
Drones, electronic warfare, missiles and defence systems.
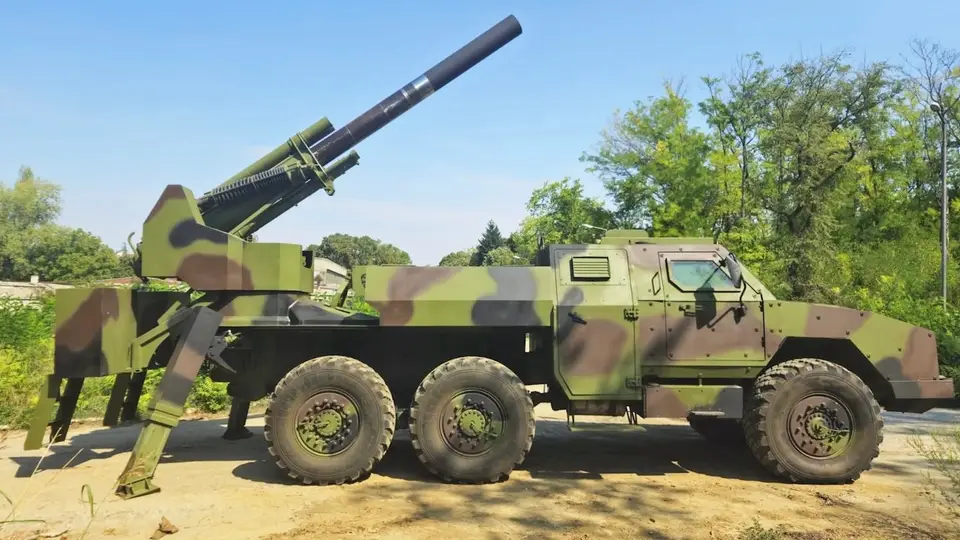
This Serbian Truck Carries A Truly Massive Mortar (opens the original article)
The War Zone says the Serbian TSMB M-25 mortar combines high destructive potential with high mobility.
Warfare The War Zone
Why it mattersThe system highlights an effort to pair heavy mortar capability with mobility.
Sources1The War Zone
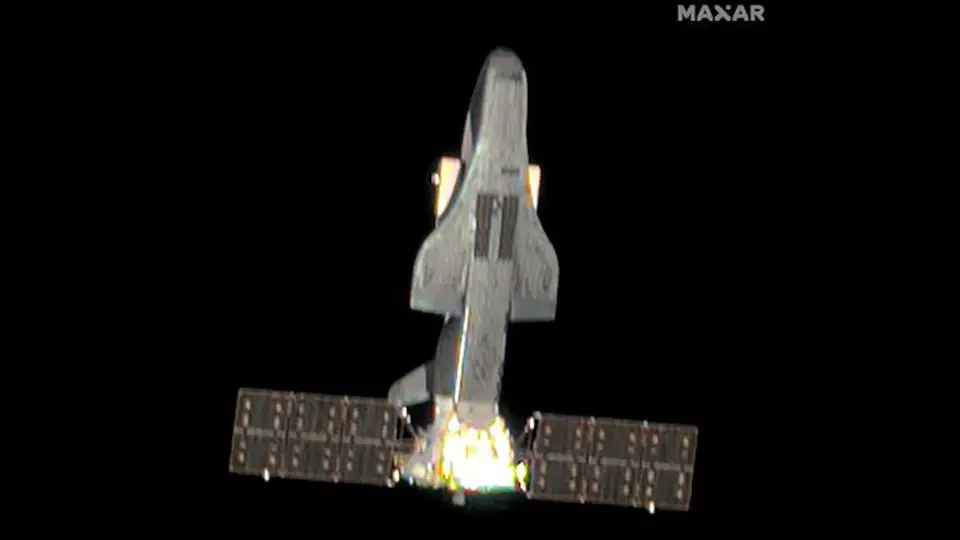
U.S. Intel Confirms This Is China’s Secret Spaceplane (opens the original article)
The War Zone says Chinese intelligence confirms a Chinese spaceplane design that is very similar to the U.S. Space Force’s X-37B.
Warfare The War Zone
Why it mattersThe reported design similarity makes the spaceplane relevant to comparing space technologies.
Sources1The War Zone
China has tripled its satellite fleet since 2018 as expansion continues: DIA (opens the original article)
The Defense Intelligence Agency says China has tripled its satellite fleet since 2018; its unclassified space-threat report includes a newly released image.
Warfare Breaking Defense
Why it mattersSatellite expansion is relevant to assessing the changing space environment and its strategic significance.
Sources1Breaking Defense
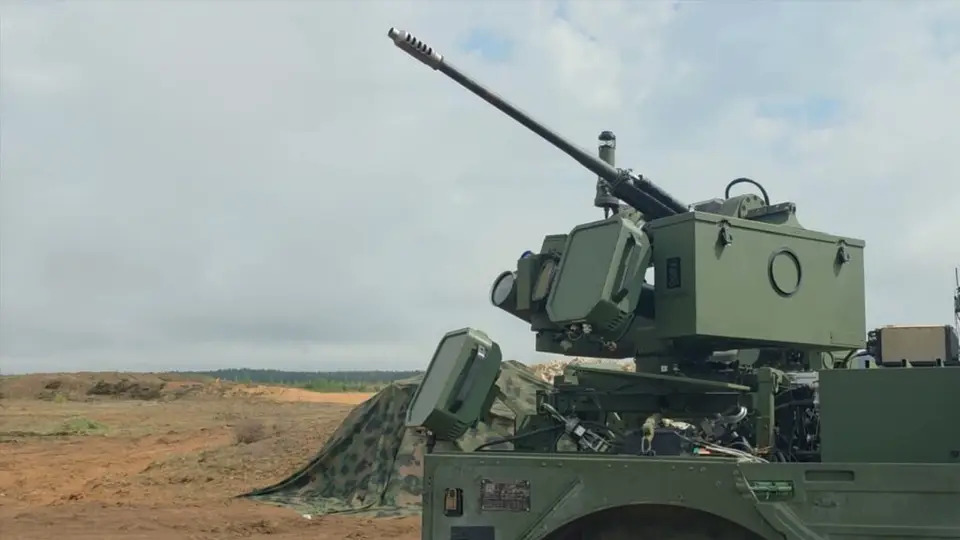
A more flexible way to defend maneuver forces from drones that doesn’t tie them down (opens the original article)
A sponsored item describes short-range air defense designed to move and adapt regardless of vehicle.
Warfare Breaking Defense
Why it mattersMobility and adaptability are relevant to protecting maneuver forces from drones.
Sources1Breaking Defense
What’s haunting the Pentagon this Halloween? (opens the original article)
Breaking Defense discusses mysteries including the dangers of war in space and the intricacies of upgrading America’s nuclear weapons.
Warfare Breaking Defense
Why it mattersThese topics highlight the operational and technology challenges of space warfare and nuclear modernization.
Sources1Breaking Defense
Financial aid for Ukraine is getting harder to find (opens the original article)
Defense One says aid for Ukraine is becoming harder to find: rearming amid economic stress leaves less money to give, despite political support for helping a European neighbor.
Warfare Defense One
Why it mattersThe funding pressure matters to understanding the resources available for Ukraine’s support.
Sources1Defense One
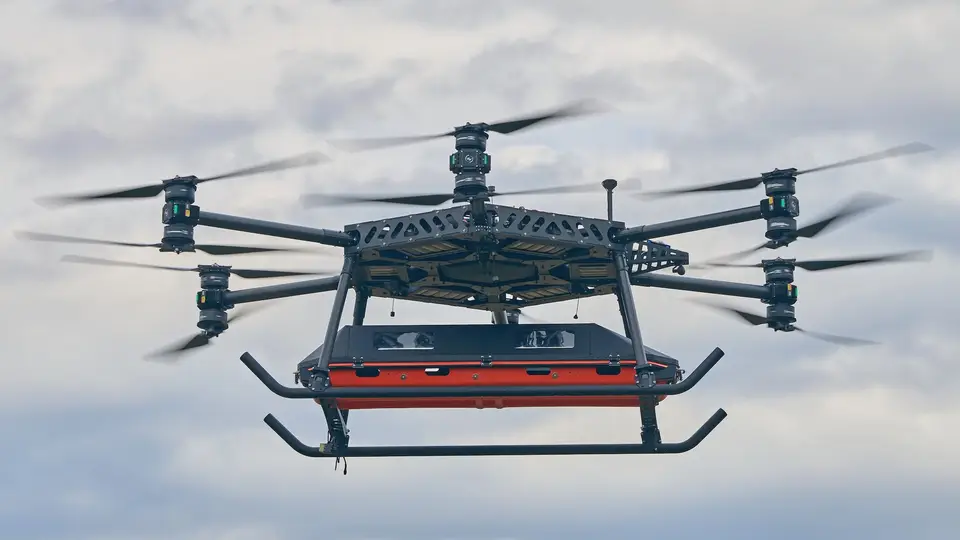
Ukraine’s StarGate Drone Now Evacuating Wounded Soldiers (opens the original article)
The War Zone reports that Ukraine’s StarGate drone is claimed to have completed two battlefield evacuations, including one under electronic attack.
Warfare The War Zone
Why it mattersThe claimed missions illustrate an aerial evacuation role and operation under electronic attack.
Sources1The War Zone
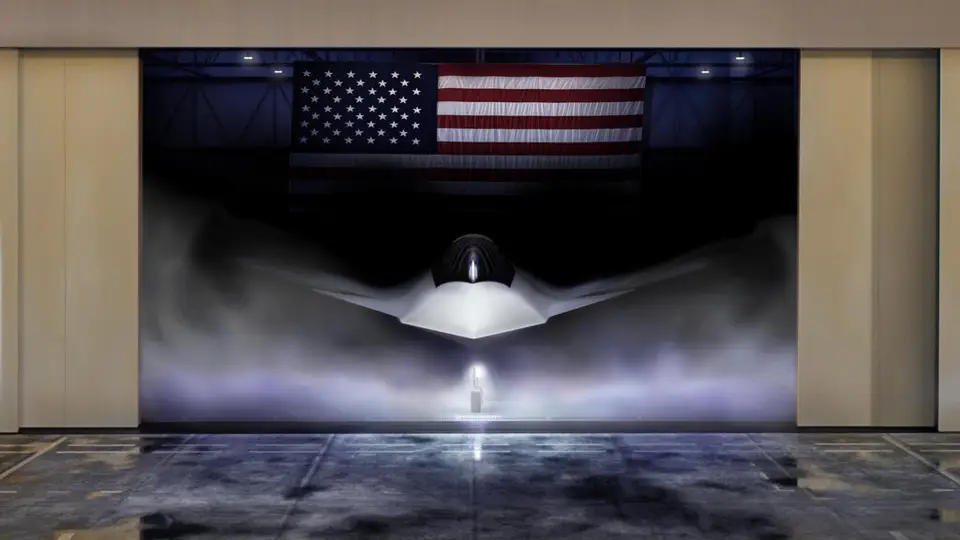
How the F-15 and F-22 should inform the F-47’s procurement (opens the original article)
An analyst argues that budgetary lessons from the F-15 and F-22 can help the Air Force anticipate hard choices in F-47 procurement.
Warfare Breaking Defense
Why it mattersThe story highlights how past aircraft budgets may inform procurement choices for a new platform.
Sources1Breaking Defense
Geopolitics & geodata
Strategy, geo wars, GNSS and satellite security.
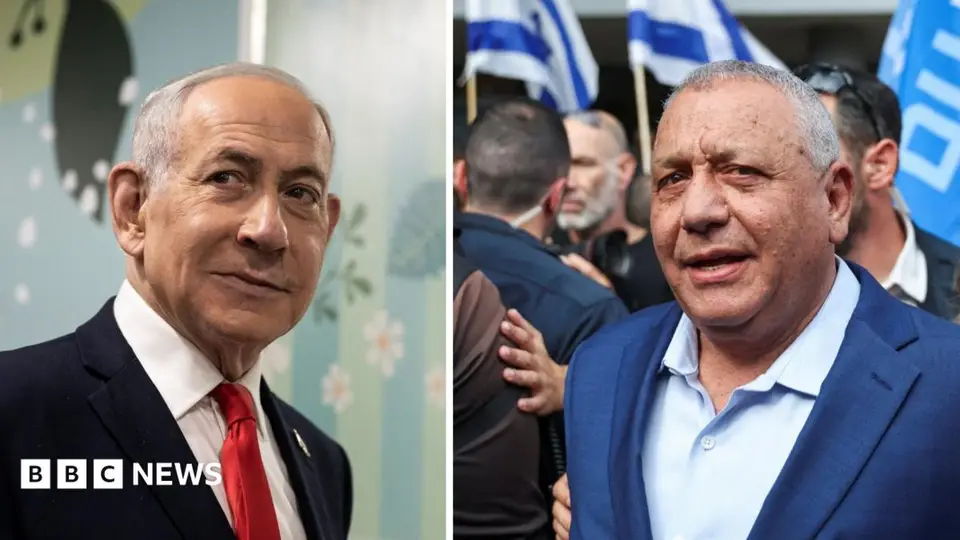
Watch: 'No clear winner' in Israel election - what happens now? (opens the original article)
The BBC World item says polls have closed in Israel’s election, but there is no clear winner.
Geopolitics BBC World
Strategic relevanceAn unclear result makes the election’s political outcome relevant to regional analysis.
Sources1BBC World
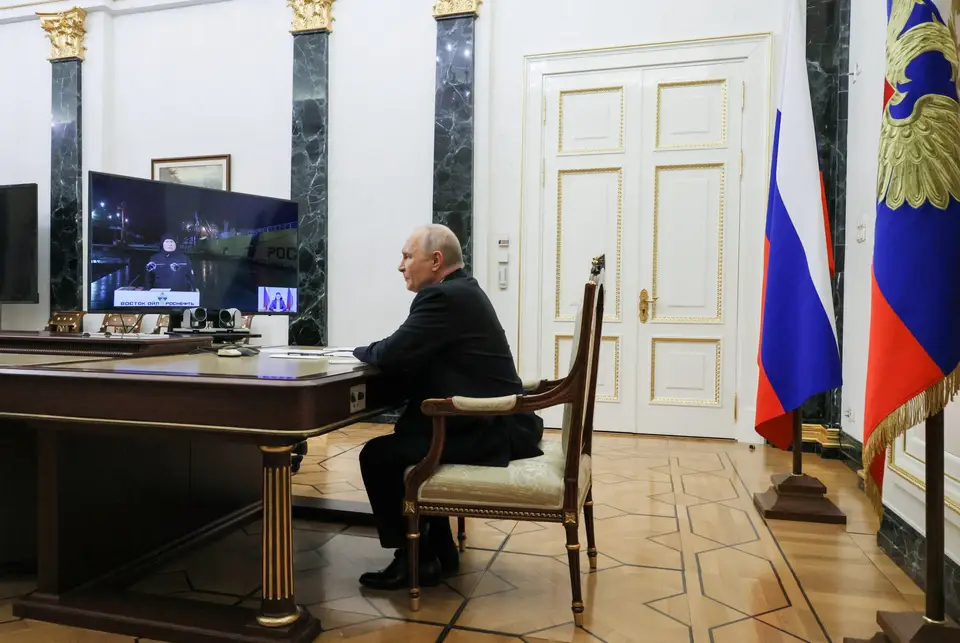
For Russia, Trump’s diesel deal was just the first ask (opens the original article)
Atlantic Council questions the rationale behind the Trump administration’s General License 135, described in the title as part of a diesel deal with Russia.
Geopolitics Atlantic Council
Strategic relevanceThe questions around the license may matter to analysis of Russia-related policy.
Sources1Atlantic Council
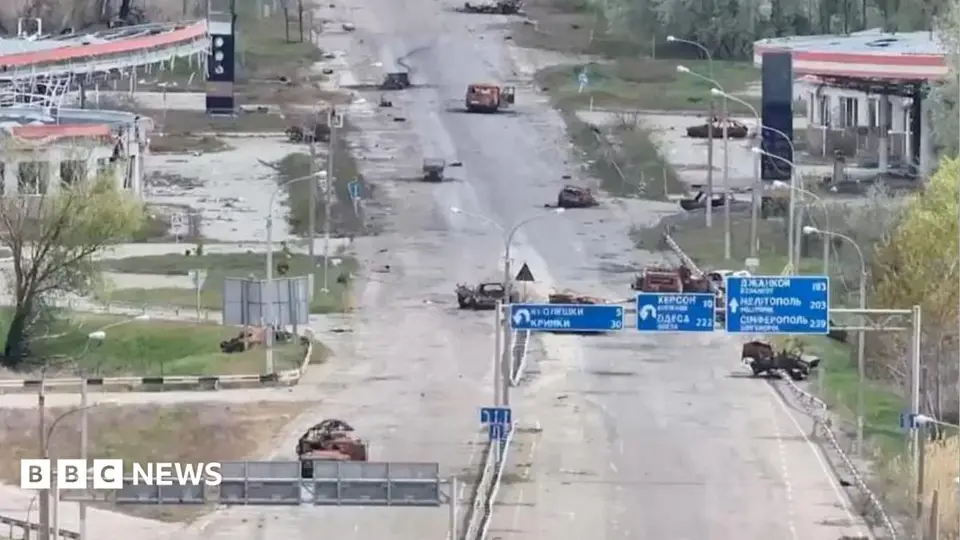
Ceasefire extended across Ukraine's Kherson region, officials say (opens the original article)
The ceasefire across Ukraine's Kherson region was initially planned for stranded residents of Oleshky. Russia and Ukraine say no breaches have been reported.
Geopolitics BBC World
Strategic relevanceThe truce concerns residents in Oleshky and the situation in the Kherson region.
Sources1BBC World
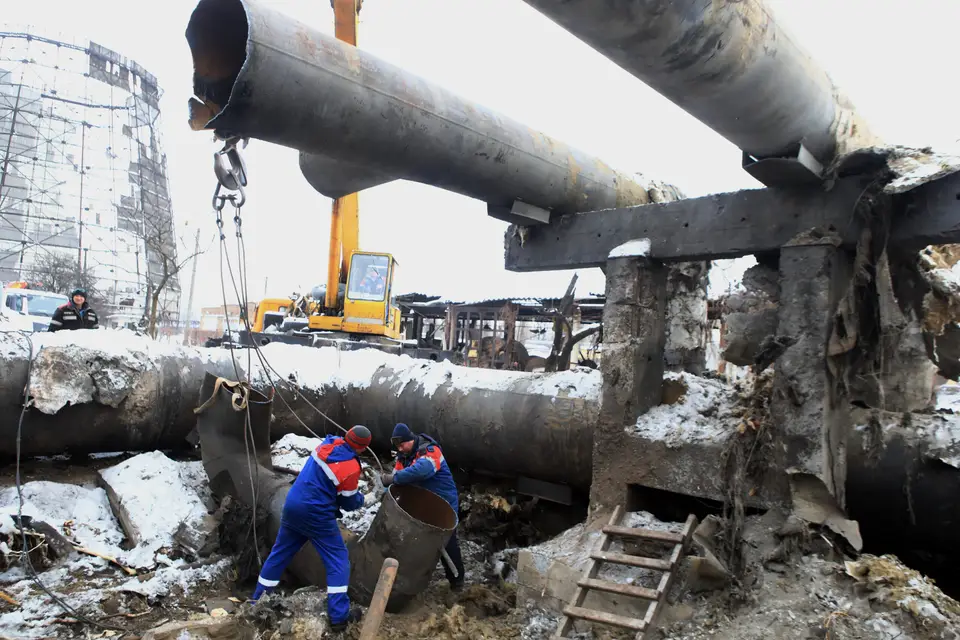
UN report: Russian attacks on Ukraine’s power grid are a ‘crime against humanity’ (opens the original article)
A UN commission report says Russia’s attacks on Ukraine’s civilian power grid qualify as a crime against humanity.
Geopolitics Atlantic Council
Strategic relevanceAttacks on power infrastructure underscore its strategic and civilian significance in the conflict.
Sources1Atlantic Council
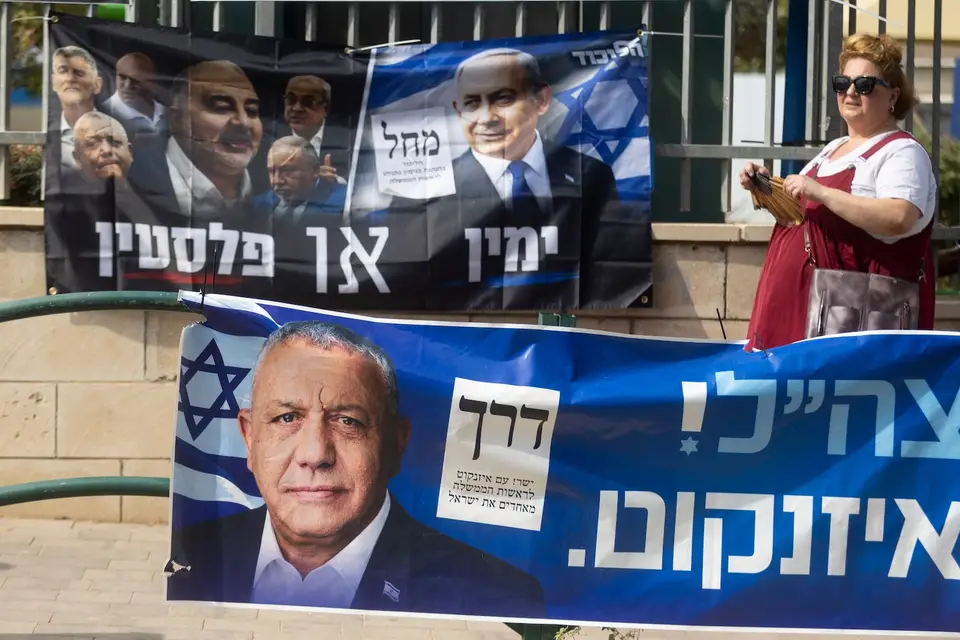
Decoding Israel’s Election Results (opens the original article)
Foreign Policy reports that exit polls show no clear winner, with Eisenkot’s opposition bloc slightly ahead of Netanyahu’s.
Geopolitics Foreign Policy
Strategic relevanceThe exit polls offer a snapshot of the balance between political blocs.
Sources1Foreign Policy
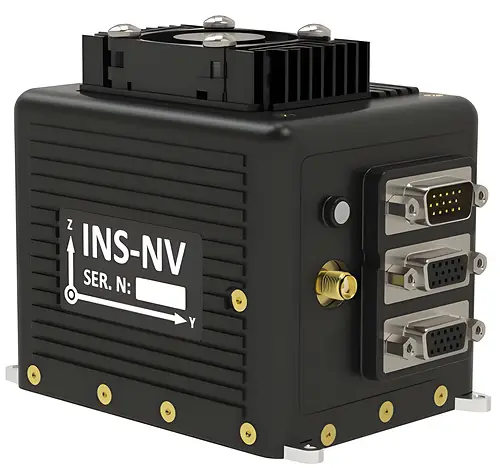
Inertial Labs, a VIAVI Solutions Company, Accelerates Complex Alt-PNT and Guidance Systems Design with Programmable INS Development Platform (opens the original article)
Inertial Labs says its INS-NV platform combines an AI processor, tactical-grade MEMS sensors and a full-constellation GNSS receiver to speed development of navigation systems.
Geopolitics Inside GNSS
Strategic relevanceThe platform brings together inertial and GNSS navigation components for alternative positioning and guidance systems.
Sources1Inside GNSS
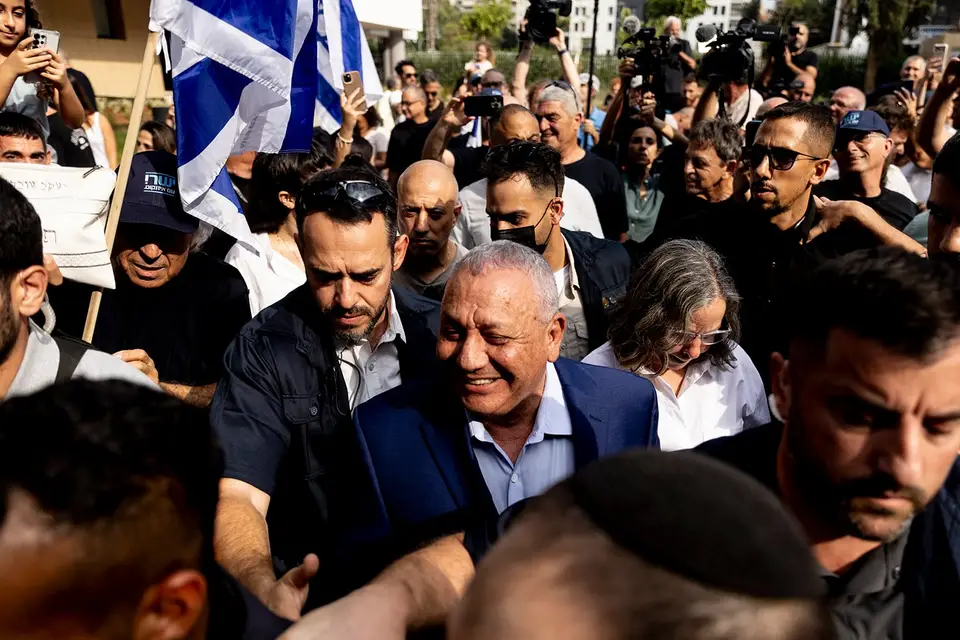
Dramatic Changes Are Unlikely in Israel, Even if Netanyahu Is Ousted (opens the original article)
Foreign Policy says Eisenkot’s centrist bloc leads in exit polls, while dramatic changes in Israel are unlikely even if Netanyahu is ousted.
Geopolitics Foreign Policy
Strategic relevanceThe item highlights the limits of how much a possible leadership change may shift Israeli politics.
Sources1Foreign Policy
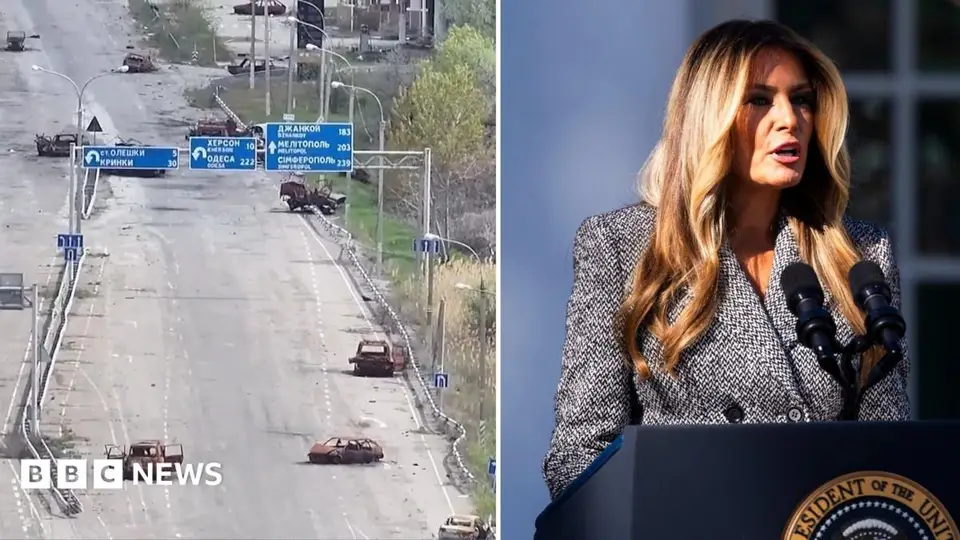
What we know about Ukraine-Russia truce in Oleshky, brokered by Melania Trump (opens the original article)
The BBC World item says Oleshky has lacked electricity, gas and water for three years; residents reported eating weeds to survive.
Geopolitics BBC World
Strategic relevanceThe reported loss of basic services highlights the city’s humanitarian and infrastructure conditions.
Sources1BBC World
| CVE | CVSS | Product | Ransomware | Added / due | Required action |
|---|---|---|---|---|---|
| CVE-2026-48356 | 9.3Critical | Adobe Commerce and Magento | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-111497 | 9.2Critical | Google Brotli | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-109618 | 9.2Critical | PHP Group PHP | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-109619 | 9.2Critical | PHP Group PHP | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-114625 | 9.4Critical | Arista VeloCloud Orchestrator | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-110447 | 9.2Critical | Collabora Collabora Online – Built-in CODE Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-106931 | 8.5High | EG Secure Solutions SiteGuard Server Edition | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-96656 | 8.6High | Plex Media Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-96655 | 5.3Medium | Plex Media Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-96654 | 6.9Medium | Plex Media Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-96652 | 5.3Medium | Plex Media Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-110936 | 8.4High | Siemens Software Center | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
Source: CISA KEV catalogue; CVSS scores from NVD where published. “No score” means NVD has not scored it yet.
Keyword index
Counted from this page. Select one to filter.