 OUTPOST
Edition 226 — 28 October 2026
Cyber, warfare technology and geopolitics as compiled on 28 October 2026.
Cyber
Breaches, campaigns, advisories and research.
CISA Warns of Node2Shell Exploitation as Honeypots Log Attack Attempts (opens the original article)
CISA added the Brotli flaw to its KEV catalog. Two honeypot operators logged attempts, including one using a broken exploit.
Cyber SecurityWeek
What to checkCheck for affected Brotli components and prioritize remediation in line with the KEV listing.
Sources1SecurityWeek
Anthropic's Unreleased AI Model Chains Flaws Into Working Chrome, Safari, Windows and Linux Exploits (opens the original article)
Anthropic says an unreleased AI model found flaws in Chrome, Safari, Android, Windows and Linux, then chained them into working proof-of-concept exploits built in a lab.
Cyber The Hacker News
What to checkCheck whether affected software is in use and review available security updates.
Sources1The Hacker News
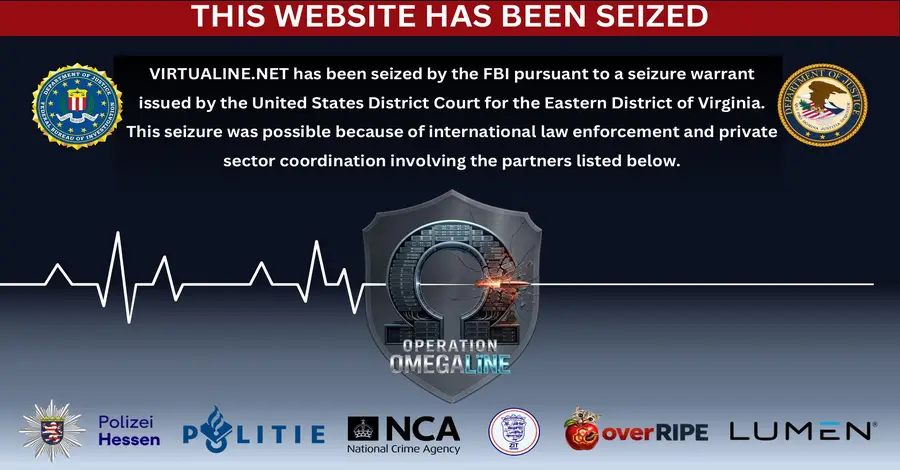
FBI Seizes Virtualine Domain Over Alleged Criminal Hosting and Bitcoin Money Laundering (opens the original article)
The U.S. Department of Justice announced seizure of a domain associated with Virtualine, a bulletproof hosting provider, over alleged criminal activity.
Cyber The Hacker News
What to checkReview exposure to the named hosting provider and monitor for domain-related disruption.
Sources1The Hacker News
Mitsubishi Electric GENESIS, GENESIS64, ICONICS Suite, Hyper Historian, AnalytiX, MobileHMI, IoTWorX, MC Works64, GENESIS32 and BizViz (opens the original article)
The title lists Mitsubishi Electric GENESIS and related products; the advisory snippet says successful exploitation of vulnerabilities, but provides no further detail.
Cyber CISA Advisories
What to checkDefenders should consult the advisory and check whether listed products are present in their environments.
Sources1CISA Advisories
EPICS Base (opens the original article)
The title identifies EPICS Base; the advisory snippet says successful exploitation of vulnerabilities, but provides no further detail.
Cyber CISA Advisories
What to checkDefenders should consult the advisory and check whether EPICS Base is present in their environments.
Sources1CISA Advisories
CISA Adds Two Known Exploited Vulnerabilities to Catalog (opens the original article)
CISA added two vulnerabilities to its Known Exploited Vulnerabilities Catalog, based on evidence of active exploitation, according to the snippet.
Cyber CISA Advisories
What to checkCheck the catalog and assess whether the listed vulnerabilities affect your systems.
Sources1CISA Advisories
Japan's GMO Offers $1 Million Bounty to Catch Hackers Behind FX Trading Cloud Breach (opens the original article)
GMO Internet Group says it is offering up to $1 million for tips identifying attackers who breached its Onamae.com Desktop Cloud service. The company says it refused an extortion demand.
Cyber The Hacker News
What to checkReview cloud access and incident-response procedures; check whether any systems or accounts were affected.
Sources1The Hacker News
Tailscale Patches SSH Flaws That Could Let Hacked Devices Gain Root Access on Other Servers (opens the original article)
Tailscale says version 1.104.4 fixes built-in SSH server flaws that could let an attacker reach services and files on other servers reserved for root users.
Cyber The Hacker News
What to checkUpdate Tailscale to version 1.104.4 and review systems using its built-in SSH server.
Sources1The Hacker News
ShinyHunters-Exploited Oracle PeopleSoft Zero-Day Turns Out to Be Three Chained Flaws (opens the original article)
Researchers say the Oracle PeopleSoft bug exploited by ShinyHunters is three chained flaws. Oracle patched all three under one identifier in June.
Cyber The Hacker News
What to checkCheck PeopleSoft systems for the Oracle patch covering all three flaws.
Sources1The Hacker News
Adobe Commerce PolyShell Attacks Breach Hundreds of Stores as Brotli Exploit Traffic Emerges (opens the original article)
CISA added vulnerabilities affecting Adobe Commerce, Magento, and Google's Brotli decoder library to its KEV catalog, citing evidence of active exploitation.
Cyber The Hacker News
What to checkCheck whether affected products are deployed and prioritize applicable KEV catalog remediation.
Sources1The Hacker News
Warfare
Drones, electronic warfare, missiles and defence systems.
The Next Congress Needs to Reclaim Its Oversight of the Department of Defense (opens the original article)
War on the Rocks says Congress has not adequately exercised oversight of the executive branch, particularly over the Department of Defense.
Warfare War on the Rocks
Why it mattersOversight shapes how defense authority and activity are scrutinized.
Sources1War on the Rocks
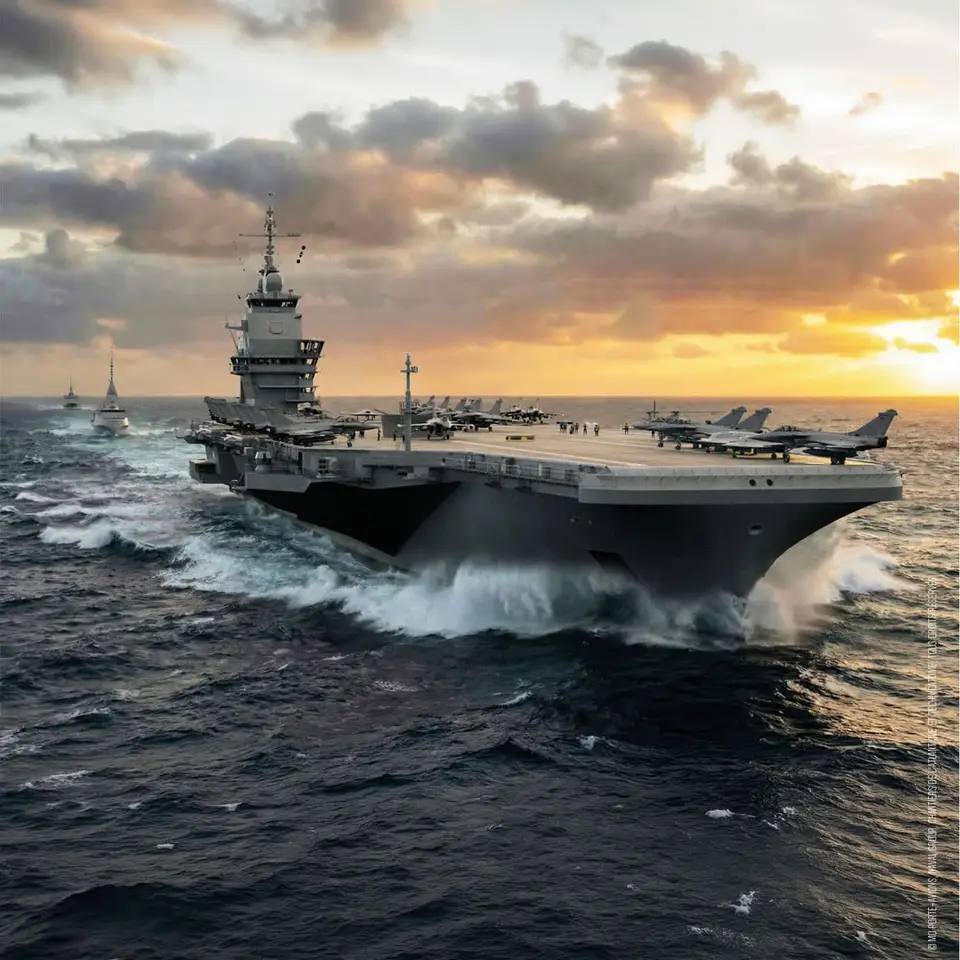
French Parliamentary Report Urges Construction of a Second Aircraft Carrier by 2029 (opens the original article)
A French parliamentary report urges ordering a second next-generation aircraft carrier by 2029 to ensure a permanent Carrier Strike Group presence at sea.
Warfare Naval News
Why it mattersThe proposal links carrier procurement to maintaining a persistent naval presence.
Sources1Naval News
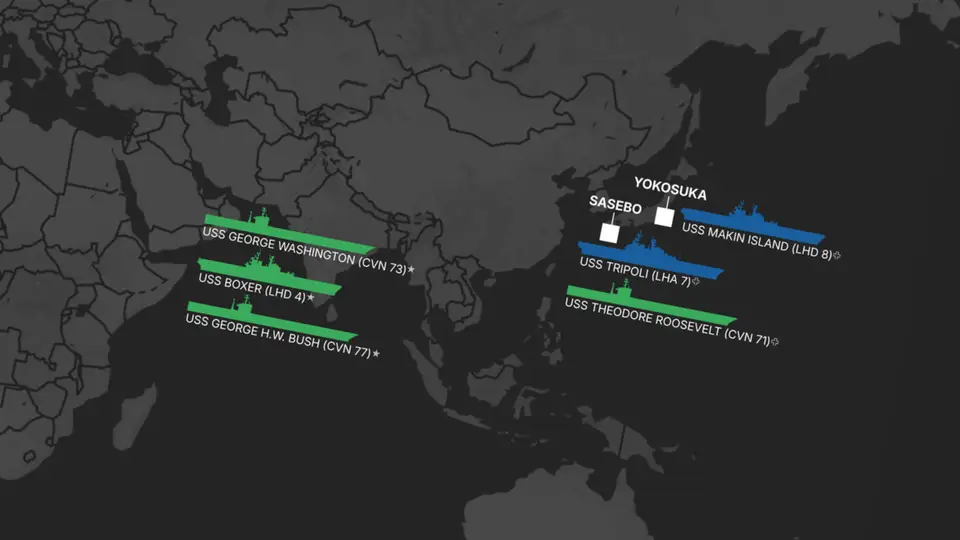
Where Are The Aircraft Carriers?: October 27, 2026 (opens the original article)
The Makin Island amphibious ready group arrived in Yokosuka after the Theodore Roosevelt carrier strike group, whose jets conducted a simulated strike during Keen Sword 27.
Warfare The War Zone
Why it mattersThe exercise and group movements provide a snapshot of carrier and amphibious operations in the region.
Sources1The War Zone
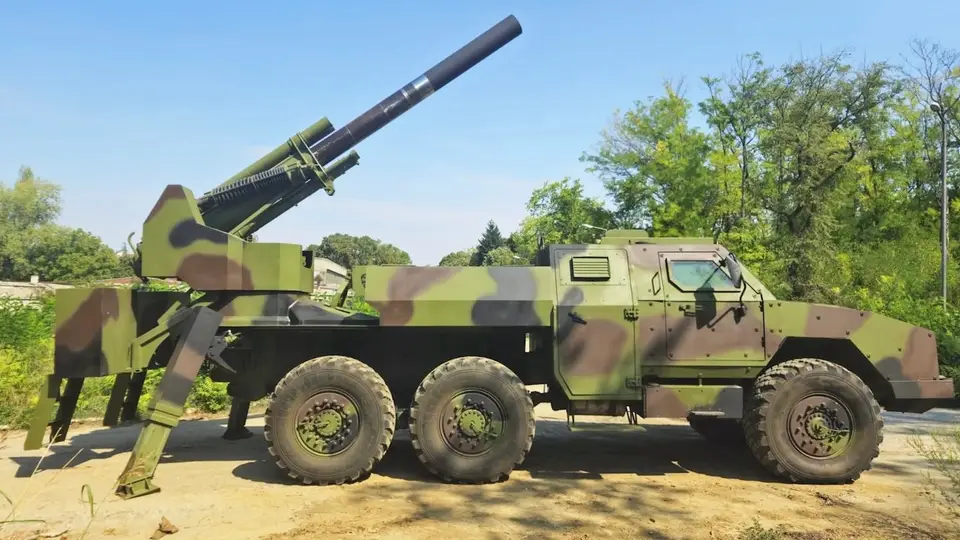
This Serbian Truck Carries A Truly Massive Mortar (opens the original article)
The War Zone says the Serbian TSMB M-25 mortar combines high destructive potential with high mobility.
Warfare The War Zone
Why it mattersThe system highlights an effort to pair heavy mortar capability with mobility.
Sources1The War Zone
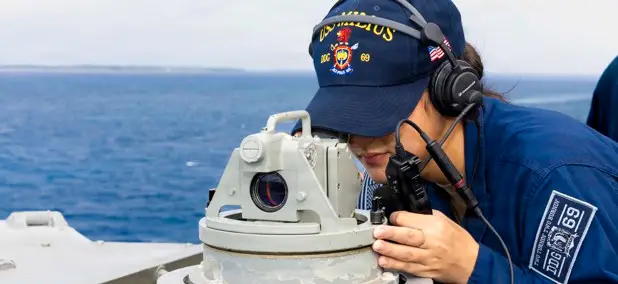
The port-call situation is wearing out Navy warships (opens the original article)
Defense One says Diego Garcia is the only safe place for ships fighting Iran, but the remote atoll cannot provide needed maintenance, wearing out Navy warships.
Warfare Defense One
Why it mattersMaintenance limits at a safe port-call location may affect the availability of ships operating in the area.
Sources1Defense One
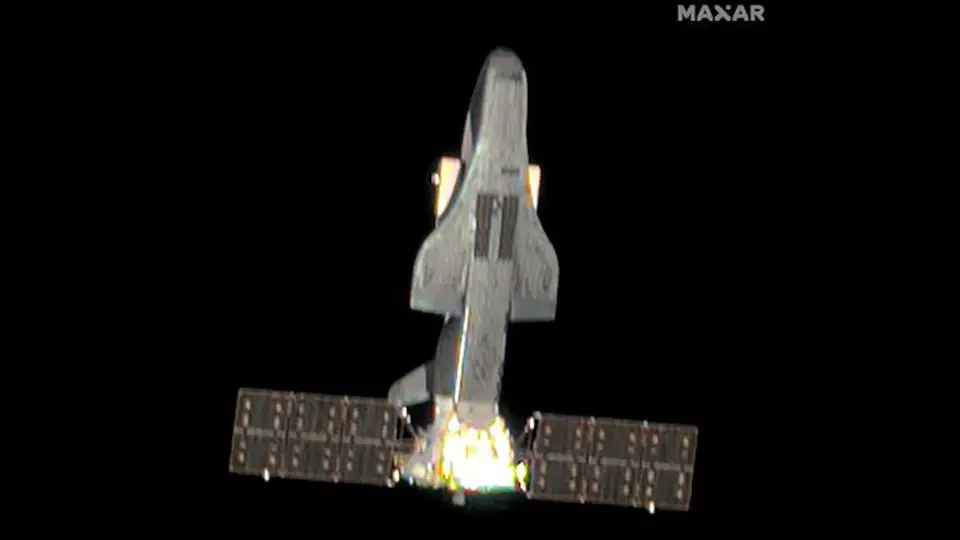
U.S. Intel Confirms This Is China’s Secret Spaceplane (opens the original article)
The War Zone says Chinese intelligence confirms a Chinese spaceplane design that is very similar to the U.S. Space Force’s X-37B.
Warfare The War Zone
Why it mattersThe reported design similarity makes the spaceplane relevant to comparing space technologies.
Sources1The War Zone
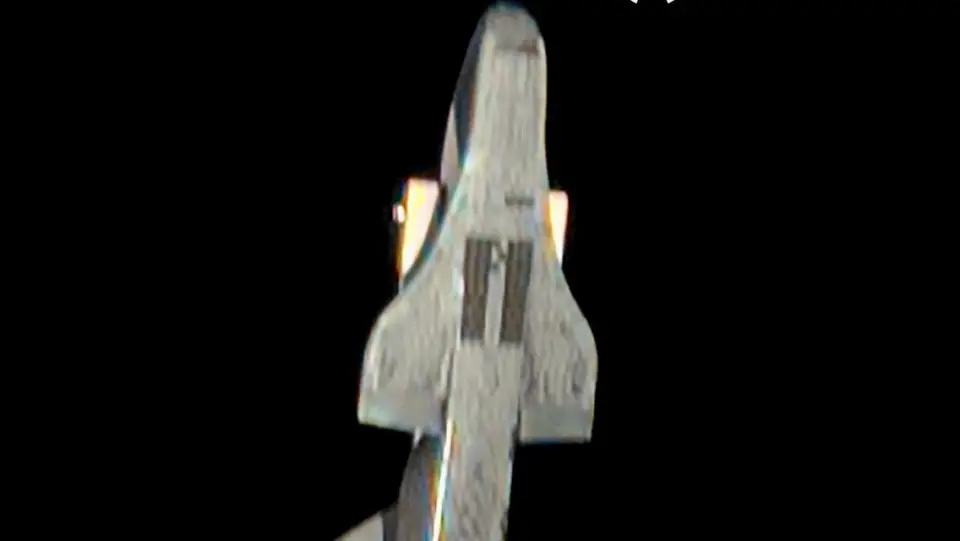
China has tripled its satellite fleet since 2018 as expansion continues: DIA (opens the original article)
The Defense Intelligence Agency says China has tripled its satellite fleet since 2018; its unclassified space-threat report includes a newly released image.
Warfare Breaking Defense
Why it mattersSatellite expansion is relevant to assessing the changing space environment and its strategic significance.
Sources1Breaking Defense
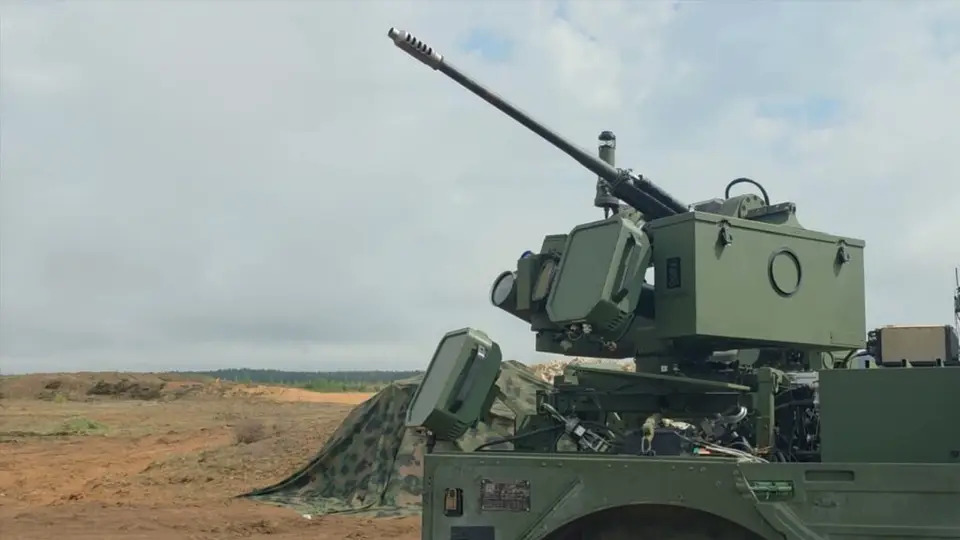
A more flexible way to defend maneuver forces from drones that doesn’t tie them down (opens the original article)
A sponsored item describes short-range air defense designed to move and adapt regardless of vehicle.
Warfare Breaking Defense
Why it mattersMobility and adaptability are relevant to protecting maneuver forces from drones.
Sources1Breaking Defense
Geopolitics & geodata
Strategy, geo wars, GNSS and satellite security.
Khouri: Strong Israel-Arab bloc result does not mean Israel has changed (opens the original article)
Rami Khouri challenges the idea that a strong Israel-Arab bloc result signals a positive shift in Israeli society.
Geopolitics Al Jazeera
Strategic relevanceThe distinction matters when interpreting political results and claims about shifts in society.
Sources1Al Jazeera
Is AIPAC losing its grip on US politics? (opens the original article)
AIPAC is changing its strategy, ending candidate endorsements and direct campaign contributions.
Geopolitics Al Jazeera
Strategic relevanceThe shift is relevant to how organized political influence may operate in US politics.
Sources1Al Jazeera
Why the US midterms matter even if you don’t live in America (opens the original article)
The US midterms could shape decisions on military aid, sanctions, trade and tariffs, with effects beyond the United States.
Geopolitics Al Jazeera
Strategic relevanceThe results may affect policy choices with international and strategic consequences.
Sources1Al Jazeera
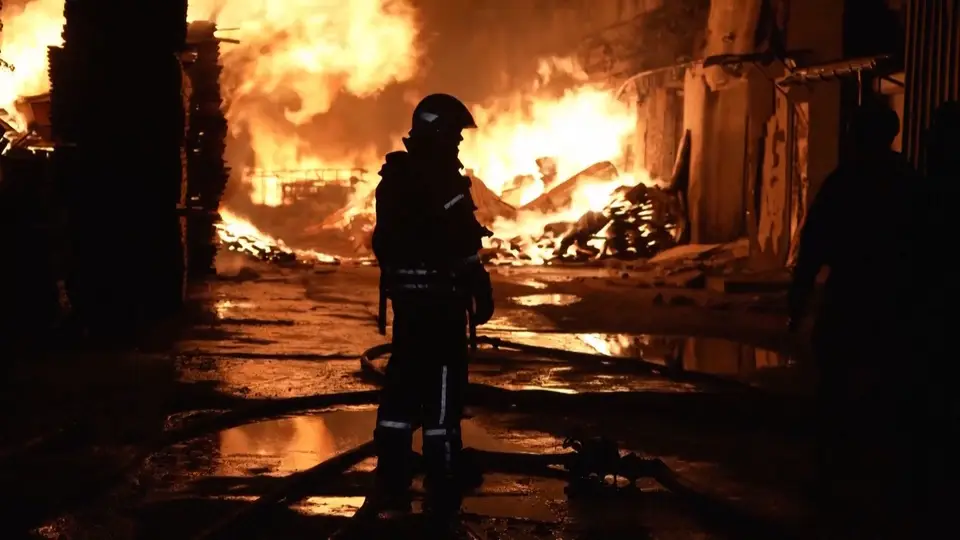
Elderly women and children survive Russian attack on Kharkiv (opens the original article)
Al Jazeera reports that a Russian drone attack in Kharkiv forced elderly women and children to evacuate their homes.
Geopolitics Al Jazeera
Strategic relevanceThe reported evacuation highlights civilian impacts of drone attacks in an urban area.
Sources1Al Jazeera
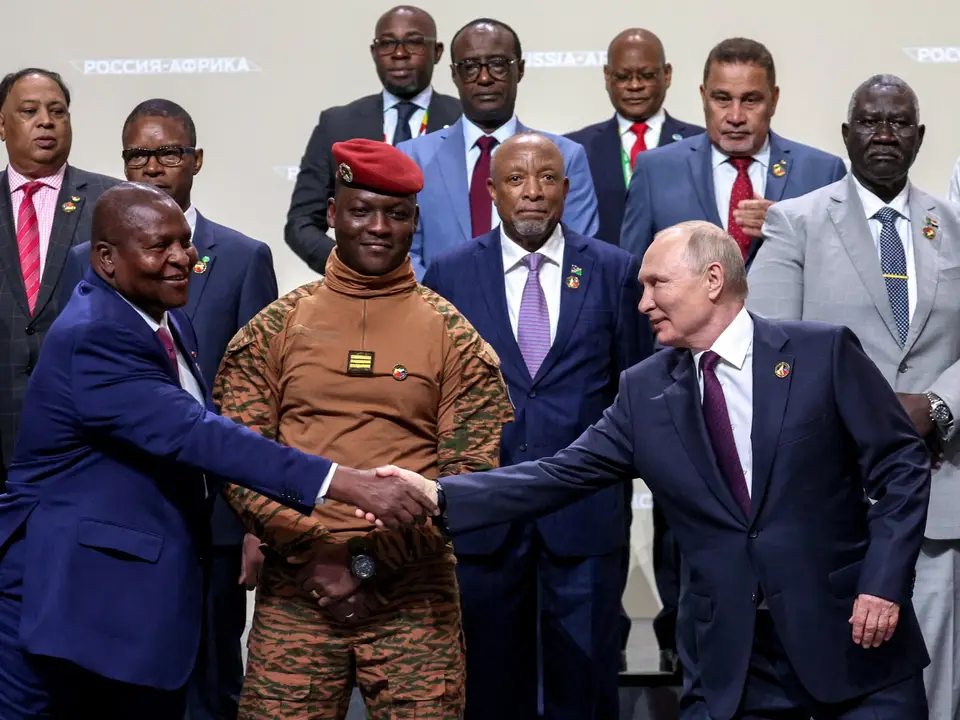
Russia is selling Africa dependence disguised as partnership (opens the original article)
Al Jazeera says Russia is securing resources and protecting rulers at the expense of African people as leaders gather in Moscow.
Geopolitics Al Jazeera
Strategic relevanceThe account frames Russia’s engagement in Africa as a question of influence, resources, and political dependence.
Sources1Al Jazeera
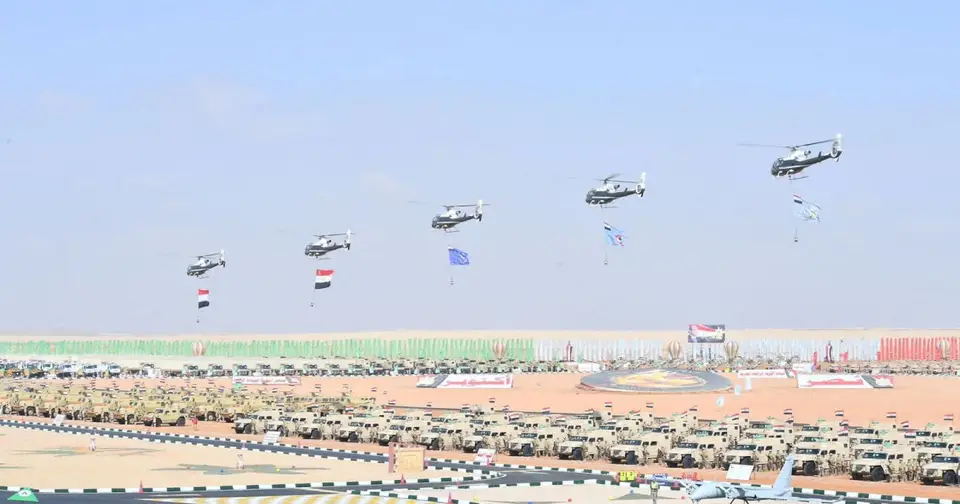
The next phase of military rule in Egypt is here (opens the original article)
El-Sisi’s announcement that he will not run for a fourth term may signal a new leadership arrangement, according to Al Jazeera.
Geopolitics Al Jazeera
Strategic relevanceThe announcement may mark a change in Egypt’s political leadership arrangements.
Sources1Al Jazeera
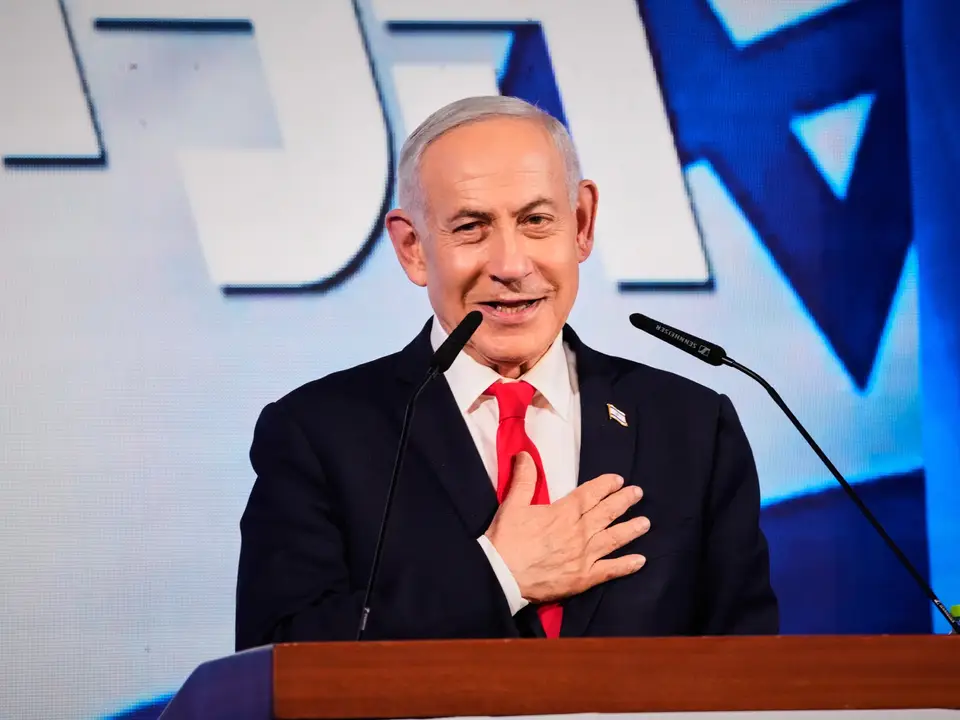
Netanyahu outlines achievements, future plans as Likud leads Israeli polls (opens the original article)
Netanyahu says the ‘true’ election results are due in one or two days, while Likud leads Israeli polls, according to the title and snippet.
Geopolitics Al Jazeera
Strategic relevanceElection results may clarify the political context for Israel’s leadership and future plans.
Sources1Al Jazeera
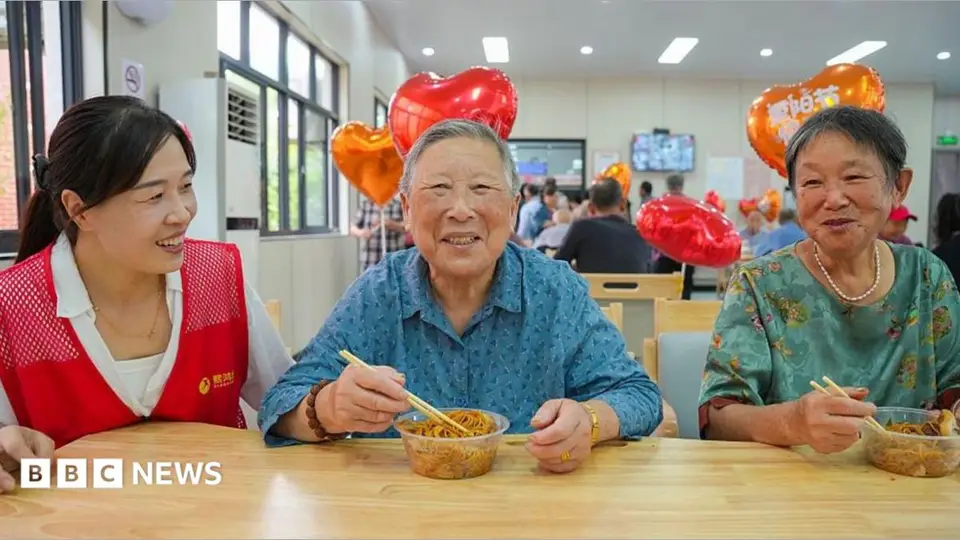
China's families are now supporting more old people than kids (opens the original article)
Latest figures mark a milestone as Beijing grapples with an ageing population and families support more older people than children.
Geopolitics BBC World
Strategic relevancePopulation age structure is relevant to understanding China's social and strategic context.
Sources1BBC World
| CVE | CVSS | Product | Ransomware | Added / due | Required action |
|---|---|---|---|---|---|
| CVE-2026-48356 | 9.3Critical | Adobe Commerce and Magento | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-111497 | 9.2Critical | Google Brotli | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-109618 | 9.2Critical | PHP Group PHP | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-109619 | 9.2Critical | PHP Group PHP | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-114625 | 9.4Critical | Arista VeloCloud Orchestrator | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-110447 | 9.2Critical | Collabora Collabora Online – Built-in CODE Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-106931 | 8.5High | EG Secure Solutions SiteGuard Server Edition | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-96656 | 8.6High | Plex Media Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-96655 | 5.3Medium | Plex Media Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-96654 | 6.9Medium | Plex Media Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-96652 | 5.3Medium | Plex Media Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-110936 | 8.4High | Siemens Software Center | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
Source: CISA KEV catalogue; CVSS scores from NVD where published. “No score” means NVD has not scored it yet.
Keyword index
Counted from this page. Select one to filter.