 OUTPOST
Edition 227 — 29 October 2026
Cyber, warfare technology and geopolitics as compiled on 29 October 2026.
Cyber
Breaches, campaigns, advisories and research.
Hitachi Energy CoreTec Product (opens the original article)
Hitachi Energy says OS command injection and Dirty Frag vulnerabilities affect its CoreTec product.
Cyber CISA Advisories
What to checkCheck whether CoreTec is in your environment and review the relevant advisory for mitigation guidance.
Sources1CISA Advisories
Siemens Mendix SAML Module (opens the original article)
The Mendix SAML module contains an authentication bypass vulnerability, according to the advisory snippet.
Cyber CISA Advisories
What to checkIdentify use of the Mendix SAML module and review authentication controls and the advisory.
Sources1CISA Advisories
Hitachi Energy TRO600 series products (opens the original article)
Hitachi Energy says multiple vulnerabilities affect TRO600 series products.
Cyber CISA Advisories
What to checkCheck for TRO600 products and consult the advisory for affected versions and recommended action.
Sources1CISA Advisories
Chrome extensions with 13.4 million installs caught hijacking searches (opens the original article)
BleepingComputer reports that 319 Chrome extensions with 13.4 million reported installations redirected searches through tracking servers to generate advertising revenue from Bing and Yahoo.
Cyber BleepingComputer
What to checkReview installed extensions, remove untrusted ones, and investigate unexpected search redirects.
Sources1BleepingComputer
Federal bankruptcy courts contractor says no data stolen during cyber intrusion (opens the original article)
BAE Systems says no data was extracted during its probe into a cyberattack on systems for federal bankruptcy courts.
Cyber The Record
What to checkCheck the contractor’s incident findings and monitor for updates about affected systems or data.
Sources1The Record
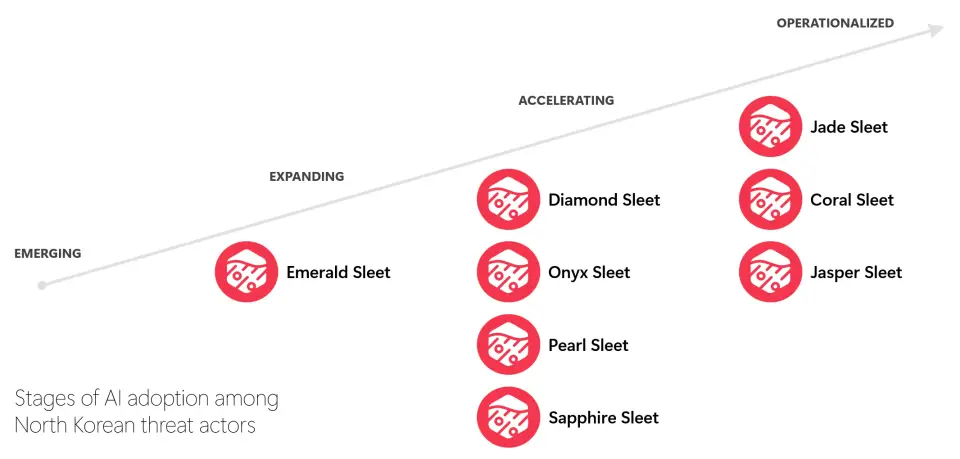
Tracking AI adoption in North Korean threat actor tradecraft (opens the original article)
Microsoft says North Korean threat actors are expanding their use of AI, with varying levels of adoption, to increase attack speed and efficiency.
Cyber Microsoft Security
What to checkReview threat intelligence for changes in reported attacker use of AI and update relevant detection guidance.
Sources1Microsoft Security
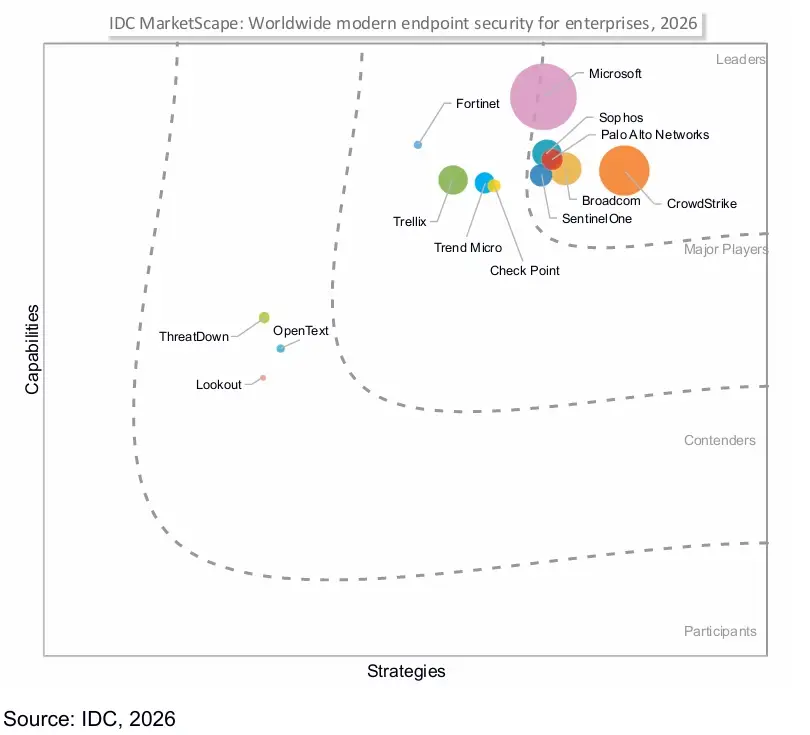
IDC MarketScape names Microsoft a Leader in the 2026 Worldwide Modern Endpoint Security for Enterprises Vendor Assessment (opens the original article)
IDC named Microsoft a Leader in its 2026 Worldwide Modern Endpoint Security for Enterprises Vendor Assessment.
Cyber Microsoft Security
What to checkTreat the assessment as vendor positioning; compare endpoint security claims with your organization’s needs.
Sources1Microsoft Security
Microsoft fixes Remote Desktop failures caused by recent Windows updates (opens the original article)
Microsoft says it resolved a known issue preventing non-admin users from connecting through Remote Desktop when Administrator protection is enabled.
Cyber BleepingComputer
What to checkCheck Remote Desktop access for non-admin users where Administrator protection is enabled.
Sources1BleepingComputer
3 Ways AI Agents Already Operate in Your Browser (opens the original article)
Keep Aware says AI agents can use authenticated browsers, corporate applications, and sensitive data while appearing to act as legitimate employees.
Cyber BleepingComputer
What to checkReview which agents can access authenticated browsers, corporate applications, and sensitive data.
Sources1BleepingComputer
CISA warns of Fragnesia Linux flaw chained in PHP2Shell attacks (opens the original article)
CISA warned federal agencies to patch a high-severity Linux kernel privilege escalation bug attackers are chaining with PHP2Shell flaws.
Cyber BleepingComputer
What to checkCheck for exposure to the Linux flaw and PHP2Shell, and prioritize patching.
Sources1BleepingComputer
Warfare
Drones, electronic warfare, missiles and defence systems.
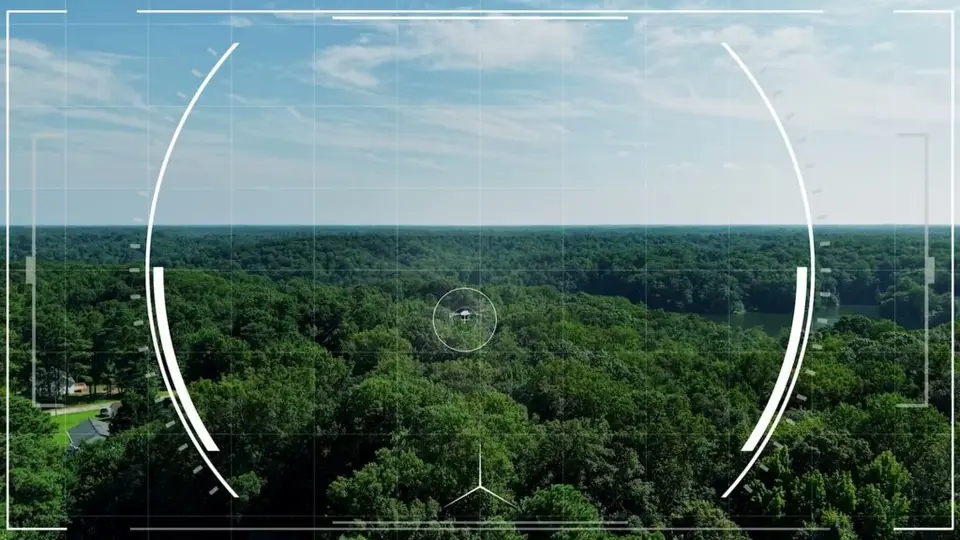
Giving counter-UAS operators 75 km of advance warning throws the advantage to them (opens the original article)
SkyValor says its RF detection extends counter-UAS warning range, giving operators more time to assess and respond to drone threats.
Warfare Breaking Defense
Why it mattersRF detection range can affect the time available to assess and respond to drone threats.
Sources1Breaking Defense
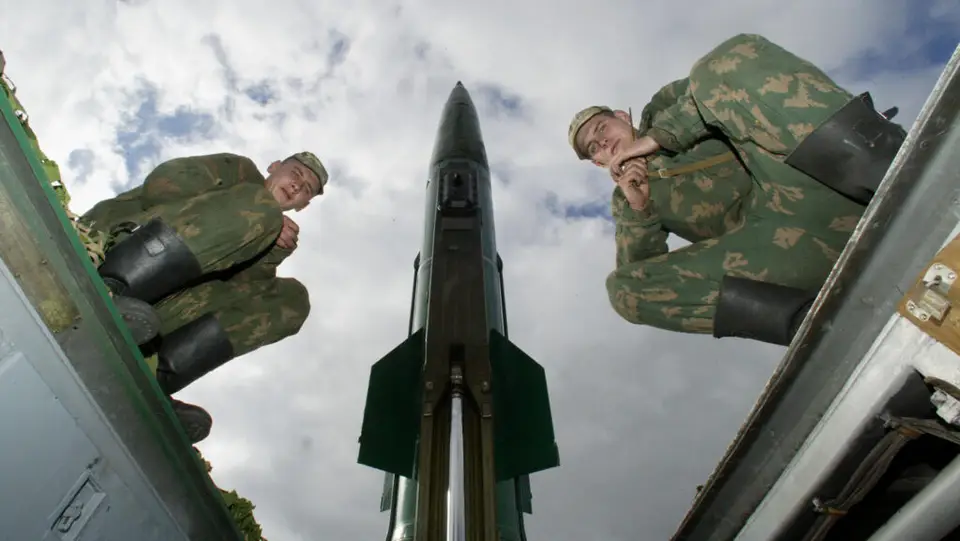
Kaliningrad is more than the Suwałki Gap, and NATO cannot ignore it (opens the original article)
Breaking Defense says Kaliningrad’s location challenges a neat division between frontline states and others, amid drones and long-range precision weapons.
Warfare Breaking Defense
Why it mattersKaliningrad’s location highlights the wider geographic relevance of European security planning.
Sources1Breaking Defense
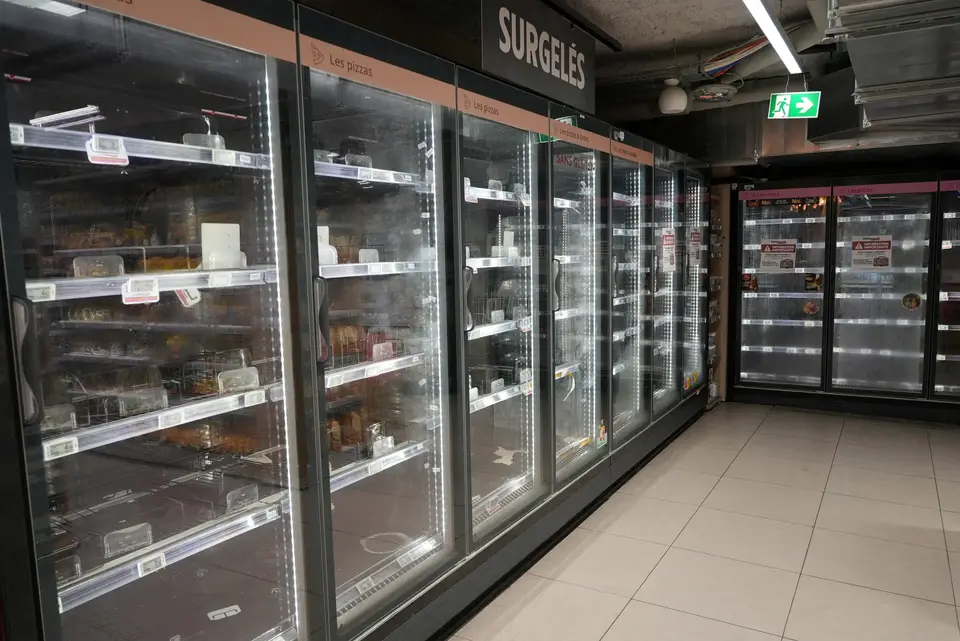
Pentagon treating military base freezer malfunctions as suspected cyberattack, officials say (opens the original article)
Defense News reports that the Pentagon is treating freezer malfunctions that spoiled food at US military bases in August as a suspected hack.
Warfare Defense News
Why it mattersThe report highlights the operational relevance of investigating suspected cyber incidents affecting military-base systems.
Sources1Defense News
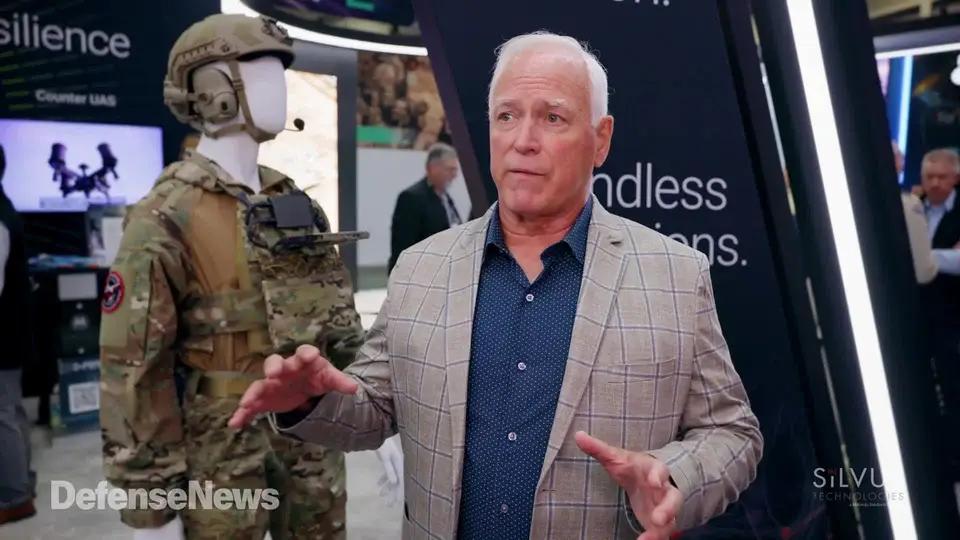
How Silvus Is Connecting Soldiers and Systems Across the Battlefield (opens the original article)
Silvus says tactical radios, threat detection and anti-jamming capabilities can help the Army maintain communications in contested environments.
Warfare Defense News
Why it mattersThese capabilities are relevant to maintaining battlefield communications when networks face disruption.
Sources1Defense News
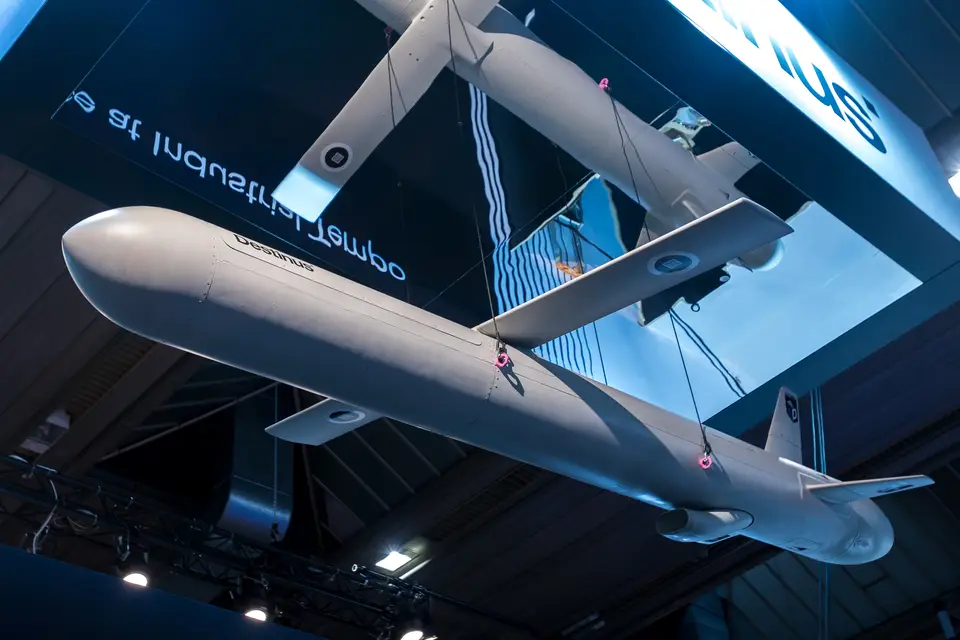
Destinus’ monthly output tops Europe’s pre-war annual cruise missile production (opens the original article)
Destinus says it has built more than 1,750 Ruta cruise missiles in Europe and now makes more in a month than Europe did annually before Russia's full-scale invasion of Ukraine.
Warfare Defense News
Why it mattersThe reported production scale is relevant to assessments of European cruise-missile manufacturing capacity.
Sources1Defense News
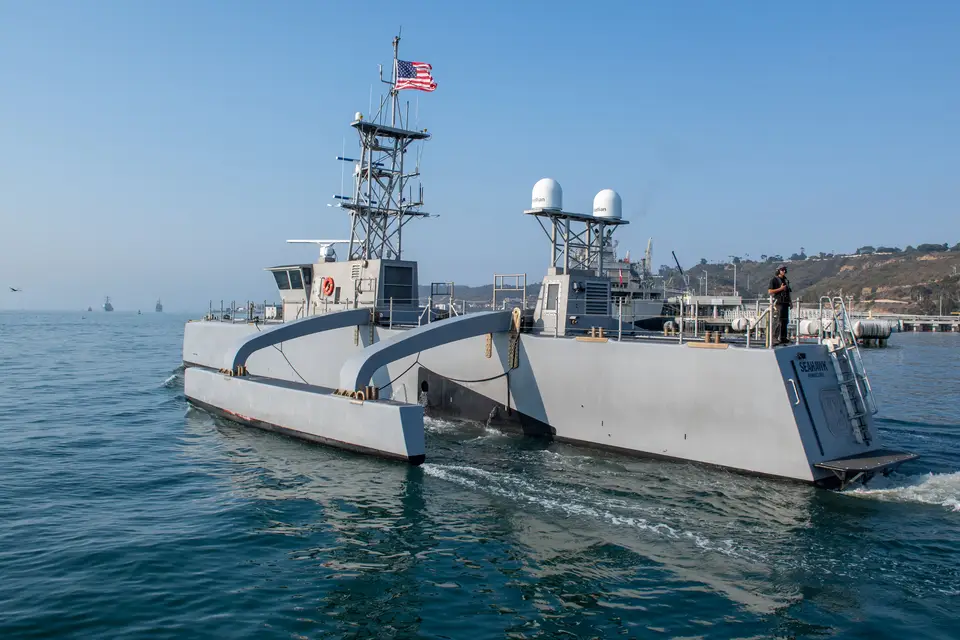
US Navy wants more visible role for drone boats as one deploys for the first time (opens the original article)
A senior U.S. Navy officer described the value medium unmanned surface vessels could bring to the fleet as one deploys for the first time.
Warfare Defense News
Why it mattersThe story concerns the potential fleet role of unmanned surface vessels.
Sources1Defense News

A Tale of Two Markets: A Dickensian Take on the Coming Years in Defense Tech (opens the original article)
War on the Rocks describes unease among defense technology investors and leaders despite headlines about capital, valuations, and budgets; production contracts remain elusive.
Warfare War on the Rocks
Why it mattersThe gap between funding and production contracts is relevant to assessing defense technology capacity.
Sources1War on the Rocks

Sitting Ducks or Strategic Shields: What Does the Small Reactor Promise Mean for Future Conflicts? (opens the original article)
The article says nuclear power is increasingly viewed as a reliable source to complement variable solar and hydropower as clean-energy demand rises.
Warfare War on the Rocks
Why it mattersReliable energy could matter to conflict planning where power supply is important.
Sources1War on the Rocks
Geopolitics & geodata
Strategy, geo wars, GNSS and satellite security.
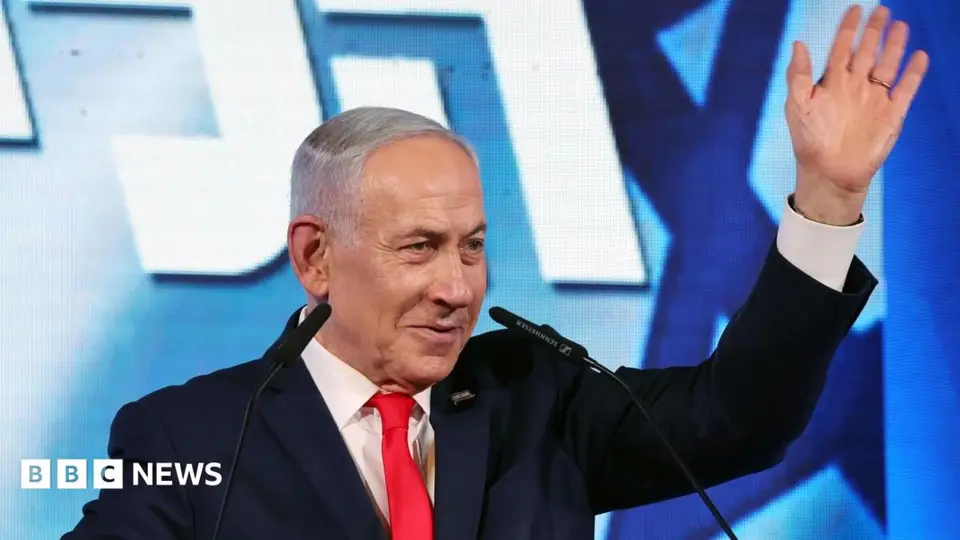
Netanyahu's bloc leading Israel election but short of majority, partial results show (opens the original article)
Partial results show Netanyahu's Likud party and allies set to win 53 of 120 Knesset seats, with 85% of ballots counted.
Geopolitics BBC World
Strategic relevanceThe partial count indicates the parliamentary balance remains relevant to forming a government.
Sources1BBC World
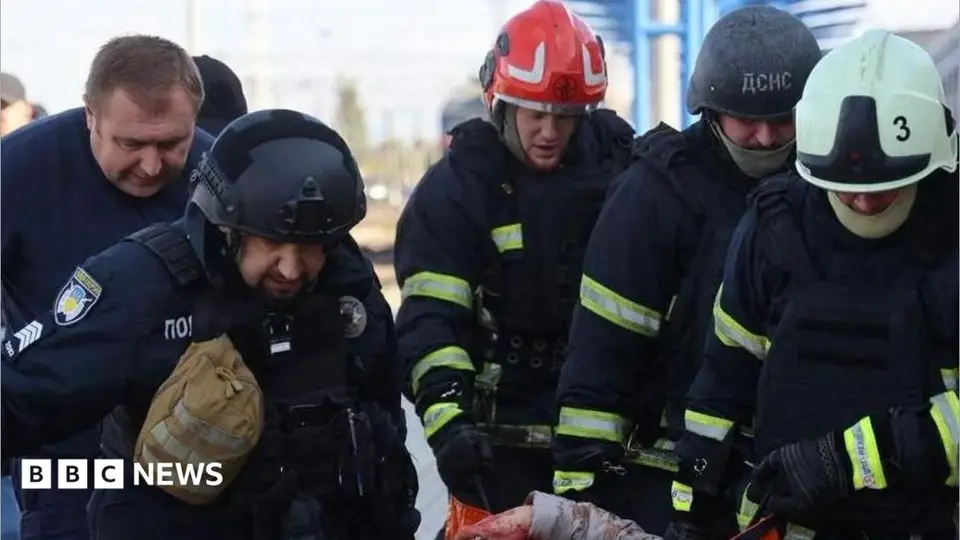
Russian drone attack on Ukrainian train station kills at least 14, officials say (opens the original article)
Dnipro regional head Oleksandr Hanzha said a Russian drone attack on a Ukrainian train station killed at least 13 people and wounded at least 10 others.
Geopolitics BBC World
Strategic relevanceThe attack highlights the human impact of drone strikes on transport locations.
Sources1BBC World
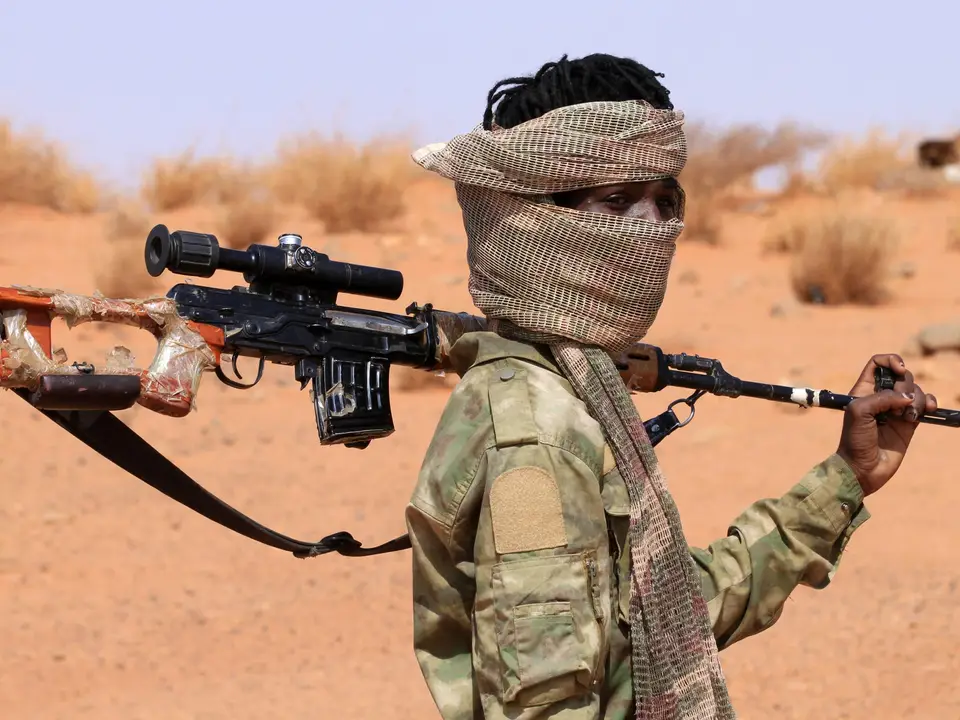
UAE sentences eight people to life over arms supplies to Sudan’s army (opens the original article)
Defendants handed life sentences amid tensions between Khartoum and Abu Dhabi over Sudan's war and the RSF.
Geopolitics Al Jazeera
Sources1Al Jazeera
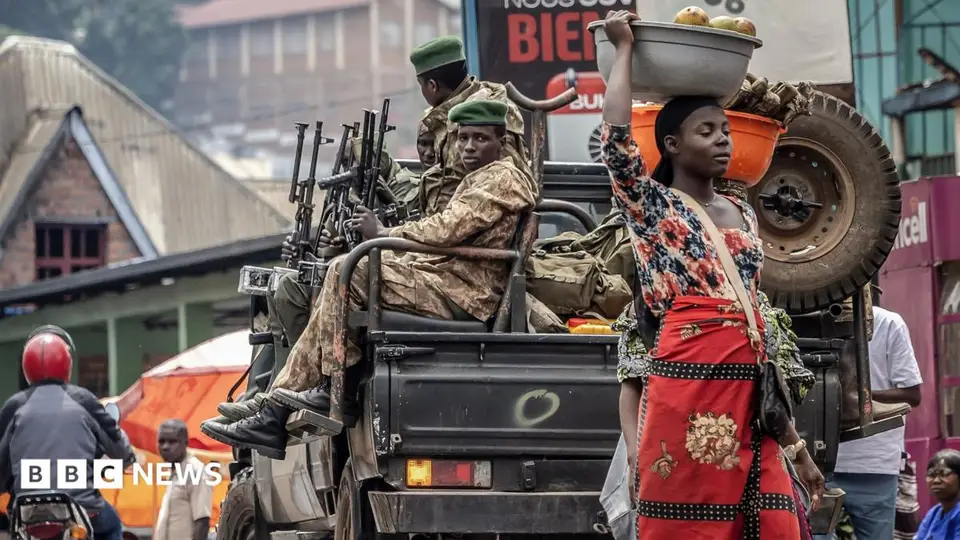
US sanctions Rwanda's defence ministry over DR Congo conflict (opens the original article)
The U.S. sanctioned Rwanda's defence ministry over the DR Congo conflict. Congo accuses Rwanda of backing M23 rebels and plundering minerals.
Geopolitics BBC World
Strategic relevanceThe sanctions connect the conflict with regional security and mineral interests.
Sources1BBC World
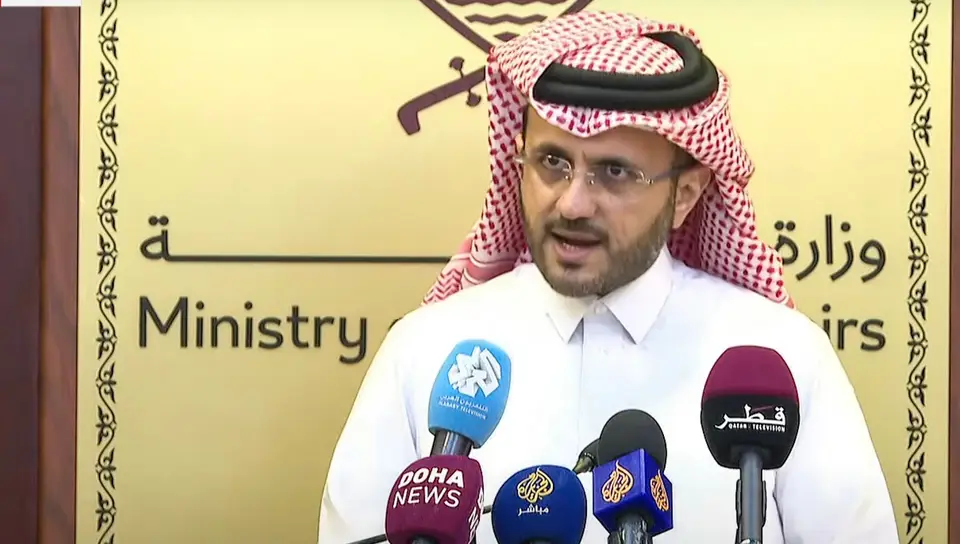
Israel’s anti-Qatar campaign bleeds into elections (opens the original article)
Qatar's Foreign Ministry spokesman rejects claims of disinformation amid allegations by some Israelis of voting interference.
Geopolitics Al Jazeera
Strategic relevanceThe dispute highlights competing claims around elections and information.
Sources1Al Jazeera
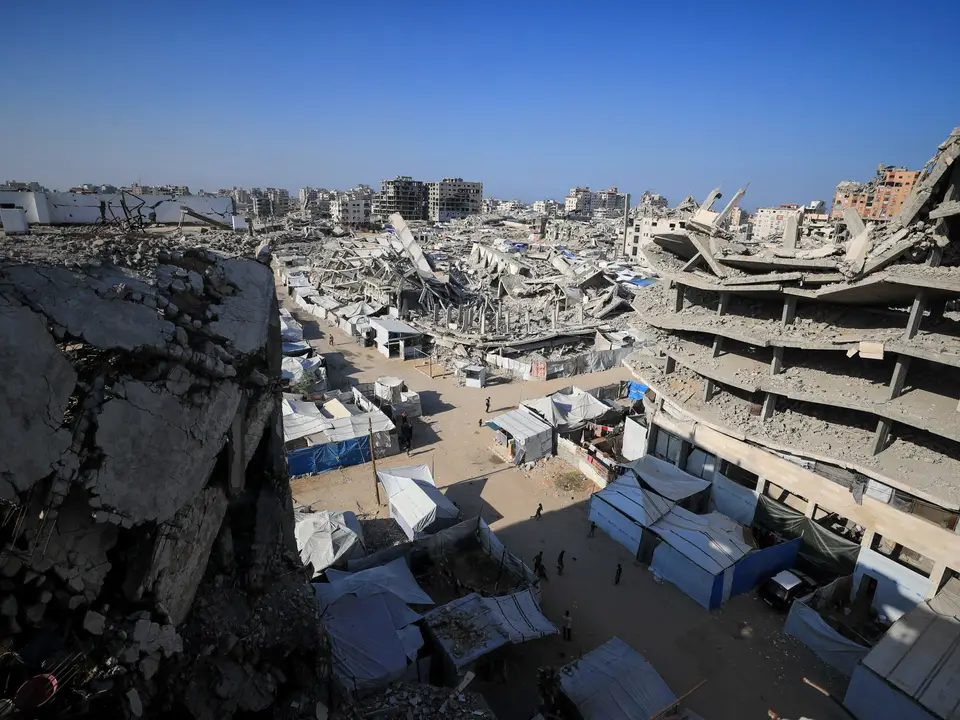
Israeli strikes hit Gaza as Health Ministry urges Rafah opening (opens the original article)
Gaza's Health Ministry says dozens died awaiting treatment abroad as Israeli attacks continue despite a 'ceasefire.'
Geopolitics Al Jazeera
Strategic relevanceThe report links the conflict to access to medical treatment and conditions in Rafah.
Sources1Al Jazeera
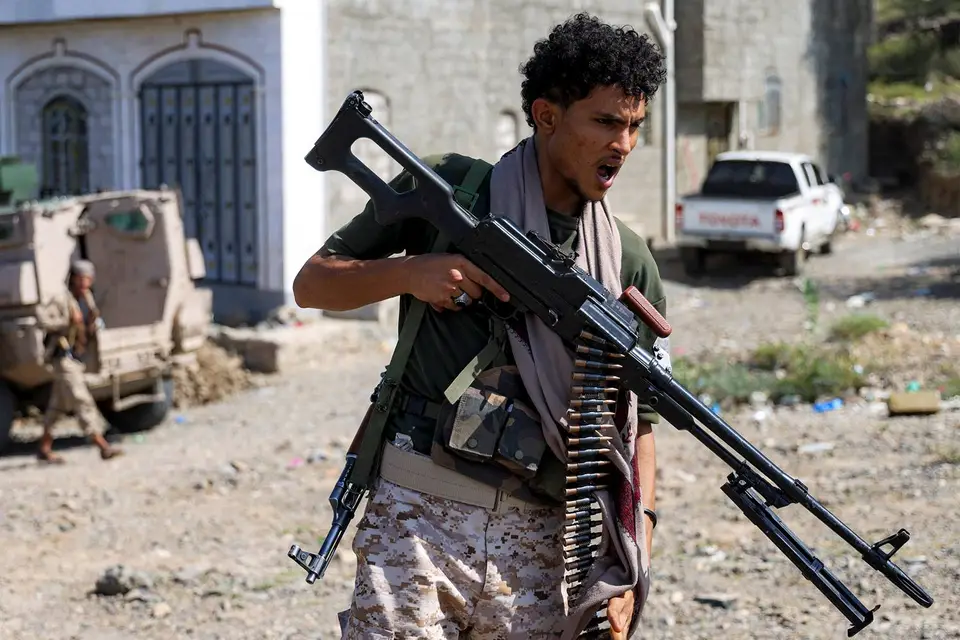
Is the UAE the Missing Link in the Fight Against the Houthis? (opens the original article)
A leading Yemen expert says reconciliation between Riyadh and Abu Dhabi could be a gamechanger in the fight against the Houthis.
Geopolitics Foreign Policy
Strategic relevanceWatch how Saudi-Emirati relations may affect regional coordination on the Houthis.
Sources1Foreign Policy
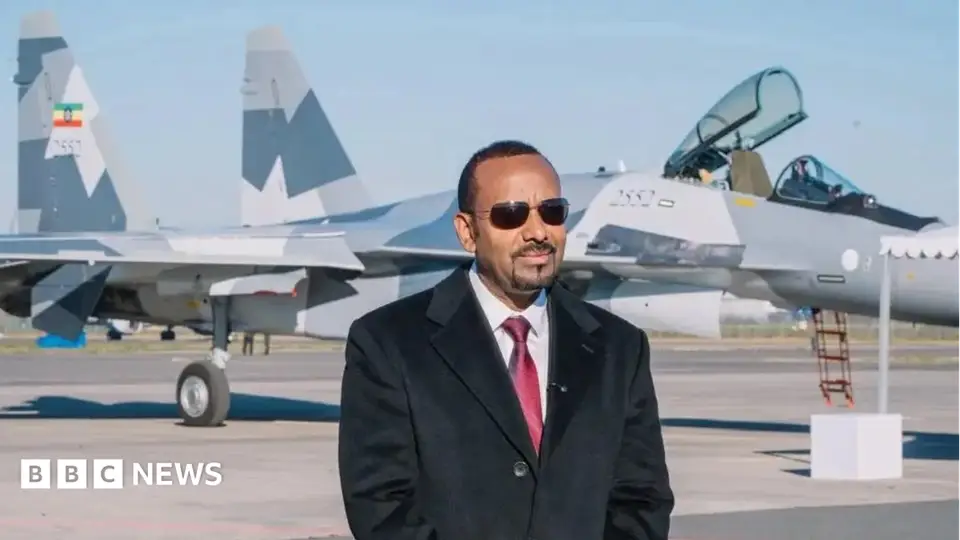
Ethiopia acquires Russian fighter jets and air defence systems amid war in Tigray (opens the original article)
BBC World reports that Ethiopia acquired Russian fighter jets and air defence systems amid ongoing fighting in northern Tigray.
Geopolitics BBC World
Strategic relevanceThe acquisition is relevant to military capabilities amid fighting in the region.
Sources1BBC World
| CVE | CVSS | Product | Ransomware | Added / due | Required action |
|---|---|---|---|---|---|
| CVE-2026-41709 | 2.7Low | Broadcom VMware ESX | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-46300 | 7.8High | Linux Kernel | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-48356 | 9.3Critical | Adobe Commerce and Magento | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-111497 | 9.2Critical | Google Brotli | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-109618 | 9.2Critical | PHP Group PHP | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-109619 | 9.2Critical | PHP Group PHP | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-114625 | 9.4Critical | Arista VeloCloud Orchestrator | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-110447 | 9.2Critical | Collabora Collabora Online – Built-in CODE Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-106931 | 8.5High | EG Secure Solutions SiteGuard Server Edition | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-96656 | 8.6High | Plex Media Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-96655 | 5.3Medium | Plex Media Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-96654 | 6.9Medium | Plex Media Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
Source: CISA KEV catalogue; CVSS scores from NVD where published. “No score” means NVD has not scored it yet.
Keyword index
Counted from this page. Select one to filter.