 OUTPOST
Edition 228 — 30 October 2026
Cyber, warfare technology and geopolitics as compiled on 30 October 2026.
Cyber
Breaches, campaigns, advisories and research.
Hitachi Energy CoreTec Product (opens the original article)
Hitachi Energy says OS command injection and Dirty Frag vulnerabilities affect its CoreTec product.
Cyber CISA Advisories
What to checkCheck whether CoreTec is in your environment and review the relevant advisory for mitigation guidance.
Sources1CISA Advisories
CISA Adds Two Known Exploited Vulnerabilities to Catalog (opens the original article)
CISA says it added two vulnerabilities to its Known Exploited Vulnerabilities Catalog based on evidence of active exploitation.
Cyber CISA Advisories
What to checkCheck whether affected systems are present and prioritize mitigation using CISA’s KEV Catalog.
Sources1CISA Advisories
Hitachi Energy TRO600 series products (opens the original article)
Hitachi Energy says multiple vulnerabilities affect TRO600 series products.
Cyber CISA Advisories
What to checkCheck for TRO600 products and consult the advisory for affected versions and recommended action.
Sources1CISA Advisories
Siemens Mendix SAML Module (opens the original article)
The Mendix SAML module contains an authentication bypass vulnerability, according to the advisory snippet.
Cyber CISA Advisories
What to checkIdentify use of the Mendix SAML module and review authentication controls and the advisory.
Sources1CISA Advisories
OpenAI doubles ChatGPT Pro usage limits after backlash over planned 50% cut (opens the original article)
OpenAI says it will keep usage limits unchanged for ChatGPT Pro and Business Premium plans, and keep Dots usage independent.
Cyber BleepingComputer
What to checkFor teams using these plans, check whether usage limits affect service availability or operational planning.
Sources1BleepingComputer
Threat Brief: Critical Vulnerabilities in PHP: CVE-2026-109618, CVE-2026-109619 (Updated October 29) (opens the original article)
Unit 42 identifies CVE-2026-109618 and CVE-2026-109619 as critical PHP vulnerabilities affecting software used for web servers and CMS systems.
Cyber Unit 42
What to checkCheck PHP-based web servers and CMS systems for exposure and patches.
Sources1Unit 42
Binance probes potential $5.8 billion crypto-theft hack (opens the original article)
Binance is investigating a potential security breach involving up to $5.8 billion in digital assets, BleepingComputer reports.
Cyber BleepingComputer
What to checkDefenders should monitor relevant accounts and transaction activity while Binance investigates.
Sources1BleepingComputer
Hugging Face malware campaign returns to hijack GPUs for crypto mining (opens the original article)
BleepingComputer reports a crypto-mining campaign abusing Hugging Face models has returned after a takedown, hijacking GPU servers and planting backdoors. A model was downloaded over 28,000 times.
Cyber BleepingComputer
What to checkCheck GPU servers for unauthorized mining and backdoors, and review the models and packages used by AI tools.
Sources1BleepingComputer
Japan Airlines suffers third-party data breach exposing passenger info (opens the original article)
Japan Airlines says a breach at Amadeus's Passenger Service System exposed data belonging to about 92,000 customers.
Cyber BleepingComputer
What to checkReview third-party access and incident procedures for systems handling passenger information.
Sources1BleepingComputer
Polymarket halts trading after crypto-draining script breach, $2.5M traced (opens the original article)
BleepingComputer reports Polymarket suspended trading after hackers used a compromised third-party service to distribute cryptocurrency-draining JavaScript; about $2.5 million in assets was traced to a suspected attacker wallet.
Cyber BleepingComputer
What to checkCheck third-party services and review JavaScript delivered to users for unauthorized changes.
Sources1BleepingComputer
Warfare
Drones, electronic warfare, missiles and defence systems.
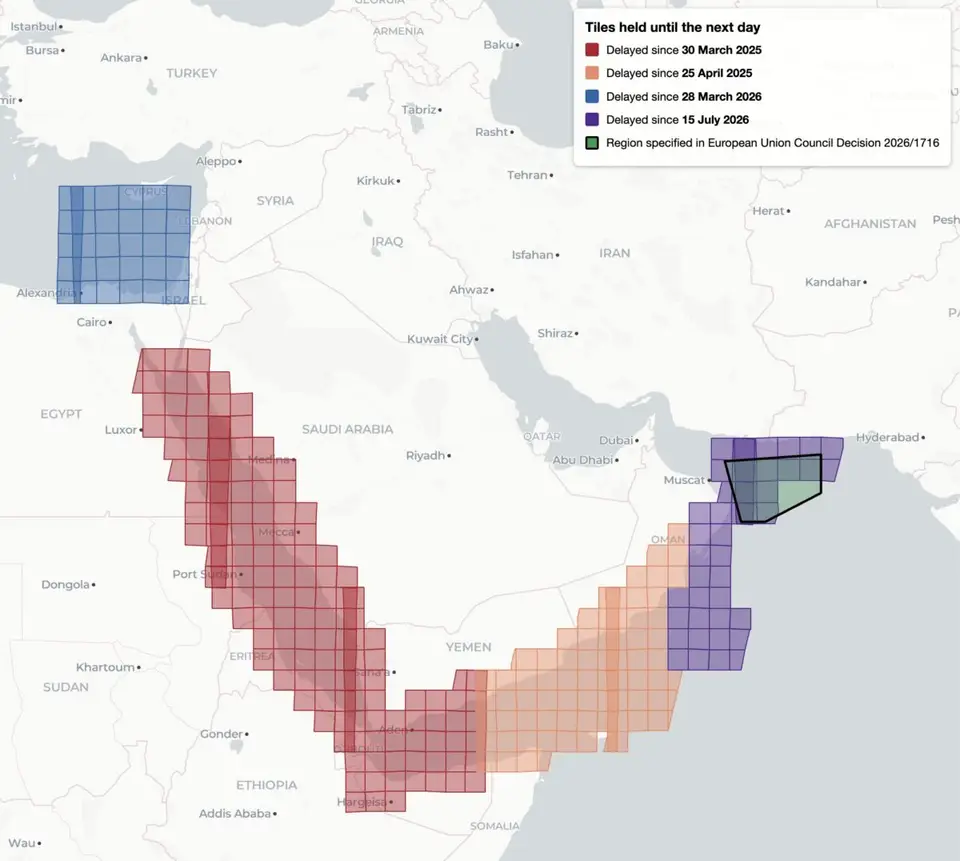
EU Satellite Imagery Delayed Over Gaza and Parts of West Bank by 24-hours (opens the original article)
Bellingcat reports that EU satellite imagery over Gaza and parts of the West Bank is delayed by 24 hours. Its snippet refers to imagery from freely available Sentinel satellites.
Warfare Bellingcat
Why it mattersThe delay matters to analysts relying on satellite imagery for timely geospatial assessment.
Sources1Bellingcat
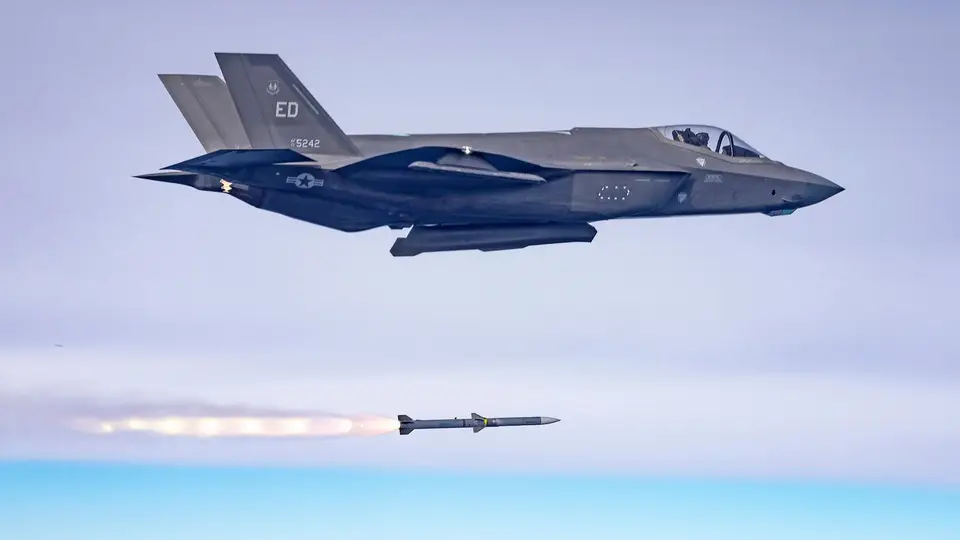
Japan To Assemble AMRAAM Missiles As U.S. Moves To Dramatically Boost AIM-120 Production (opens the original article)
The report says Japan will assemble AMRAAM missiles as the U.S. boosts AIM-120 production; Washington and Tokyo also seek to accelerate SM-3 Block IIA interceptor production.
Warfare The War Zone
Why it mattersMissile assembly and production plans are relevant to regional defense capacity and supply.
Sources1The War Zone
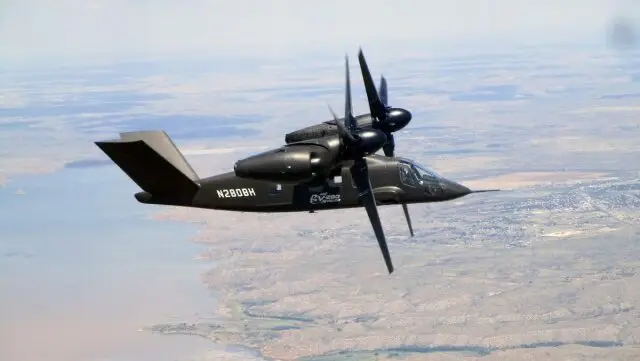
Army’s MV-75 production award could slip due to CR, raising program costs: Textron (opens the original article)
Bell Textron executives warned that a delay in the MV-75 helicopter’s first low-rate production contract could increase the program’s expected financial hit to as much as $150 million.
Warfare Breaking Defense
Why it mattersContract timing may affect the program’s production schedule and expected costs.
Sources1Breaking Defense
Beyond autopilot: Understanding the five levels of battlefield drone autonomy (opens the original article)
The sponsored article says drones can perform tasks with minimal operator input when they go beyond simple automation.
Warfare Breaking Defense
Why it mattersLevels of autonomy help frame how much operator input battlefield drone tasks require.
Sources1Breaking Defense
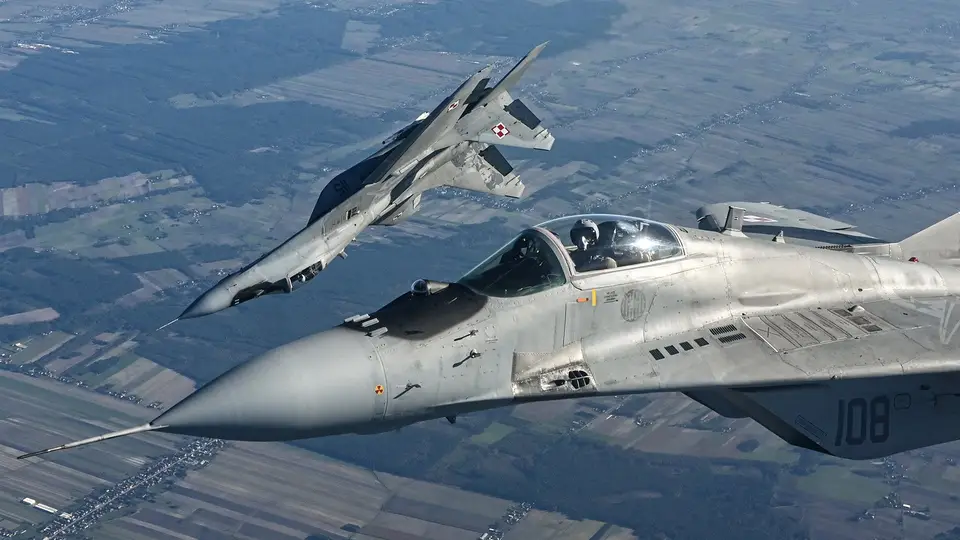
Polish MiG-29s, F-16 Cannon Ammo Reportedly Headed To Ukraine As Bitter Warsaw-Kyiv Rift Heals (opens the original article)
The War Zone reports that Polish MiG-29s and F-16 cannon ammunition are headed to Ukraine; the snippet says relations had soured and the MiG-29 deal was called off.
Warfare The War Zone
Why it mattersReported aircraft and ammunition transfers are relevant to military support and Ukraine-Poland relations.
Sources1The War Zone
What Israel’s Election Results Mean for the Middle East and Beyond (opens the original article)
War on the Rocks says neither Netanyahu’s bloc nor the opposition alliance won enough Knesset seats to form a government after Israel’s election.
Warfare War on the Rocks
Why it mattersThe result may shape regional politics; watch how the opposition responds to its choice.
Sources1War on the Rocks
What’s a Revolution in Military Affairs Good For? (opens the original article)
War on the Rocks examines what makes a revolution in military affairs revolutionary, and whether current change is about drones and AI or something broader.
Warfare War on the Rocks
Why it mattersThe debate helps analysts assess whether emerging technologies are changing military practice or are only part of a wider shift.
Sources1War on the Rocks
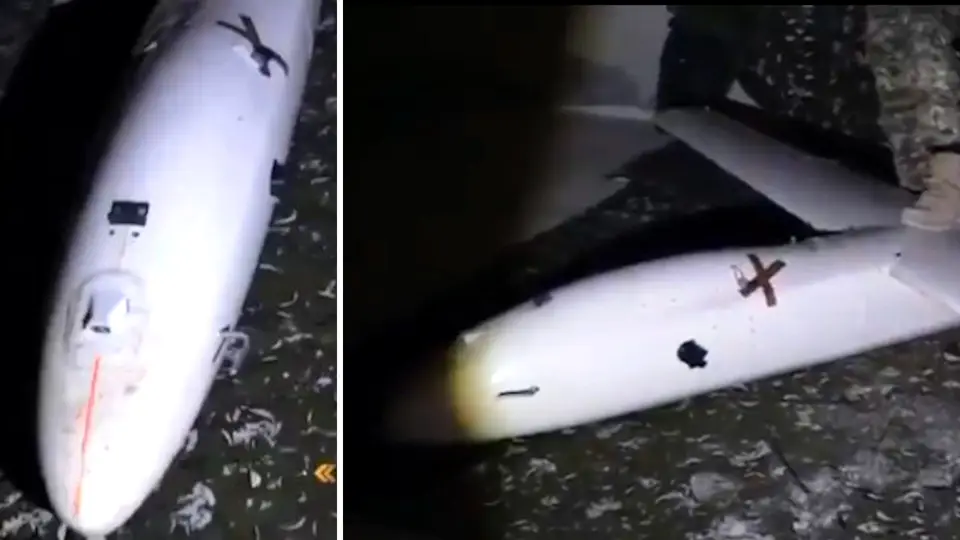
Let’s Talk About The U.S. Target Drone Iran Claims To Have Recovered Intact (opens the original article)
The War Zone says the target drone Iran claims to have recovered intact could help stimulate its air defenses and collect intelligence on them.
Warfare The War Zone
Why it mattersThe drone could serve as a tool for testing air defenses and gathering intelligence.
Sources1The War Zone
Geopolitics & geodata
Strategy, geo wars, GNSS and satellite security.
ION GNSS+ 2026: Trust, Resilience and a Sky Getting Fuller (opens the original article)
Inside GNSS says jamming, spoofing, cyber vulnerabilities and unexpected signal failures are exposing weaknesses in GNSS systems operating in a hostile, complex environment.
Geopolitics Inside GNSS
Strategic relevanceGNSS resilience matters to systems that rely on satellite signals; check fallback and failure-handling arrangements.
Sources1Inside GNSS
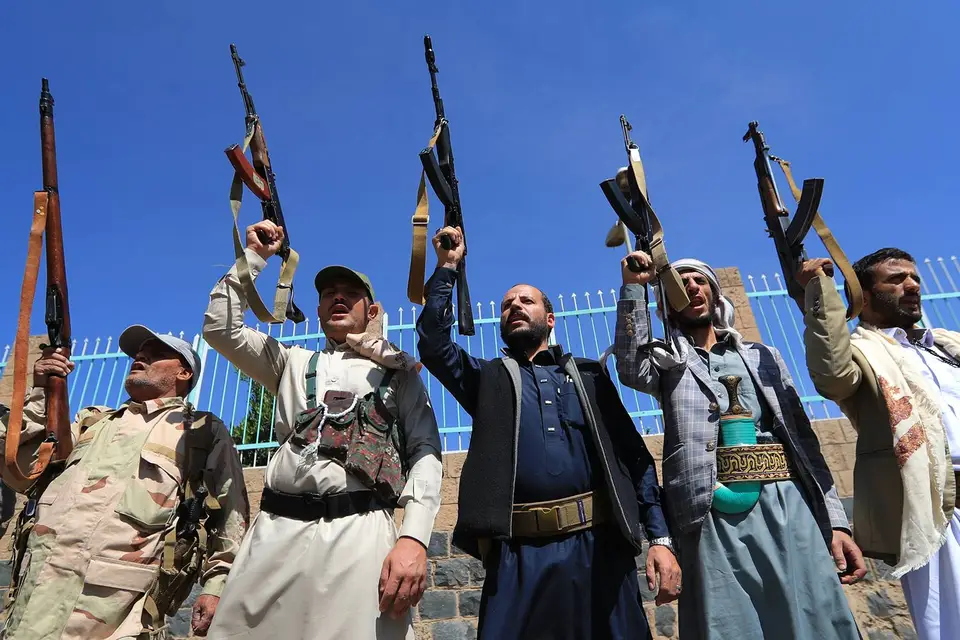
How Big of a Threat Are the Houthis? (opens the original article)
Foreign Policy reports that the Saudi ambassador to the U.S. compared the Houthis to the Islamic State.
Geopolitics Foreign Policy
Strategic relevanceThe comparison offers insight into how a Saudi official frames the Houthis as a security concern.
Sources1Foreign Policy
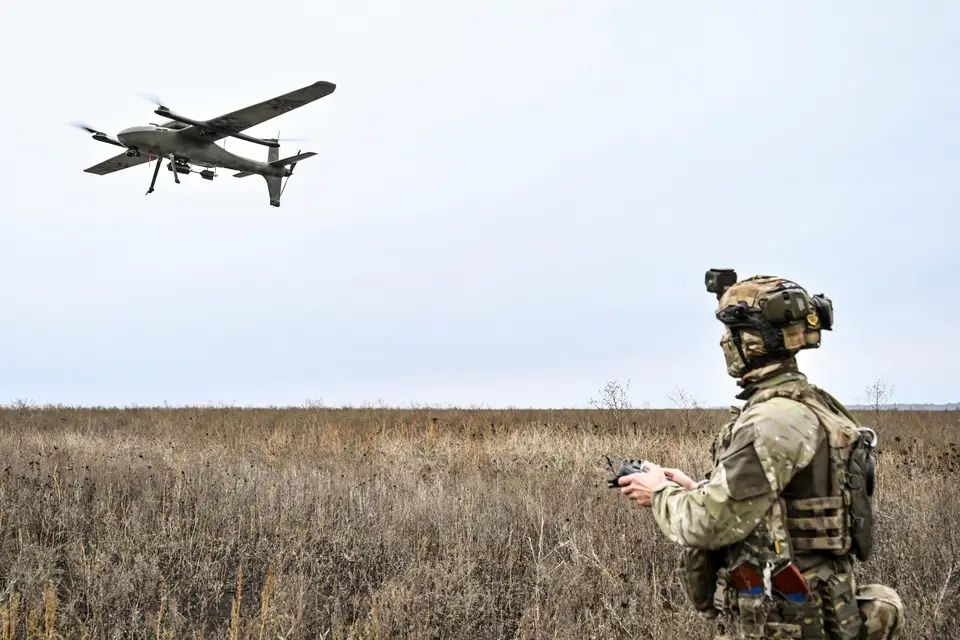
Ukraine’s drone defenses debunk the myth of inevitable Russian victory (opens the original article)
Mykola Bielieskov argues that Ukraine’s drone-based air defenses have received less attention than their battlefield role warrants.
Geopolitics Atlantic Council
Strategic relevanceDrone-based air defense highlights how drones can shape battlefield operations.
Sources1Atlantic Council
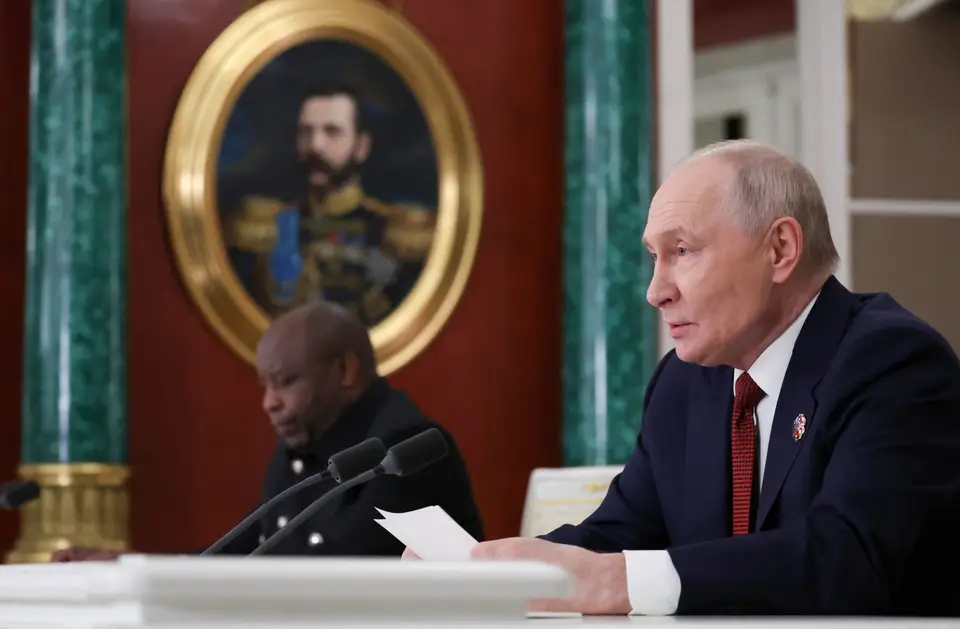
Putin’s quest to reclaim ‘historical Russian lands’ is a recipe for endless war (opens the original article)
Peter Dickinson writes that Putin's claim that Ukraine is historically Russian land reflects imperial ambitions and risks endless war.
Geopolitics Atlantic Council
Strategic relevanceThe claim frames the conflict as a contest over territory and historical narratives.
Sources1Atlantic Council
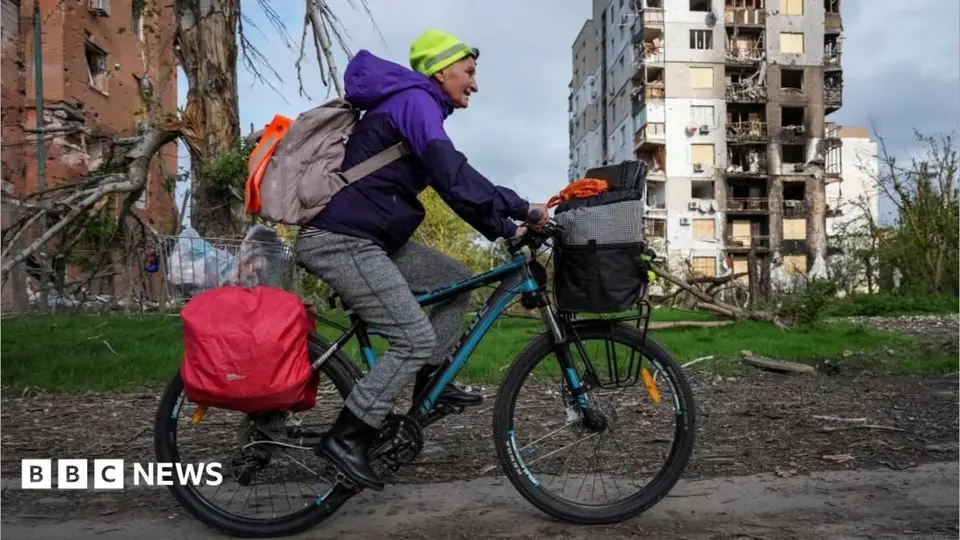
'The city is alive': A brief peace in Kherson, but residents fear what comes next (opens the original article)
A temporary ceasefire has brought rare quiet to Kherson, giving residents a glimpse of normal life before fighting resumes.
Geopolitics BBC World
Strategic relevanceThe pause shows how ceasefires can change conditions for residents in a contested city.
Sources1BBC World
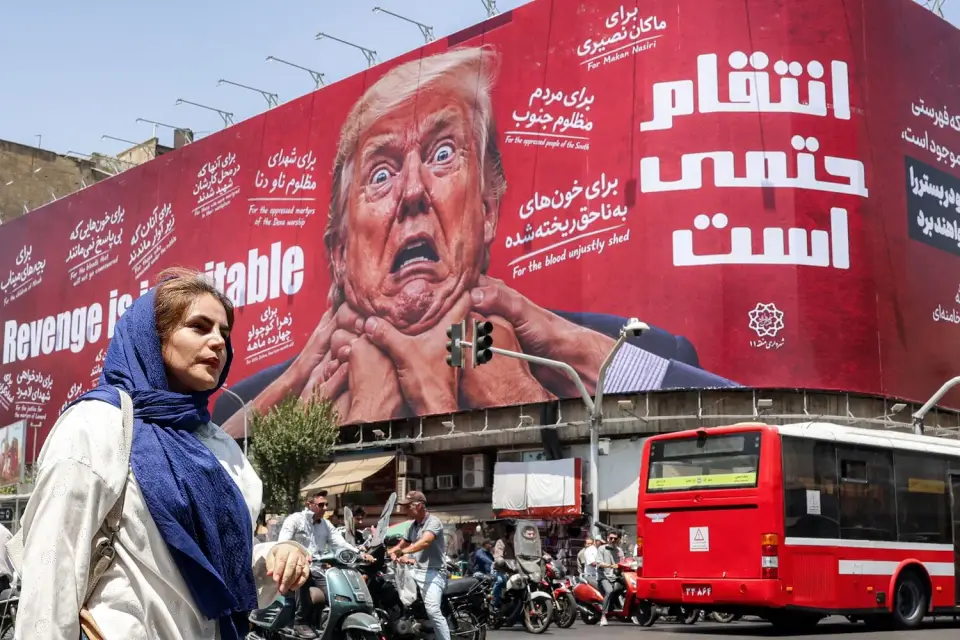
A New War on Iran Would Deal a Death Blow to U.S. Leadership in the Mideast (opens the original article)
Foreign Policy says Netanyahu and Trump appear to be planning another round of war on Iran, which the headline says would harm U.S. leadership in the Middle East.
Geopolitics Foreign Policy
Strategic relevanceThe article frames a possible conflict as relevant to regional strategy and U.S. leadership.
Sources1Foreign Policy
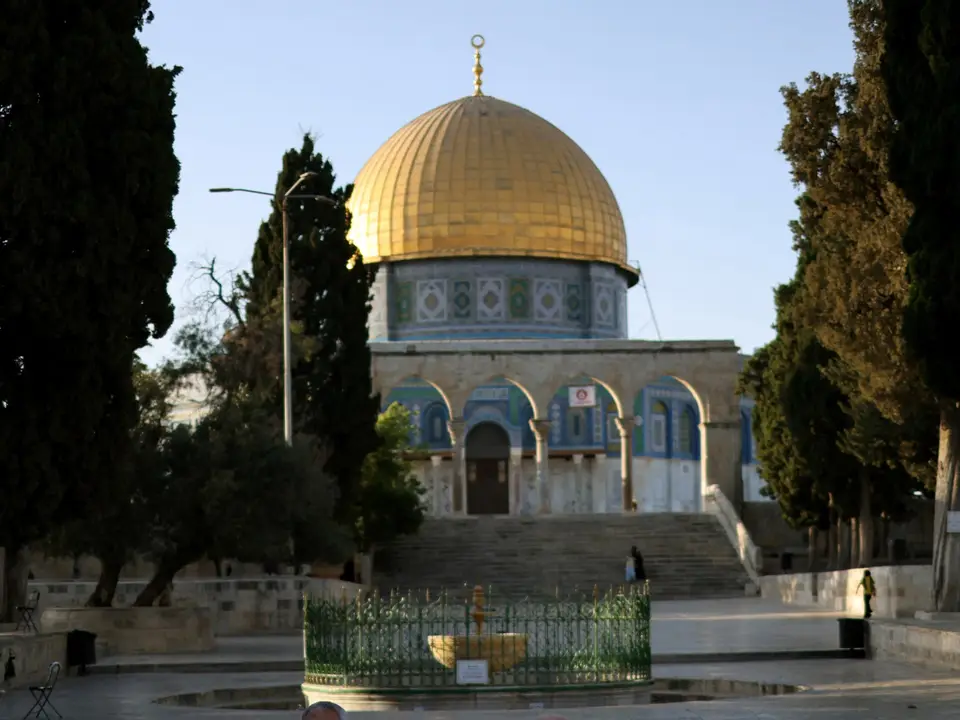
Palestinians face growing bans from Al-Aqsa as Israel tightens control (opens the original article)
Al Jazeera reports that Israel renewed a ban on the Al-Aqsa imam; Islamic Waqf officials warn that their authority at the Muslim holy site is shrinking.
Geopolitics Al Jazeera
Strategic relevanceThe reported restrictions and concerns center on authority at a strategically and religiously significant site.
Sources1Al Jazeera
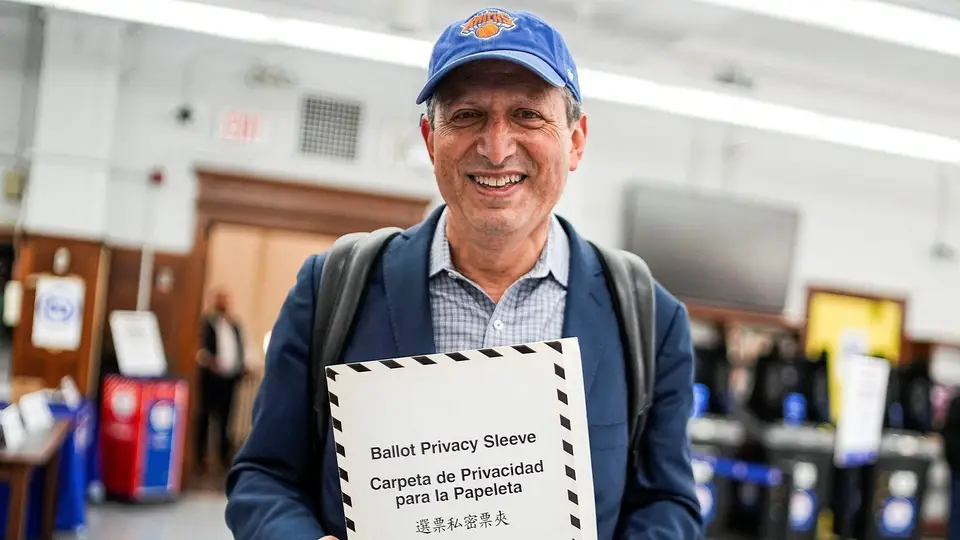
Israel bans travel for Brad Lander after detention in occupied West Bank (opens the original article)
Al Jazeera reports that Israel revoked travel authorisation for U.S. Democratic congressional candidate Brad Lander after his detention in the occupied West Bank.
Geopolitics Al Jazeera
Strategic relevanceTravel authorisation is a point of control over movement in the reported context.
Sources1Al Jazeera
| CVE | CVSS | Product | Ransomware | Added / due | Required action |
|---|---|---|---|---|---|
| CVE-2026-97229 | 10.0Critical | GitLab Community Edition and Enterprise Edition | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-76418 | 8.6High | Cisco Secure Firewall ASA Software and Cisco Secure FTD Software | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-41709 | 2.7Low | Broadcom VMware ESX | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-46300 | 7.8High | Linux Kernel | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-48356 | 9.3Critical | Adobe Commerce and Magento | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-111497 | 9.2Critical | Google Brotli | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-109618 | 9.2Critical | PHP Group PHP | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-109619 | 9.2Critical | PHP Group PHP | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-114625 | 9.4Critical | Arista VeloCloud Orchestrator | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-110447 | 9.2Critical | Collabora Collabora Online – Built-in CODE Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-106931 | 8.5High | EG Secure Solutions SiteGuard Server Edition | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-96656 | 8.6High | Plex Media Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
Source: CISA KEV catalogue; CVSS scores from NVD where published. “No score” means NVD has not scored it yet.
Keyword index
Counted from this page. Select one to filter.