 OUTPOST
Edition 229 — 31 October 2026
Cyber, warfare technology and geopolitics as compiled on 31 October 2026.
Cyber
Breaches, campaigns, advisories and research.
CISA Adds Two Known Exploited Vulnerabilities to Catalog (opens the original article)
CISA added two vulnerabilities to its Known Exploited Vulnerabilities Catalog, citing evidence of active exploitation.
Cyber CISA Advisories
What to checkCheck whether affected systems are present and prioritize the catalogued vulnerabilities.
Sources1CISA Advisories
Critical Linux kernel flaw allows remote root attacks on MPTCP servers (opens the original article)
Researchers at Anthropic developed an exploit for a critical Linux kernel vulnerability that allows unauthenticated remote command execution as root on servers running MPTCP.
Cyber BleepingComputer
What to checkCheck whether Linux servers run MPTCP and assess exposure to unauthenticated remote attacks.
Sources1BleepingComputer
Official Claude Code Extension on Cursor Marketplace Trojanized with Persistent SSH Backdoor (opens the original article)
Researchers disclosed that a trojanized version of Anthropic's official Claude Code extension was distributed through the Cursor Marketplace as a legitimate update, attempting to install a persistent SSH backdoor.
Cyber The Hacker News 2 outlets
What to checkCheck extension provenance and systems for unexpected SSH persistence.
DOJ raises privacy concerns over potential sale of Character.AI chats (opens the original article)
The DOJ’s Executive Office for U.S. Trustees says a consumer privacy ombudsman is needed to advise a court on terms for selling Character.AI data.
Cyber The Record
What to checkReview what user data may be retained, shared, or sold, and how those terms are disclosed.
Sources1The Record
Fashion retailer Resolve says hackers stole payment card information (opens the original article)
Resolve says a recent hack exposed customer payment card numbers.
Cyber The Record
What to checkPayment teams should assess potential card exposure and follow their incident response procedures.
Sources1The Record
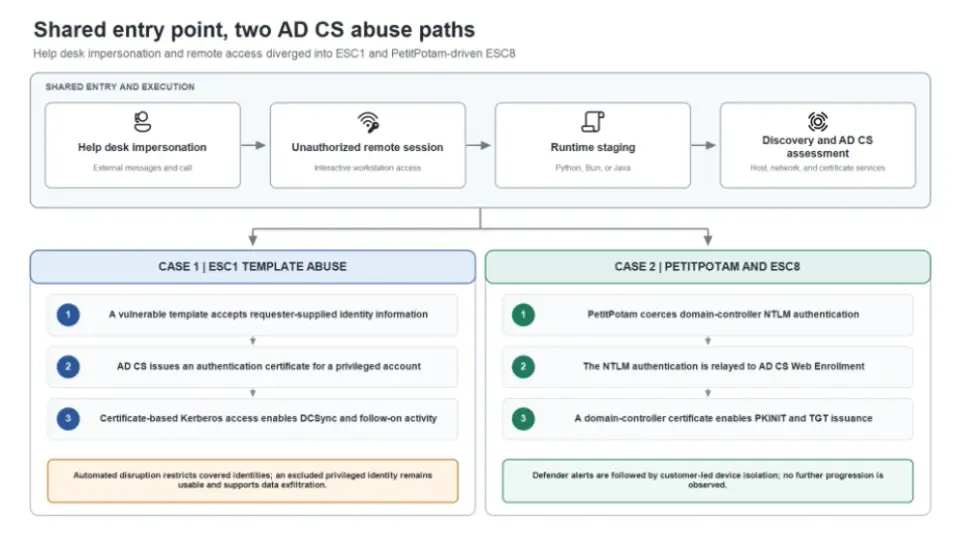
From help desk impersonation to AD CS abuse: Investigating ESC1 and ESC8 intrusion paths (opens the original article)
The post describes Teams support impersonation leading to remote access, malicious runtime execution, and AD CS abuse through authentication relay and Kerberos.
Cyber Microsoft Security
What to checkReview help desk verification, certificate services, and authentication relay exposure.
Sources1Microsoft Security
Trezor warns of suspected crypto-theft implant in hardware wallet (opens the original article)
Trezor says it received credible reports of a suspected crypto-theft implant in a Trezor Safe 5 sold by reseller CryptoBilis in Southeast Asia.
Cyber BleepingComputer
What to checkBuyers should check device provenance and follow Trezor's guidance.
Sources1BleepingComputer
Florida warns that 4.9 million people had Social Security numbers leaked in financial aid site breach (opens the original article)
Florida’s Department of Education said it became aware of a breach involving the Florida Student Financial Aid website on October 19. The title says 4.9 million people had Social Security numbers leaked.
Cyber The Record
What to checkReview exposure and response procedures for sensitive personal data.
Sources1The Record
Malicious Claude Code extension on Cursor planted SSH backdoors (opens the original article)
A malicious Claude Code extension distributed through Cursor's marketplace for about 11 hours exposed up to 5,000 developers to malware designed to install persistent SSH backdoors.
Cyber BleepingComputer
What to checkCheck installed extensions and investigate unexpected SSH access or persistence.
Sources1BleepingComputer
Syrian Electronic Army hacker gets prison time for attacks on Western targets (opens the original article)
Ahmad Umar Agha, known as “Th3Pr0,” was sentenced to 42 months for his role in a conspiracy organized by former Syrian President Bashar al-Assad's closest advisers.
Cyber The Record
What to checkThe case illustrates the legal consequences of cyberattacks on Western targets.
Sources1The Record
Warfare
Drones, electronic warfare, missiles and defence systems.
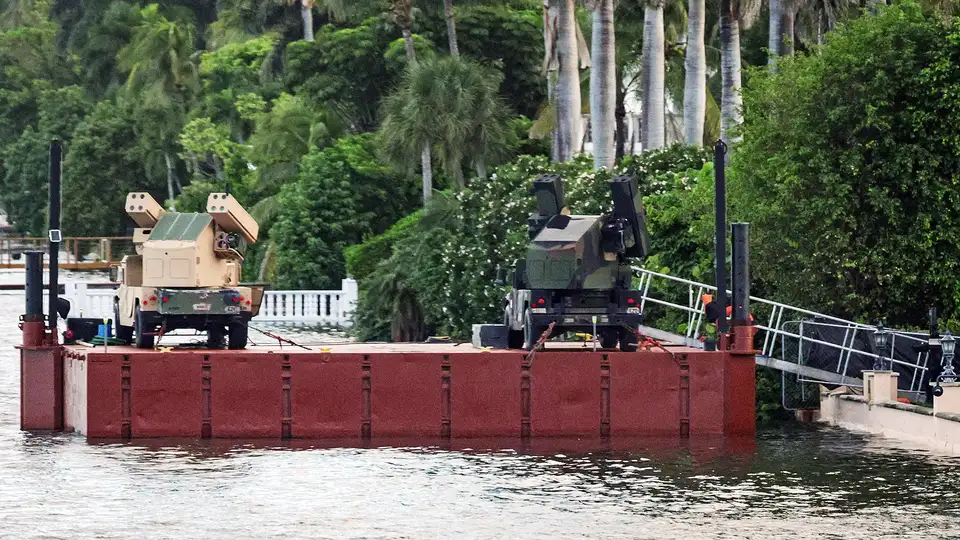
Surface-To-Air Missiles Deployed To Protect Trump’s Mar-a-Lago Estate (opens the original article)
AN/TWQ-1 Avengers with FIM-92 Stinger missiles have been joined by counter-drone sensor and jammer kits from U.S. Northern Command.
Warfare The War Zone
Why it mattersThe mix of missile and counter-drone systems shows layered protection around a high-profile site.
Sources1The War Zone
Bunker Talk: Let’s Talk About All The Things We Did And Didn’t Cover This Week (opens the original article)
Bunker Talk invites discussion of topics not covered during the week.
Warfare The War Zone
Why it mattersThe item provides no specific technology or operational detail.
Sources1The War Zone
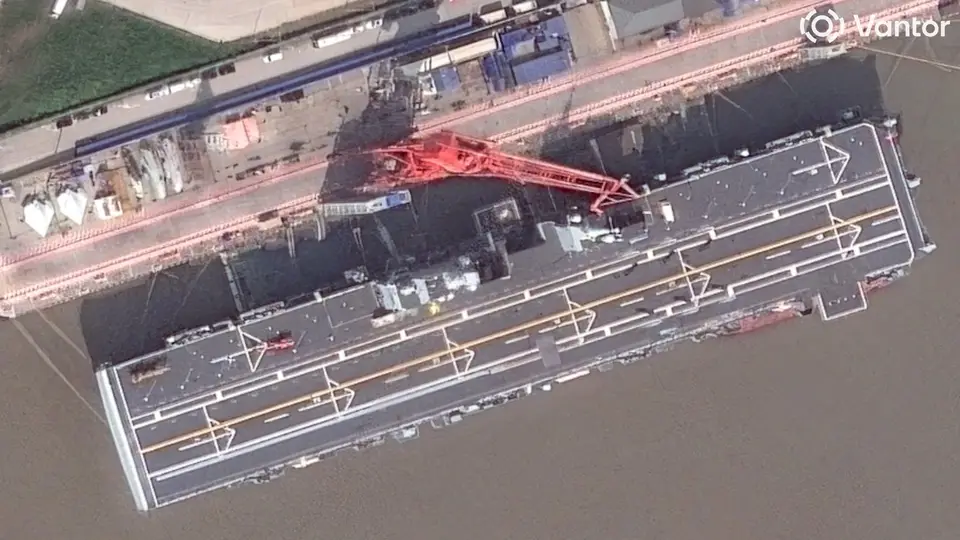
Stealthy GJ-21 Drone Has Launched And Recovered From Type 076 Amphibious Assault Ship, China Claims (opens the original article)
China claims its GJ-21 drone launched and recovered from a Type 076 amphibious assault ship; the item describes this as a milestone in naval airpower.
Warfare The War Zone
Why it mattersShip-based launch and recovery is relevant to naval airpower and operations.
Sources1The War Zone
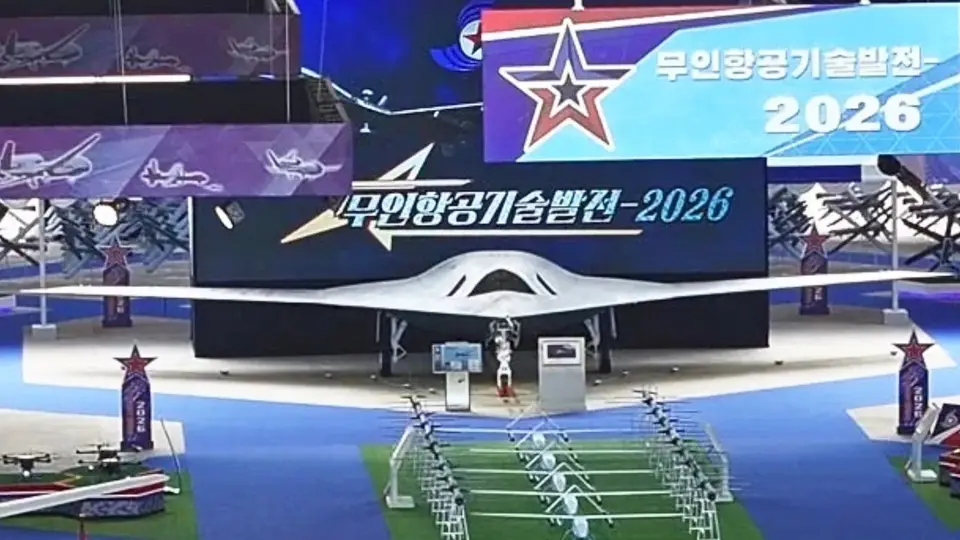
Highlights From North Korea’s Drone-A-Palooza (opens the original article)
The War Zone describes North Korea displaying reconnaissance and attack drones, including an aspirational stealthy UCAV concept.
Warfare The War Zone
Why it mattersThe display highlights reconnaissance and attack drones as capabilities to track in military assessments.
Sources1The War Zone
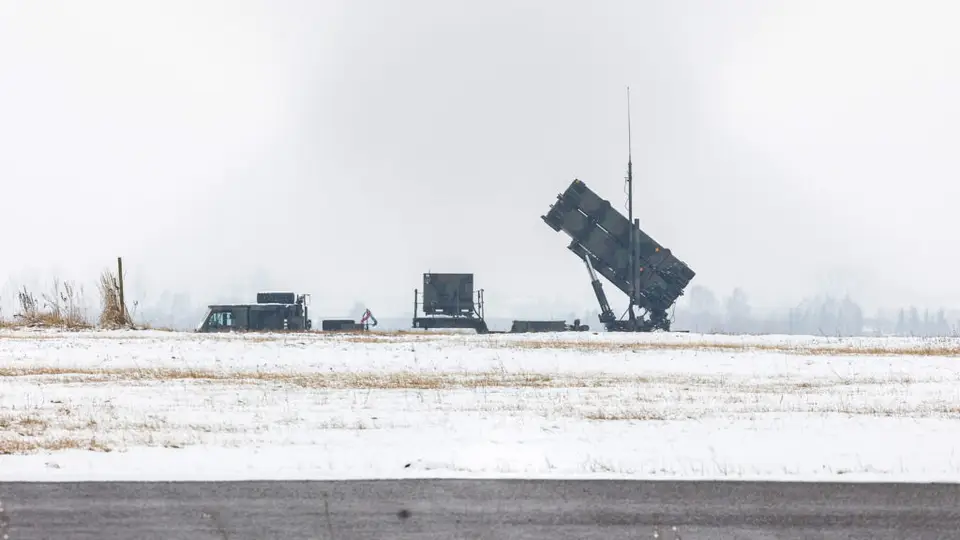
US greenlights 500 Patriot missiles for Ukraine, with $2.1 billion to be paid by allies (opens the original article)
The announcement of 500 Patriot missiles for Ukraine comes amid heightened Kyiv-Washington tensions and purported delays in interceptor transfers.
Warfare Breaking Defense
Why it mattersThe reported transfer and delays are relevant to assessing Ukraine’s interceptor supply.
Sources1Breaking Defense
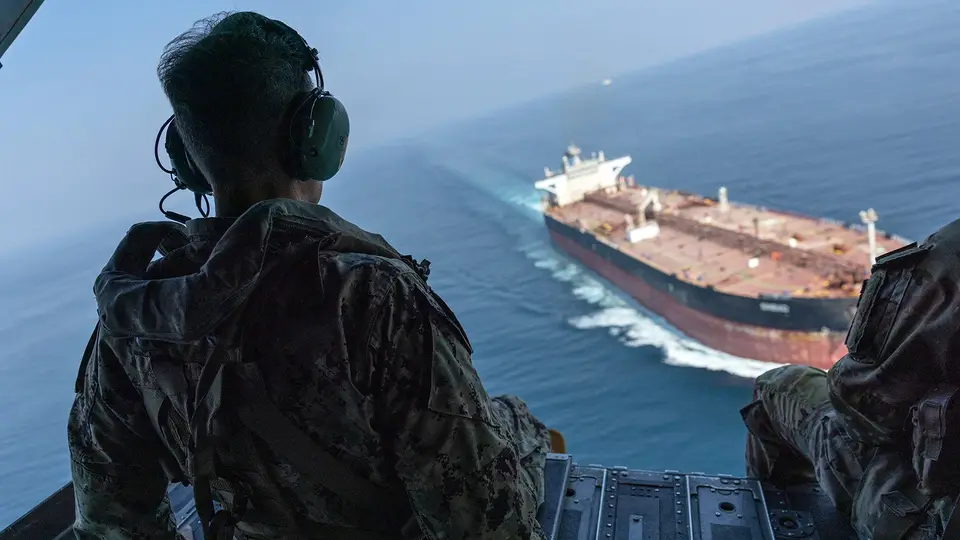
Iran Used Limpet Mine Placed On Ship’s Hull In Latest Strait Of Hormuz Attack: Report (opens the original article)
The title reports a limpet mine placed on a ship’s hull in a Strait of Hormuz attack. The snippet describes additional regional air defenses, ships, troops, ammunition, and supplies.
Warfare The War Zone
Why it mattersA hull-placed mine highlights the relevance of ship protection and maritime security.
Sources1The War Zone
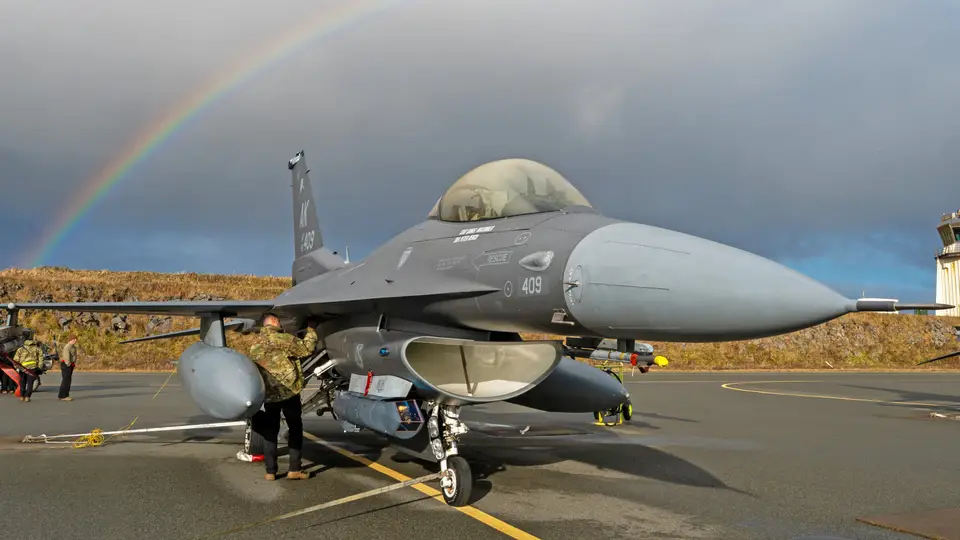
USAF F-16s Back On Alert Duty In Aleutian Islands For First Time In Decades (opens the original article)
NORAD has returned to fighter alert operations on remote Shemya Island, which the article describes as a reminder of an eroding security environment in the Pacific and Arctic.
Warfare The War Zone
Why it mattersThe return of alert duty is relevant to monitoring regional air operations.
Sources1The War Zone
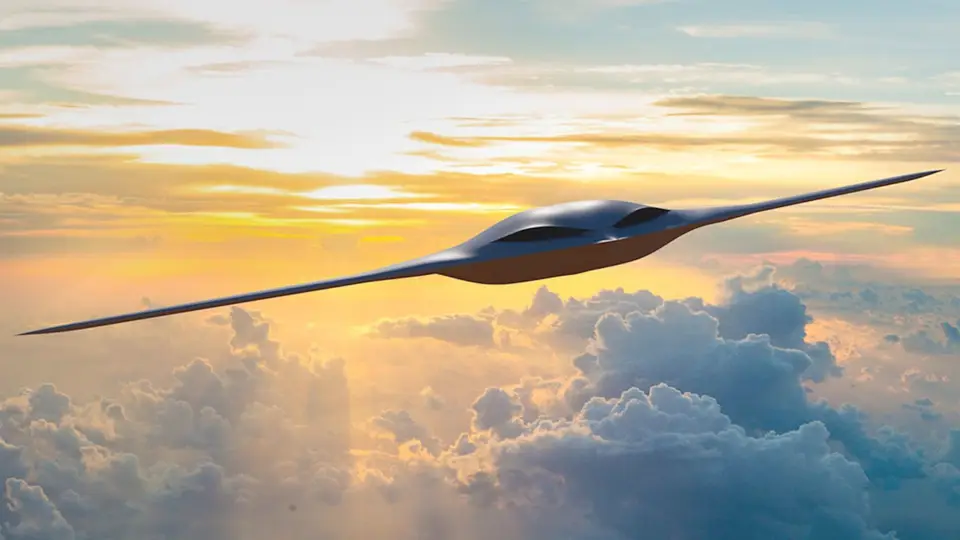
General Atomics Developing Strike-Recon Flying Wing Called NextGen That Uses Hybrid-Electric Propulsion (opens the original article)
General Atomics is developing a strike-recon flying wing using hybrid-electric propulsion and aims to trial an air-to-ground derivative of its FQ-42 Vengeance CCA in live-fire tests next year.
Warfare The War Zone
Why it mattersThe project combines reconnaissance, strike, and hybrid-electric propulsion.
Sources1The War Zone
Geopolitics & geodata
Strategy, geo wars, GNSS and satellite security.
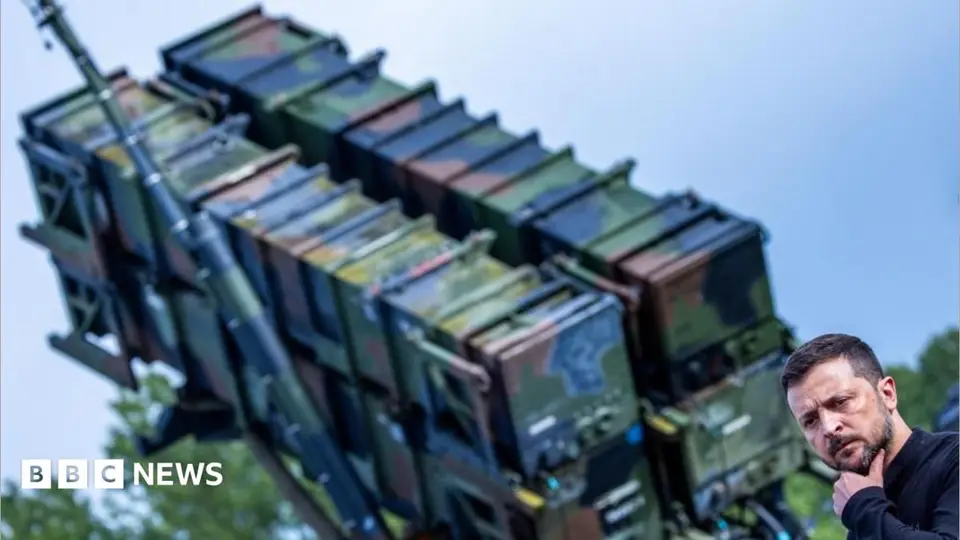
US approves sale of 500 Patriot missiles to Ukraine (opens the original article)
The United States approved the sale of 500 Patriot missiles to Ukraine. The item says the interceptors are effective against Russia's ballistic missiles.
Geopolitics BBC World
Strategic relevanceThe sale is relevant to Ukraine's air defense against ballistic missiles.
Sources1BBC World
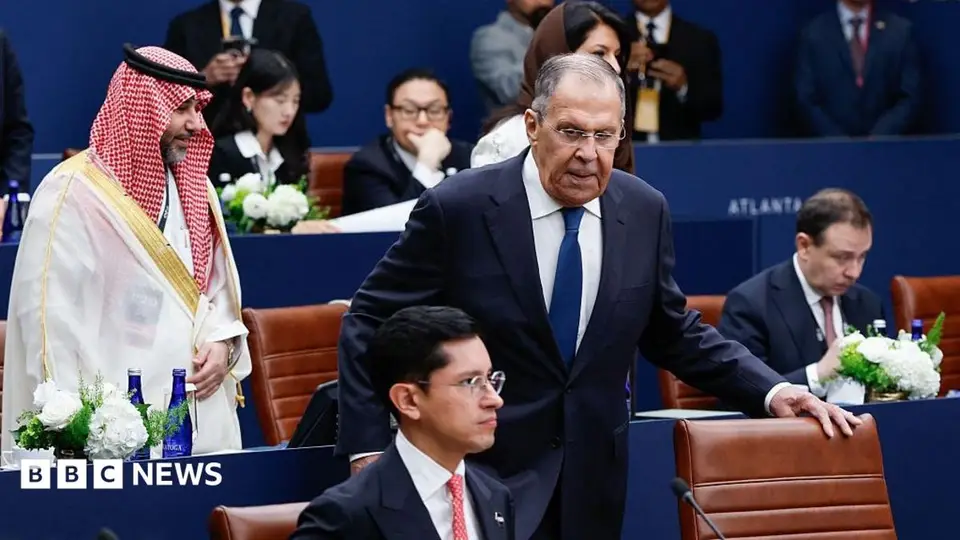
G20 'family photo' cancelled after protests over presence of Russian minister (opens the original article)
The G20 family photo was cancelled after protests over the presence of a Russian minister. The UK foreign secretary confronted his Russian counterpart and accused his government of killing civilians in Ukraine.
Geopolitics BBC World
Strategic relevanceThe episode shows diplomatic tensions shaping a high-profile international meeting.
Sources1BBC World
Crypto giant Binance attempting to recover $6.3bn stolen in hack linked to North Korea (opens the original article)
Binance is attempting to recover $6.3 billion stolen in a hack linked to North Korea; the company describes the cyberattack as complex.
Geopolitics BBC World
Strategic relevanceThe recovery effort makes incident response and tracing stolen crypto assets relevant.
Sources1BBC World
The World’s Biggest Crypto Heist (opens the original article)
Foreign Policy says suspected North Korean hackers stole $6.36 billion in digital coins from Binance.
Geopolitics Foreign Policy
Strategic relevanceThe reported theft makes tracking digital-asset incident claims and response important for security teams.
Sources1Foreign Policy
They strangled us, says founder of Russian newspaper shut under pressure from authorities (opens the original article)
The BBC reports that Novaya Gazeta’s founder says authorities pressured the Russian newspaper, which has been a prominent independent outlet for decades.
Geopolitics BBC World
Strategic relevanceThe account is relevant to understanding constraints on independent media in Russia.
Sources1BBC World
ESA Adds Four Galileo G2 Satellites, Funds Norwegian Work on Jamming and Spoofing Resilience (opens the original article)
ESA announced orders for four more Galileo Second Generation satellites and funding for Norwegian work on jamming and spoofing resilience.
Geopolitics Inside GNSS
Strategic relevanceThe announcements connect navigation infrastructure with resilience to signal interference.
Sources1Inside GNSS
FORTRESS America: Will PNT Resilience Become a Pentagon Priority? (opens the original article)
The article says Defense Secretary Pete Hegseth announced FORTRESS America on September 30, an initiative intended to strengthen the nation’s ability to sustain military operations.
Geopolitics Inside GNSS
Strategic relevanceThe initiative raises the role of PNT resilience in sustaining military operations.
Sources1Inside GNSS
Russia the Disruptor (opens the original article)
Foreign Policy describes how Moscow broke with the West and unleashed a more chaotic world.
Geopolitics Foreign Policy
Strategic relevanceThe framing offers geopolitical context for assessing Russia’s relationship with the West.
Sources1Foreign Policy
| CVE | CVSS | Product | Ransomware | Added / due | Required action |
|---|---|---|---|---|---|
| CVE-2026-118527 | —No score | Ivanti Connect Secure | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-111357 | 7.0High | Ivanti Connect Secure | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-97229 | 10.0Critical | GitLab Community Edition and Enterprise Edition | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-76418 | 8.6High | Cisco Secure Firewall ASA Software and Cisco Secure FTD Software | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-41709 | 2.7Low | Broadcom VMware ESX | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-46300 | 7.8High | Linux Kernel | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-48356 | 9.3Critical | Adobe Commerce and Magento | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-111497 | 9.2Critical | Google Brotli | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-109618 | 9.2Critical | PHP Group PHP | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-109619 | 9.2Critical | PHP Group PHP | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-114625 | 9.4Critical | Arista VeloCloud Orchestrator | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-110447 | 9.2Critical | Collabora Collabora Online – Built-in CODE Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
Source: CISA KEV catalogue; CVSS scores from NVD where published. “No score” means NVD has not scored it yet.
Keyword index
Counted from this page. Select one to filter.