 OUTPOST
Edition 230 — 1 November 2026
Cyber, warfare technology and geopolitics as compiled on 1 November 2026.
Cyber
Breaches, campaigns, advisories and research.
Northflank security breach leads to abuse of customers' AI API keys (opens the original article)
Northflank is warning customers to rotate credentials and secrets stored on its platform after a breach led to unauthorized use of their AI API keys.
Cyber BleepingComputer
What to checkRotate exposed credentials and secrets, then check for unauthorized use of AI API keys.
Sources1BleepingComputer
New Android SMS of Death exploit can remotely crash unpatched phones (opens the original article)
A researcher released a proof-of-concept for a recently patched Android vulnerability that can disrupt cellular service or crash phones through a crafted SMS.
Cyber BleepingComputer
What to checkApply the Android patch and check whether affected devices remain unpatched.
Sources1BleepingComputer
Reddit to lock content behind logins to fight scrapers (opens the original article)
Reddit says it will gradually become a logged-in service, limiting access for visitors without accounts as it fights scrapers.
Cyber BleepingComputer
What to checkDefenders should review how login requirements affect access controls and automated traffic monitoring.
Sources1BleepingComputer
From Beginner to Bug Hunter: Learning Cybersecurity in the AI Era. (opens the original article)
The title presents a guide to learning cybersecurity and bug hunting in the AI era; the snippet provides no further details.
Cyber BleepingComputer
What to checkLearners should assess any specific guidance against their own security testing rules.
Sources1BleepingComputer
Chainalysis discloses data breach from "offensive agentic techniques" (opens the original article)
Chainalysis says attackers used “offensive agentic techniques” to access internal systems and tools, exposing customer names, email addresses, user IDs, and organizational roles.
Cyber BleepingComputer
What to checkReview access to internal tools and assess whether exposed customer identity data appears in your environment.
Sources1BleepingComputer
Chainalysis Confirms Intrusion Into Internal Tools and Exposure of Customer Identity Data (opens the original article)
Chainalysis said an external actor accessed non-sensitive customer data in a cybersecurity incident. The snippet says unauthorized access to its investigat—before ending.
Cyber The Hacker News
What to checkCheck the company’s incident updates for the full scope of accessed data and systems.
Sources1The Hacker News
Syrian Hacker Gets Prison Time in US After Over a Decade on the Run (opens the original article)
A US court sentenced Syrian hacker Ahmad Umar Agha to 42 months for pro-Assad attacks on media, businesses, and government entities.
Cyber SecurityWeek
What to checkThe case highlights the operational reach of attacks against media, businesses, and government entities.
Sources1SecurityWeek
Attackers Chain Three Ivanti Connect Secure Flaws to Gain Unauthenticated Root Access (opens the original article)
CISA added two Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog following active exploitation; the title says attackers chain three flaws for unauthenticated root access.
Cyber The Hacker News
What to checkCheck Ivanti Connect Secure exposure and prioritize the flaws listed in CISA’s KEV catalog.
Sources1The Hacker News
A Shared ChatGPT Link Could Run Attacker Code in Your Session and Read Private Chats (opens the original article)
Researchers at Parameter say a malicious ChatGPT share link could run code in a logged-in session and expose private conversations.
Cyber The Hacker News
What to checkTreat unexpected shared-chat links cautiously and review session protections for logged-in users.
Sources1The Hacker News
Cloudflare Reports 18.2 Million Network-Layer DDoS Attacks in Q3, Up 38% (opens the original article)
Cloudflare reported 18.2 million network-layer DDoS attacks in Q3, up 38%, and said it autonomously mitigated them.
Cyber The Hacker News
What to checkReview network-layer DDoS monitoring and mitigation readiness.
Sources1The Hacker News
Warfare
Drones, electronic warfare, missiles and defence systems.
Across the line (opens the original article)
A Useful Fiction story explores how Army infantry, armor, and robotic systems might fight together.
Warfare Defense One
Why it mattersThe story frames how robotic systems could relate to infantry and armor in combined operations.
Sources1Defense One
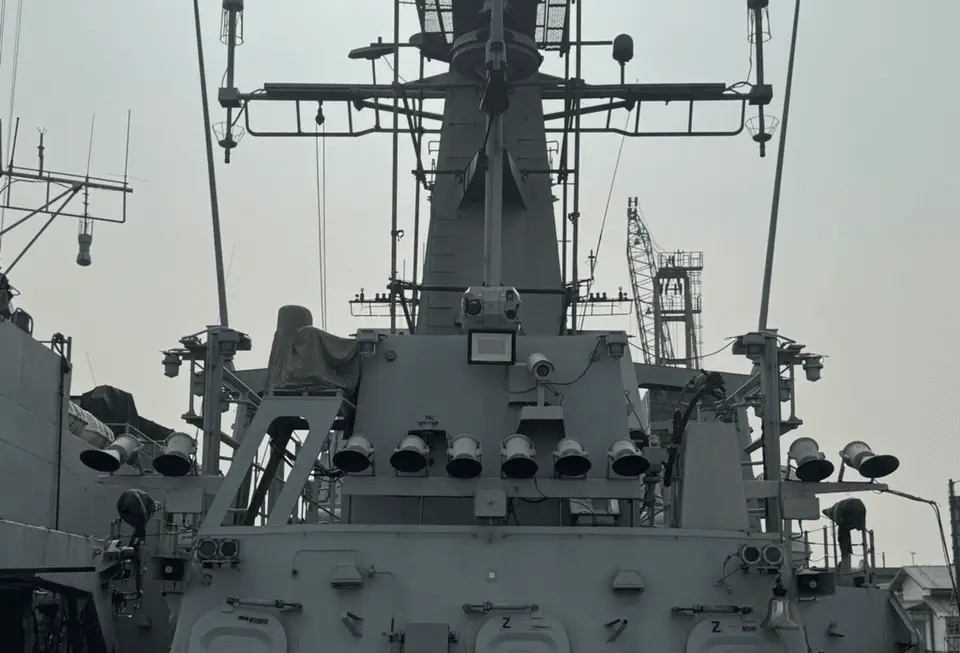
Chess Dynamics Wins £3M Contract for Indonesian Bung Tomo-Class Frigates (opens the original article)
Chess Dynamics announced a contract to supply SeaEagle Fire Control Electro-Optical systems for two Indonesian Bung Tomo-class frigates.
Warfare Naval News
Why it mattersThe contract highlights electro-optical fire-control equipment as part of frigate capability.
Sources1Naval News
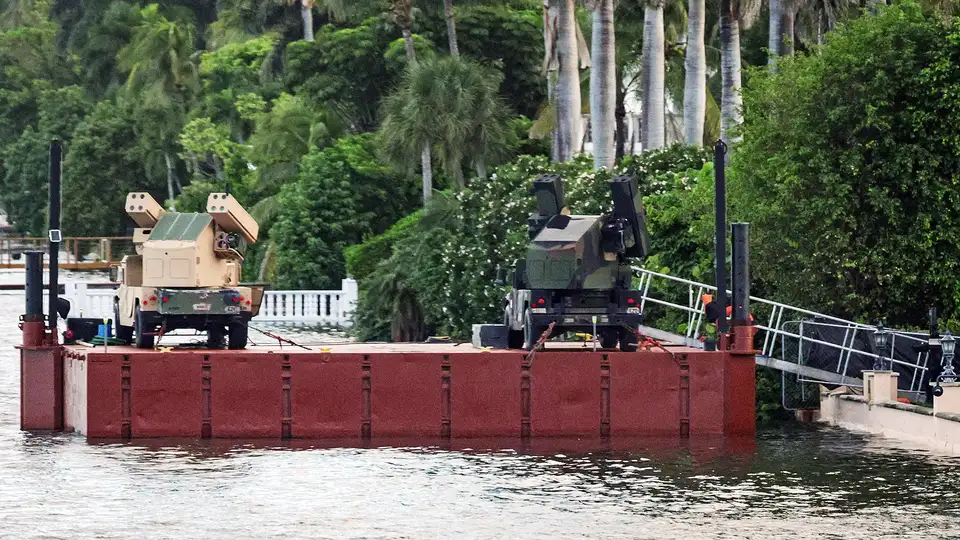
Surface-To-Air Missiles Deployed To Protect Trump’s Mar-a-Lago Estate (opens the original article)
AN/TWQ-1 Avengers with FIM-92 Stinger missiles have been joined by counter-drone sensor and jammer kits from U.S. Northern Command.
Warfare The War Zone
Why it mattersThe mix of missile and counter-drone systems shows layered protection around a high-profile site.
Sources1The War Zone
Bunker Talk: Let’s Talk About All The Things We Did And Didn’t Cover This Week (opens the original article)
Bunker Talk invites discussion of topics not covered during the week.
Warfare The War Zone
Why it mattersThe item provides no specific technology or operational detail.
Sources1The War Zone
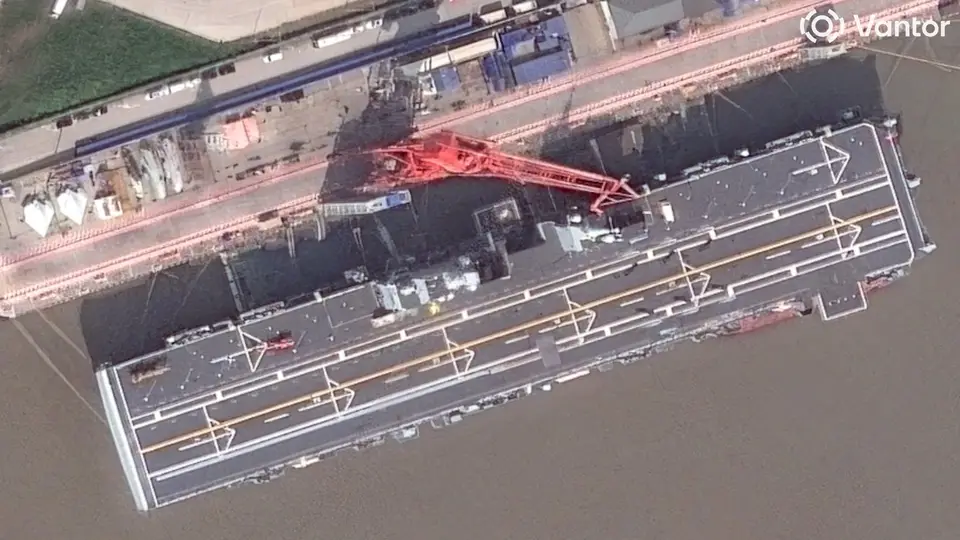
Stealthy GJ-21 Drone Has Launched And Recovered From Type 076 Amphibious Assault Ship, China Claims (opens the original article)
China claims its GJ-21 drone launched and recovered from a Type 076 amphibious assault ship; the item describes this as a milestone in naval airpower.
Warfare The War Zone
Why it mattersShip-based launch and recovery is relevant to naval airpower and operations.
Sources1The War Zone
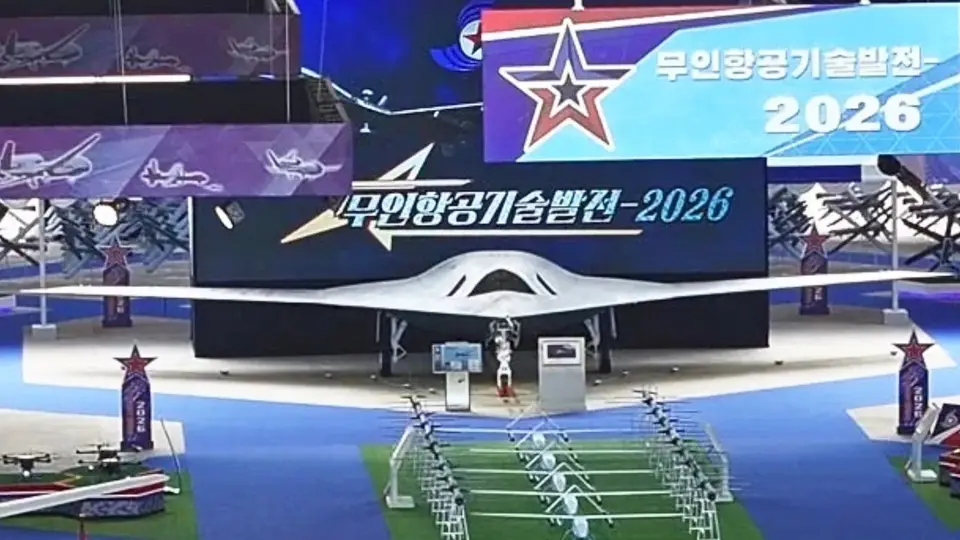
Highlights From North Korea’s Drone-A-Palooza (opens the original article)
The War Zone describes North Korea displaying reconnaissance and attack drones, including an aspirational stealthy UCAV concept.
Warfare The War Zone
Why it mattersThe display highlights reconnaissance and attack drones as capabilities to track in military assessments.
Sources1The War Zone
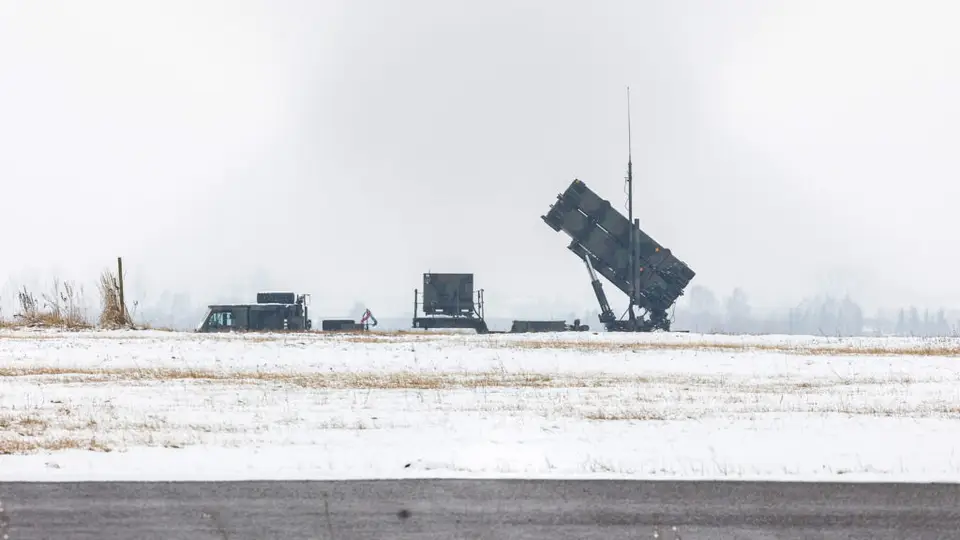
US greenlights 500 Patriot missiles for Ukraine, with $2.1 billion to be paid by allies (opens the original article)
The announcement of 500 Patriot missiles for Ukraine comes amid heightened Kyiv-Washington tensions and purported delays in interceptor transfers.
Warfare Breaking Defense
Why it mattersThe reported transfer and delays are relevant to assessing Ukraine’s interceptor supply.
Sources1Breaking Defense
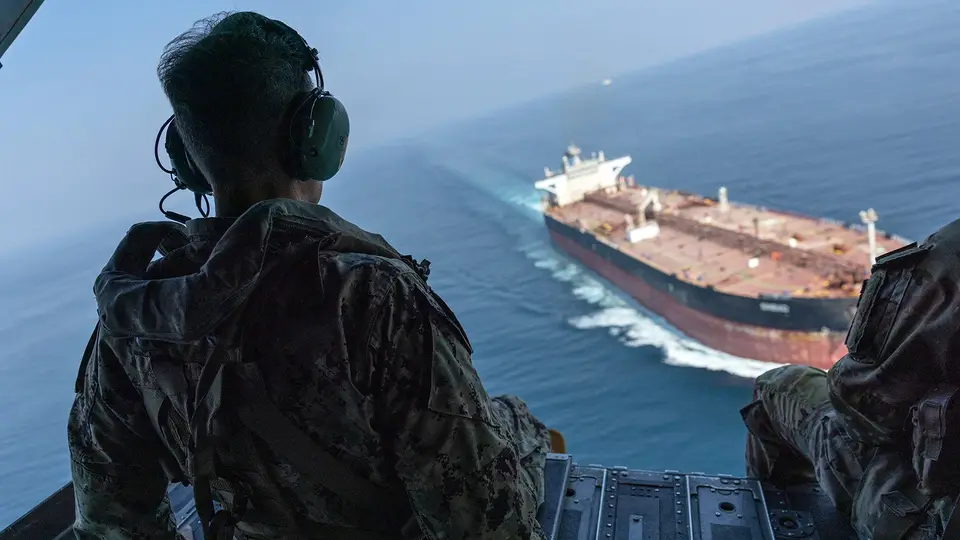
Iran Used Limpet Mine Placed On Ship’s Hull In Latest Strait Of Hormuz Attack: Report (opens the original article)
The title reports a limpet mine placed on a ship’s hull in a Strait of Hormuz attack. The snippet describes additional regional air defenses, ships, troops, ammunition, and supplies.
Warfare The War Zone
Why it mattersA hull-placed mine highlights the relevance of ship protection and maritime security.
Sources1The War Zone
Geopolitics & geodata
Strategy, geo wars, GNSS and satellite security.
Crypto firm Binance covers 90% of losses after $6.3bn hack (opens the original article)
Binance covers 90% of losses after a hack; two analytics firms say a North Korean state-backed group is the likely culprit.
Geopolitics BBC World
Strategic relevanceAttribution remains an assessment; analysts should distinguish the firms’ claim from confirmed responsibility.
Sources1BBC World
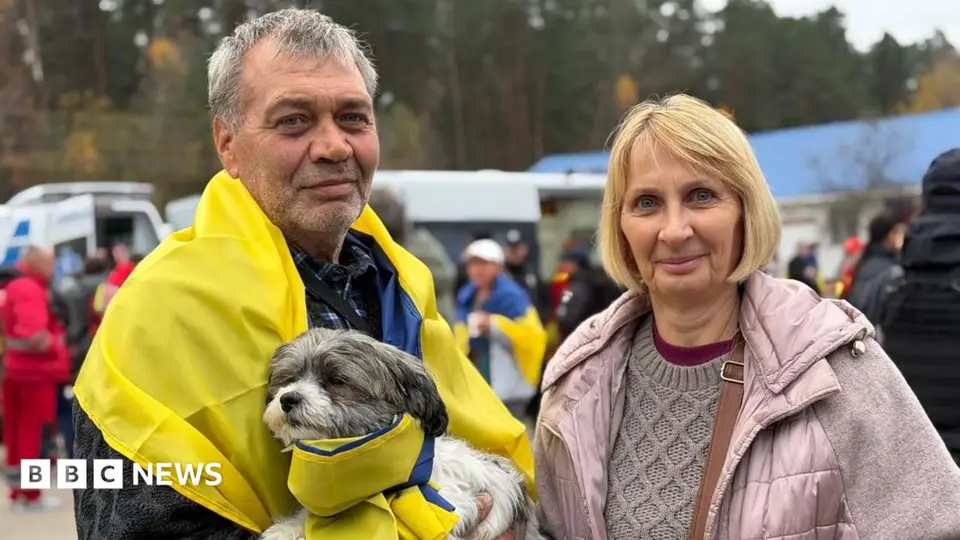
'We came back from hell', say Ukrainians after years in Russia-occupied front-line city (opens the original article)
An evacuated couple says they crossed minefields in Oleshky while searching for food.
Geopolitics BBC World
Strategic relevanceMinefields shape movement and access to essential supplies in the front-line city.
Sources1BBC World
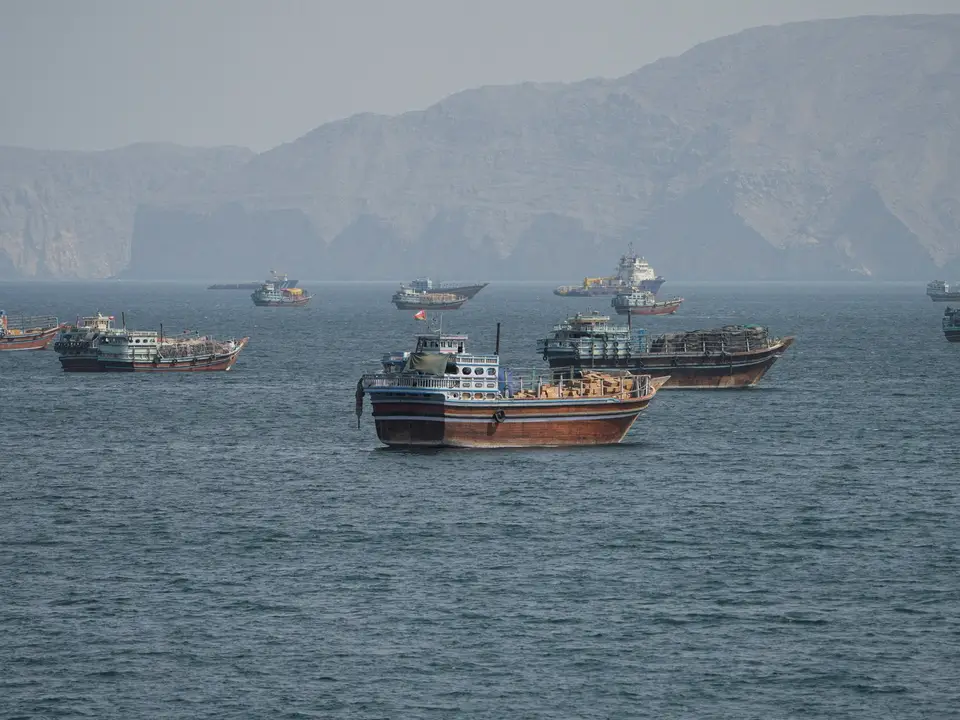
Iran war live: Araghchi says talks under way on 2-day plan to reopen Hormuz (opens the original article)
Iran’s top diplomat says Iran and Qatar have reached a plan to reopen Hormuz in two days if the US meets Tehran’s conditions.
Geopolitics Al Jazeera
Strategic relevanceThe proposed reopening links access through Hormuz to negotiations and could affect the route’s strategic significance.
Sources1Al Jazeera
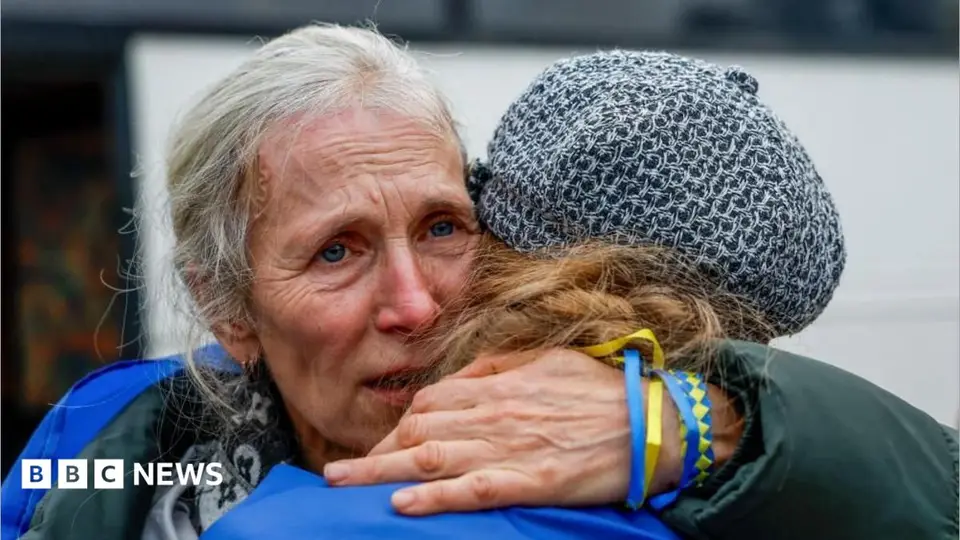
Ukrainian evacuees reunite with family after years trapped in Russia-occupied city (opens the original article)
The BBC says residents left a devastated Russia-occupied city and arrived in Ukraine following a ceasefire brokered by US First Lady Melania Trump.
Geopolitics BBC World
Strategic relevanceThe movement of evacuees and the ceasefire are relevant to tracking displacement and conditions around the city.
Sources1BBC World
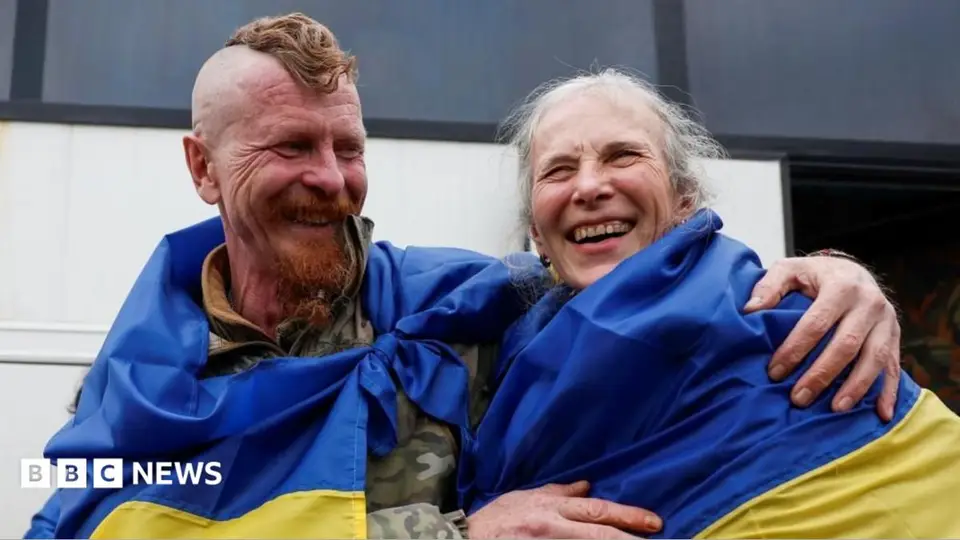
Emotional reunions with loved ones for Oleshky evacuees (opens the original article)
The BBC reports that evacuated Oleshky residents arrived at the northern Ukrainian border with Belarus in buses and ambulances after a temporary ceasefire.
Geopolitics BBC World
Strategic relevanceThe evacuation and temporary ceasefire are relevant to movement across the border area.
Sources1BBC World
Israel’s allegations of Qatari election interference rejected (opens the original article)
Al Jazeera reports that Israel’s allegations of Qatari election interference were rejected.
Geopolitics Al Jazeera
Strategic relevanceThe dispute concerns allegations of election interference between states.
Sources1Al Jazeera
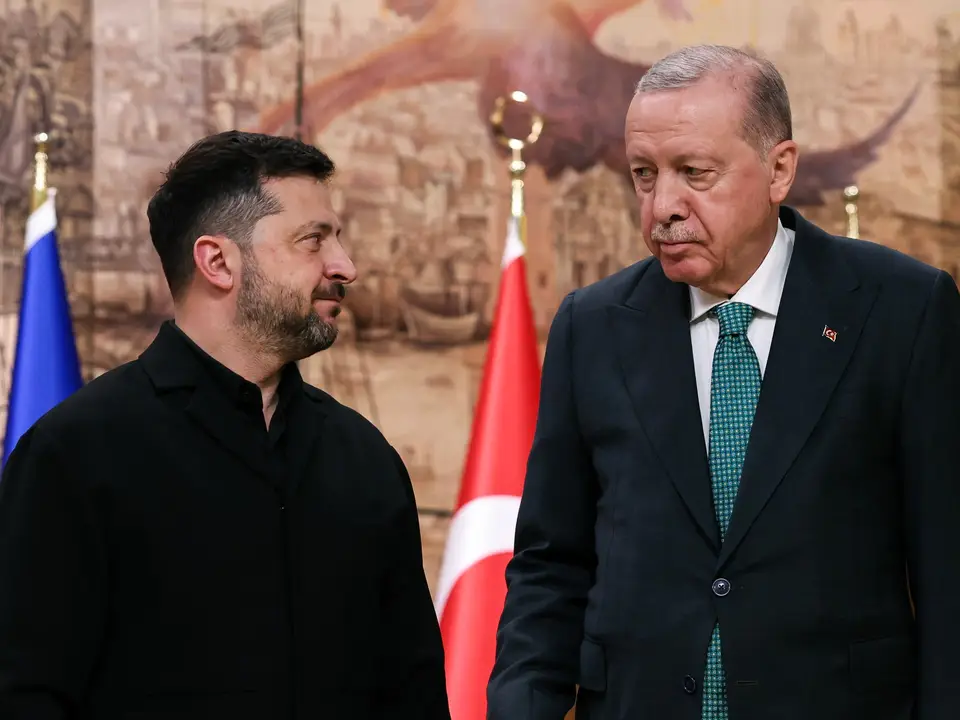
Turkiye’s Erdogan urges Russia and Ukraine to stop Black Sea attacks (opens the original article)
Turkiye’s Erdogan urged Russia and Ukraine to stop Black Sea attacks. The leaders agreed to work on a new Black Sea grain corridor.
Geopolitics Al Jazeera
Strategic relevanceThe proposed corridor links Black Sea security with grain movement.
Sources1Al Jazeera
How vulnerable are cryptocurrency platforms? (opens the original article)
Al Jazeera says hackers have targeted Binance, the world’s largest cryptocurrency exchange.
Geopolitics Al Jazeera
Strategic relevanceCheck protections on cryptocurrency platform accounts and monitor for suspicious activity.
Sources1Al Jazeera
| CVE | CVSS | Product | Ransomware | Added / due | Required action |
|---|---|---|---|---|---|
| CVE-2026-118527 | —No score | Ivanti Connect Secure | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-111357 | 7.0High | Ivanti Connect Secure | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-97229 | 10.0Critical | GitLab Community Edition and Enterprise Edition | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-76418 | 8.6High | Cisco Secure Firewall ASA Software and Cisco Secure FTD Software | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-41709 | 2.7Low | Broadcom VMware ESX | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-46300 | 7.8High | Linux Kernel | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-48356 | 9.3Critical | Adobe Commerce and Magento | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-111497 | 9.2Critical | Google Brotli | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-109618 | 9.2Critical | PHP Group PHP | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-109619 | 9.2Critical | PHP Group PHP | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-114625 | 9.4Critical | Arista VeloCloud Orchestrator | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-110447 | 9.2Critical | Collabora Collabora Online – Built-in CODE Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
Source: CISA KEV catalogue; CVSS scores from NVD where published. “No score” means NVD has not scored it yet.
Keyword index
Counted from this page. Select one to filter.