 OUTPOST
Edition 231 — 2 November 2026
Cyber, warfare technology and geopolitics as compiled on 2 November 2026.
Cyber
Breaches, campaigns, advisories and research.
Ivanti patches two more Connect Secure zero-days chained in attacks (opens the original article)
Ivanti released updates for two Connect Secure remote-access gateway flaws that it says have been chained in zero-day attacks since at least October 1.
Cyber BleepingComputer 2 outlets
What to checkApply the updates and check Connect Secure systems for signs of exploitation.
FBI links $6.3 billion Binance crypto heist to North Korean hackers (opens the original article)
The FBI says North Korean state-sponsored hackers known as TraderTraitor carried out the $6.3 billion Binance crypto theft.
Cyber BleepingComputer 2 outlets
What to checkReview cryptocurrency custody and transaction controls; the snippet does not identify the attack method.
Polymarket Returns $3.9 Million to Traders as DebugBear Cites DNS Hijack (opens the original article)
DebugBear says attackers compromised its DNS records through its domain registrar; early findings indicate one customer was targeted.
Cyber SecurityWeek
What to checkReview registrar access and DNS changes, and investigate whether users were redirected.
Sources1SecurityWeek
FBI Flags Over 600 Addresses Tied to North Korea’s Binance Heist (opens the original article)
The FBI says more than 600 addresses are tied to North Korea’s Binance heist as attackers launder stolen cryptocurrency.
Cyber SecurityWeek
What to checkCheck whether relevant addresses appear in transaction monitoring and apply current screening controls.
Sources1SecurityWeek
New VOLTA Infostealer Uses Claude, Gemini, and Kimi AI to Rank Victims by Financial Value (opens the original article)
Researchers say VOLTA infostealer uses a large language model to rank stolen victim data by potential monetization value.
Cyber The Hacker News
What to checkReview endpoint alerts for infostealer activity and investigate suspected credential or data theft.
Sources1The Hacker News
FBI blames N. Korea’s TraderTraitor for Binance theft, urges crypto industry to block transactions (opens the original article)
The FBI and U.S. Secret Service allege North Korean hackers were responsible for stealing more than $6.3 billion from Binance.
Cyber The Record
What to checkCrypto organizations should review transaction monitoring and consider the FBI’s call to block transactions.
Sources1The Record
DeepSeek open-sources Super-Agent, a coding agent that watches team chats for work (opens the original article)
DeepSeek released a research prototype of a coding agent that can work on a GitHub repository when an allowed user or team rule requests it.
Cyber Help Net Security
What to checkReview who can authorize agent work and what repository permissions it receives.
Sources1Help Net Security
The first ten lines of a command policy for AI coding agents (opens the original article)
A KloudStax executive explains how to set identity, credentials, and network limits for AI agents, arguing they should have their own identity.
Cyber Help Net Security
What to checkGive agents distinct identities and restrict their credentials and network access.
Sources1Help Net Security
Byoky: Open-source wallet for AI API keys (opens the original article)
Byoky is an open-source app for storing AI API keys encrypted on a device, available as browser extensions and mobile apps.
Cyber Help Net Security
What to checkAssess how keys are stored and which apps can access them before adopting a key wallet.
Sources1Help Net Security
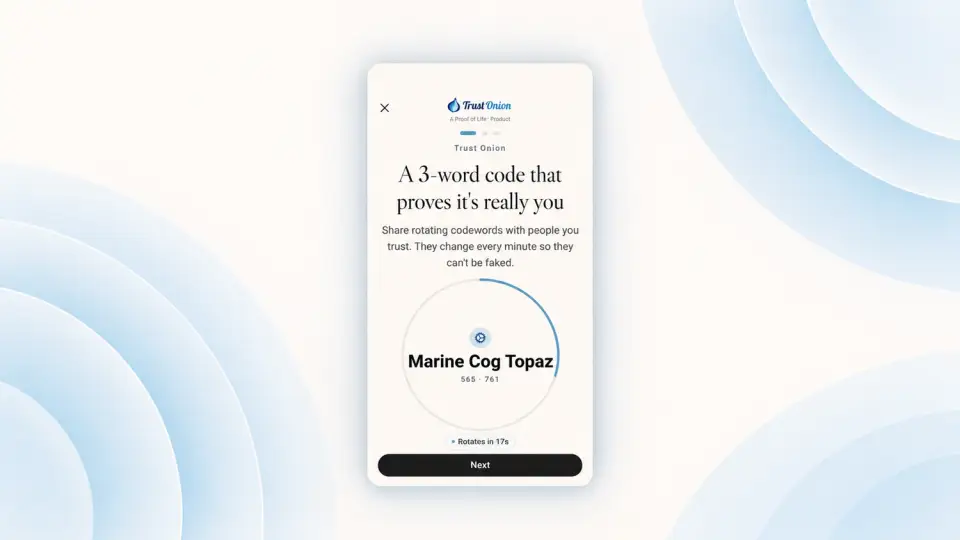
Product showcase: Trust Onion uses rotating codewords to verify callers (opens the original article)
Trust Onion is an app that uses rotating codewords to help groups verify callers; it also offers signed selfies, message checks, and callback requests.
Cyber Help Net Security
What to checkConsider independent caller verification for trusted groups communicating through potentially uncertain channels.
Sources1Help Net Security
Warfare
Drones, electronic warfare, missiles and defence systems.
The Pentagon-Silicon Complex and the Rise of the Neo-Primes (opens the original article)
A War on the Rocks discussion asks what happens when the military depends on technologies it does not own, drawing on a book about Big Tech and war.
Warfare War on the Rocks
Why it mattersThe discussion raises how reliance on privately owned technology may shape military capabilities.
Sources1War on the Rocks
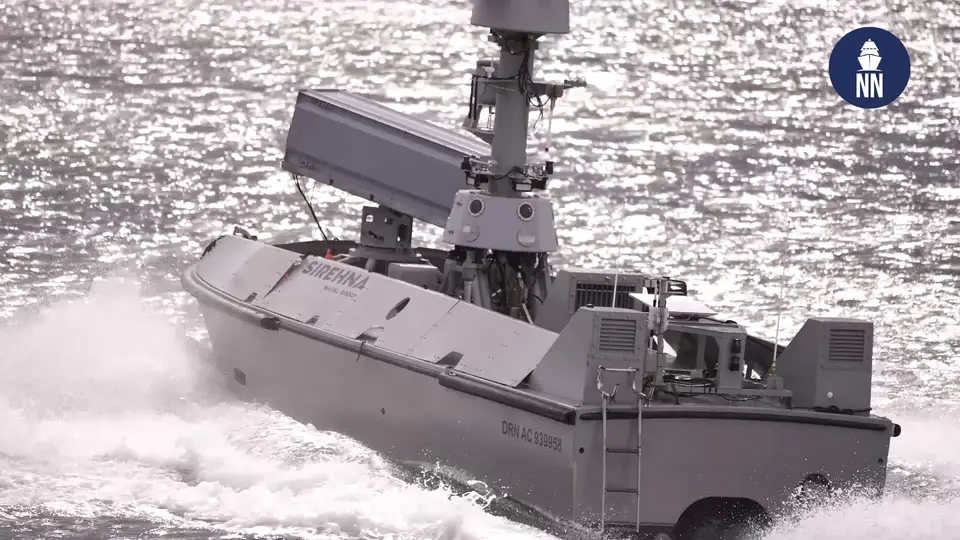
Video: Naval Group Demonstrates Armed SEAQUEST-S USV (opens the original article)
Naval Group’s Sirehna demonstrated the SEAQUEST-S, a multi-role combat uncrewed surface vessel designed for deployment from warships.
Warfare Naval News
Why it mattersThe demonstration highlights a surface vessel designed to operate from warships.
Sources1Naval News
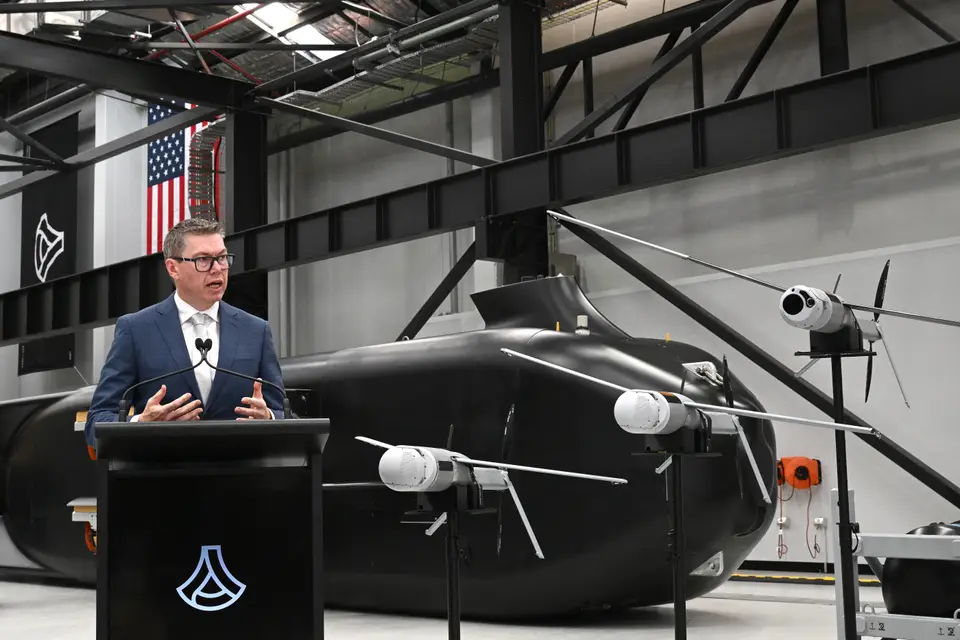
Australia unveils secretive Ghost Shark underwater drone payloads (opens the original article)
The Australian Navy disclosed some payloads it is fielding on its Ghost Shark extra-large autonomous underwater vehicles.
Warfare Defense News
Why it mattersThe disclosed payloads offer a glimpse of equipment used on autonomous underwater vehicles.
Sources1Defense News
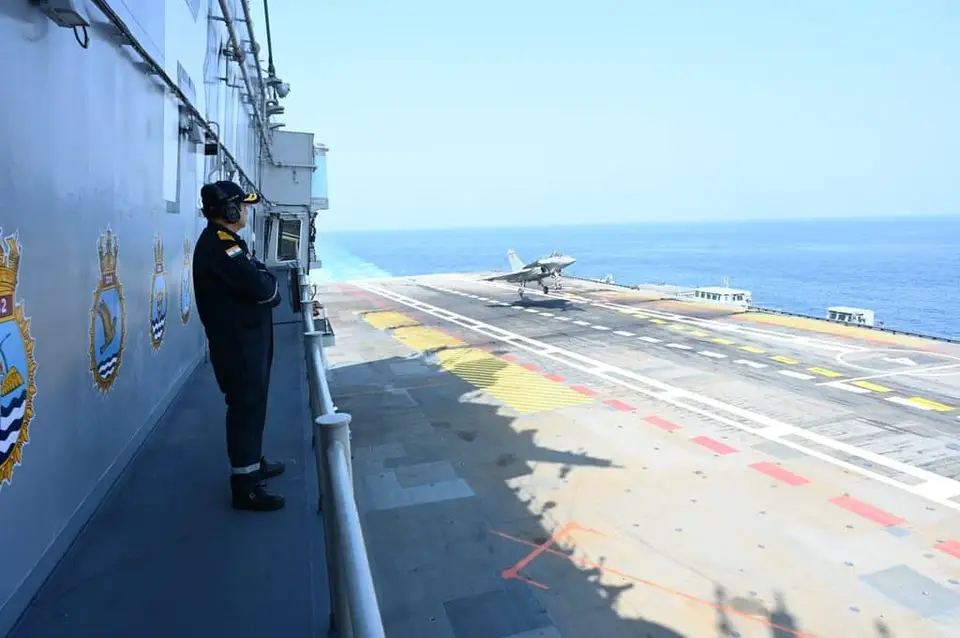
Rafale M Conducts Maiden Trials onboard Indian Aircraft Carrier INS Vikrant (opens the original article)
A French Rafale M made its maiden landing on India’s INS Vikrant, succeeding on its first attempt, Naval News reports.
Warfare Naval News
Why it mattersThe trial demonstrates carrier operations involving a French fighter and an Indian aircraft carrier.
Sources1Naval News
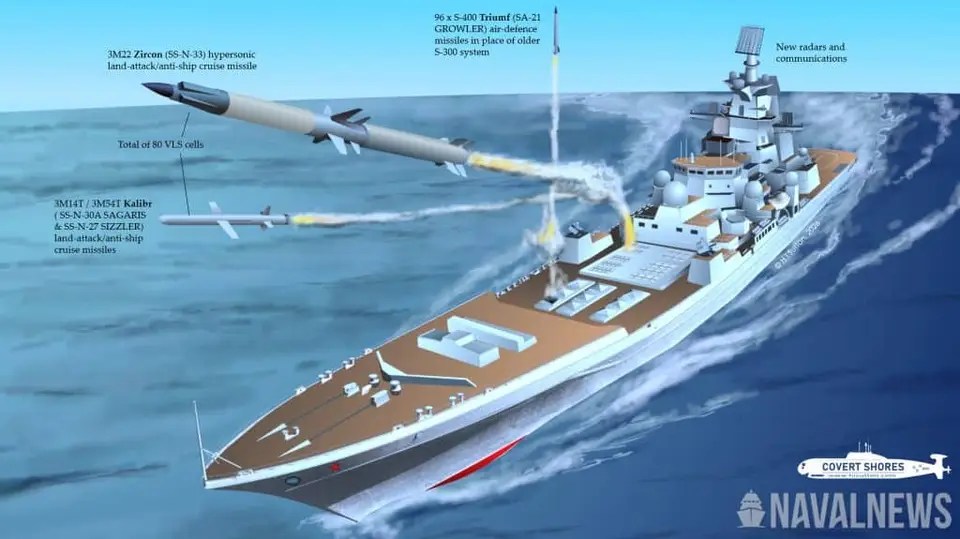
Russian Navy Cancels Modernization of Kirov-Class Battlecruiser Pyotr Velikiy (opens the original article)
Naval News reports that the Russian Navy canceled modernization plans for the Kirov-class battlecruiser Pyotr Velikiy.
Warfare Naval News
Why it mattersThe cancellation is relevant to assessments of plans for Russia’s surface fleet.
Sources1Naval News
Geopolitics & geodata
Strategy, geo wars, GNSS and satellite security.
Ryanair may freeze workers' pay and raise airfares (opens the original article)
Ryanair says fuel prices may rise by €2bn in 2028 unless the US-Israel war with Iran ends; the airline may freeze workers’ pay and raise fares.
Geopolitics BBC World
Strategic relevanceThe airline’s statement links fuel costs to the war, with potential implications for fares and pay.
Sources1BBC World
Binance users withdraw $3.6bn after largest-ever crypto hack (opens the original article)
Binance froze transactions after the largest-ever crypto hack, which has been linked to a North Korean group; users withdrew $3.6bn.
Geopolitics BBC World
Strategic relevanceThe withdrawals and transaction freeze show how a crypto incident can affect exchange activity.
Sources1BBC World
Don’t Read Too Much Into These Midterms (opens the original article)
Foreign Policy argues that anger about the Iran war among voters does not necessarily mean they want a return to the pre-Trump status quo.
Geopolitics Foreign Policy
Strategic relevanceThe article cautions against treating opposition to a war as evidence of broader political preference.
Sources1Foreign Policy
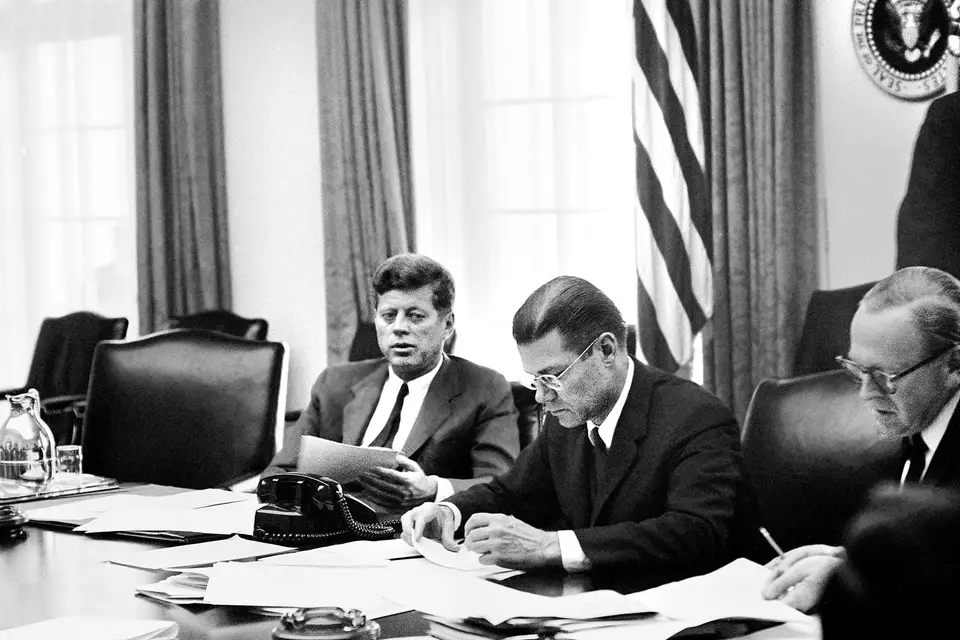
The Biggest October Surprise of All (opens the original article)
Foreign Policy says a crisis that brought the U.S. and the Soviets close to nuclear war in 1962 reshaped U.S. politics.
Geopolitics Foreign Policy
Strategic relevanceThe story links a nuclear crisis to subsequent political change in the United States.
Sources1Foreign Policy
UN staffer’s death in custody exposes Houthi ‘political extortion’ in Yemen (opens the original article)
Rights experts say a UN staffer’s death in custody exposes systematic abuses in Yemen and call for international accountability.
Geopolitics Al Jazeera
Strategic relevanceThe case draws attention to accountability and conditions affecting UN staff in Yemen.
Sources1Al Jazeera
Hormuz shipping still faces major risks (opens the original article)
Al Jazeera says the Strait of Hormuz remains dangerous and costly for shipping, despite U.S. claims that it is open.
Geopolitics Al Jazeera
Strategic relevanceThe differing assessments matter to operators evaluating shipping routes through the strait.
Sources1Al Jazeera
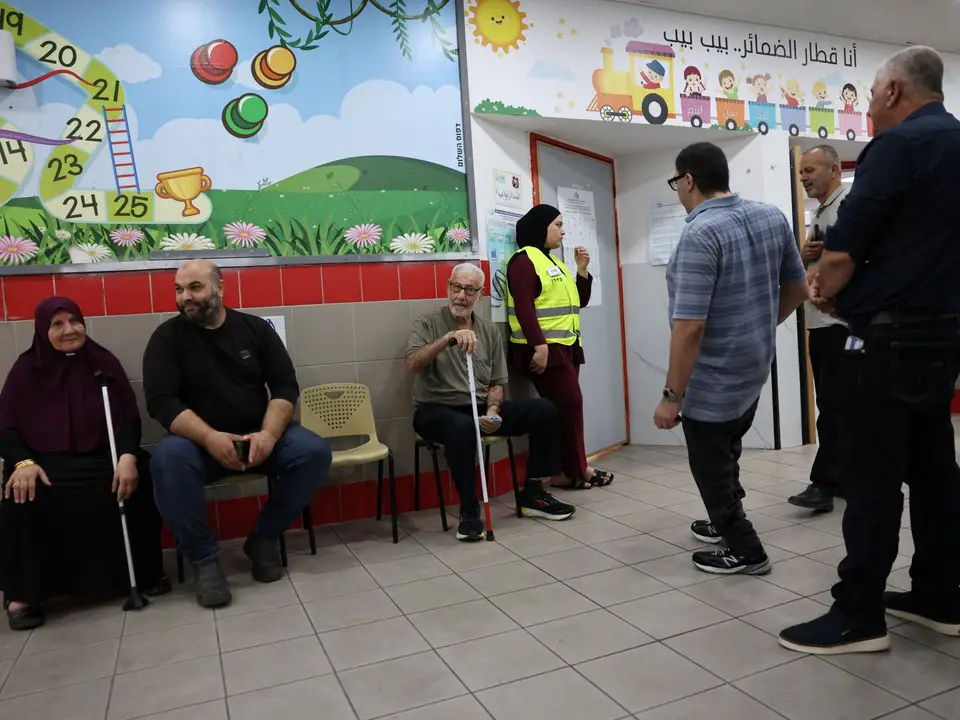
The future of the Palestinian vote in Israel (opens the original article)
Al Jazeera says backlash against high Palestinian turnout reveals tensions around Israeli democracy and its future.
Geopolitics Al Jazeera
Strategic relevanceThe story frames turnout and its reception as relevant to Israel’s political outlook.
Sources1Al Jazeera
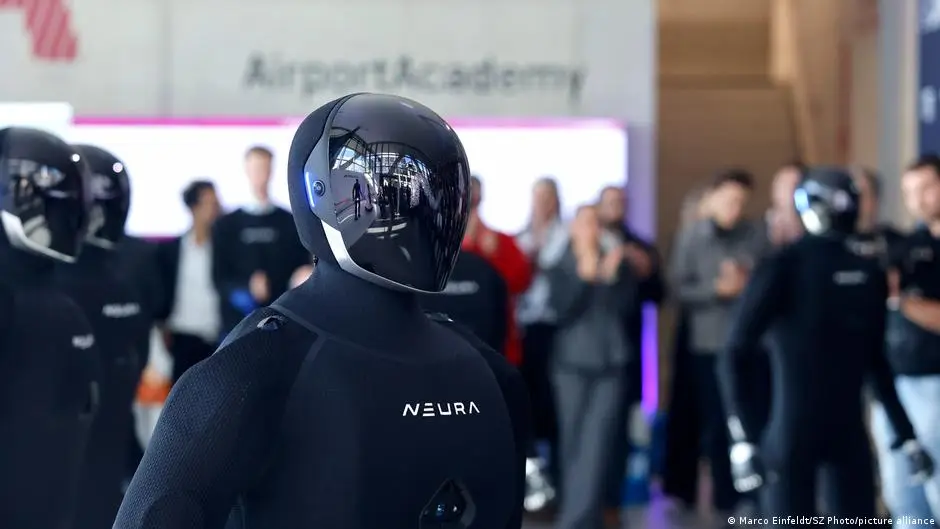
Germany news: Berlin hosts digital summit with AI focus (opens the original article)
Berlin will host a government-run summit on AI’s uses and dangers as German and UK defense ministers discuss expanding AI’s military role.
Geopolitics DW
Strategic relevanceThe summit and ministerial discussions put AI policy and military cooperation in focus.
Sources1DW
| CVE | CVSS | Product | Ransomware | Added / due | Required action |
|---|---|---|---|---|---|
| CVE-2026-118527 | —No score | Ivanti Connect Secure | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-111357 | 7.0High | Ivanti Connect Secure | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-97229 | 10.0Critical | GitLab Community Edition and Enterprise Edition | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-76418 | 8.6High | Cisco Secure Firewall ASA Software and Cisco Secure FTD Software | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-41709 | 2.7Low | Broadcom VMware ESX | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-46300 | 7.8High | Linux Kernel | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-48356 | 9.3Critical | Adobe Commerce and Magento | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-111497 | 9.2Critical | Google Brotli | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-109618 | 9.2Critical | PHP Group PHP | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-109619 | 9.2Critical | PHP Group PHP | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-114625 | 9.4Critical | Arista VeloCloud Orchestrator | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-110447 | 9.2Critical | Collabora Collabora Online – Built-in CODE Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
Source: CISA KEV catalogue; CVSS scores from NVD where published. “No score” means NVD has not scored it yet.
Keyword index
Counted from this page. Select one to filter.