 OUTPOST
Edition 232 — 3 November 2026
Cyber, warfare technology and geopolitics as compiled on 3 November 2026.
Cyber
Breaches, campaigns, advisories and research.
Google disrupts million-device XCPE Android malware botnet, bans TV box maker (opens the original article)
Google and industry partners dismantled the XCPE botnet; Google says its manufacturer intentionally infected more than 1.3 million Android TV boxes.
Cyber BleepingComputer 2 outlets
What to checkReview Android TV devices for malware and assess their exposure to botnet activity.
Unit 42 Threat Intelligence Highlights - Nov. 2, 2026 (opens the original article)
Unit 42 highlights cyberespionage, financial extortion, and rapid AI adoption across offensive workflows.
Cyber Unit 42
What to checkReview controls and monitoring for threats involving espionage, extortion, and AI-assisted workflows.
Sources1Unit 42
Ivanti patches two more Connect Secure zero-days chained in attacks (opens the original article)
Ivanti released updates for two Connect Secure remote-access gateway flaws that it says have been chained in zero-day attacks since at least October 1.
Cyber BleepingComputer 2 outlets
What to checkApply the updates and check Connect Secure systems for signs of exploitation.
UK faces ‘unprecedented rise’ in cyberattacks in coming months, warns cyber chief (opens the original article)
The NCSC chief will warn that tolerated vulnerabilities can now be discovered and exploited at an unprecedented scale.
Cyber The Record
What to checkFind and remediate long-tolerated vulnerabilities before they are exploited.
Sources1The Record
Chinese hackers use ARTEX AI in automated attacks against 200 orgs (opens the original article)
BleepingComputer says Chinese hackers used the ARTEX AI penetration-testing framework in attacks against more than 200 organizations across 14 countries.
Cyber BleepingComputer
What to checkCheck for attacks involving ARTEX and review exposure to automated penetration-testing tools.
Sources1BleepingComputer
Largest crypto exchange in Brazil confirms cyberattack as millions flow out of platform (opens the original article)
Blockchain security companies said more than $46 million left the Mercado Bitcoin platform after a cyberattack.
Cyber The Record
What to checkReview exchange incident reporting and monitor platform transactions for suspicious outflows.
Sources1The Record
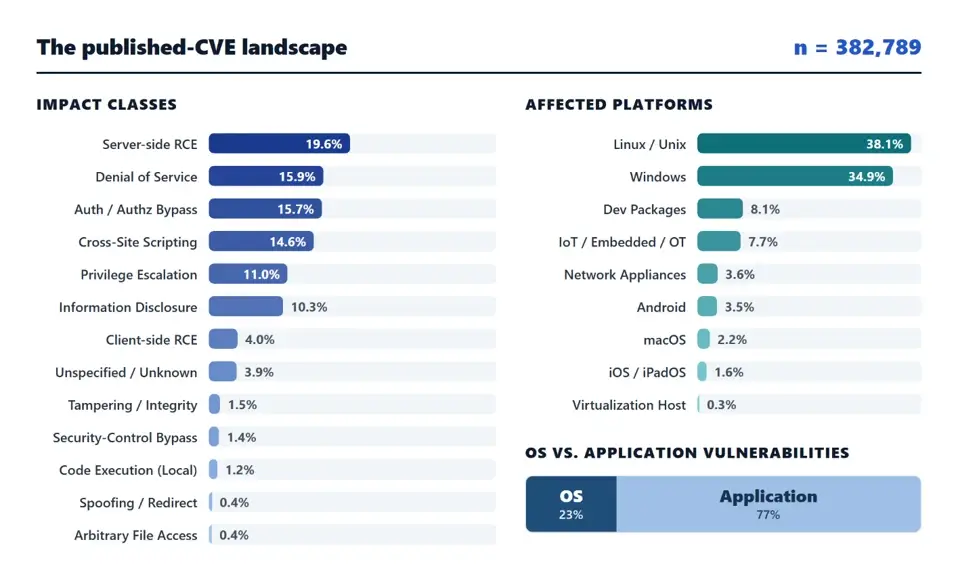
What exploited vulnerabilities have in common: A data-driven analysis of real-world attacks (opens the original article)
Microsoft says real-world exploitation concentrates in a small, high-impact subset of CVEs and describes prioritization by likelihood, exposure, and blast radius.
Cyber Microsoft Security
What to checkPrioritize vulnerability remediation using exploitation likelihood, exposure, and potential blast radius.
Sources1Microsoft Security
Michigan State cyber incident claimed by ransomware gang behind recent hospital attack (opens the original article)
The Record says a BYOD gang post appears to align with a Michigan State incident that prompted campus-wide action.
Cyber The Record
What to checkCheck incident response and campus-wide security actions against the reported ransomware claim.
Sources1The Record
Fintech platform Sageworks taken offline after suspected cyberattack (opens the original article)
Abrigo says it restored Sageworks after an outage triggered by “irregular activity,” but borrower-facing capabilities remain unavailable.
Cyber BleepingComputer
What to checkCheck service status and confirm which borrower-facing functions remain unavailable.
Sources1BleepingComputer
Polymarket pledges to give $3.9 million back to victims after site compromise (opens the original article)
Polymarket says it will repay users’ losses and compensate them for downtime after an October 29 site compromise.
Cyber The Record
What to checkReview incident communications and account activity following the site compromise.
Sources1The Record
Warfare
Drones, electronic warfare, missiles and defence systems.
A Nuclear Strike On Iran? It Sounds Absurd Because It Is. Let’s Talk About It (opens the original article)
The article argues that a nuclear strike on Iran, if entertained, would face a greater disaster than closure of the Strait of Hormuz.
Warfare The War Zone
Why it mattersThe discussion highlights the potential strategic consequences of a strike involving Iran and the Strait of Hormuz.
Sources1The War Zone
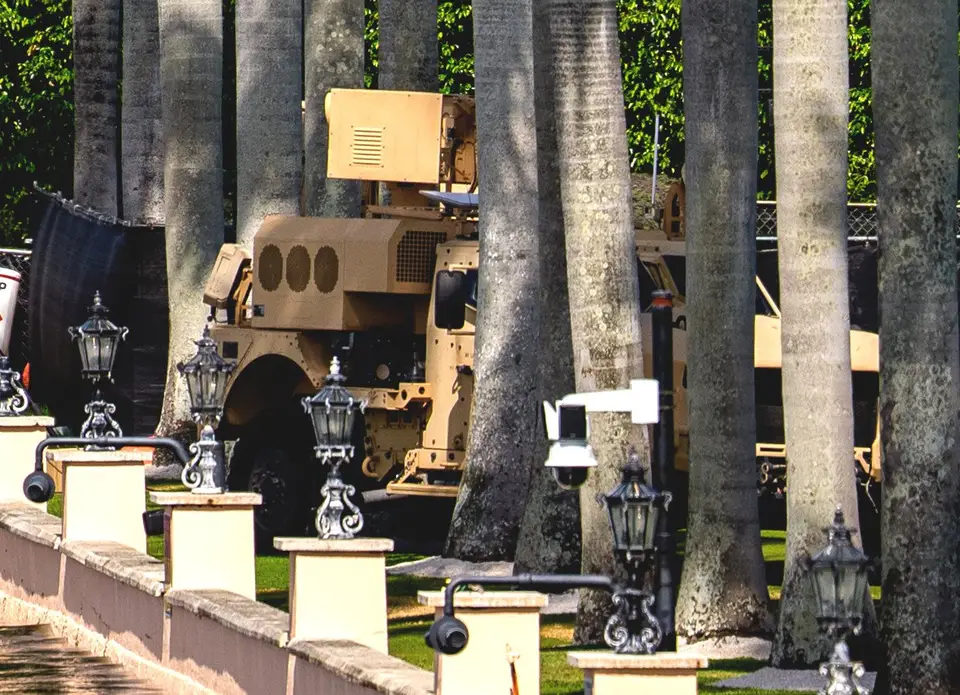
Counter-Drone Laser Weapon Now Guarding Trump’s Mar-a-Lago Alongside SAMs (opens the original article)
The War Zone reports that Mar-a-Lago is the latest real-world deployment of the U.S. military's LOCUST counter-drone lasers.
Warfare The War Zone
Why it mattersThe deployment illustrates the operational use of laser weapons against drones.
Sources1The War Zone
Inside the Secretive, Contradictory World of Campaign Ads Funded by AI Super PACs (opens the original article)
Bellingcat’s snippet describes an online campaign ad funded by AI Super PACs but provides little detail about the investigation.
Warfare Bellingcat
Why it mattersThe snippet offers limited detail on the ads’ operational relevance.
Sources1Bellingcat
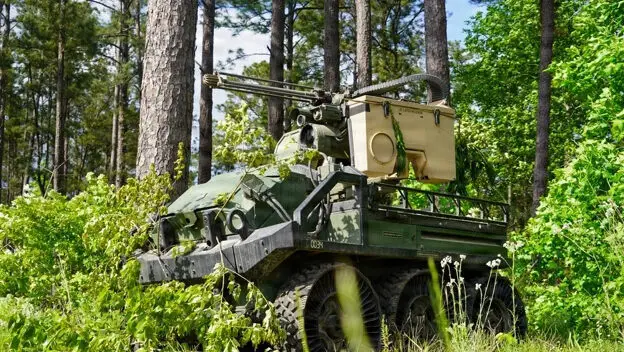
Industry needs more consistent demand signal to scale UGV production: Autonomy consortium exec (opens the original article)
A NAMC executive says industry needs a more consistent demand signal to decide where to invest in scaling UGV production.
Warfare Breaking Defense
Why it mattersDemand signals may shape investment and the pace of UGV production.
Sources1Breaking Defense
Corruption in the Crosshairs: The Debate Over Transparency and Saving Face (opens the original article)
The snippet describes a War on the Rocks digest of Ukrainian commentary about transparency and saving face.
Warfare War on the Rocks
Why it mattersThe snippet identifies a debate but gives little detail about its operational relevance.
Sources1War on the Rocks
UK to lead multinational military training exercise to prepare for peace in Ukraine (opens the original article)
The UK will lead an exercise in Poland with British troops, RAF jets, and forces from 11 nations to rehearse securing lasting peace in Ukraine.
Warfare UK Ministry of Defence
Why it mattersThe exercise concerns multinational preparation for security arrangements after fighting in Ukraine ends.
Sources1UK Ministry of Defence
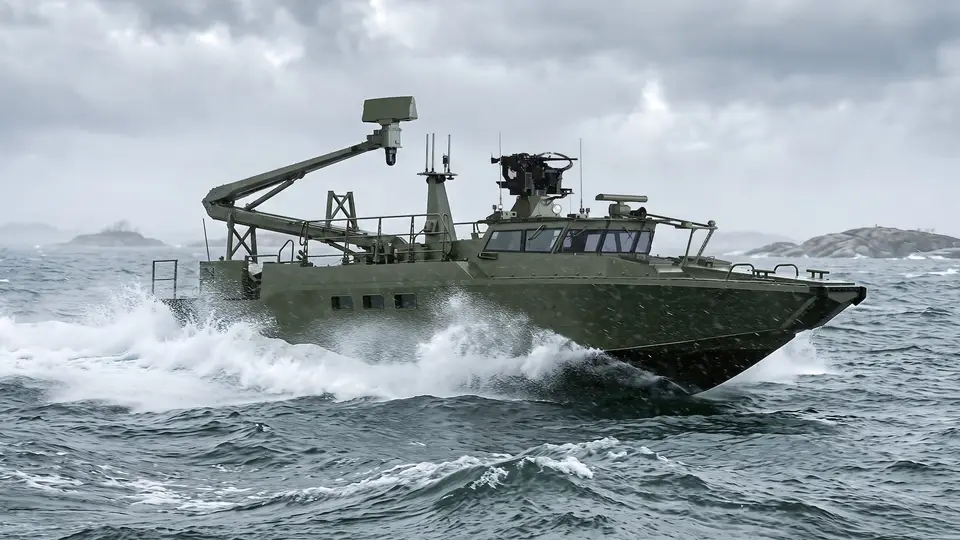
New CB90 CX Is Bigger, Optionally Crewed Evolution Of Saab’s Proven Combat Boat (opens the original article)
The CB90 CX adds expanded payload capacity and new combat capabilities to the familiar combat boat, according to the snippet.
Warfare The War Zone
Why it mattersThe expanded payload and capabilities indicate an evolution in combat boat design.
Sources1The War Zone
New X-Plane To Be Announced At Max Power Airshow: NASA Administrator Isaacman (opens the original article)
NASA’s administrator says a new X-Plane will be announced at the Max Power Airshow; the snippet also mentions a question about the SR-71.
Warfare The War Zone
Why it mattersThe announcement may make the X-Plane’s development relevant to aerospace watchers.
Sources1The War Zone
Geopolitics & geodata
Strategy, geo wars, GNSS and satellite security.
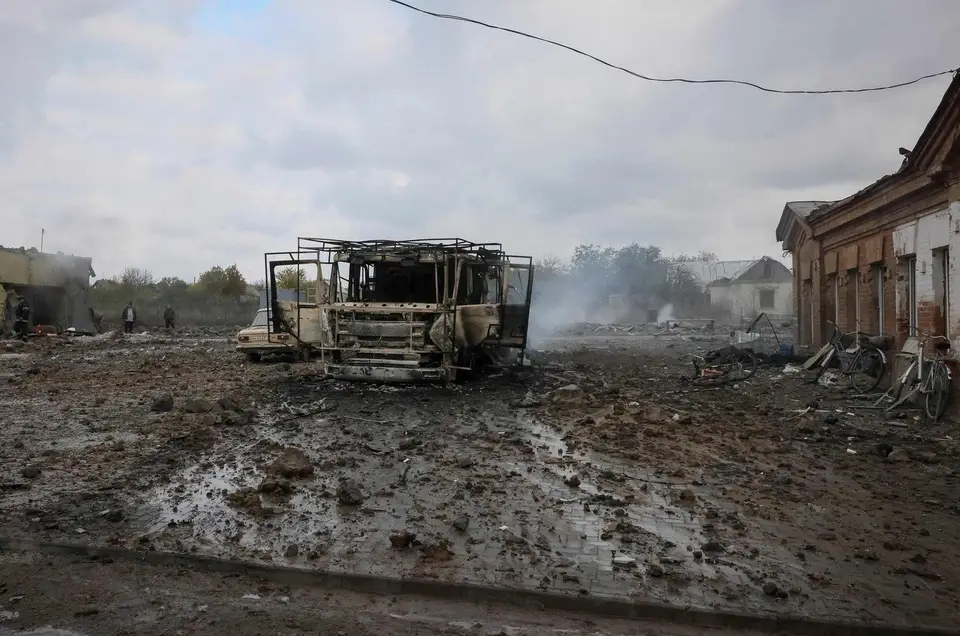
Multiple Russian strikes kill at least 26 at Ukraine aid centre (opens the original article)
Al Jazeera reports that at least 26 people were killed in Russian strikes on a school used as a humanitarian aid centre.
Geopolitics Al Jazeera 2 outlets
Strategic relevanceThe reported strikes underline the humanitarian and geographic significance of sites used for aid.
Sources1Al Jazeera2DW
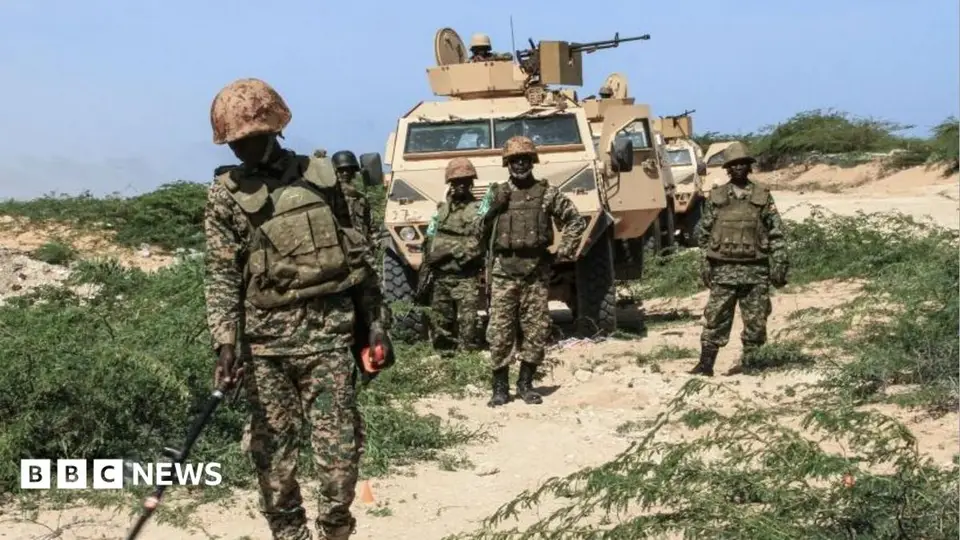
Uganda begins withdrawing troops from Somalia after 20 years (opens the original article)
Uganda has begun withdrawing troops from Somalia after helping the country battle an al-Shabab insurgency since 2007.
Geopolitics BBC World 2 outlets
Strategic relevanceThe withdrawal is relevant to Uganda’s military role in Somalia and the fight against al-Shabab.
Sources1BBC World2DW
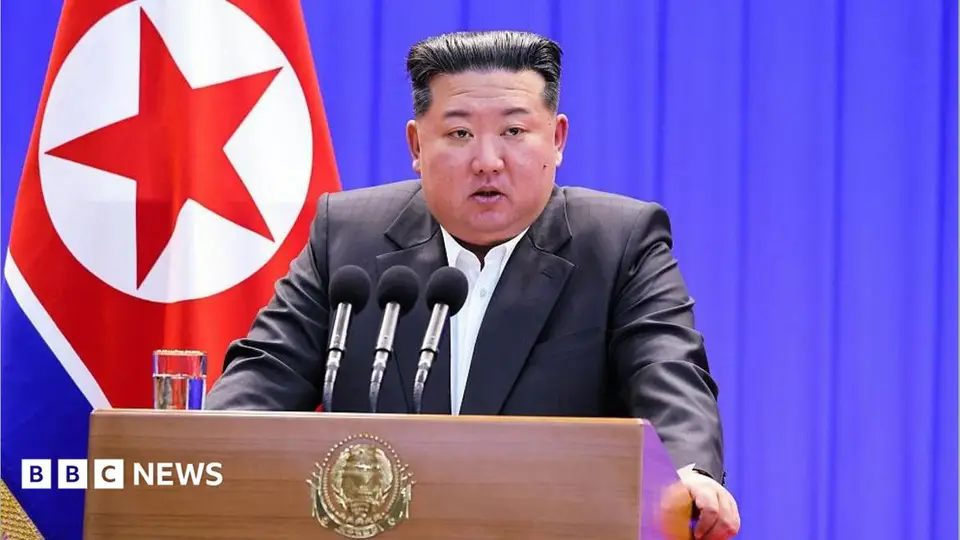
North Korea denies being behind record $6.3bn Binance hack (opens the original article)
North Korea denies responsibility for the Binance hack; U.S. agencies and cyber analysts have blamed Pyongyang.
Geopolitics BBC World
Strategic relevanceTrack the competing attribution claims and their implications for assessing the hack.
Sources1BBC World
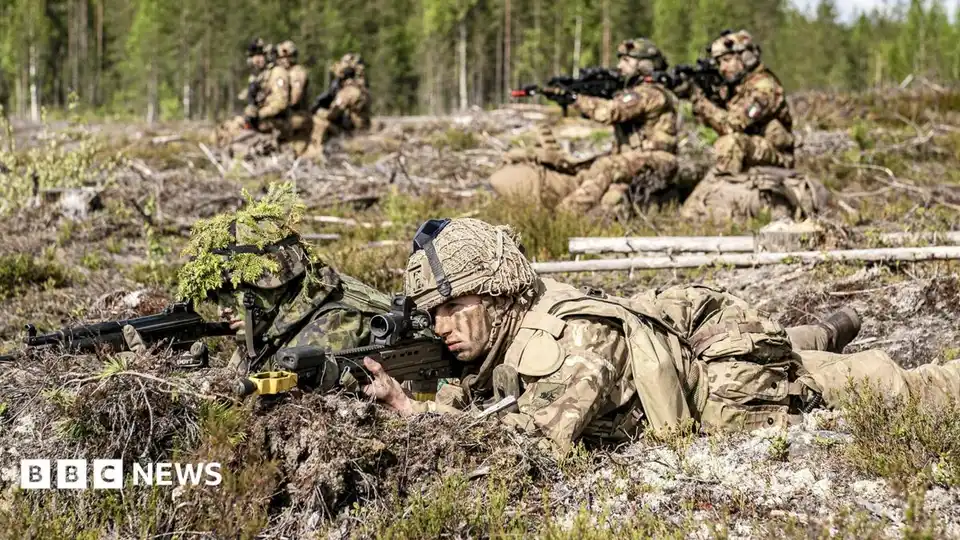
Thousands of European troops to rehearse Ukraine deployment in event of peace (opens the original article)
European troops will rehearse a possible Ukraine deployment; Western officials stress the force would not take part in offensive operations.
Geopolitics BBC World
Strategic relevanceThe rehearsal concerns the possible role and limits of a Western force in Ukraine.
Sources1BBC World
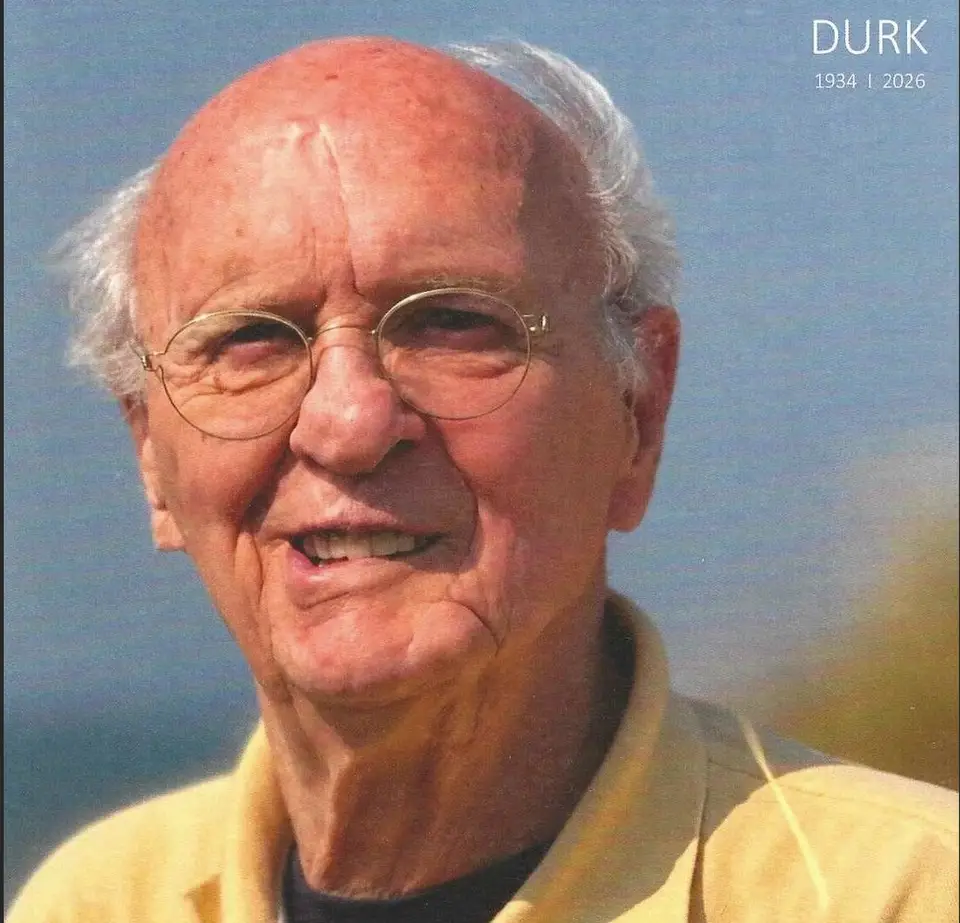
In Memoriam: Dr. Durk van Willigen (opens the original article)
Professor van Willigen founded Reelektronika and blended GNSS with eLoran, according to the snippet.
Geopolitics Inside GNSS
Strategic relevanceThe GNSS and eLoran combination is relevant to navigation technology.
Sources1Inside GNSS
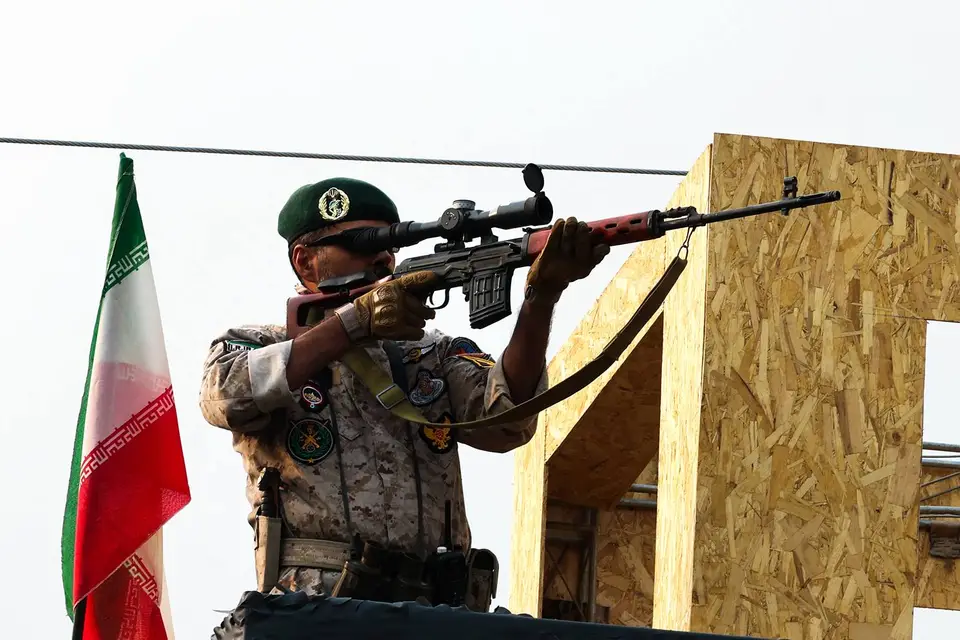
Reigniting War With Iran Would Be a ‘Huge Gamble’ (opens the original article)
Foreign Policy reports that one expert described the U.S. military's long-term readiness concerns as profound amid debate over war with Iran.
Geopolitics Foreign Policy
Strategic relevanceReadiness concerns are relevant to assessing the strategic implications of renewed conflict with Iran.
Sources1Foreign Policy
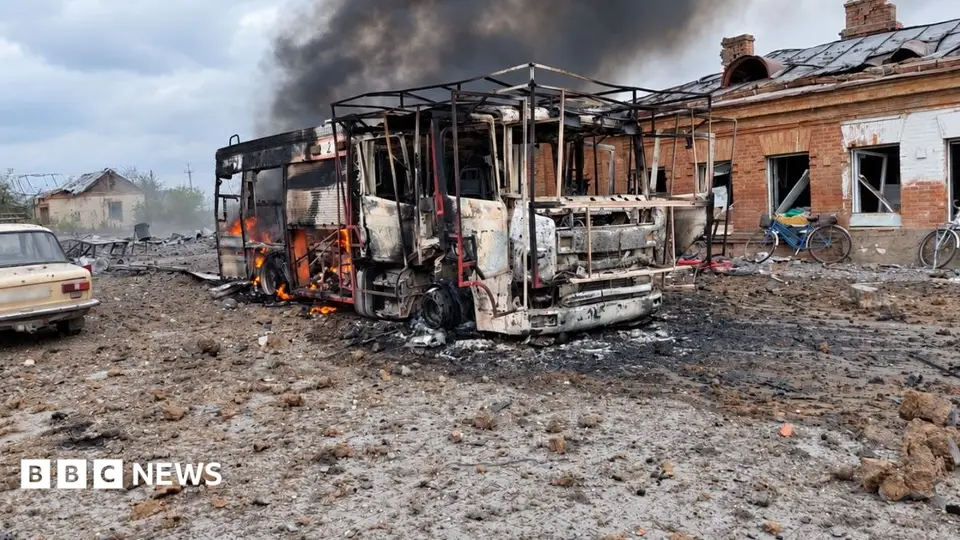
Russian bombing kills 26 people at Ukraine aid centre, Kyiv says (opens the original article)
Kyiv says Russian bombing killed 24 people at a Ukraine aid centre; local officials say 27 people had been missing after bombs hit a southern village.
Geopolitics BBC World
Strategic relevanceThe reported strike and missing people are relevant to the conflict’s civilian impact in southern Ukraine.
Sources1BBC World
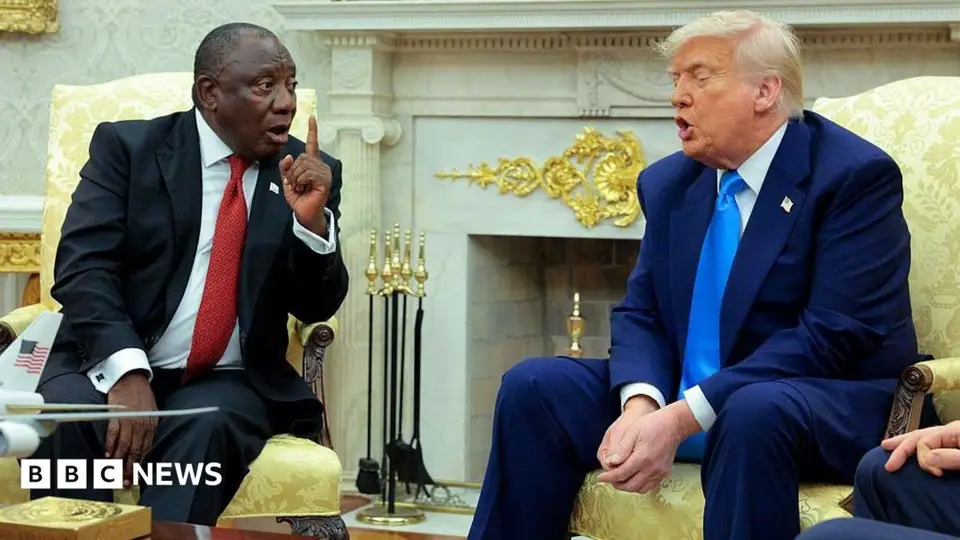
Trump to remove Rwanda and South Africa from US trade deal (opens the original article)
The BBC reports that Trump plans to remove Rwanda and South Africa from a U.S. trade deal, following sanctions on Rwanda's defence ministry.
Geopolitics BBC World
Strategic relevanceThe proposed trade change and sanctions link trade policy with U.S. relations in Africa.
Sources1BBC World
| CVE | CVSS | Product | Ransomware | Added / due | Required action |
|---|---|---|---|---|---|
| CVE-2026-118527 | —No score | Ivanti Connect Secure | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-111357 | 7.0High | Ivanti Connect Secure | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-97229 | 10.0Critical | GitLab Community Edition and Enterprise Edition | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-76418 | 8.6High | Cisco Secure Firewall ASA Software and Cisco Secure FTD Software | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-41709 | 2.7Low | Broadcom VMware ESX | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-46300 | 7.8High | Linux Kernel | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-48356 | 9.3Critical | Adobe Commerce and Magento | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-111497 | 9.2Critical | Google Brotli | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-109618 | 9.2Critical | PHP Group PHP | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-109619 | 9.2Critical | PHP Group PHP | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-114625 | 9.4Critical | Arista VeloCloud Orchestrator | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-110447 | 9.2Critical | Collabora Collabora Online – Built-in CODE Server | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
Source: CISA KEV catalogue; CVSS scores from NVD where published. “No score” means NVD has not scored it yet.
Keyword index
Counted from this page. Select one to filter.