 OUTPOST
Edition 233 — 4 November 2026
Cyber, warfare technology and geopolitics as compiled on 4 November 2026.
Cyber
Breaches, campaigns, advisories and research.
Google: LLMjacking attacks rack up $1 million in cloud AI charges (opens the original article)
Google says LLMjacking attacks are generating fraudulent cloud AI charges, with some organizations losing more than $100,000 per day.
Cyber BleepingComputer 2 outlets
What to checkReview access to cloud AI services and monitor usage and charges for unexpected activity.
Subnet Solutions PowerSYSTEM Center (opens the original article)
A CISA advisory for Subnet Solutions PowerSYSTEM Center says successful exploitation of vulnerabilities could allow an attacker to execute unauthorized actions; the snippet is incomplete.
Cyber CISA Advisories
What to checkCheck the full advisory and assess whether affected PowerSYSTEM Center systems need attention.
Sources1CISA Advisories
CISA Adds One Known Exploited Vulnerability to Catalog (opens the original article)
CISA added one vulnerability to its Known Exploited Vulnerabilities Catalog based on evidence of active exploitation.
Cyber CISA Advisories
What to checkCheck whether the listed vulnerability affects your systems and prioritize remediation as appropriate.
Sources1CISA Advisories
Hackers hijack cPGuard autoupdate to deploy backdoor, steal data (opens the original article)
Attackers compromised cPGuard’s update infrastructure to distribute a backdoor and a data-stealing script, BleepingComputer reports.
Cyber BleepingComputer
What to checkCheck cPGuard update integrity and systems for signs of backdoor installation or data theft.
Sources1BleepingComputer
WorkOS says attacker used ARTEX AI to breach internal sales app (opens the original article)
WorkOS says an attacker accessed business contact records and summaries of customer communications in a breach of its internal sales app.
Cyber BleepingComputer
What to checkReview access to sales applications and consider what sensitive information their records contain.
Sources1BleepingComputer
Binance says fake job interview led to $6.3 billion crypto heist (opens the original article)
Binance says a fake job interview led an employee to install malware, enabling attackers to compromise wallet infrastructure and steal digital assets.
Cyber BleepingComputer
What to checkCheck recruitment-related security controls and access to critical wallet infrastructure.
Sources1BleepingComputer
Google dismantles massive botnet hidden in Android TV boxes (opens the original article)
Google says most devices in the X.CPE botnet were Android TV boxes; other infected devices included telehealth equipment, karaoke machines and digital signage.
Cyber The Record
What to checkInventory Android-based connected devices and check how they are monitored and secured.
Sources1The Record
Several German lawmakers and foreign policy staff received Apple warnings on spyware (opens the original article)
Apple warned spyware targets in 99 countries, including members of Germany's political elite.
Cyber The Record
What to checkTreat spyware warnings as a reason to review device security and follow relevant guidance.
Sources1The Record
British businesses caught in Europe-wide supermarket fridge attacks (opens the original article)
Refrigerator controls at supermarkets and grocery stores across Europe were hacked, with perpetrators defrosting fridges, according to the report.
Cyber The Record
What to checkReview access to refrigeration controls and the monitoring of changes to their settings.
Sources1The Record
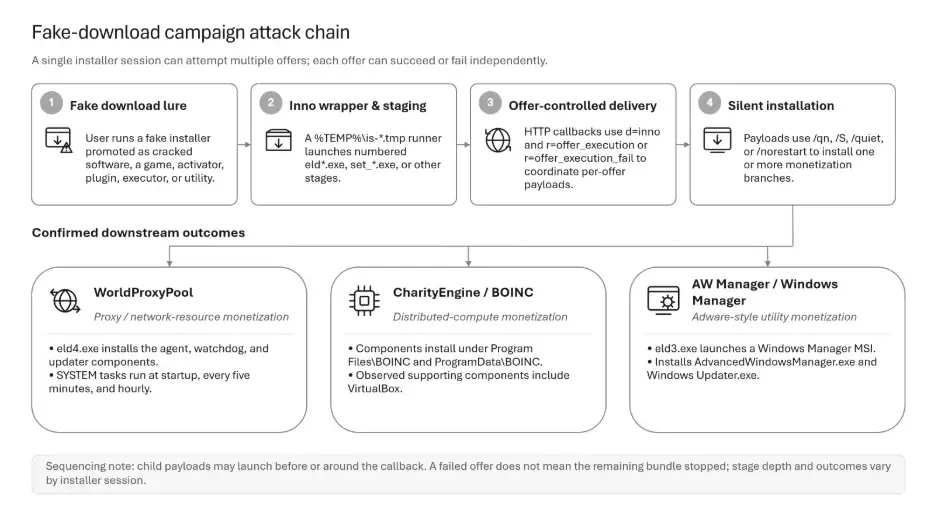
Fake-download campaign uses trojanized installers to deliver monetization payloads (opens the original article)
Microsoft says a fake-download campaign uses trojanized Inno installers to deliver monetization offers and provides detection and investigation guidance.
Cyber Microsoft Security
What to checkUse Microsoft's detection guidance to investigate suspicious installer sessions.
Sources1Microsoft Security
Warfare
Drones, electronic warfare, missiles and defence systems.
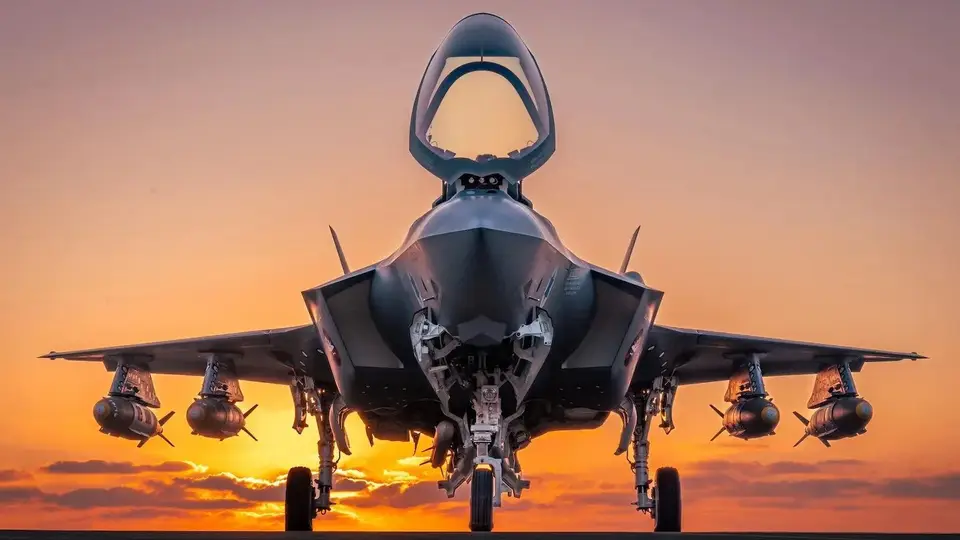
What Trump’s Drastic Reduction Of U.S. Military Aid To Israel Could Mean (opens the original article)
Trump announced he was cutting off Israel’s annual military aid by the end of the year, The War Zone reports.
Warfare The War Zone
Why it mattersThe reported aid change may affect military support and planning.
Sources1The War Zone
The Cost of Waiting: Why the Houthis Are Getting More Dangerous and Where to Hit Them (opens the original article)
A War on the Rocks article revisits the Houthis' Red Sea gains, the limits of killing leaders and the prospect of a ceasefire giving them time to rearm.
Warfare War on the Rocks
Why it mattersThe article highlights the operational limits of leadership targeting and the role of time to rearm.
Sources1War on the Rocks
AUSA 2026: The ground truth on the Army’s next chapter (opens the original article)
Breaking Defense examines US Army developments and priorities, including autonomous warfare, drones, acquisition reform and the defense industrial base.
Warfare Breaking Defense
Why it mattersThese priorities connect future operational concepts with procurement and industrial capacity.
Sources1Breaking Defense
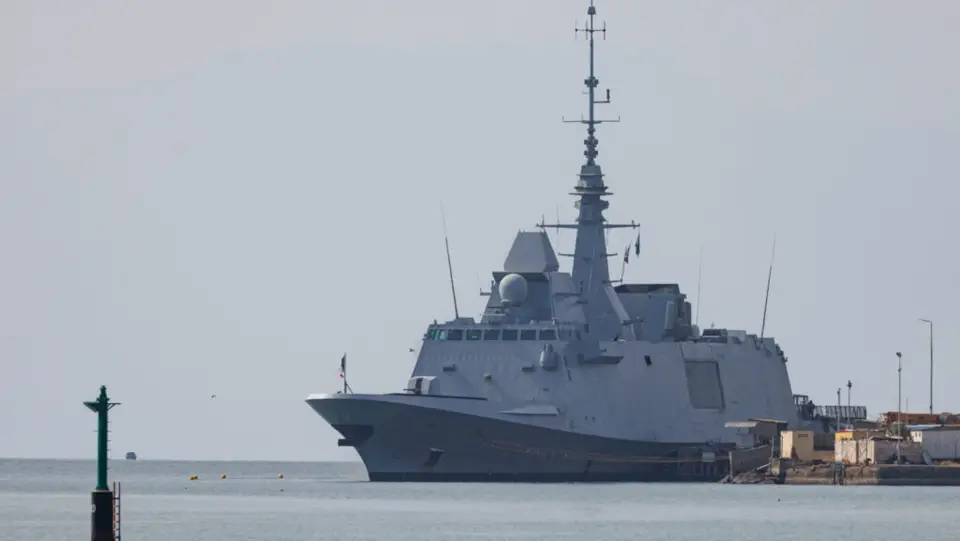
France investing in naval power as military ambition is ‘to be feared’: Armed forces minister (opens the original article)
France's armed forces minister described the country's military ambition as 'to be feared'; the snippet also refers to Macron's nuclear strategy address.
Warfare Breaking Defense
Why it mattersThe remarks relate French military ambition to its wider strategic posture.
Sources1Breaking Defense
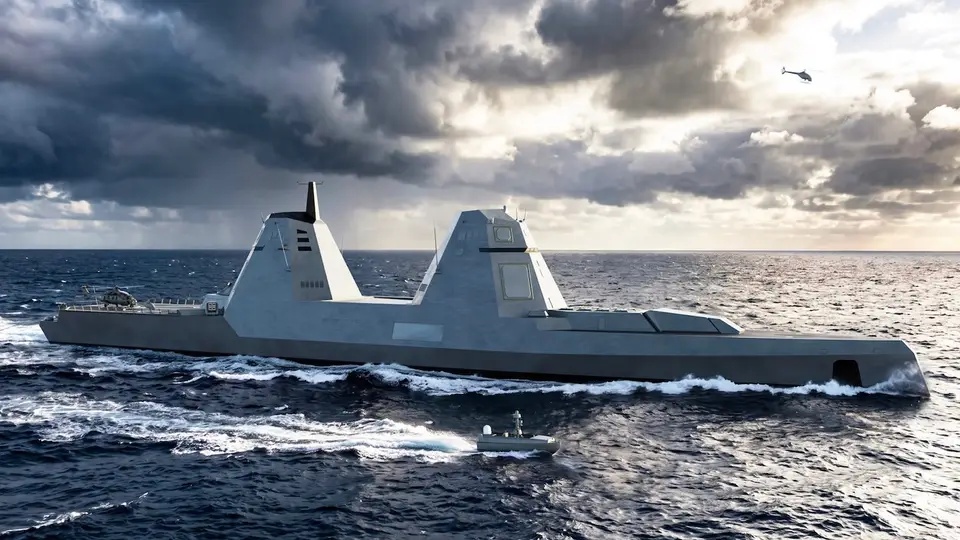
This Is Naval Group’s Concept For A Stealthy, Drone-Armed Future Destroyer (opens the original article)
Naval Group's SCX26 concept pairs a stealthy split-superstructure design with advanced weapons and facilities for uncrewed systems.
Warfare The War Zone
Why it mattersThe concept illustrates how a future destroyer might integrate stealth and uncrewed systems.
Sources1The War Zone
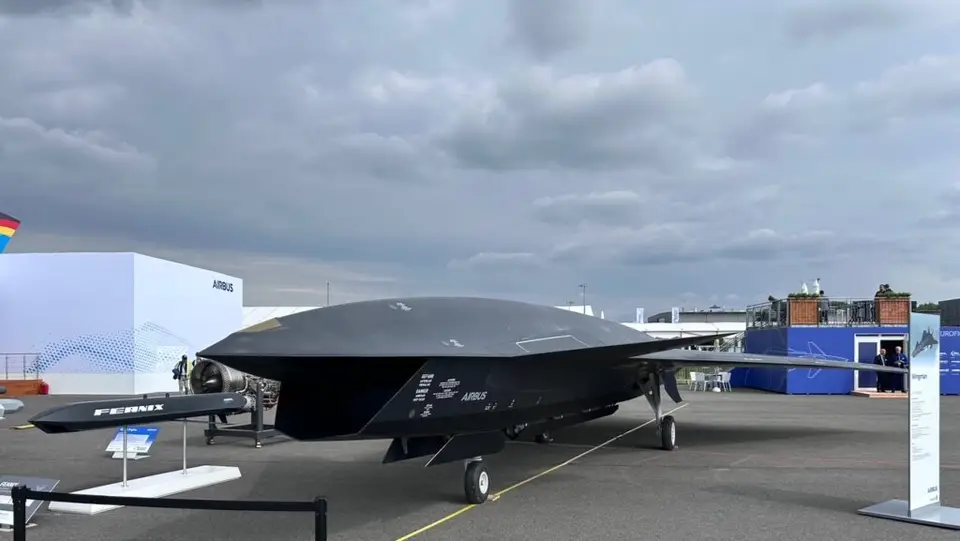
Wingman out, Ravenstorm in: Airbus changes tact to meet Germany’s accelerated operations timeline (opens the original article)
Airbus is prioritizing development of the U760 Ravenstorm, which has a subsonic cruise speed and an internal weapons payload of 500kg.
Warfare Breaking Defense
Why it mattersThe reported shift links aircraft development to Germany's accelerated operations timeline.
Sources1Breaking Defense
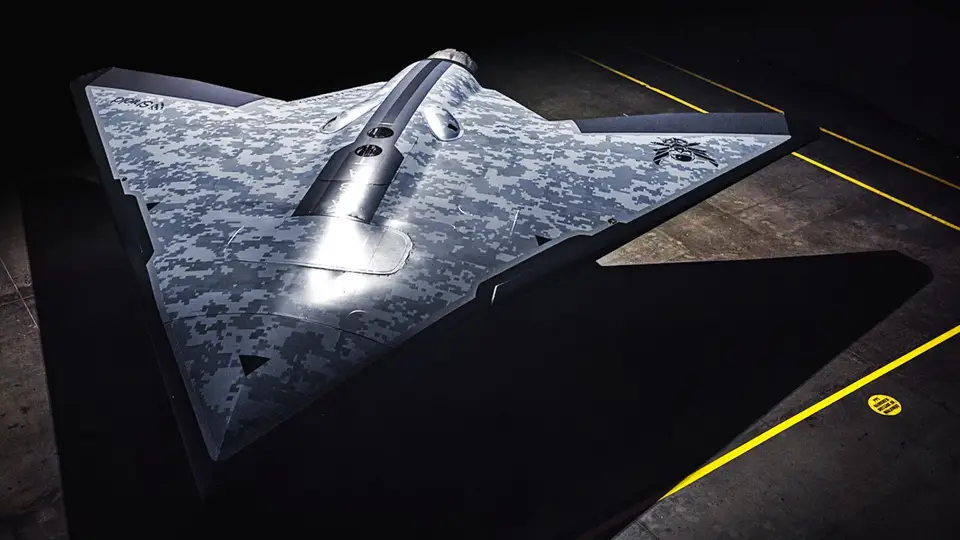
Prototype X-BAT VTOL ‘Fighter’ Drone Unveiled (opens the original article)
Shield AI has unveiled the prototype X-BAT, described as a multi-role combat drone with a tail-sitting vertical takeoff and landing design.
Warfare The War Zone
Why it mattersThe prototype's VTOL design is relevant to how combat drones may operate from varied launch settings.
Sources1The War Zone
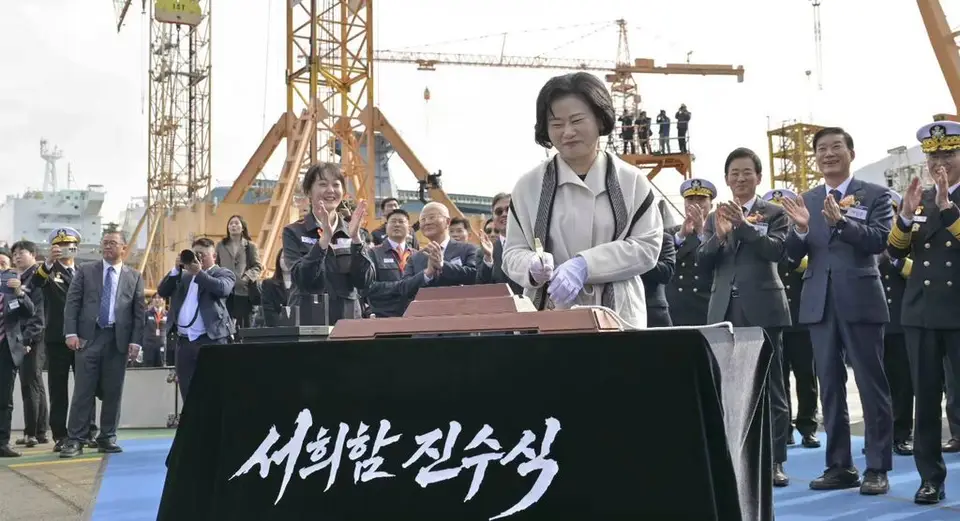
South Korea Launches Second KSS-III Batch-II Submarine, ROKS Seo Hui (opens the original article)
The Republic of Korea Navy launched Seo Hui, the second Jang Bogo KSS-III Batch-II submarine; the snippet notes domestically developed equipment.
Warfare Naval News
Why it mattersThe launch reflects South Korea's submarine program and domestic equipment development.
Sources1Naval News
Geopolitics & geodata
Strategy, geo wars, GNSS and satellite security.
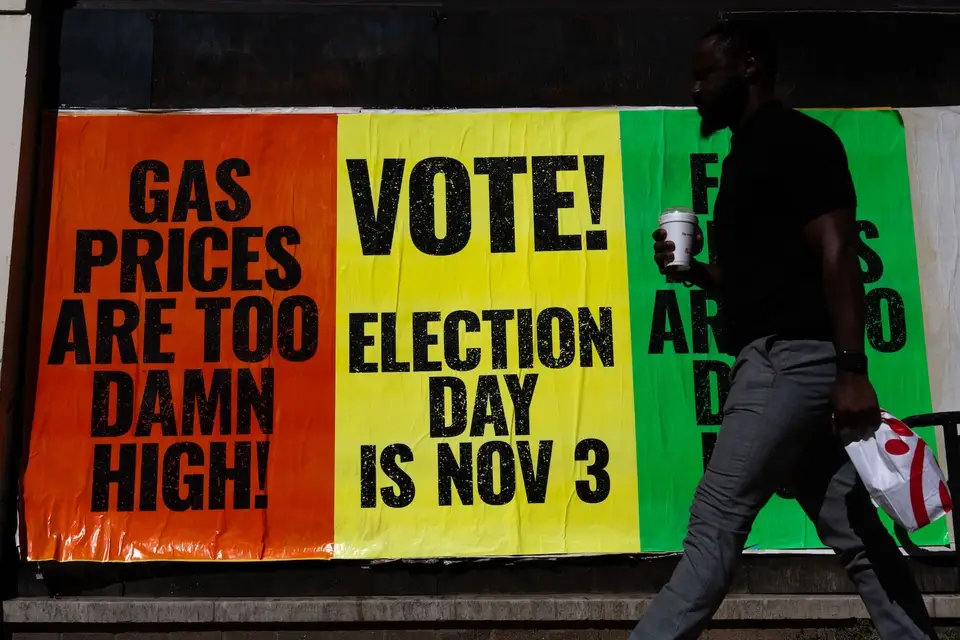
Iran Strikes and Israel Aid Cuts Shake Up Election Day (opens the original article)
Foreign Policy says two last-minute foreign-policy developments could affect U.S. voters’ midterm decisions.
Geopolitics Foreign Policy
Strategic relevanceThe item links foreign-policy developments with domestic electoral decisions.
Sources1Foreign Policy
A $6 billion hack in a season of AI anxiety (opens the original article)
The Atlantic Council reports headlines about a $6.3 billion Binance hack and AI-assisted vulnerability discoveries, while cautioning that not everything is as new or alarming as it seems.
Geopolitics Atlantic Council
Strategic relevanceThe discussion may help analysts distinguish novel risks from familiar ones.
Sources1Atlantic Council
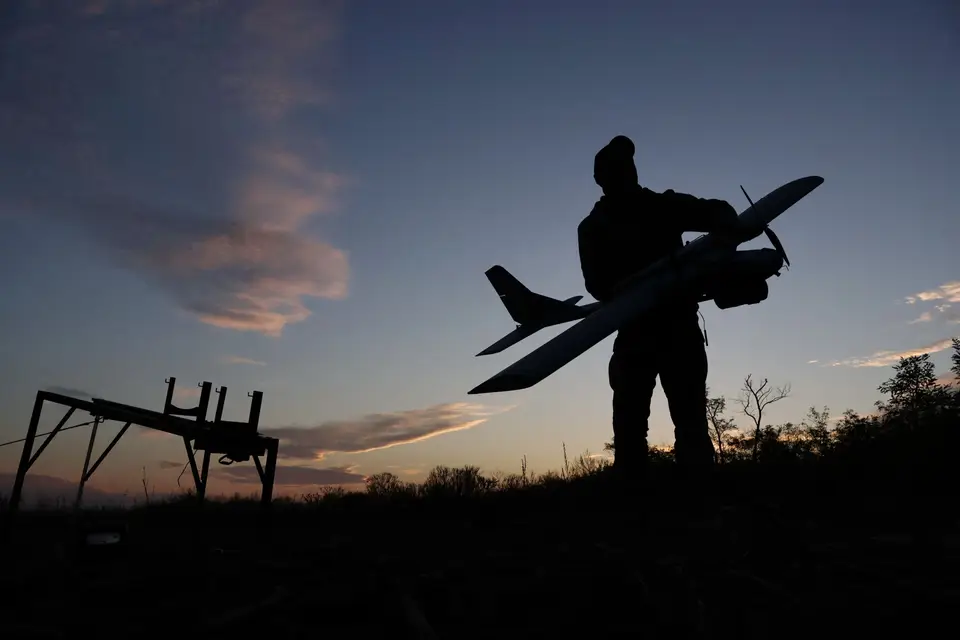
Europe must weigh rising Ukraine costs against higher price of Russian victory (opens the original article)
Peter Dickinson argues that the consequences of a Russian victory in Ukraine would outweigh the current cost of supporting Kyiv.
Geopolitics Atlantic Council
Strategic relevanceThe argument frames support for Ukraine as a strategic cost comparison for Europe.
Sources1Atlantic Council
Safran Launches StarSync™ U4, a New Generation of High-Accuracy and Resilient Timing (opens the original article)
Safran introduced StarSync U4, a high-performance time server and interoperability platform designed for high-speed Ethernet networks.
Geopolitics Inside GNSS
Strategic relevanceResilient timing and interoperability are relevant to systems that depend on network time.
Sources1Inside GNSS
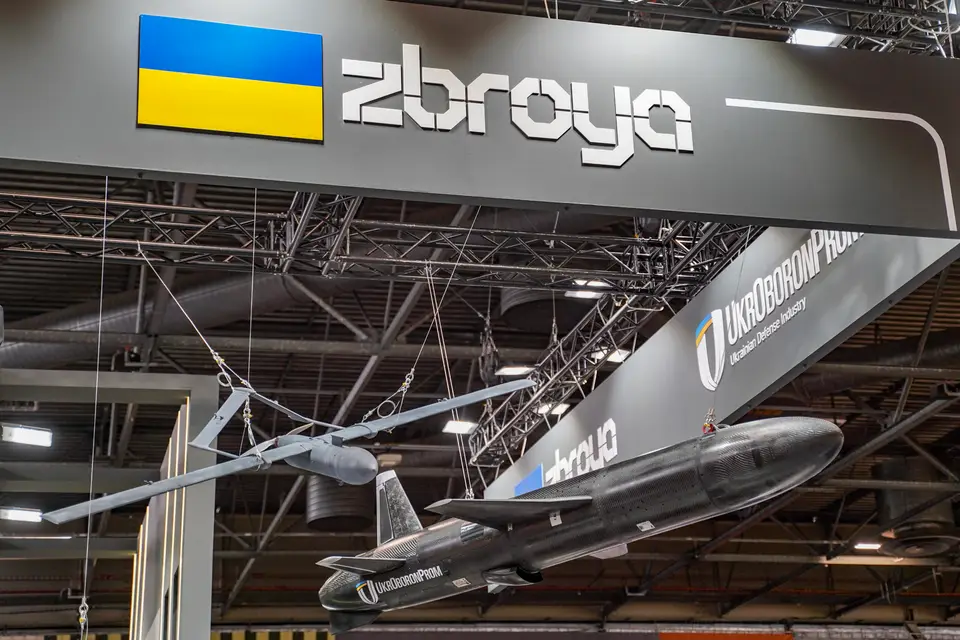
A strong defense industry may be Ukraine’s best security guarantee (opens the original article)
The article argues that a strong Ukrainian military backed by a domestic defense industry may be Ukraine's most realistic security guarantee.
Geopolitics Atlantic Council
Strategic relevanceThe piece links Ukraine's security prospects to military capacity and domestic industry.
Sources1Atlantic Council
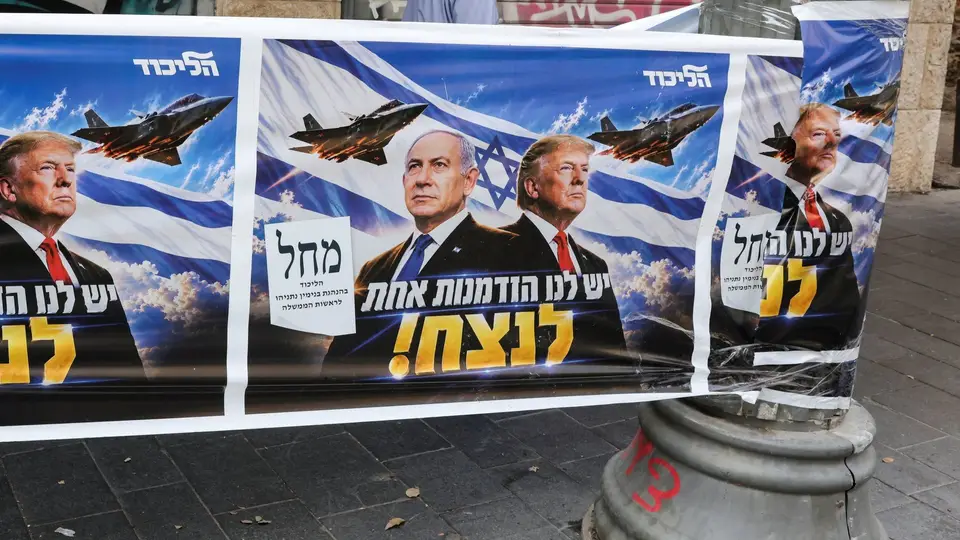
Scepticism as Trump says he’s ending Israel’s $3.8 bn military aid deal (opens the original article)
Trump says he plans to stop Israel’s annual $3.8bn military aid package by the end of the year, Al Jazeera reports.
Geopolitics Al Jazeera
Strategic relevanceThe stated plan is relevant to assessing military support for Israel.
Sources1Al Jazeera
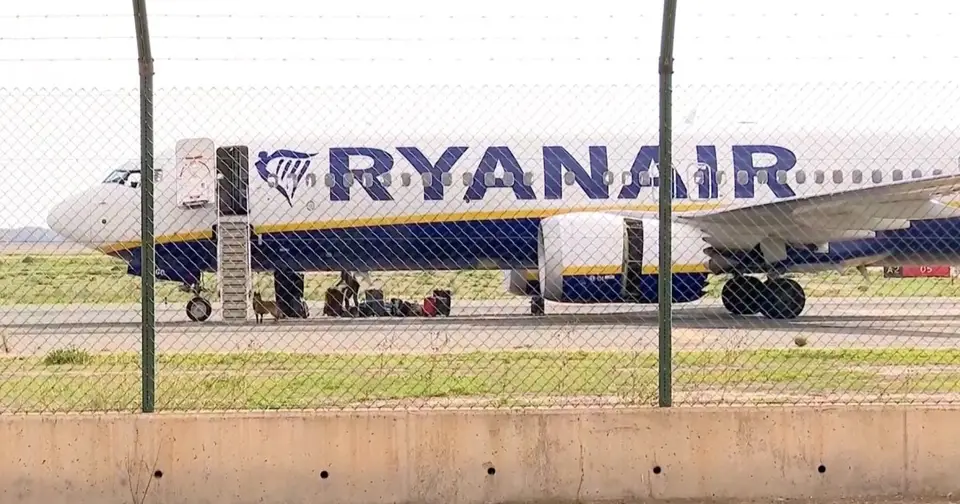
Bomb threats disrupt flights across Europe, no explosive devices found (opens the original article)
Threats targeted at least seven flights and an Israel-bound cruise ship; officials say searches found no explosives, Al Jazeera reports.
Geopolitics Al Jazeera
Strategic relevanceThe disruptions highlight the need to track threat reports and search outcomes across transport routes.
Sources1Al Jazeera
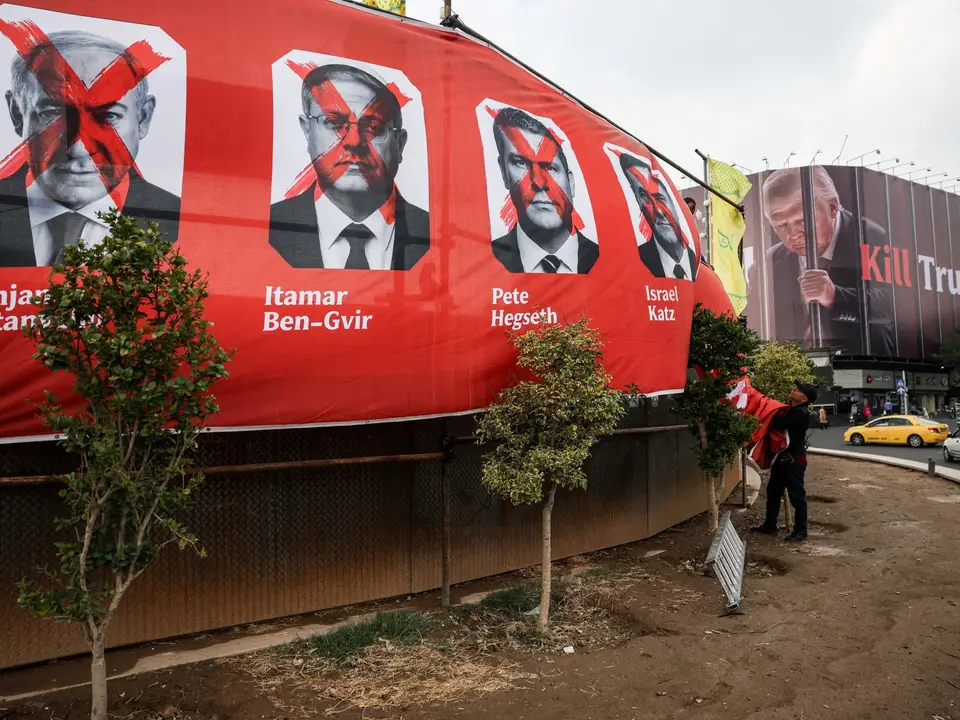
Iran war live: Tehran prepares ‘maximum deterrence’ plan for any new attack (opens the original article)
Iran says it has a ‘maximum deterrence’ plan ready for any new U.S. attack and warns of an immediate response, Al Jazeera reports.
Geopolitics Al Jazeera
Strategic relevanceThe stated plan and warning are relevant to understanding Iran’s posture toward a possible attack.
Sources1Al Jazeera
| CVE | CVSS | Product | Ransomware | Added / due | Required action |
|---|---|---|---|---|---|
| CVE-2026-119977 | 8.1High | WordPress WordPress Core | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-118527 | 4.3Medium | Ivanti Connect Secure | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-111357 | 7.0High | Ivanti Connect Secure | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-97229 | 10.0Critical | GitLab Community Edition and Enterprise Edition | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-76418 | 8.6High | Cisco Secure Firewall ASA Software and Cisco Secure FTD Software | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-41709 | 2.7Low | Broadcom VMware ESX | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-46300 | 7.8High | Linux Kernel | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-48356 | 9.3Critical | Adobe Commerce and Magento | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-111497 | 9.2Critical | Google Brotli | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-109618 | 9.2Critical | PHP Group PHP | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-109619 | 9.2Critical | PHP Group PHP | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-114625 | 9.4Critical | Arista VeloCloud Orchestrator | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
Source: CISA KEV catalogue; CVSS scores from NVD where published. “No score” means NVD has not scored it yet.
Keyword index
Counted from this page. Select one to filter.