 OUTPOST
Edition 234 — 5 November 2026
Cyber, warfare technology and geopolitics as compiled on 5 November 2026.
Cyber
Breaches, campaigns, advisories and research.
Vercel rolls out new protection against stolen session cookie attacks (opens the original article)
Vercel is gradually rolling out Device Bound Session Credentials as a defense against information stealer malware.
Cyber BleepingComputer
What to checkCheck whether session credentials are protected against theft and whether the new defense is available in your environment.
Sources1BleepingComputer
More Asian airlines announce data breaches after attack on Spanish IT provider Amadeus (opens the original article)
Several Asian airlines reported data breaches traced back to Amadeus IT Group, which builds and maintains platforms for flight reservations.
Cyber The Record
What to checkReview exposure to the affected provider and check for relevant breach notices.
Sources1The Record
Zyxel fixes zero-day exploited to hack nearly 1,000 network switches (opens the original article)
Zyxel patched a zero-day in GS1900 network switches that hackers exploited to compromise nearly 1,000 devices and steal configuration files and credentials.
Cyber BleepingComputer
What to checkApply Zyxel’s patch and check affected switches for compromise and exposed credentials.
Sources1BleepingComputer
Canadian extradited to US for allegedly hacking schools in at least four states (opens the original article)
The Department of Justice said it identified two suspects in a case involving illicit cryptomining on U.S. educational institutions’ computers.
Cyber The Record
What to checkThe report highlights the need to check institutional computers for unauthorized cryptomining.
Sources1The Record
DreamHost confirms data breach exposed FTP logins and webmail sessions (opens the original article)
DreamHost says attackers accessed its File Manager platform for two months and stole customers’ FTP/SFTP usernames and passwords.
Cyber BleepingComputer
What to checkCheck FTP/SFTP credentials and webmail sessions, and review relevant access for signs of misuse.
Sources1BleepingComputer
French bank confirms cyber heist, hackers suspected to have stolen an estimated $133 million (opens the original article)
Crédit Mutuel Arkéa said attackers made transfers using the bank’s own account after compromising an unnamed supplier.
Cyber The Record
What to checkReview supplier access and transfers involving organizational accounts.
Sources1The Record
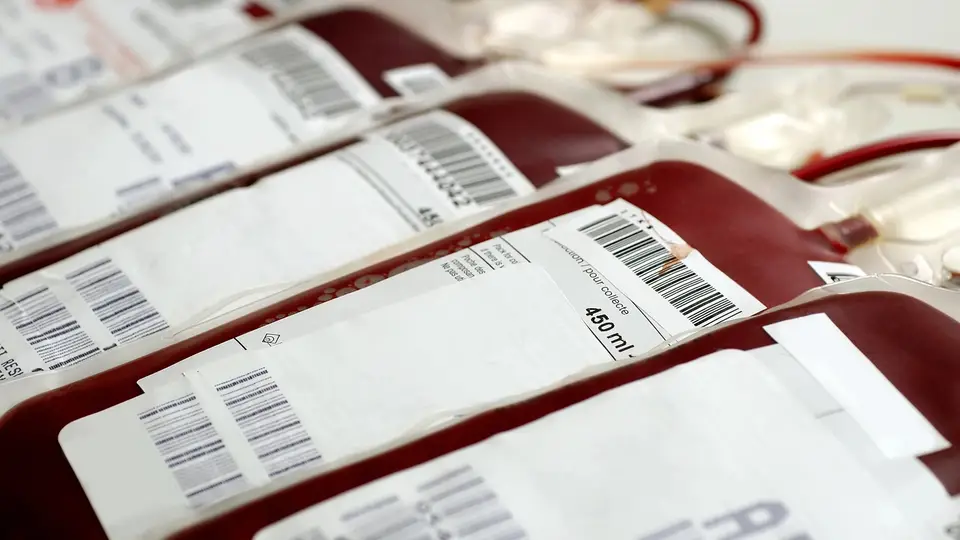
Cyberattack disrupts blood storage refrigeration systems in France (opens the original article)
France's national blood service says a cyberattack targeting a refrigeration provider altered temperature and defrost settings at three facilities, threatening stored blood products.
Cyber BleepingComputer
What to checkCheck refrigeration controls and provider access for unauthorized setting changes.
Sources1BleepingComputer
NIKKE PC game launcher hacked to spread remote access, data-stealing malware (opens the original article)
The developers of Goddess of Victory: NIKKE say hackers altered PC launcher scripts in a supply-chain attack, distributing malware that can steal credentials and cryptocurrency wallet data.
Cyber BleepingComputer
What to checkVerify game launcher scripts and review endpoints for credential or wallet theft.
Sources1BleepingComputer
Ukrainian news outlet Kyiv Independent hit by suspected Russian cyberattack (opens the original article)
A suspected Russian cyberattack disrupted the website of Ukrainian news outlet The Kyiv Independent.
Cyber The Record
What to checkReview website availability and incident evidence while treating attribution as suspected.
Sources1The Record
mSecure password manager hack prompts password reset warnings (opens the original article)
mSeven Software warns current and former mSecure customers to change passwords, reset two-factor authentication, and remove passkeys after a cyberattack reportedly exposed an encrypted customer database.
Cyber BleepingComputer
What to checkFollow the vendor's reset guidance and check for reused passwords or affected authentication methods.
Sources1BleepingComputer
Warfare
Drones, electronic warfare, missiles and defence systems.
NASA Announces X-70 “Fractal” Experimental Aircraft (opens the original article)
The War Zone says NASA’s X-70 will test new flight-control capabilities and push the bounds of maneuverability.
Warfare The War Zone
Why it mattersIts flight-control testing may inform how experimental aircraft pursue greater maneuverability.
Sources1The War Zone
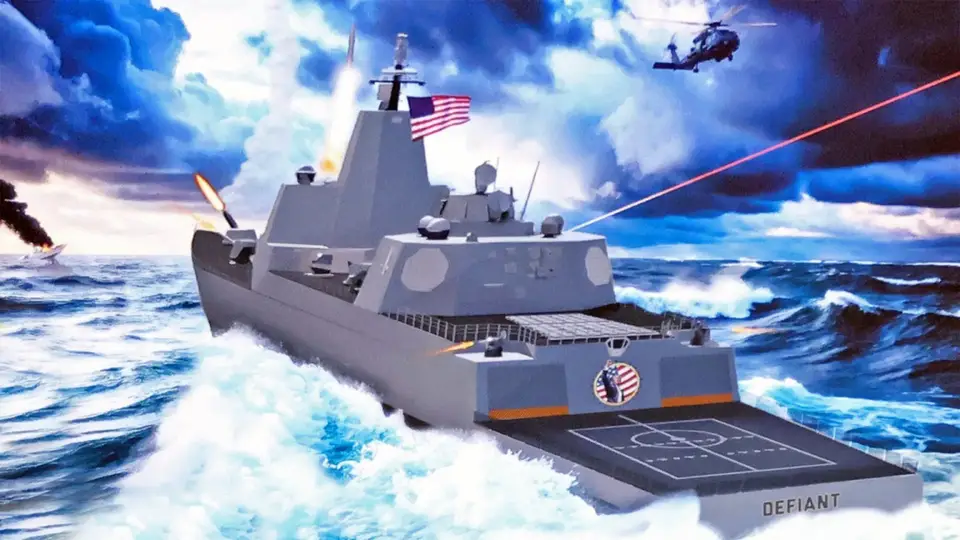
Did The Blue Wave Just Sink Trump’s Battleship? (opens the original article)
The validity and cost of President Trump’s battleship program were already under fire before Democrats’ historic mid-term wins.
Warfare The War Zone
Why it mattersThe debate links political developments with scrutiny of a proposed military program.
Sources1The War Zone
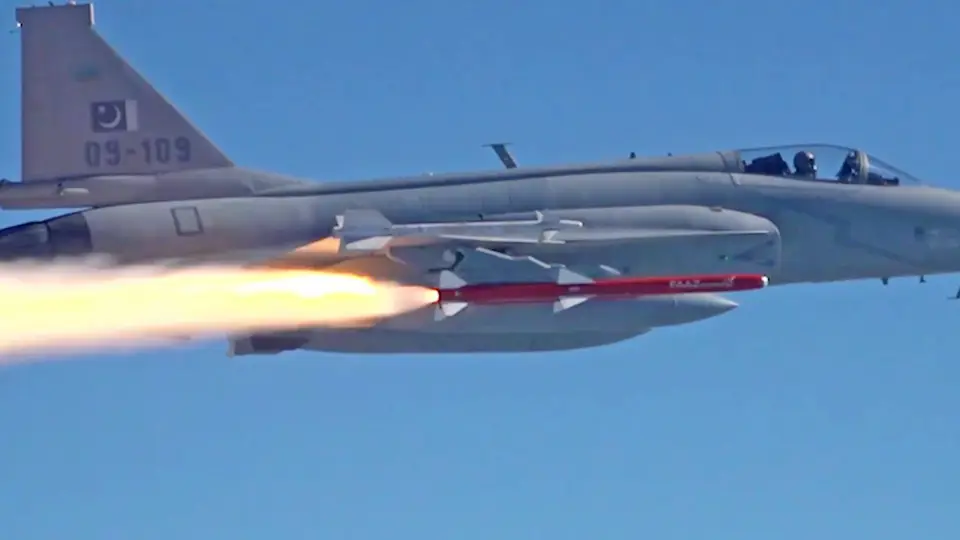
Pakistan Joins Air-to-Air Missile Club With Successful Test Of Fa’az (opens the original article)
Pakistan’s successful Fa’az test is described as a major step toward a homegrown air-to-air missile capability.
Warfare The War Zone
Why it mattersThe test is relevant to Pakistan’s development of domestic air-to-air weapons.
Sources1The War Zone
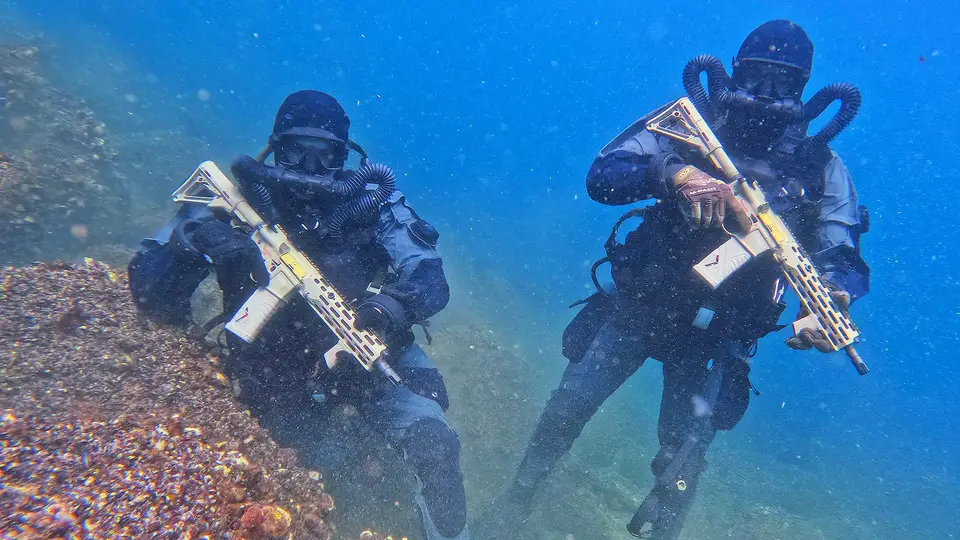
Ukrainian Soldiers Tell Us Which Guns And Optics Work Best In Combat (opens the original article)
Ukrainian troops describe their preferences for rifles, optics, and other equipment used in combat.
Warfare The War Zone
Why it mattersTroops’ equipment preferences offer an operational perspective on small arms and optics.
Sources1The War Zone
Why Are Wars Increasingly Difficult to End? (opens the original article)
Researchers warn that many armed conflicts are lasting longer and have become more difficult to end; experts consider whether that trend is continuing.
Warfare War on the Rocks
Why it mattersThe discussion concerns the duration of conflicts and the challenges of ending wars.
Sources1War on the Rocks
The Army’s Command-and-Control Reboot (opens the original article)
The Army’s Next Generation Command and Control is changing how it makes decisions, communicates orders, and coordinates forces.
Warfare War on the Rocks
Why it mattersThe reboot is relevant to how the Army coordinates decisions, communications, and operations.
Sources1War on the Rocks
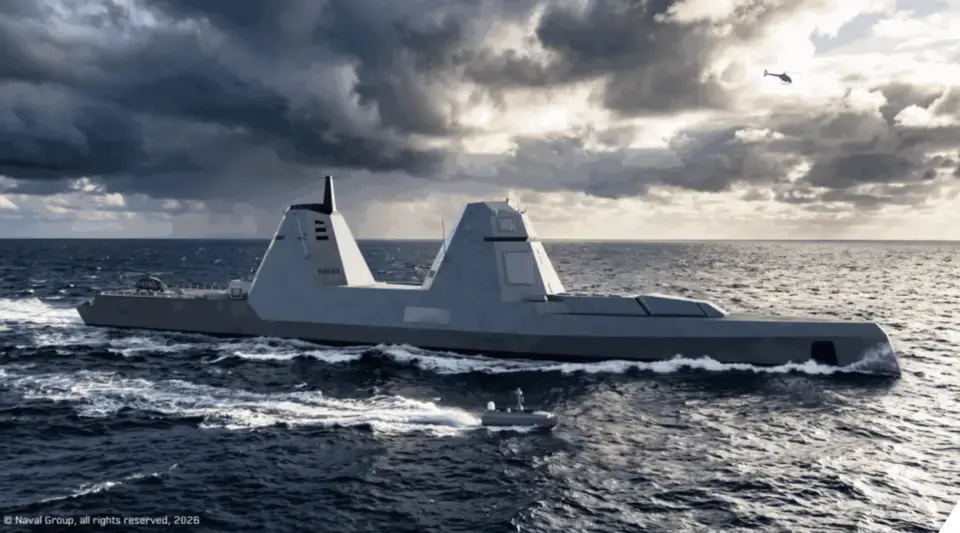
Naval Group unveils new drone carrier concept (opens the original article)
Naval Group says its SCX 26 drone carrier concept answers the return of high-intensity conflict and the emergence of hybrid naval warfare.
Warfare Breaking Defense
Why it mattersThe concept connects drone carriers with the company’s view of changing naval warfare.
Sources1Breaking Defense
Amid Iran conflict, ‘non-hostile’ deaths of 2 US airmen raise overseas toll (opens the original article)
Two U.S. airmen supporting operations against Iran died in incidents described as non-hostile, raising the reported death toll since the war began.
Warfare Defense News
Why it mattersThe report concerns personnel losses during operations against Iran.
Sources1Defense News
Geopolitics & geodata
Strategy, geo wars, GNSS and satellite security.
Vance walks Trump tightrope with scathing election critique blaming Iran war (opens the original article)
BBC World reports that the vice-president’s critique of a Republican election defeat blamed the Iran war and marked a sharp break with a sitting president.
Geopolitics BBC World
Strategic relevanceThe dispute links election politics with debate over the Iran war.
Sources1BBC World
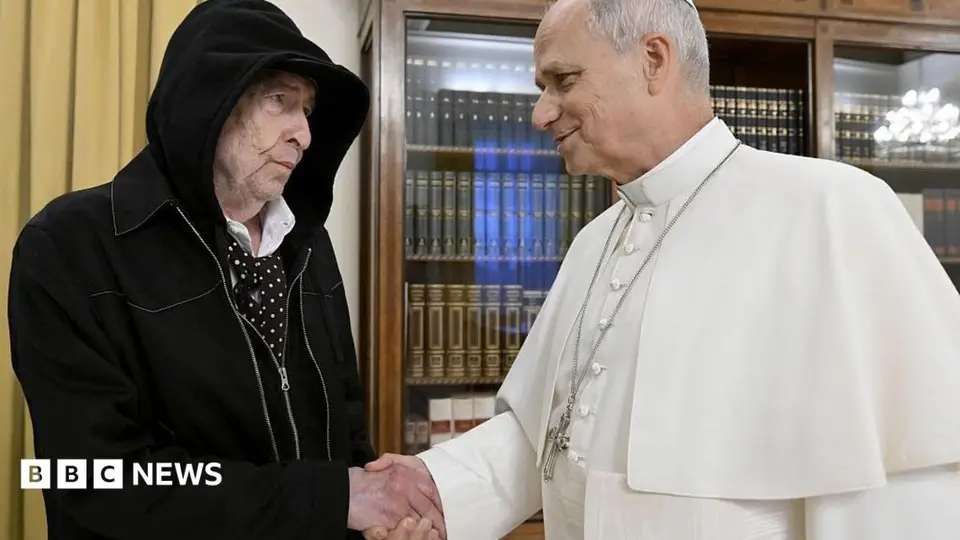
Pope Leo hosts Bob Dylan at official residence in Rome (opens the original article)
BBC World reports that Pope Leo hosted Bob Dylan in Rome. Leo had previously quoted Dylan in a book preface warning against nuclear rearmament.
Geopolitics BBC World
Strategic relevanceThe reported connection brings public cultural figures into discussion of nuclear rearmament.
Sources1BBC World
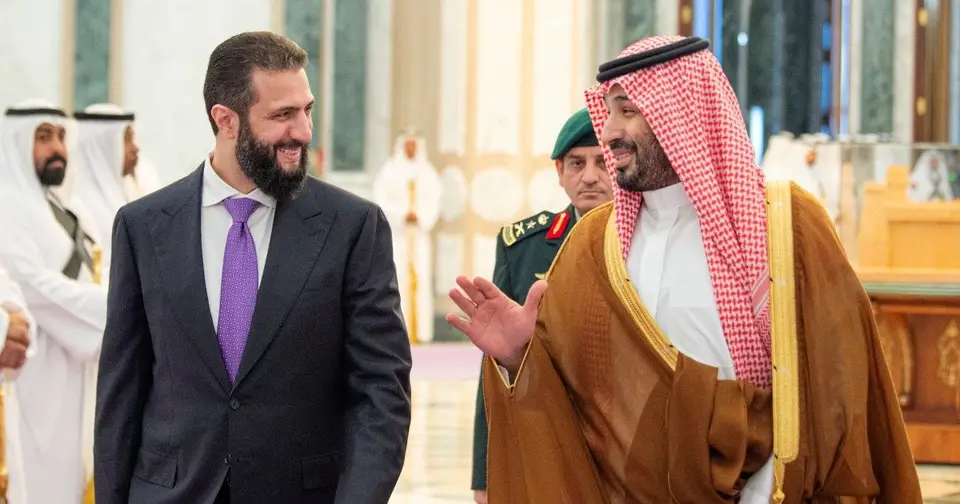
Syria, Saudi Arabia sign defence cooperation deal, agree $403m in loans (opens the original article)
Al Jazeera reports that Syria and Saudi Arabia signed a defence cooperation deal and agreed to loans during President al-Sharaa’s visit to Riyadh.
Geopolitics Al Jazeera
Strategic relevanceThe deal and visit are relevant to defence ties between Syria and Saudi Arabia.
Sources1Al Jazeera
Rohde & Schwarz Puts GNSS Resilience to the Test (opens the original article)
Rohde & Schwarz is providing receiver developers a controlled environment to test GNSS resilience as jamming and spoofing threaten satellite navigation.
Geopolitics Inside GNSS
Strategic relevanceTesting receiver resilience can help assess responses to GNSS jamming and spoofing.
Sources1Inside GNSS
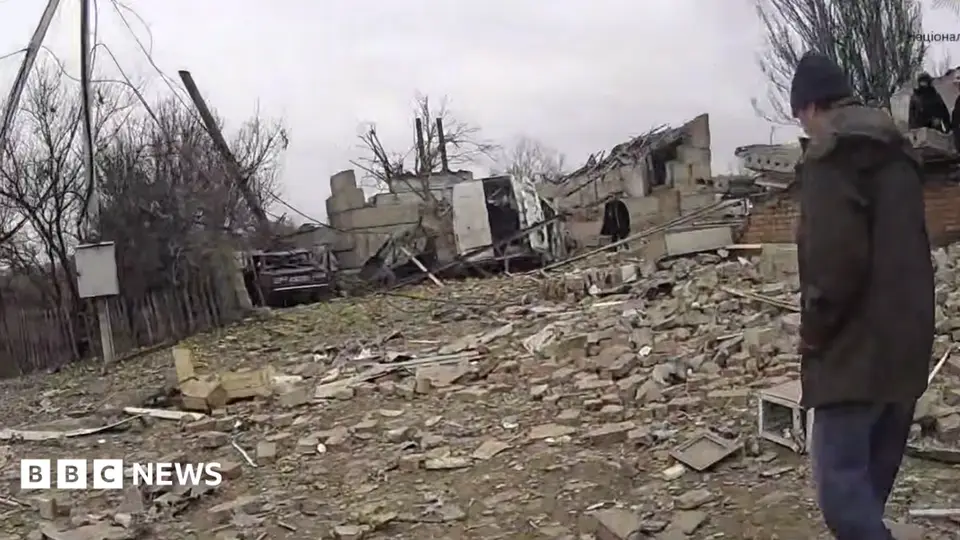
Ukraine says bodycam video shows deadly Russian double-tap bombing (opens the original article)
Kyiv says bodycam video shows a deadly Russian double-tap bombing in a Ukrainian village; at least 40 people were killed and another 30 may remain under rubble.
Geopolitics BBC World
Strategic relevanceThe reported attack and casualties are relevant to understanding the human impact of the conflict.
Sources1BBC World
Why this US midterm was unusually important for the Middle East (opens the original article)
The Atlantic Council says midterm losses may reduce the immediate risk of renewed U.S. strikes on Iran but could drive Trump toward escalation later.
Geopolitics Atlantic Council
Strategic relevanceThe analysis links U.S. electoral outcomes with possible changes in Iran policy.
Sources1Atlantic Council
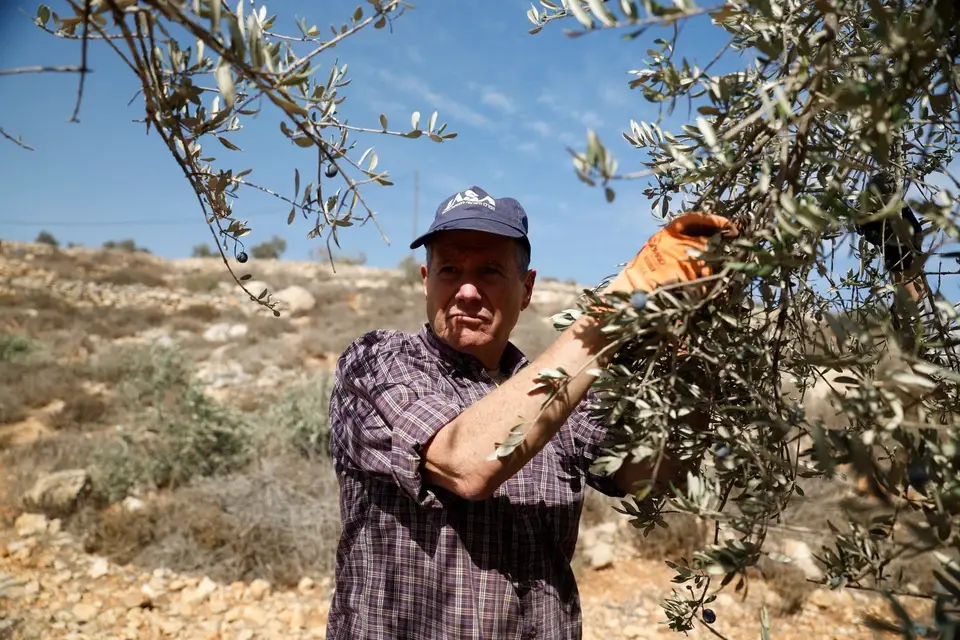
Former Israeli generals help Palestinian olive farmers (opens the original article)
Al Jazeera reports that former Israeli military generals offered help to Palestinian olive farmers in the occupied West Bank.
Geopolitics Al Jazeera
Strategic relevanceThe report concerns civilian livelihoods and former military figures in the occupied West Bank.
Sources1Al Jazeera
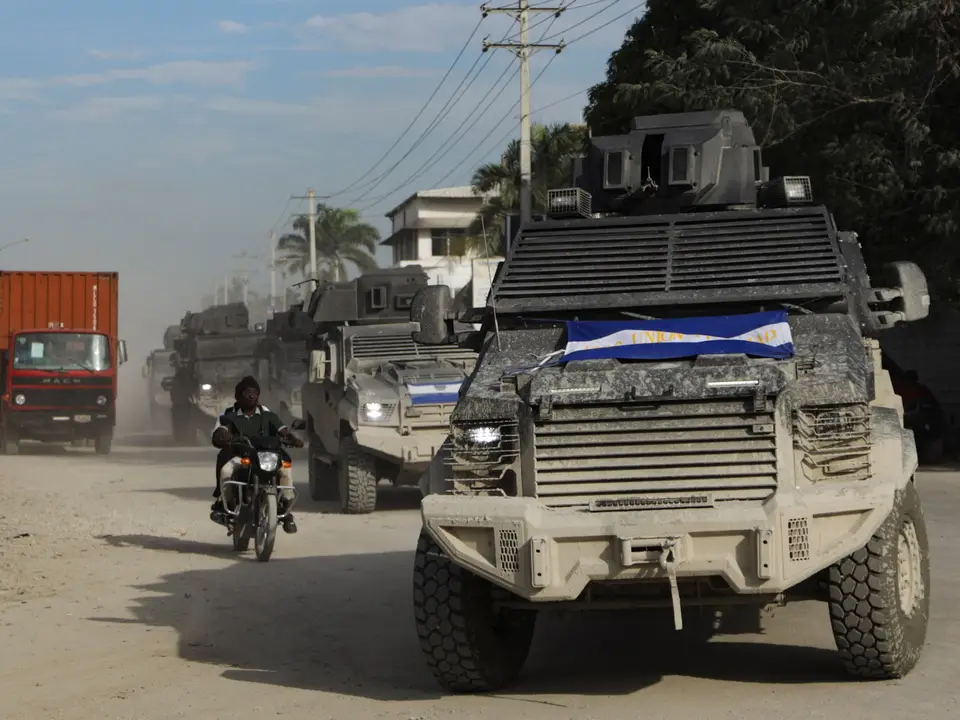
El Salvador’s Bukele touts military intervention in Haiti (opens the original article)
Al Jazeera reports that Salvadoran troops are deploying to Haiti and Haitian police found a vehicle used by four missing Salvadoran technicians.
Geopolitics Al Jazeera
Strategic relevanceThe report links a troop deployment with missing technicians and a police investigation.
Sources1Al Jazeera
| CVE | CVSS | Product | Ransomware | Added / due | Required action |
|---|---|---|---|---|---|
| CVE-2024-27834 | 5.5Medium | Apple Multiple Products | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-119977 | 8.1High | WordPress WordPress Core | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-118527 | 4.3Medium | Ivanti Connect Secure | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-111357 | 7.0High | Ivanti Connect Secure | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-97229 | 10.0Critical | GitLab Community Edition and Enterprise Edition | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-76418 | 8.6High | Cisco Secure Firewall ASA Software and Cisco Secure FTD Software | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-41709 | 2.7Low | Broadcom VMware ESX | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-46300 | 7.8High | Linux Kernel | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-48356 | 9.3Critical | Adobe Commerce and Magento | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-111497 | 9.2Critical | Google Brotli | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-109618 | 9.2Critical | PHP Group PHP | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-109619 | 9.2Critical | PHP Group PHP | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
Source: CISA KEV catalogue; CVSS scores from NVD where published. “No score” means NVD has not scored it yet.
Keyword index
Counted from this page. Select one to filter.