 OUTPOST
Edition 235 — 6 November 2026
Cyber, warfare technology and geopolitics as compiled on 6 November 2026.
Cyber
Breaches, campaigns, advisories and research.
OpenAI's new GPT-6 Cyber AI finds 81 Firefox flaws, 948 Linux bugs (opens the original article)
OpenAI says GPT-6 Cyber found 81 previously unknown high-severity Firefox vulnerabilities and developed working exploits for 948 Linux kernel flaws.
Cyber BleepingComputer 2 outlets
What to checkReview Firefox and Linux patch status, and assess exposure to vulnerabilities that may have working exploits.
CISA Adds One Known Exploited Vulnerability to Catalog (opens the original article)
CISA added one vulnerability to its Known Exploited Vulnerabilities Catalog, citing evidence of active exploitation.
Cyber CISA Advisories
What to checkCheck the KEV Catalog for the added vulnerability and prioritize affected systems for remediation.
Sources1CISA Advisories
Turning Up the Heat: Inside the Attacks on Europe’s Refrigeration System (opens the original article)
Unit 42 examines cyberattacks targeting European refrigeration systems and outlines defense and mitigation strategies.
Cyber Unit 42
What to checkReview defenses for refrigeration systems and check whether mitigation guidance applies to operational technology.
Sources1Unit 42
Medical services company settles with 4 states over 2023 hack of sensitive patient records (opens the original article)
A medical services company settled with four states over a 2023 hack involving sensitive patient records, according to The Record.
Cyber The Record
What to checkReview access controls and incident handling for systems containing sensitive patient records.
Sources1The Record
Fake security tools on GitHub push backdoors and infostealers (opens the original article)
Infected security projects on GitHub are targeting cybersecurity professionals with backdoor and information-stealer malware, BleepingComputer reports.
Cyber BleepingComputer
What to checkVerify security project sources and inspect downloaded tools for unexpected behavior before use.
Sources1BleepingComputer
Certificate authority DigiCert reports data breach involving business customer info (opens the original article)
DigiCert said an internal business system was unintentionally externally accessible and someone created an unauthorized account.
Cyber The Record
What to checkAudit external exposure of internal business systems and review account creation and access logs.
Sources1The Record
QNAP says hackers breaching NAS devices in Plex2Shell attacks (opens the original article)
QNAP says hackers are exploiting the Plex2Shell vulnerability chain to breach NAS devices and urges users to update Plex Media Server.
Cyber BleepingComputer
What to checkUpdate Plex Media Server on QNAP devices and check for signs of unauthorized access.
Sources1BleepingComputer
FBI agent pleads guilty to stealing $2.4 million in crypto from nation-state hackers (opens the original article)
The Record reports that an FBI agent admitted stealing cryptocurrency from nation-state hackers using his position on an investigative squad.
Cyber The Record
What to checkReview controls over investigative access and handling of cryptocurrency evidence.
Sources1The Record
Veeam warns of Software Appliance boot failures on AMD EPYC hosts (opens the original article)
Veeam warned of boot failures affecting Software Appliance virtual machines on hosts with AMD EPYC processors.
Cyber BleepingComputer
What to checkCheck whether affected virtual machines run on AMD EPYC hosts and monitor for boot failures.
Sources1BleepingComputer
IMSI vs IMEI: What Your Phone Broadcasts and Who Can Read It (opens the original article)
The item explains that IMSI and IMEI are identifiers phones share with networks, and says rotating an IMSI can blunt tracking.
Cyber BleepingComputer
What to checkReview how devices expose identifiers and what options reduce tracking.
Sources1BleepingComputer
Warfare
Drones, electronic warfare, missiles and defence systems.
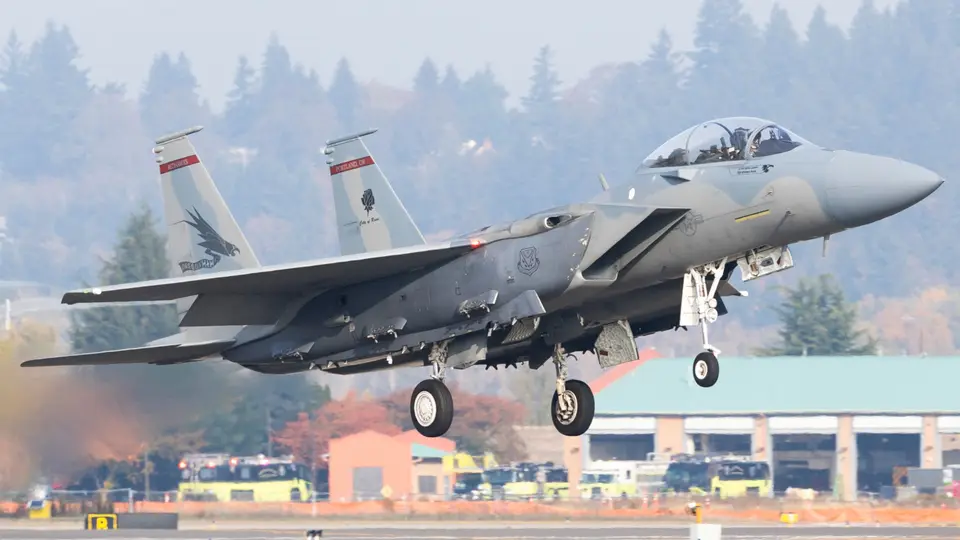
Operational F-15EXs Have Started Flying With Conformal Fuel Tanks (opens the original article)
Operational F-15EX aircraft have begun flying with conformal fuel tanks; the aircraft’s mission demands are evolving, The War Zone reports.
Warfare The War Zone
Why it mattersThe tanks reflect an operational change to an aircraft originally focused on air-to-air combat.
Sources1The War Zone
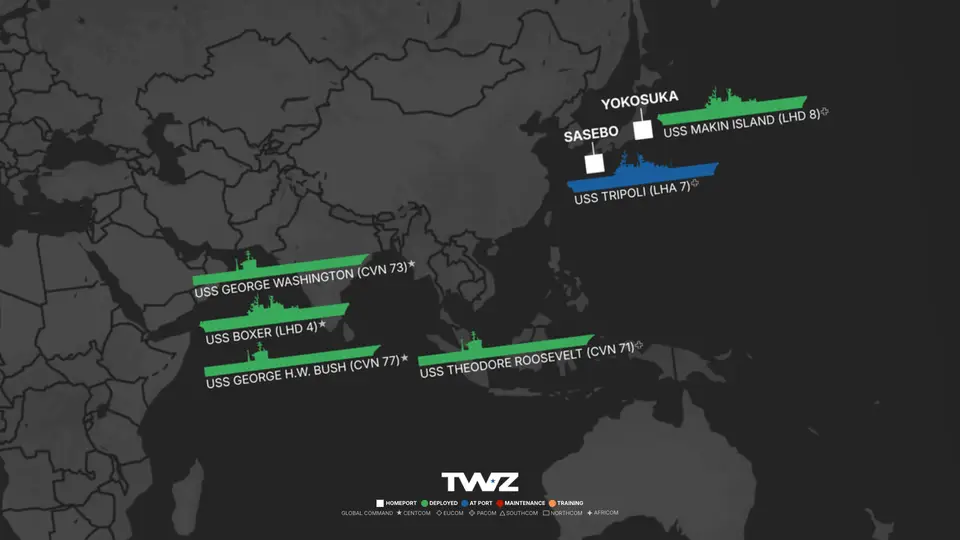
USS Theodore Roosevelt Arrives In Singapore; Last Stop Before Third Strike Group Reaches The Middle East (opens the original article)
The USS Theodore Roosevelt has arrived in Singapore, described as the last stop before a third strike group reaches the Middle East.
Warfare The War Zone
Why it mattersThe arrival provides a location update relevant to tracking carrier movements and regional deployments.
Sources1The War Zone
DoD taps Viasat to field operations ‘center’ for Golden Dome satellite data relay network (opens the original article)
The DoD tapped Viasat to design, field and scale a Mission Operation Center for the Space Data Network Backbone, under a contract worth up to $450 million.
Warfare Breaking Defense
Why it mattersThe center is intended to support operations for a satellite data relay network.
Sources1Breaking Defense
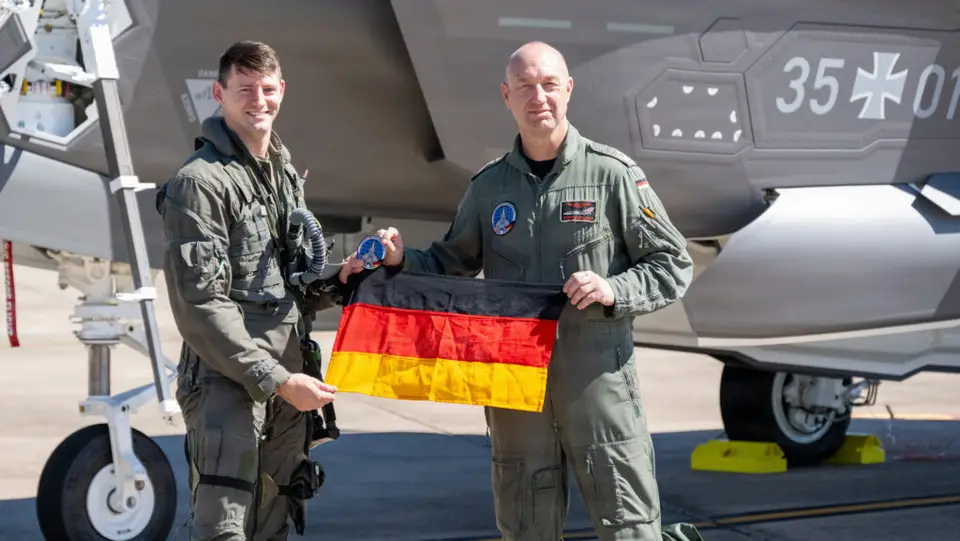
Europe’s airpower future is taking shape, but not as originally planned (opens the original article)
Germany’s next move, the fate of GCAP and the rise of CCAs are reshaping Europe’s combat aircraft strategy, Breaking Defense reports.
Warfare Breaking Defense
Why it mattersThese developments are relevant to how Europe’s future combat aircraft strategy is taking shape.
Sources1Breaking Defense
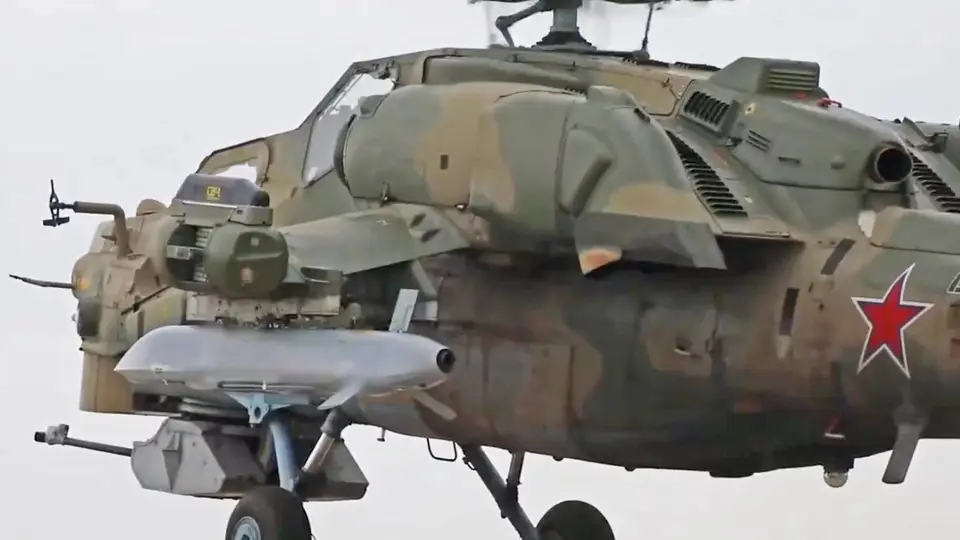
Russian Mi-28 Attack Helicopters Are Now Firing Cruise Missiles (opens the original article)
New footage shows Russian Mi-28 attack helicopters firing cruise missiles, highlighting a push to field lower-cost standoff weapons from unconventional platforms.
Warfare The War Zone
Why it mattersThe use of helicopters as missile platforms illustrates an operational approach to launching standoff weapons.
Sources1The War Zone
Talks, Attacks, and a Heist (opens the original article)
War on the Rocks introduces an every-other-week analysis of challenges involving China, Russia, Iran, North Korea and jihadists.
Warfare War on the Rocks
Why it mattersThe item outlines a broad range of actors for analysts following security challenges.
Sources1War on the Rocks
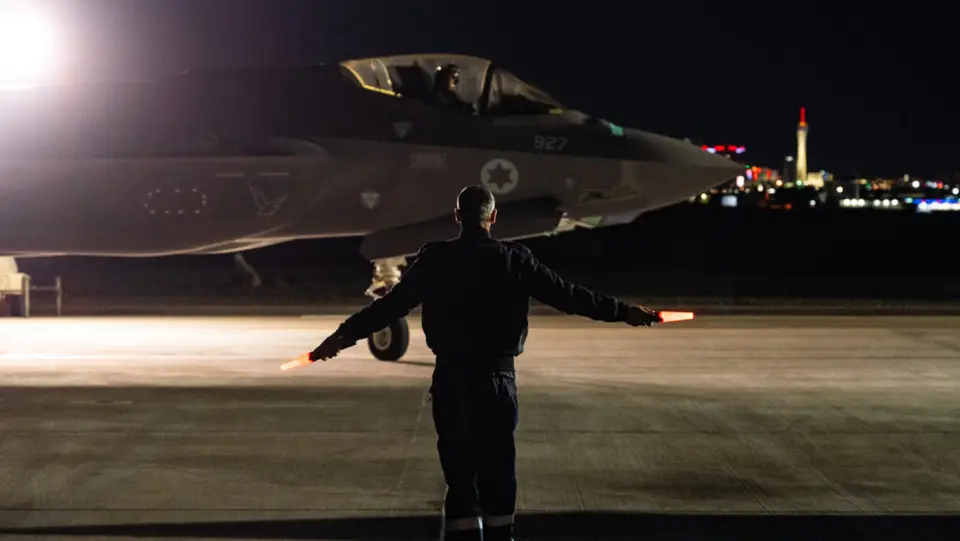
Cut to US aid would impact Israeli acquisition timelines, spending: Analysts (opens the original article)
Israel is actively seeking more Apache helicopters, F-15 and F-35 fighter jets, and munitions, according to the snippet.
Warfare Breaking Defense
Why it mattersThe requested aircraft and munitions are relevant to Israeli acquisition planning.
Sources1Breaking Defense
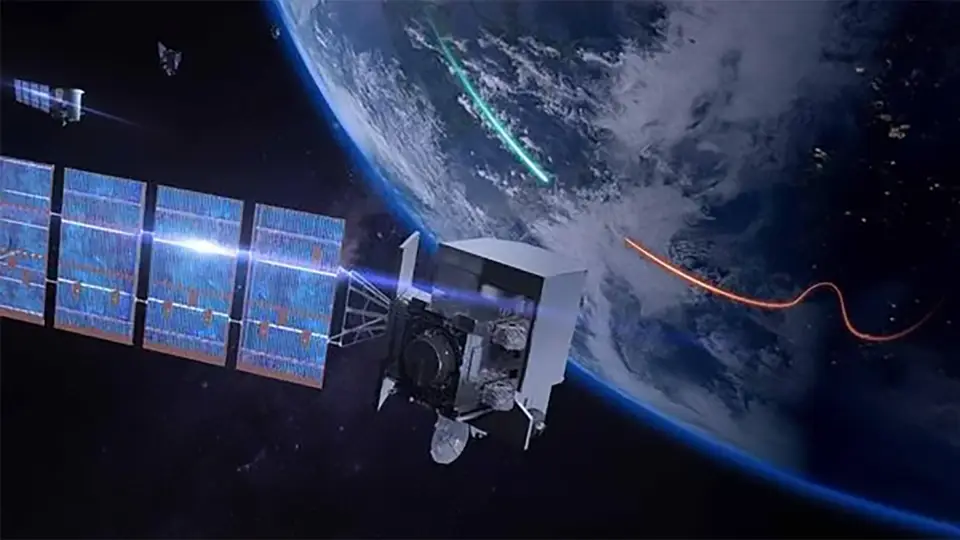
Key Space Force satellites can’t talk to each other, likely requiring $1B solution: Sources (opens the original article)
Sources say the Space Force is considering 12 or 13 Space Exchange Point satellites to translate between the SpaceX-built SDN Backbone and other Pentagon communications and missile-tracking satellites.
Warfare Breaking Defense
Why it mattersThe proposal highlights the operational importance of connecting satellite communications and missile-tracking systems.
Sources1Breaking Defense
Geopolitics & geodata
Strategy, geo wars, GNSS and satellite security.
Infleqtion Runs Optical Atomic Clock at Sea for Two Weeks During AUKUS Navy Exercise (opens the original article)
Infleqtion operated its Tiqker optical atomic clock aboard the U.S. Navy support vessel RV Merlin during a military exercise.
Geopolitics Inside GNSS
Strategic relevanceAn optical atomic clock operated at sea during a naval exercise, making the trial relevant to maritime timing technology.
Sources1Inside GNSS
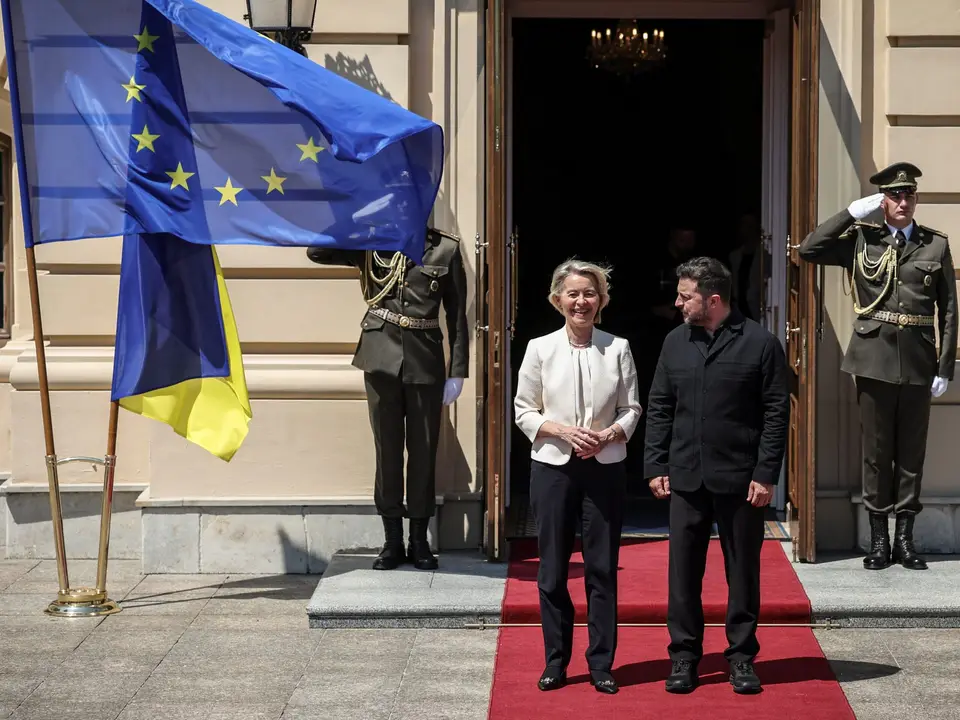
To settle Russia’s Ukraine war, Europe needs to let Kyiv in. Trump can help (really). (opens the original article)
The article argues that a Ukraine peace deal must set a date for Kyiv to join the EU, while noting hurdles and possible Washington leverage.
Geopolitics Atlantic Council
Strategic relevanceThe proposed EU accession date and role for Washington are strategic questions in any deal to end the war.
Sources1Atlantic Council
What in the World? (opens the original article)
Foreign Policy’s quiz covers Russia and Ukraine hacking each other, U.S. midterm elections and Indonesia deploying troops to its capital.
Geopolitics Foreign Policy
Strategic relevanceThe item links cyber activity and political or security developments across several regions.
Sources1Foreign Policy
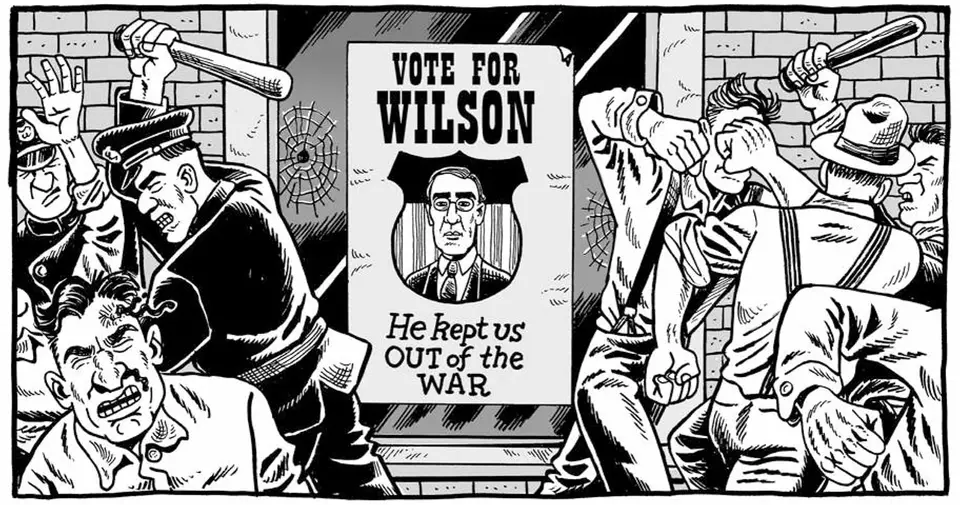
How a World War I Crackdown Predicted ICE (opens the original article)
A new graphic novel makes the case that a World War I crackdown predicted ICE, according to Foreign Policy.
Geopolitics Foreign Policy
Strategic relevanceThe piece draws a historical comparison about crackdowns and immigration enforcement.
Sources1Foreign Policy
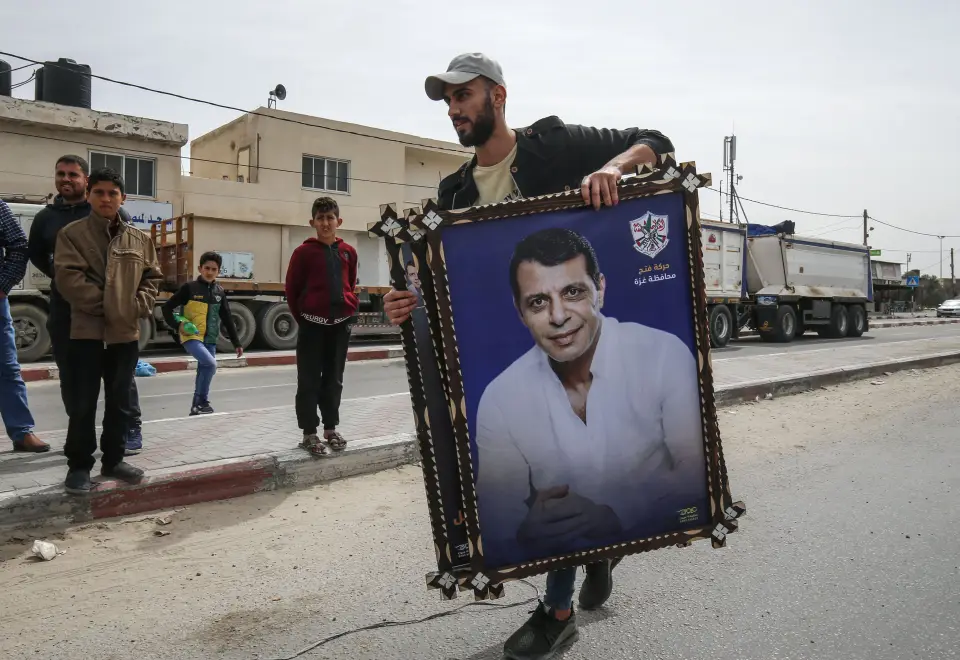
The International Power Broker Trying to Normalize Hamas (opens the original article)
Mohammed Dahlan is seeking to unite Palestine by reaching out to Gaza’s ostracized leaders, Foreign Policy reports.
Geopolitics Foreign Policy
Strategic relevanceThe outreach is relevant to Palestinian political alignment and efforts to unite Palestine.
Sources1Foreign Policy
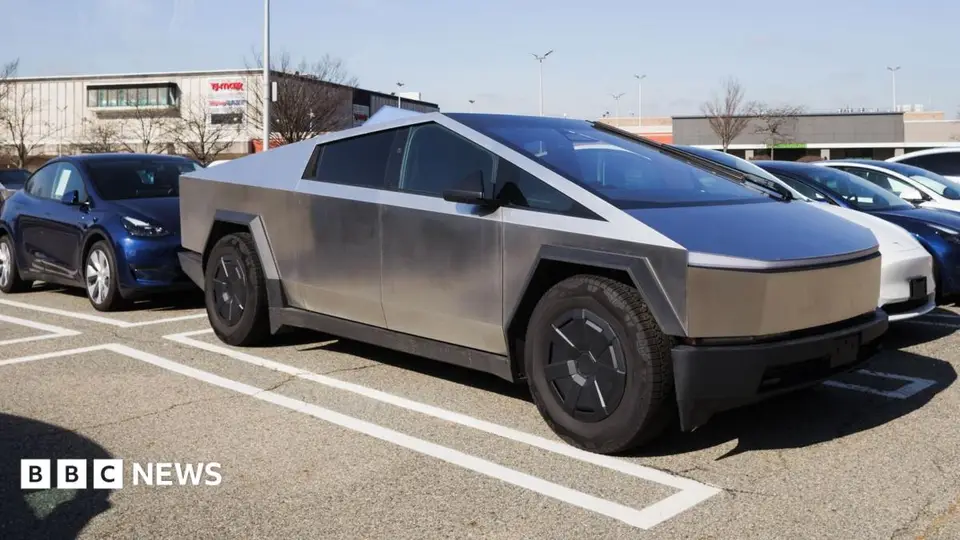
Watch: Is it the end of the road for Tesla's Cybertruck? (opens the original article)
Elon Musk said Tesla production will halt in Texas to focus on the company’s self-driving Cybercabs.
Geopolitics BBC World
Strategic relevanceThe reported shift links vehicle production with a focus on autonomous taxis.
Sources1BBC World
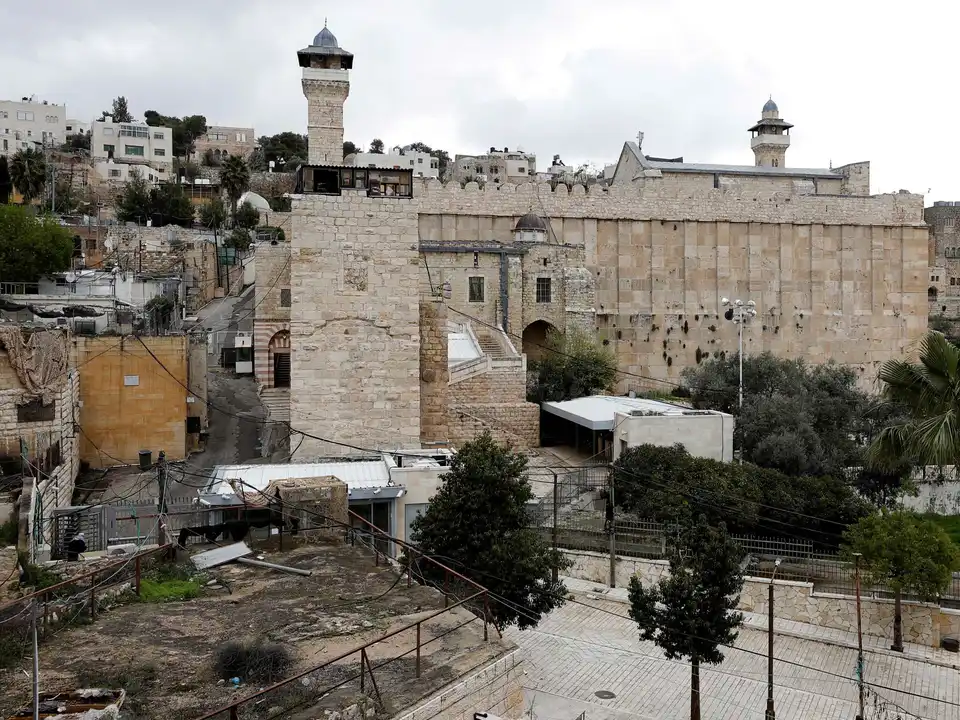
Israel closes Hebron’s Ibrahimi Mosque to Palestinians for Jewish holiday (opens the original article)
Israel closed Hebron’s Ibrahimi Mosque to Palestinians for a Jewish holiday and reopened it exclusively for Israelis, deepening tensions over control of the site.
Geopolitics Al Jazeera
Strategic relevanceThe closure highlights contested access and control at a West Bank holy site.
Sources1Al Jazeera
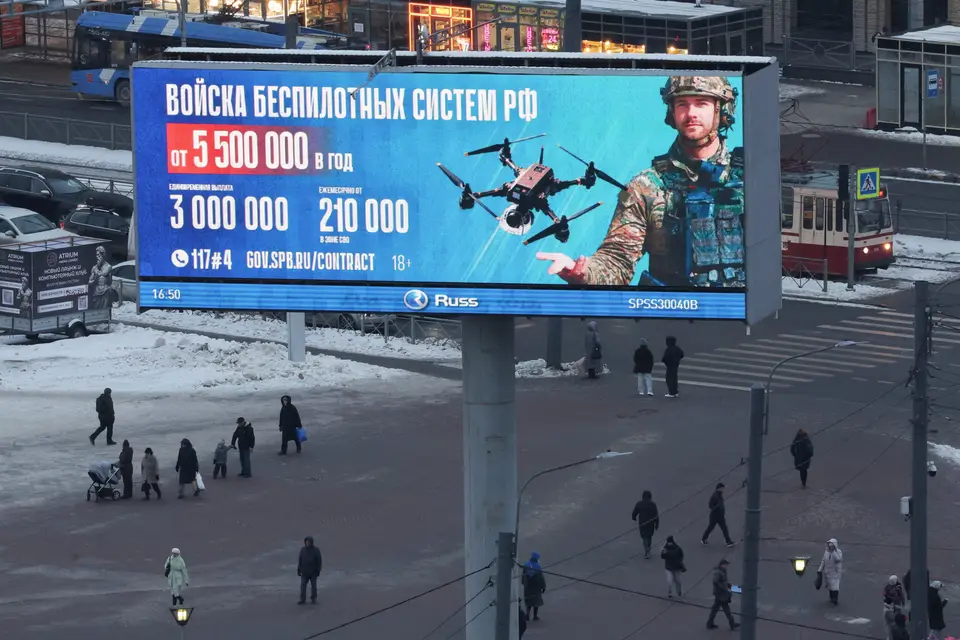
Not quite mercenaries: How Russia lures thousands of foreigners to fight in its war on Ukraine (opens the original article)
The article says many of Russia’s foreign recruits were coerced into service because of vulnerable legal or financial statuses.
Geopolitics Atlantic Council
Strategic relevanceThe reported coercion highlights how legal and financial vulnerability can intersect with recruitment in war.
Sources1Atlantic Council
| CVE | CVSS | Product | Ransomware | Added / due | Required action |
|---|---|---|---|---|---|
| CVE-2026-19868 | 7.5High | SonicWall SonicOS SSLVPN | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2024-27834 | 5.5Medium | Apple Multiple Products | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-119977 | 8.1High | WordPress WordPress Core | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-118527 | 4.3Medium | Ivanti Connect Secure | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-111357 | 7.0High | Ivanti Connect Secure | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-97229 | 10.0Critical | GitLab Community Edition and Enterprise Edition | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-76418 | 8.6High | Cisco Secure Firewall ASA Software and Cisco Secure FTD Software | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-41709 | 2.7Low | Broadcom VMware ESX | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-46300 | 7.8High | Linux Kernel | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-48356 | 9.3Critical | Adobe Commerce and Magento | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-111497 | 9.2Critical | Google Brotli | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-109618 | 9.2Critical | PHP Group PHP | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
Source: CISA KEV catalogue; CVSS scores from NVD where published. “No score” means NVD has not scored it yet.
Keyword index
Counted from this page. Select one to filter.