 OUTPOST
Edition 237 — 8 November 2026
Cyber, warfare technology and geopolitics as compiled on 8 November 2026.
Cyber
Breaches, campaigns, advisories and research.
Iris Ohyama data cloud breach exposes info of 7.7 million customers (opens the original article)
Iris Ohyama disclosed that personal information belonging to about 7.7 million people may have been exposed after unauthorized access to a third-party cloud service.
Cyber BleepingComputer
What to checkReview third-party cloud access and investigate whether personal information was exposed.
Sources1BleepingComputer
Brava Security Emerges From Stealth With $15 Million in Funding (opens the original article)
Brava Security says its multi-agent AI platform generates attack-like telemetry to help identify gaps in enterprise defenses.
Cyber SecurityWeek
What to checkAssess whether generated attack telemetry can help reveal gaps in existing defenses.
Sources1SecurityWeek
Week in review: Refrigeration cyberattacks hit European retailers again, Patch Tuesday forecast (opens the original article)
Help Net Security’s weekly review mentions cyberattacks targeting European retailers’ refrigeration systems again and a Patch Tuesday forecast.
Cyber Help Net Security
What to checkCheck access and security monitoring for systems supporting refrigeration operations.
Sources1Help Net Security
Hackers pull off $133 million French bank heist via service provider (opens the original article)
BleepingComputer reports a cyberattack targeting French cooperative bank Crédit Mutuel Arkéa enabled fraudulent transactions of up to $133 million, prompting the bank to suspend certain systems.
Cyber BleepingComputer
What to checkReview service-provider access, transaction monitoring and plans for suspending affected systems.
Sources1BleepingComputer
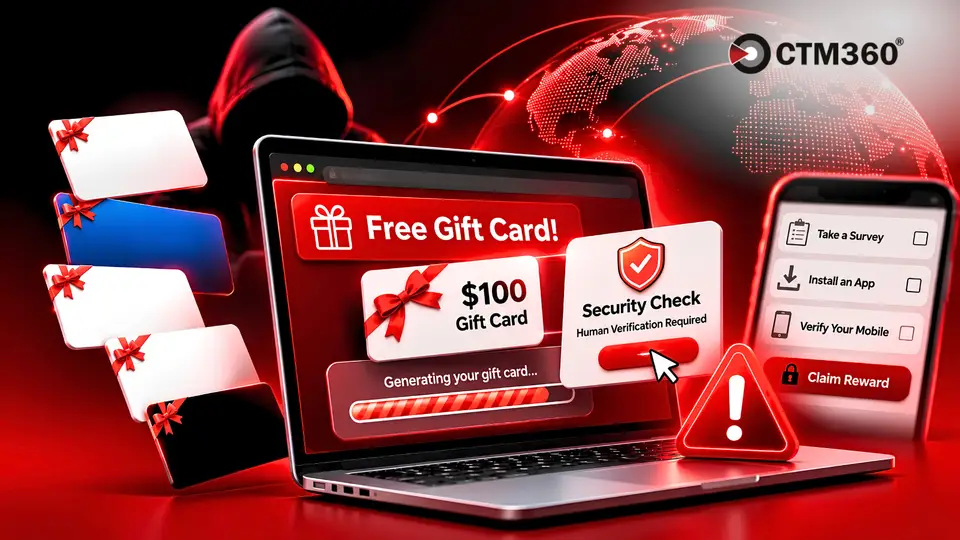
CTM360 Exposes Fake Gift Card Scams Exploiting Trusted Brands (opens the original article)
CTM360 says scammers impersonate major brands and celebrities in fake gift card giveaways that collect personal information and trigger unwanted subscriptions.
Cyber BleepingComputer
What to checkCheck for impersonation, deceptive verification steps, and unwanted subscription flows in consumer-facing campaigns.
Sources1BleepingComputer
Warfare
Drones, electronic warfare, missiles and defence systems.
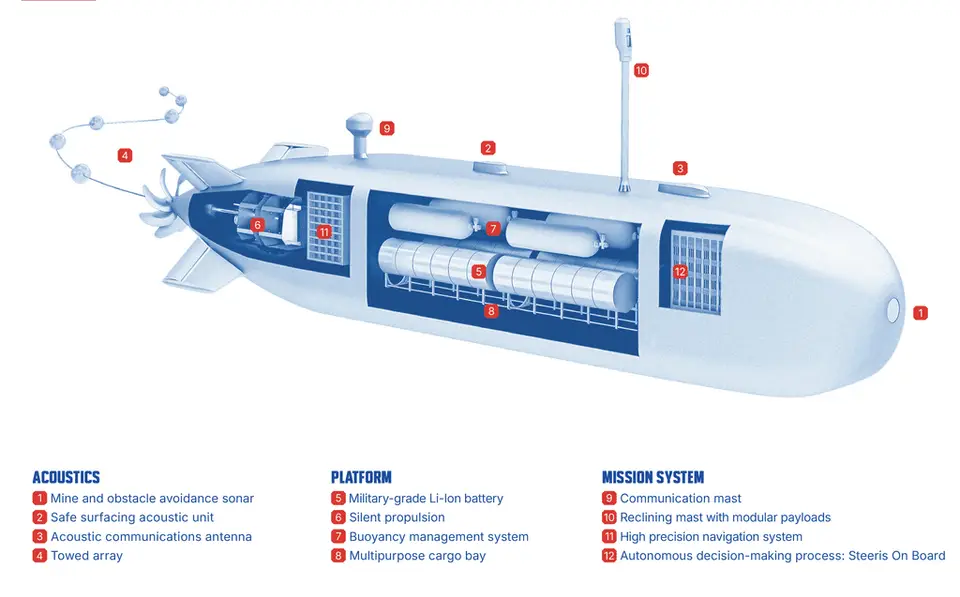
Naval Group to Build UCUV Underwater Combat Drone Demonstrator for French Navy (opens the original article)
Naval Group will build an operational underwater combat drone demonstrator for the French Navy, with sea trials scheduled to begin in 2028.
Warfare Naval News
Why it mattersThe demonstrator highlights an underwater uncrewed capability being developed for naval operations.
Sources1Naval News
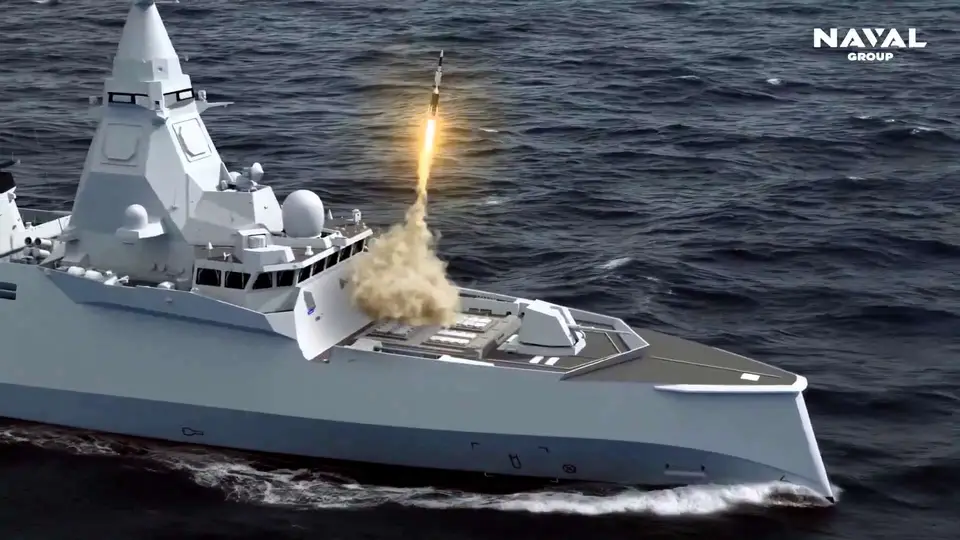
Euronaval 2026: France Orders 32-Cell Aster Missile Upgrade for FDI Frigates (opens the original article)
Naval News reports France ordered a 32-cell VLS upgrade for FDI frigates, doubling their Aster missile air defense capacity.
Warfare Naval News
Why it mattersThe upgrade changes the frigates’ air-defense capacity and missile-launch configuration.
Sources1Naval News
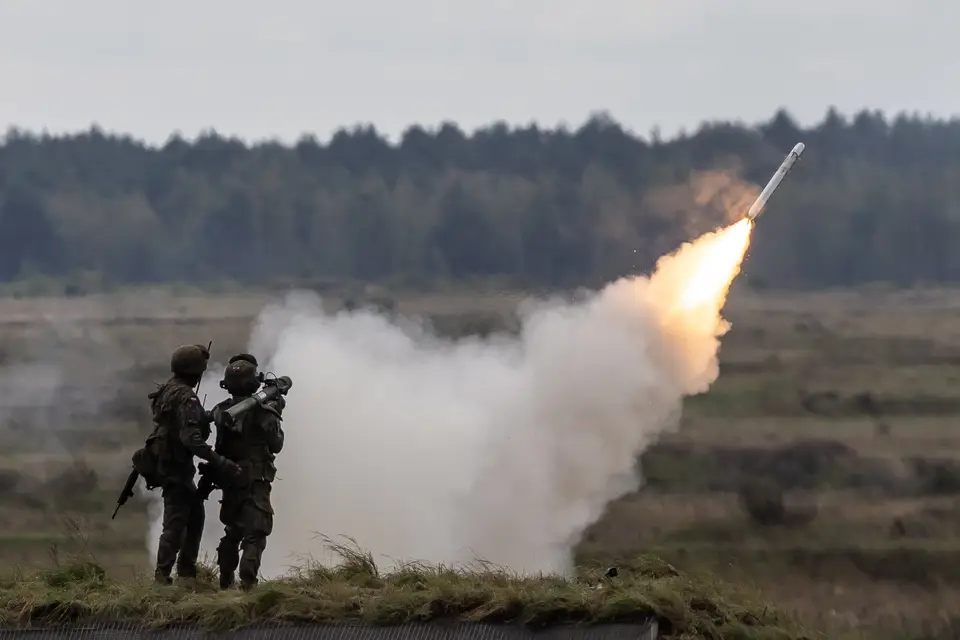
European troops set to train in Poland for postwar Ukraine deployment (opens the original article)
Britain and France will lead 2,800 troops from 11 nations in a two-week exercise on moving, protecting and supplying a force for a postwar Ukraine deployment.
Warfare Defense News
Why it mattersThe exercise tests multinational force movement, protection and supply for a possible deployment.
Sources1Defense News
Geopolitics & geodata
Strategy, geo wars, GNSS and satellite security.
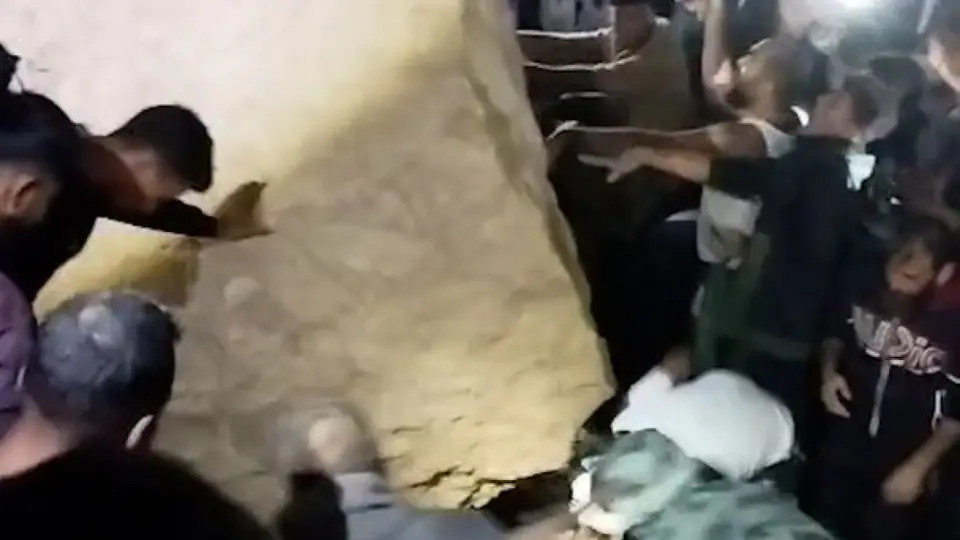
Deadly sand cliff collapses on displaced families in Gaza (opens the original article)
Al Jazeera reports that a sand cliff collapsed on displaced families in Gaza, causing deaths.
Geopolitics Al Jazeera
Strategic relevanceThe collapse highlights the immediate risks of terrain and shelter conditions for displaced people.
Sources1Al Jazeera
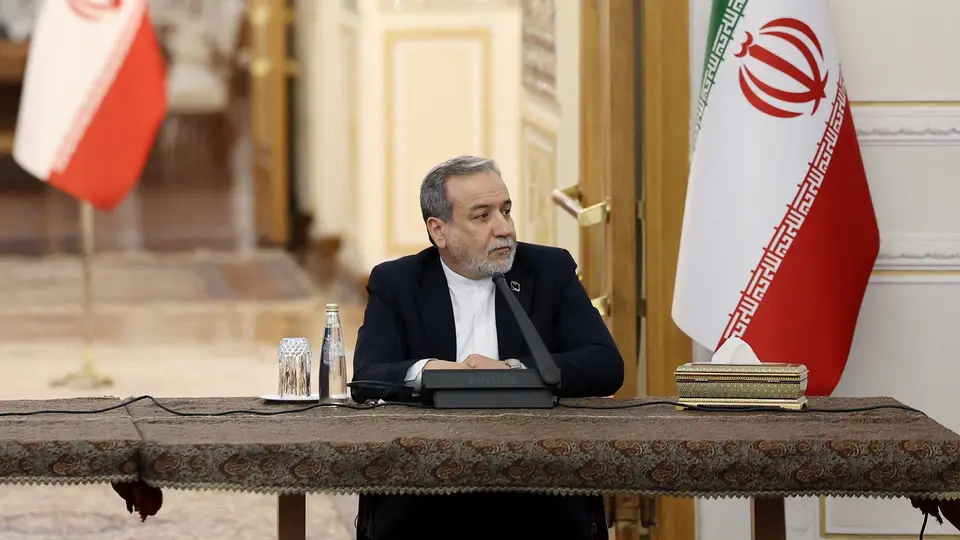
Iran waiting to resume talks after US midterms ‘shock’Iranian Foreign Minis (opens the original article)
Iranian Foreign Minister Abbas Araghchi says there has been no progress in talks with the US.
Geopolitics Al Jazeera
Strategic relevanceThe statement is relevant to tracking the status of US-Iran diplomacy.
Sources1Al Jazeera
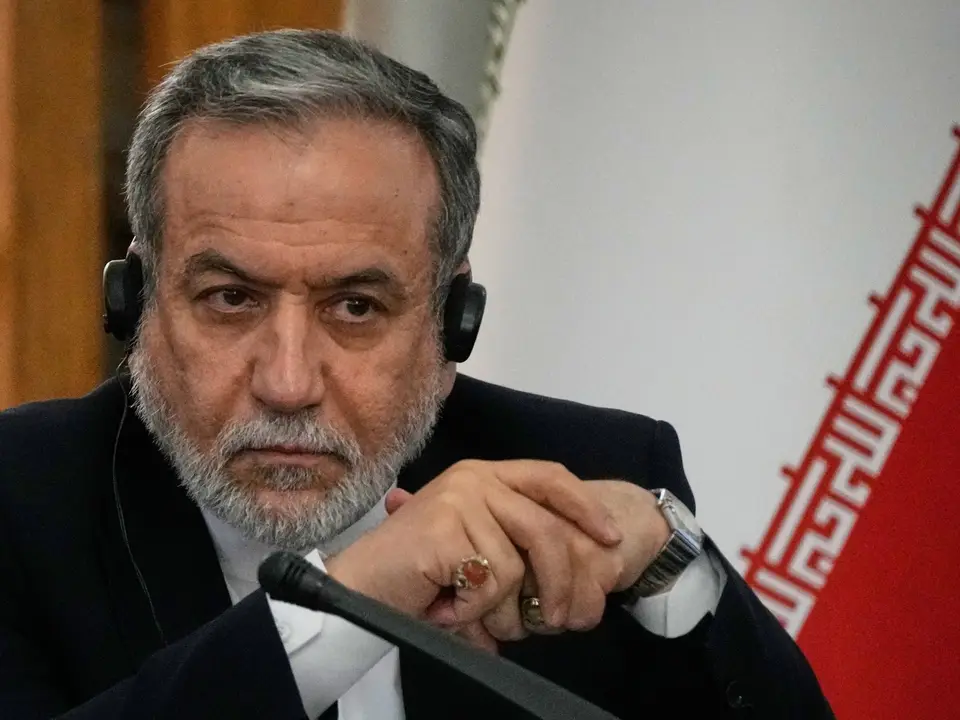
Iran threatens to ‘rain down hell’ if US escalates war (opens the original article)
The title reports an Iranian threat if the US escalates; President Trump says US forces are ready to strike if necessary.
Geopolitics Al Jazeera
Strategic relevanceThe statements underscore the operational significance of military readiness amid escalation rhetoric.
Sources1Al Jazeera
Iran executes three men for 'armed unrest' after January protests (opens the original article)
The report says Iran executed three men for “armed unrest” and claims they were part of anti-government protests earlier this year.
Geopolitics BBC World
Strategic relevanceThe executions and protest allegations are relevant to Iran’s domestic political climate.
Sources1BBC World
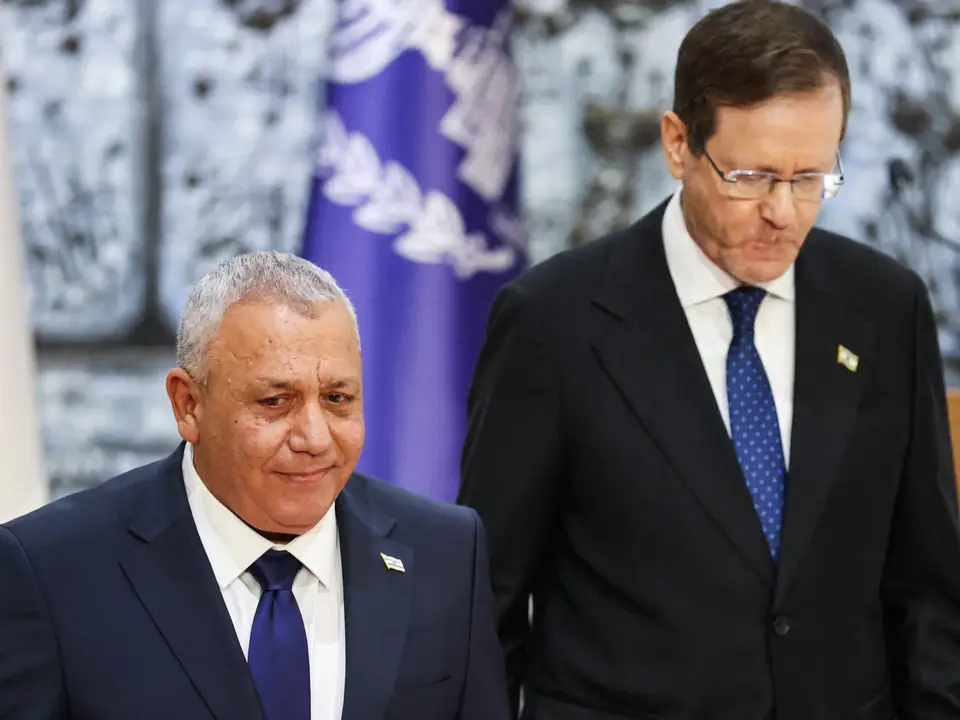
Eisenkot open to Netanyahu joining Israel’s next government (opens the original article)
Al Jazeera reports that Israel’s president tasked the opposition leader, identified in the title as Eisenkot, with forming a new government.
Geopolitics Al Jazeera
Strategic relevanceThe government-forming process is relevant to Israel’s political direction.
Sources1Al Jazeera
Nvidia CEO Huang admits affair amid rumors of China spy ties (opens the original article)
DW reports that Jensen Huang apologized for cheating on his wife amid reports of alleged espionage; Nvidia pledged to investigate.
Geopolitics DW
Strategic relevanceThe investigation makes the company's response to alleged espionage relevant to security observers.
Sources1DW
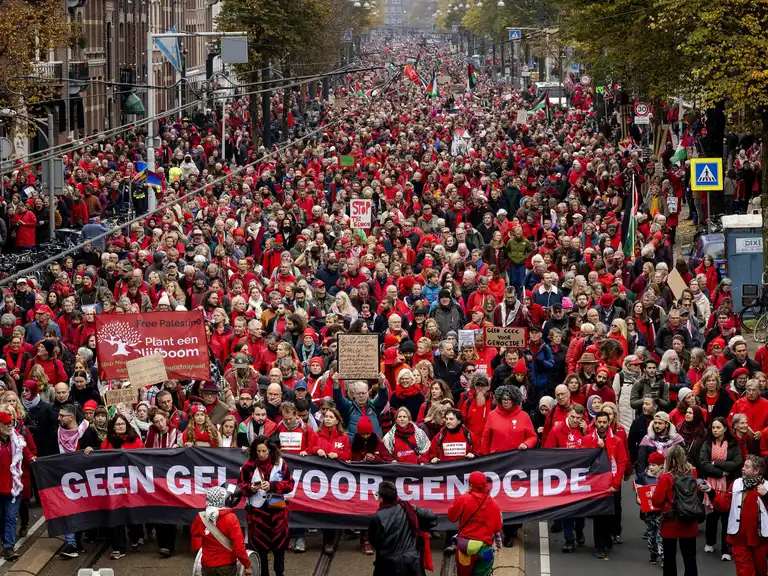
Hundreds of thousands join Amsterdam’s ‘Red Line’ protest against Israel (opens the original article)
Al Jazeera reports that protesters in Amsterdam called for stricter trade restrictions on Israel and an end to arms sales.
Geopolitics Al Jazeera
Strategic relevanceThe protest highlights public pressure over trade and arms-sale policy toward Israel.
Sources1Al Jazeera
Jerusalem Daily: Eisenkot picked over Netanyahu to form government (opens the original article)
Al Jazeera reports that Israel’s president picked Gadi Eisenkot to form the next government, passing over Benjamin Netanyahu.
Geopolitics Al Jazeera
Strategic relevanceThe choice may shape the next government’s formation and political direction.
Sources1Al Jazeera
| CVE | CVSS | Product | Ransomware | Added / due | Required action |
|---|---|---|---|---|---|
| CVE-2026-19868 | 7.5High | SonicWall SonicOS SSLVPN | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2024-27834 | 5.5Medium | Apple Multiple Products | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-119977 | 8.1High | WordPress WordPress Core | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-118527 | 4.3Medium | Ivanti Connect Secure | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-111357 | 7.0High | Ivanti Connect Secure | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-97229 | 10.0Critical | GitLab Community Edition and Enterprise Edition | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-76418 | 8.6High | Cisco Secure Firewall ASA Software and Cisco Secure FTD Software | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-41709 | 2.7Low | Broadcom VMware ESX | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-46300 | 7.8High | Linux Kernel | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-48356 | 9.3Critical | Adobe Commerce and Magento | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-111497 | 9.2Critical | Google Brotli | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-109618 | 9.2Critical | PHP Group PHP | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
Source: CISA KEV catalogue; CVSS scores from NVD where published. “No score” means NVD has not scored it yet.
Keyword index
Counted from this page. Select one to filter.