 OUTPOST
Edition 239 — 10 November 2026
Cyber, warfare technology and geopolitics as compiled on 10 November 2026.
Cyber
Breaches, campaigns, advisories and research.
CISA Adds Four Known Exploited Vulnerabilities to Catalog (opens the original article)
CISA says it added four vulnerabilities to its Known Exploited Vulnerabilities Catalog.
Cyber CISA Advisories
What to checkCheck whether your systems use affected products and prioritize applicable fixes.
Sources1CISA Advisories
Vanderbilt University hit in BYOD ransomware attack, data theft claimed (opens the original article)
Vanderbilt says it is responding to a cyberattack claimed by the BYOD ransomware gang, which claims to have encrypted university databases and stolen sensitive data.
Cyber BleepingComputer
What to checkCheck BYOD access, investigate database activity, and assess whether student, employee, or research data was exposed.
Sources1BleepingComputer
SEGA newsletter data breach exposes 2.2 million email addresses (opens the original article)
SEGA disclosed that a breach at its third-party newsletter provider exposed 2.2 million subscribers’ email addresses.
Cyber BleepingComputer
What to checkReview third-party data access and alert subscribers to relevant phishing risks.
Sources1BleepingComputer
N-able takes cloud platform offline after 30+ "zero-days" published (opens the original article)
N-able took hosted N-central environments offline and urged on-premises customers to shut down servers after a researcher disclosed alleged zero-days.
Cyber BleepingComputer
What to checkFollow N-able’s guidance and check whether your organization runs affected environments.
Sources1BleepingComputer
York University breach exposed personal information dating to 2007 (opens the original article)
York University said a threat actor stole personal information submitted through online forms.
Cyber BleepingComputer
What to checkReview what personal information online forms collect and how it is protected.
Sources1BleepingComputer
Data breach at hearing aid giant Amplifon impacts thousands (opens the original article)
Amplifon’s U.S. arm notified customers about a breach that included medical information.
Cyber The Record
What to checkCheck breach notifications and the handling of sensitive customer information.
Sources1The Record
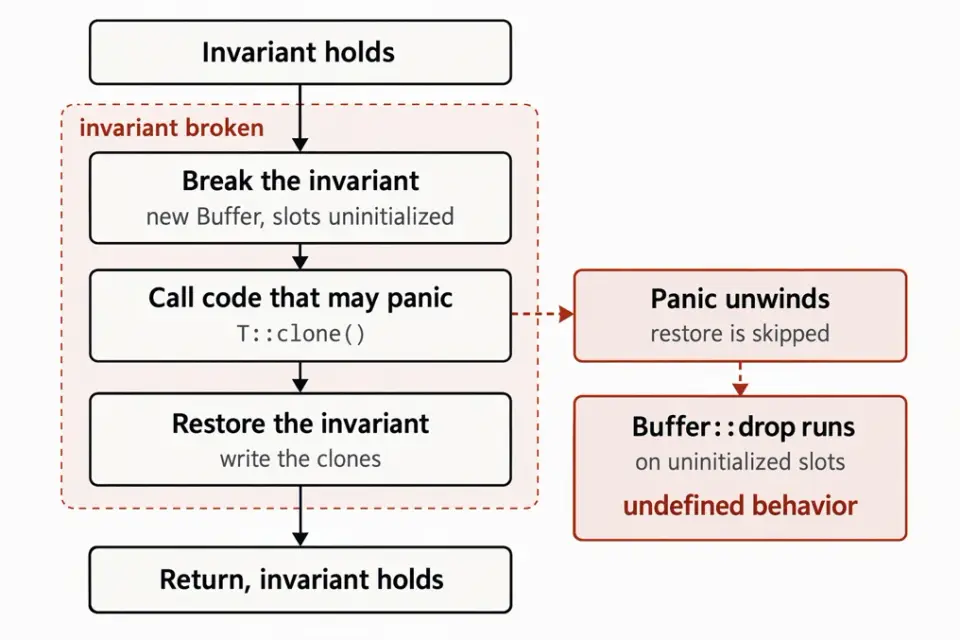
FORGE Lab uses agentic tools to identify memory safety issues in Rust (opens the original article)
Microsoft FORGE Lab researchers found memory-safety bugs in Rust’s core and std libraries, including cases where safe Rust code can trigger undefined behavior.
Cyber Microsoft Security
What to checkReview memory-safety assumptions and library use in Rust software.
Sources1Microsoft Security
France blames Iran for fridge cyberattacks, says some caused fires (opens the original article)
French authorities attributed the fridge cyberattacks to Shahid Kaveh, described as an IRGC cyber unit previously linked to attacks on industrial controllers.
Cyber The Record
What to checkCheck industrial controller exposure and incident response for operational technology.
Sources1The Record
France blames Iranian hackers for supermarket attacks that sparked fires (opens the original article)
France linked cyberattacks disrupting refrigeration systems at retail locations to Iranian state-backed hackers, saying they caused food losses and fires.
Cyber BleepingComputer
What to checkAssess protections for refrigeration and other operational technology systems.
Sources1BleepingComputer
Vanderbilt cybersecurity incident impacting campus devices and systems (opens the original article)
Vanderbilt University warned that a cyberattack may have affected campus devices and systems.
Cyber The Record
What to checkCheck campus systems for impact and follow the university’s incident guidance.
Sources1The Record
Warfare
Drones, electronic warfare, missiles and defence systems.
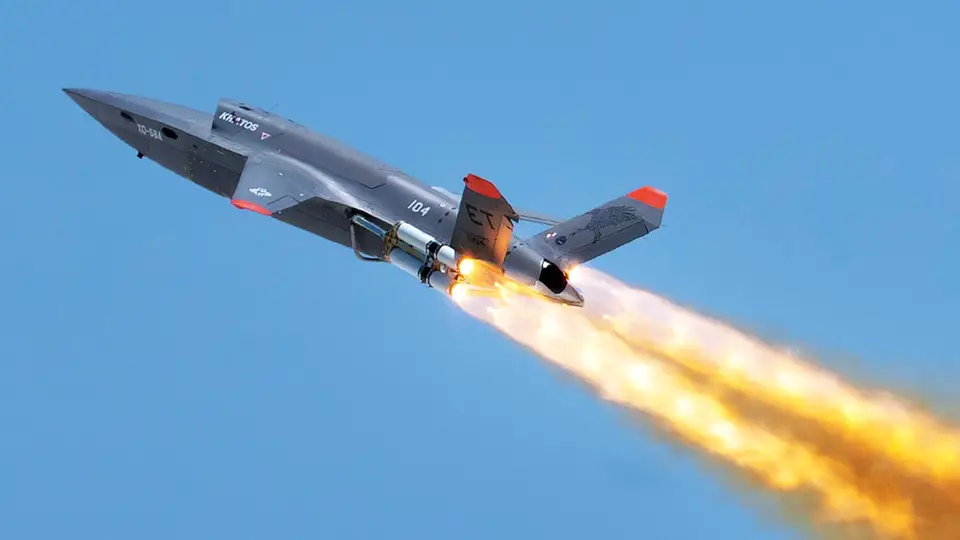
MQ-58 Valkyrie Drones Now Cost $6M-$8M Each (opens the original article)
Kratos says the MQ-58 Valkyrie's relative affordability is key to competing in a growing field of Collaborative Combat Aircraft designs; the title gives a cost of $6M-$8M each.
Warfare The War Zone
Why it mattersThe stated cost and competition offer a measure of the platform's position among collaborative combat drone designs.
Sources1The War Zone
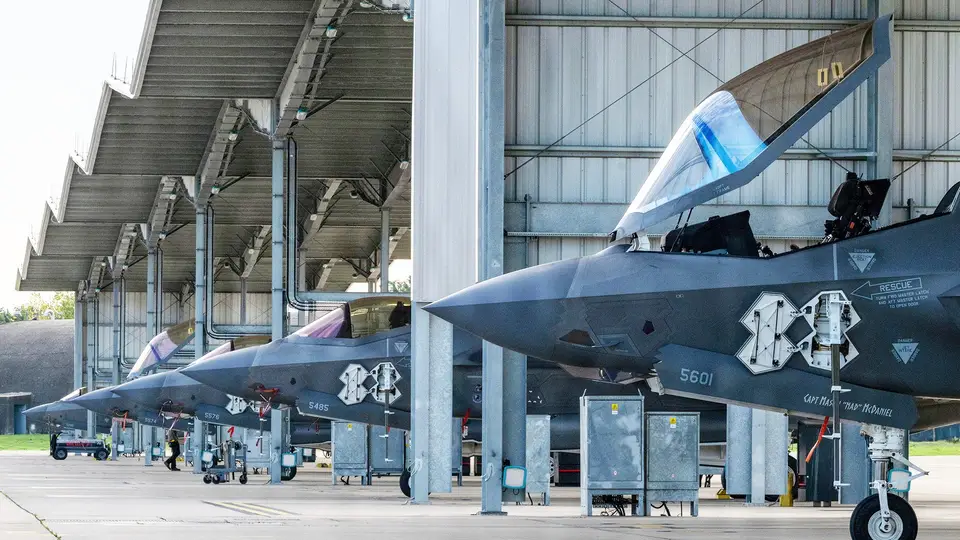
Security Levels At U.S. Bases In England Raised Without Explanation (opens the original article)
Security levels at U.S. bases in England were raised without explanation. Aviation spotters had noticed unusual activity at RAF Mildenhall.
Warfare The War Zone
Why it mattersThe unexplained change highlights the value of monitoring base security and activity.
Sources1The War Zone
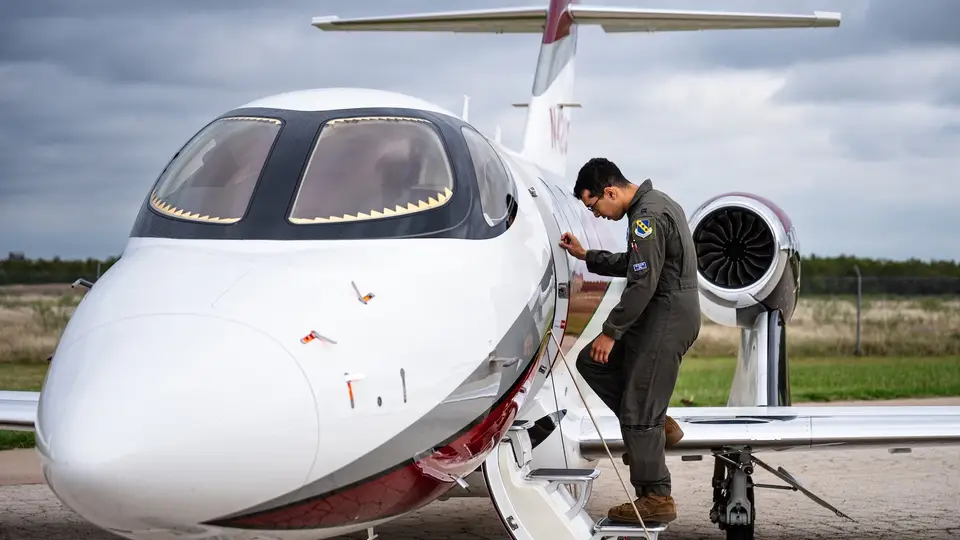
B-1B Lancer Pilots Are Now Training On HondaJets (opens the original article)
Contractor-operated HondaJets will give B-1 pilots more yearly flight time at a lower cost, the report says.
Warfare The War Zone
Why it mattersUsing contractor aircraft for training may expand pilot flight time while limiting costs.
Sources1The War Zone
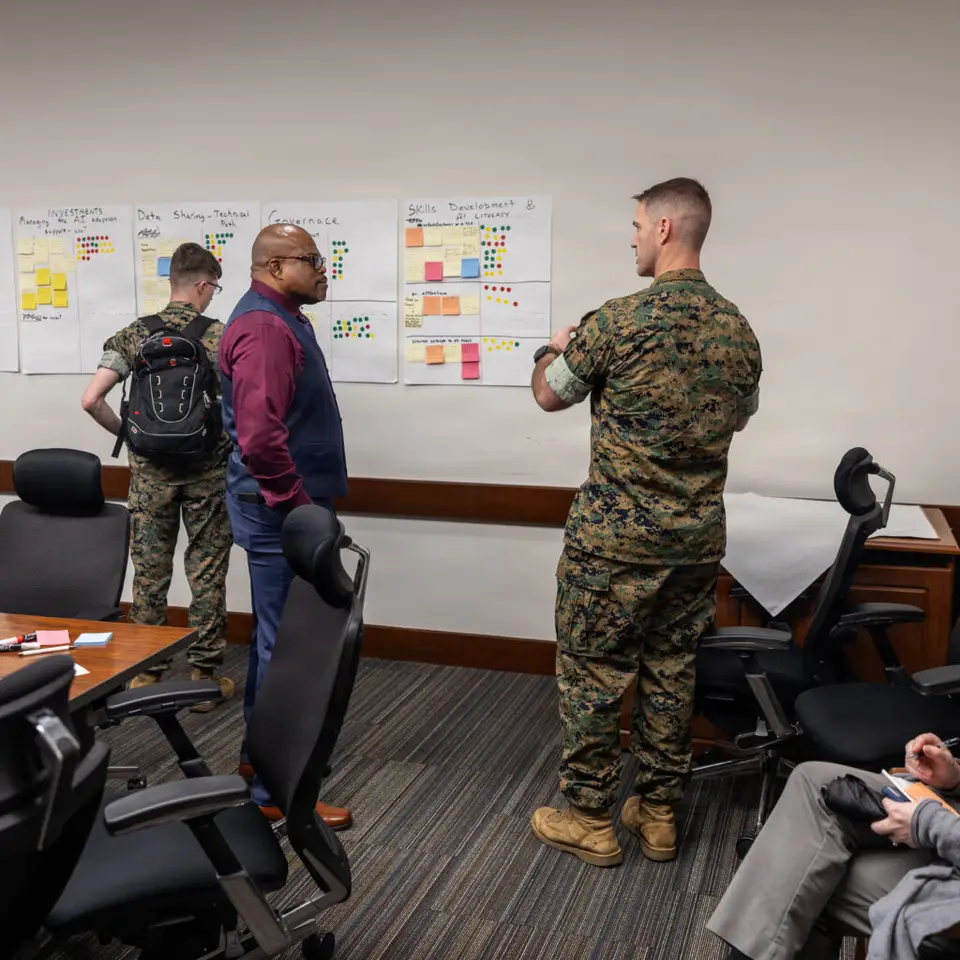
The next breakthrough is software built on the battlefield by agentic bots (opens the original article)
A sponsored article says autonomous agents and mission-specific software promise faster responses to emerging threats.
Warfare Breaking Defense
Why it mattersThe concept connects agentic software with battlefield decision and response processes.
Sources1Breaking Defense
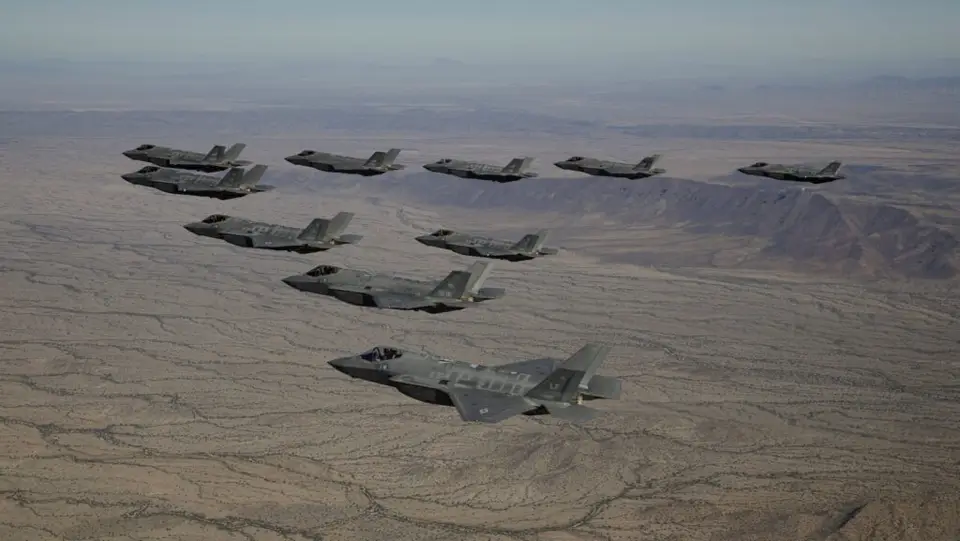
Pentagon can’t track thousands of F-35 parts: GAO (opens the original article)
The GAO found more than 17,000 F-35 parts, worth an estimated $1.3 billion, missing from the program’s inventory system.
Warfare Breaking Defense
Why it mattersThe finding highlights the operational importance of tracking military parts.
Sources1Breaking Defense
Stained Glass and Sacred Spaces: Symbolism Abounds in Ukrainian Media (opens the original article)
War on the Rocks presents a weekly digest of Ukrainian commentary and analysis from across the political spectrum.
Warfare War on the Rocks
Why it mattersThe digest offers a view of Ukrainian media commentary and political perspectives.
Sources1War on the Rocks
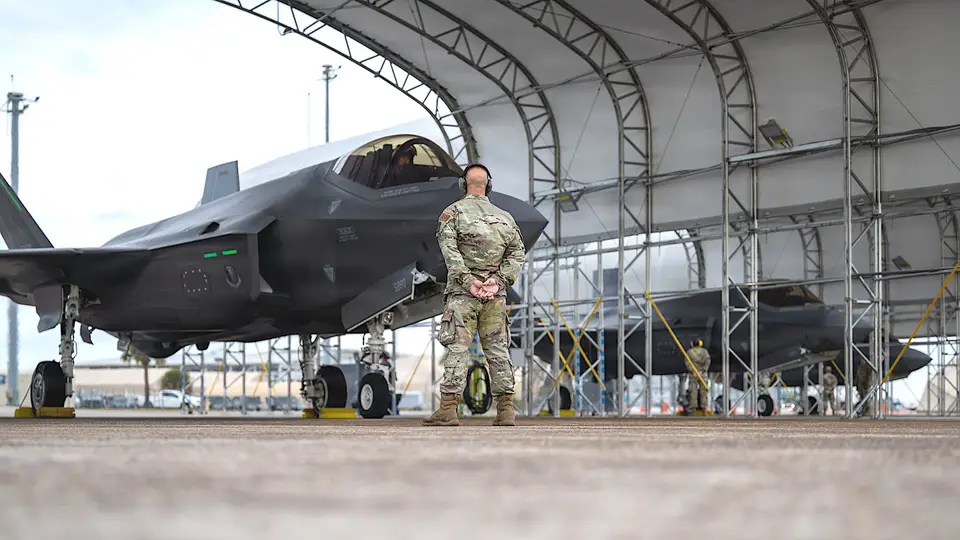
Netting To Shield F-35s At Tyndall AFB From Drone Attacks Eyed By USAF (opens the original article)
Tentative plans for anti-drone nets at Tyndall reflect debate within the USAF about investing in physical hardening.
Warfare The War Zone
Why it mattersPhysical barriers are one proposed way to shield aircraft from drone attacks.
Sources1The War Zone
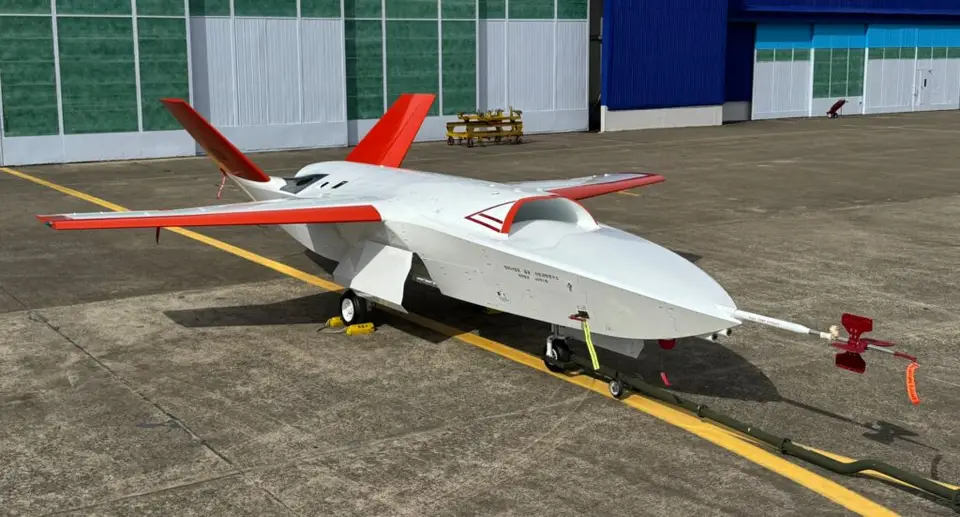
Korean Air Aerospace pushes forward with Collaborative Combat Aircraft plans (opens the original article)
Korean Air Aerospace says it delivered its Collaborative Combat Aircraft platform last year and plans flight tests at the end of this year.
Warfare Breaking Defense
Why it mattersThe plans indicate continued development and testing of collaborative combat aircraft.
Sources1Breaking Defense
Geopolitics & geodata
Strategy, geo wars, GNSS and satellite security.
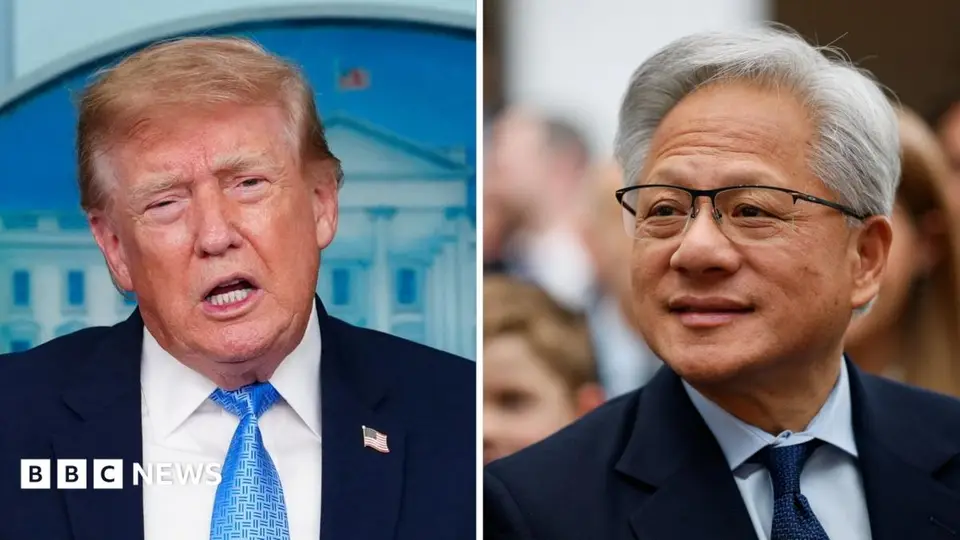
Trump says FBI investigating Nvidia boss's affair with alleged Chinese spy (opens the original article)
Trump says the FBI is investigating Nvidia boss Jensen Huang's affair with an alleged Chinese spy; he says he asked Huang about it.
Geopolitics BBC World 2 outlets
Strategic relevanceThe reported inquiry highlights the national-security relevance of alleged intelligence links involving a prominent technology leader.
Sources1BBC World2Al Jazeera
What to Know About Nvidia CEO Jensen Huang’s Chinese Spy Scandal (opens the original article)
Foreign Policy says an alleged affair involving Nvidia CEO Jensen Huang and a Chinese intelligence asset has national security implications.
Geopolitics Foreign Policy 2 outlets
Strategic relevanceThe allegation raises questions about how personal relationships may intersect with national security.
Sources1Foreign Policy2BBC World
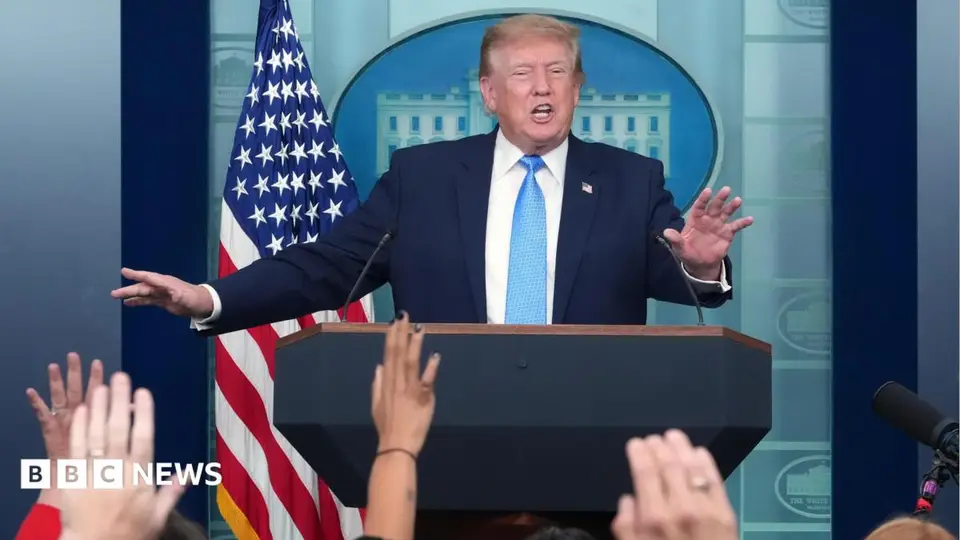
Trump says more US attacks on Iran 'highly unlikely' (opens the original article)
Trump says further US attacks on Iran are highly unlikely and describes the current position as status quo, while saying the US remains ready if the situation changes.
Geopolitics BBC World
Strategic relevanceThe statements indicate how US leaders describe current posture toward Iran and conditions that could change it.
Sources1BBC World
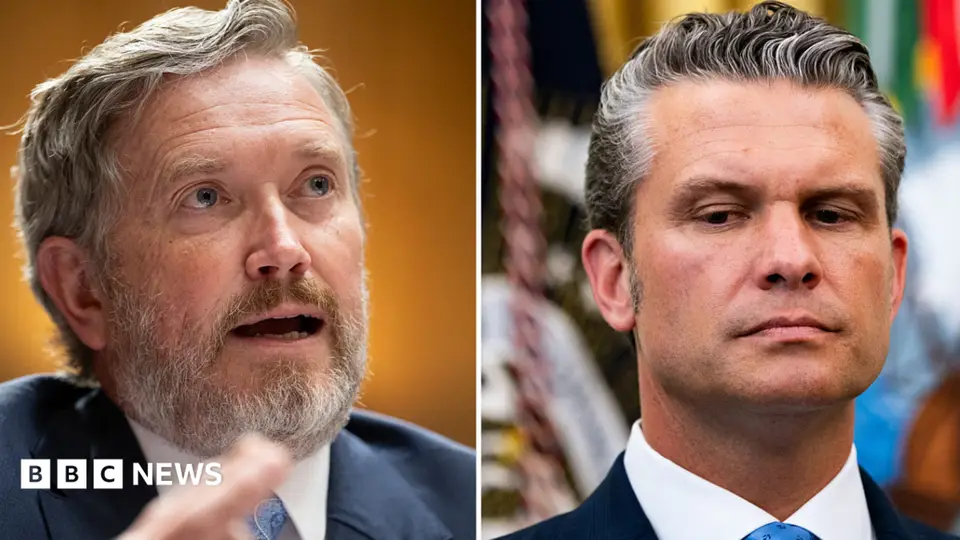
Republican congressman to force impeachment vote on Defence Secretary Hegseth (opens the original article)
Representative Thomas Massie plans to force an impeachment vote on Defense Secretary Hegseth; the report says the effort will likely fail.
Geopolitics BBC World
Strategic relevanceThe planned vote is a marker of political conflict over defense leadership.
Sources1BBC World
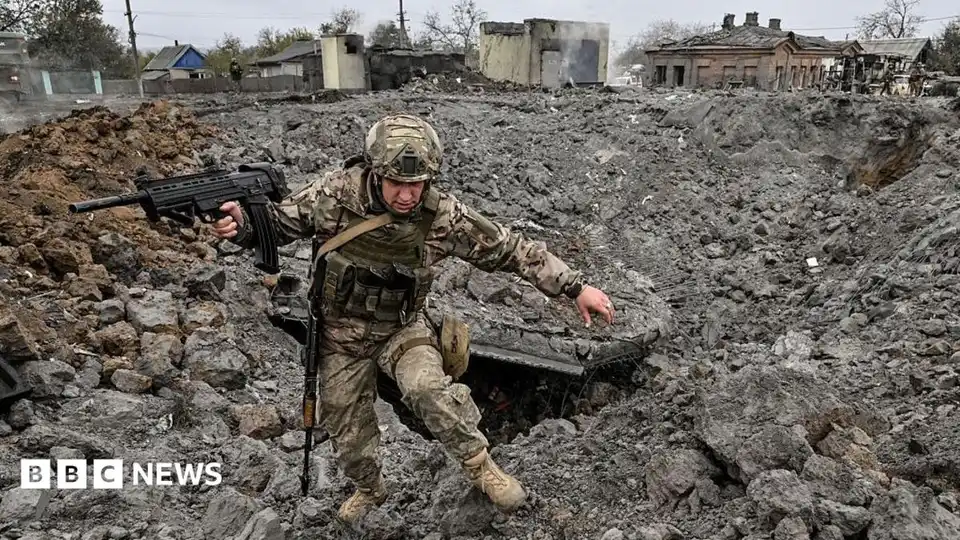
Ukraine peace talks resume with 'some flexibility' by warring sides, US officials say (opens the original article)
US officials say Kyiv, Washington, and Moscow are sending delegations to the UAE for the first trilateral talks since February; the sides show some flexibility.
Geopolitics BBC World
Strategic relevanceThe trilateral format and UAE venue are relevant to tracking diplomacy among the parties to the war.
Sources1BBC World
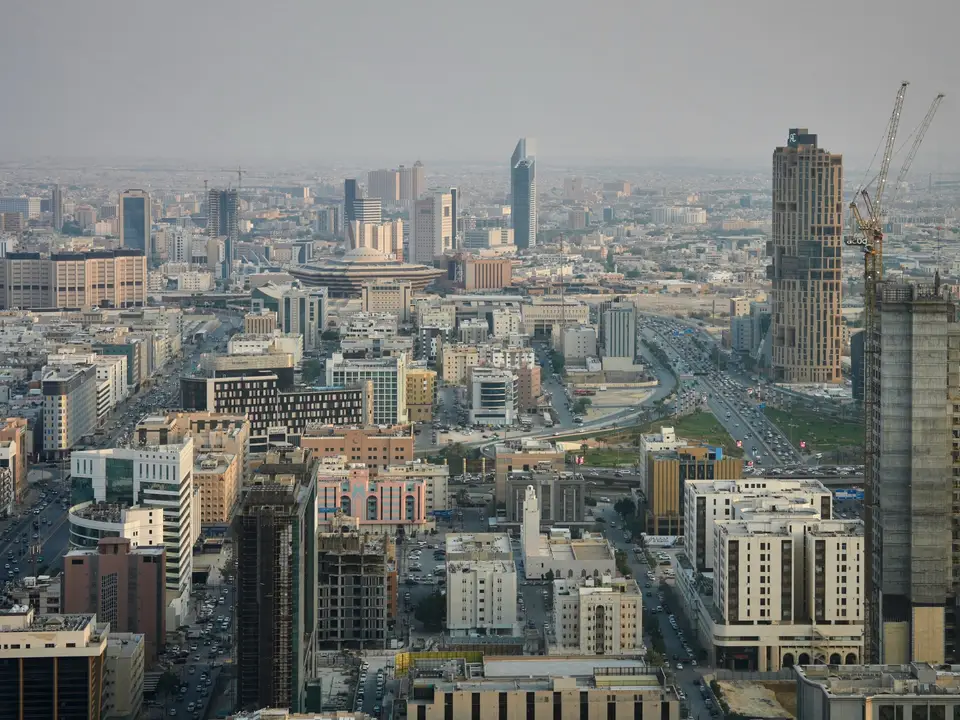
Saudi Arabia downs missiles fired at Riyadh after Houthi attack on pipeline (opens the original article)
Saudi forces intercepted two missiles fired towards Riyadh, hours after Saudi Arabia reported damage to its East-West pipeline.
Geopolitics Al Jazeera
Strategic relevanceThe reported missile interception and pipeline damage make infrastructure security and regional geography relevant.
Sources1Al Jazeera
Newly-elected Democrats react to Hegseth impeachment bid (opens the original article)
Newly elected Democrats say holding Defense Secretary Pete Hegseth accountable will be a priority in the next Congress.
Geopolitics Al Jazeera
Strategic relevanceThe stated priority signals a potential focus of congressional oversight of the defense secretary.
Sources1Al Jazeera
What students got right about the $6 billion Binance hack, and how they would prevent the next one (opens the original article)
Atlantic Council describes students encountering a scenario similar to a $6 billion cryptocurrency theft during a cyber strategy competition.
Geopolitics Atlantic Council
Strategic relevanceThe scenario illustrates how exercises can test preparation for cryptocurrency theft.
Sources1Atlantic Council
| CVE | CVSS | Product | Ransomware | Added / due | Required action |
|---|---|---|---|---|---|
| CVE-2026-102895 | 9.8Critical | GPUStack GPUStack | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-123158 | 8.1High | OpenBSD OpenSSH | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-116779 | 9.8Critical | SignalWire FreeSwitch | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-123218 | 9.8Critical | IBM Aspera Faspex | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-19868 | 7.5High | SonicWall SonicOS SSLVPN | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2024-27834 | 5.5Medium | Apple Multiple Products | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-119977 | 8.1High | WordPress WordPress Core | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-118527 | 4.3Medium | Ivanti Connect Secure | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-111357 | 7.0High | Ivanti Connect Secure | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-97229 | 10.0Critical | GitLab Community Edition and Enterprise Edition | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-76418 | 8.6High | Cisco Secure Firewall ASA Software and Cisco Secure FTD Software | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
| CVE-2026-41709 | 2.7Low | Broadcom VMware ESX | None known | Added Due | Apply mitigations in accordance with vendor instructions. Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. CISA’s full wordingApply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines. |
Source: CISA KEV catalogue; CVSS scores from NVD where published. “No score” means NVD has not scored it yet.
Keyword index
Counted from this page. Select one to filter.